
fastfinder
 codeyourweb/fastfinder
Incident Response - Fast suspicious file finder
digital-forensicsforensicsincident-response+1
codeyourweb/fastfinderIncident Response - Fast suspicious file finder
 google/grr
Remote live forensics and incident response framework with Python agent for collecting forensic data from endpoints, including memory, disk, and…
 marcosd4h/memhunter
Live hunting of code injection techniques
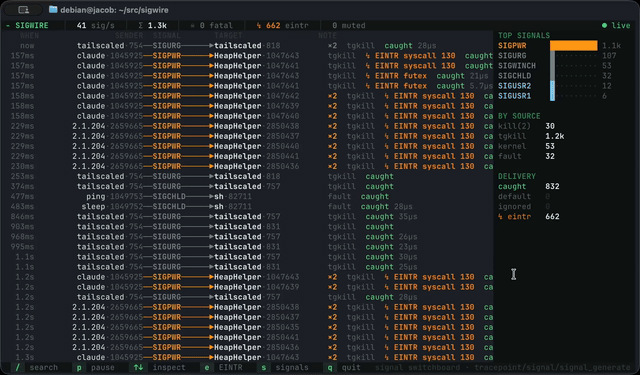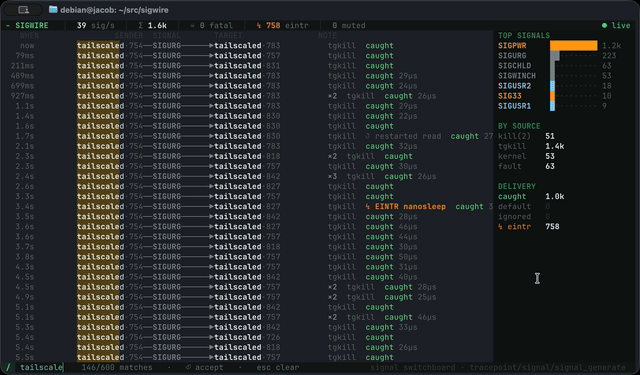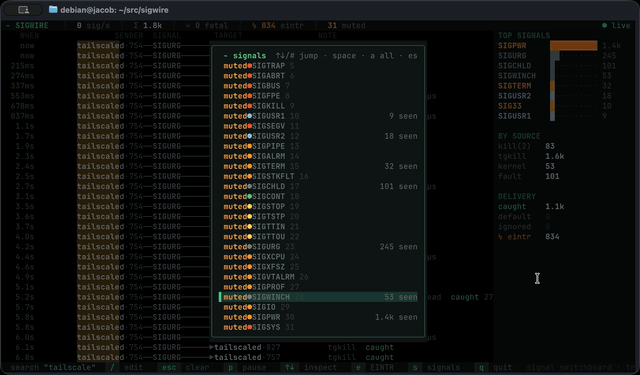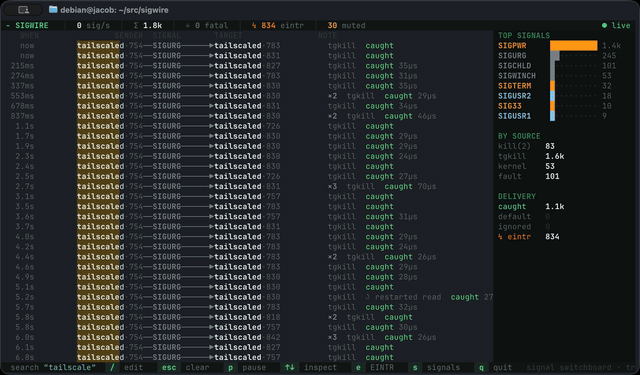 yeet-src/sigwire
Live kernel signal observability tool using eBPF tracepoints to stream every signal raised on a Linux host, showing sender, target, disposition,…
 la3ar0v/tuxresponse
Automated Linux incident response script with live triage, memory acquisition (LiME), disk imaging, YARA scanning, and HTML report generation.
 ncsc-nl/citrix-2025
Digital forensics and incident response tool using YARA rules to scan Citrix NetScaler core dumps, disk images, and live hosts for signs of…
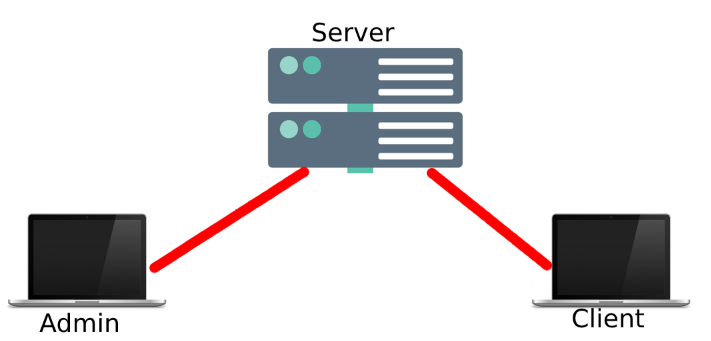 letsdefendio/simple-live-data-collection
Client-server tool for live data collection during incident response. Admin sends requests to clients to gather system information for forensic…
 ignacioj/whacamole
Live memory analysis detecting malware IOCs in processes, modules, handles, tokens, threads, .NET assemblies, memory address space and environment…
 ibondarenko1/azure-sentinel-detection-engineering
9 MITRE ATT&CK-mapped KQL detections on a live Microsoft Sentinel + Defender XDR environment (control-plane, endpoint, identity), with a PR-gated…
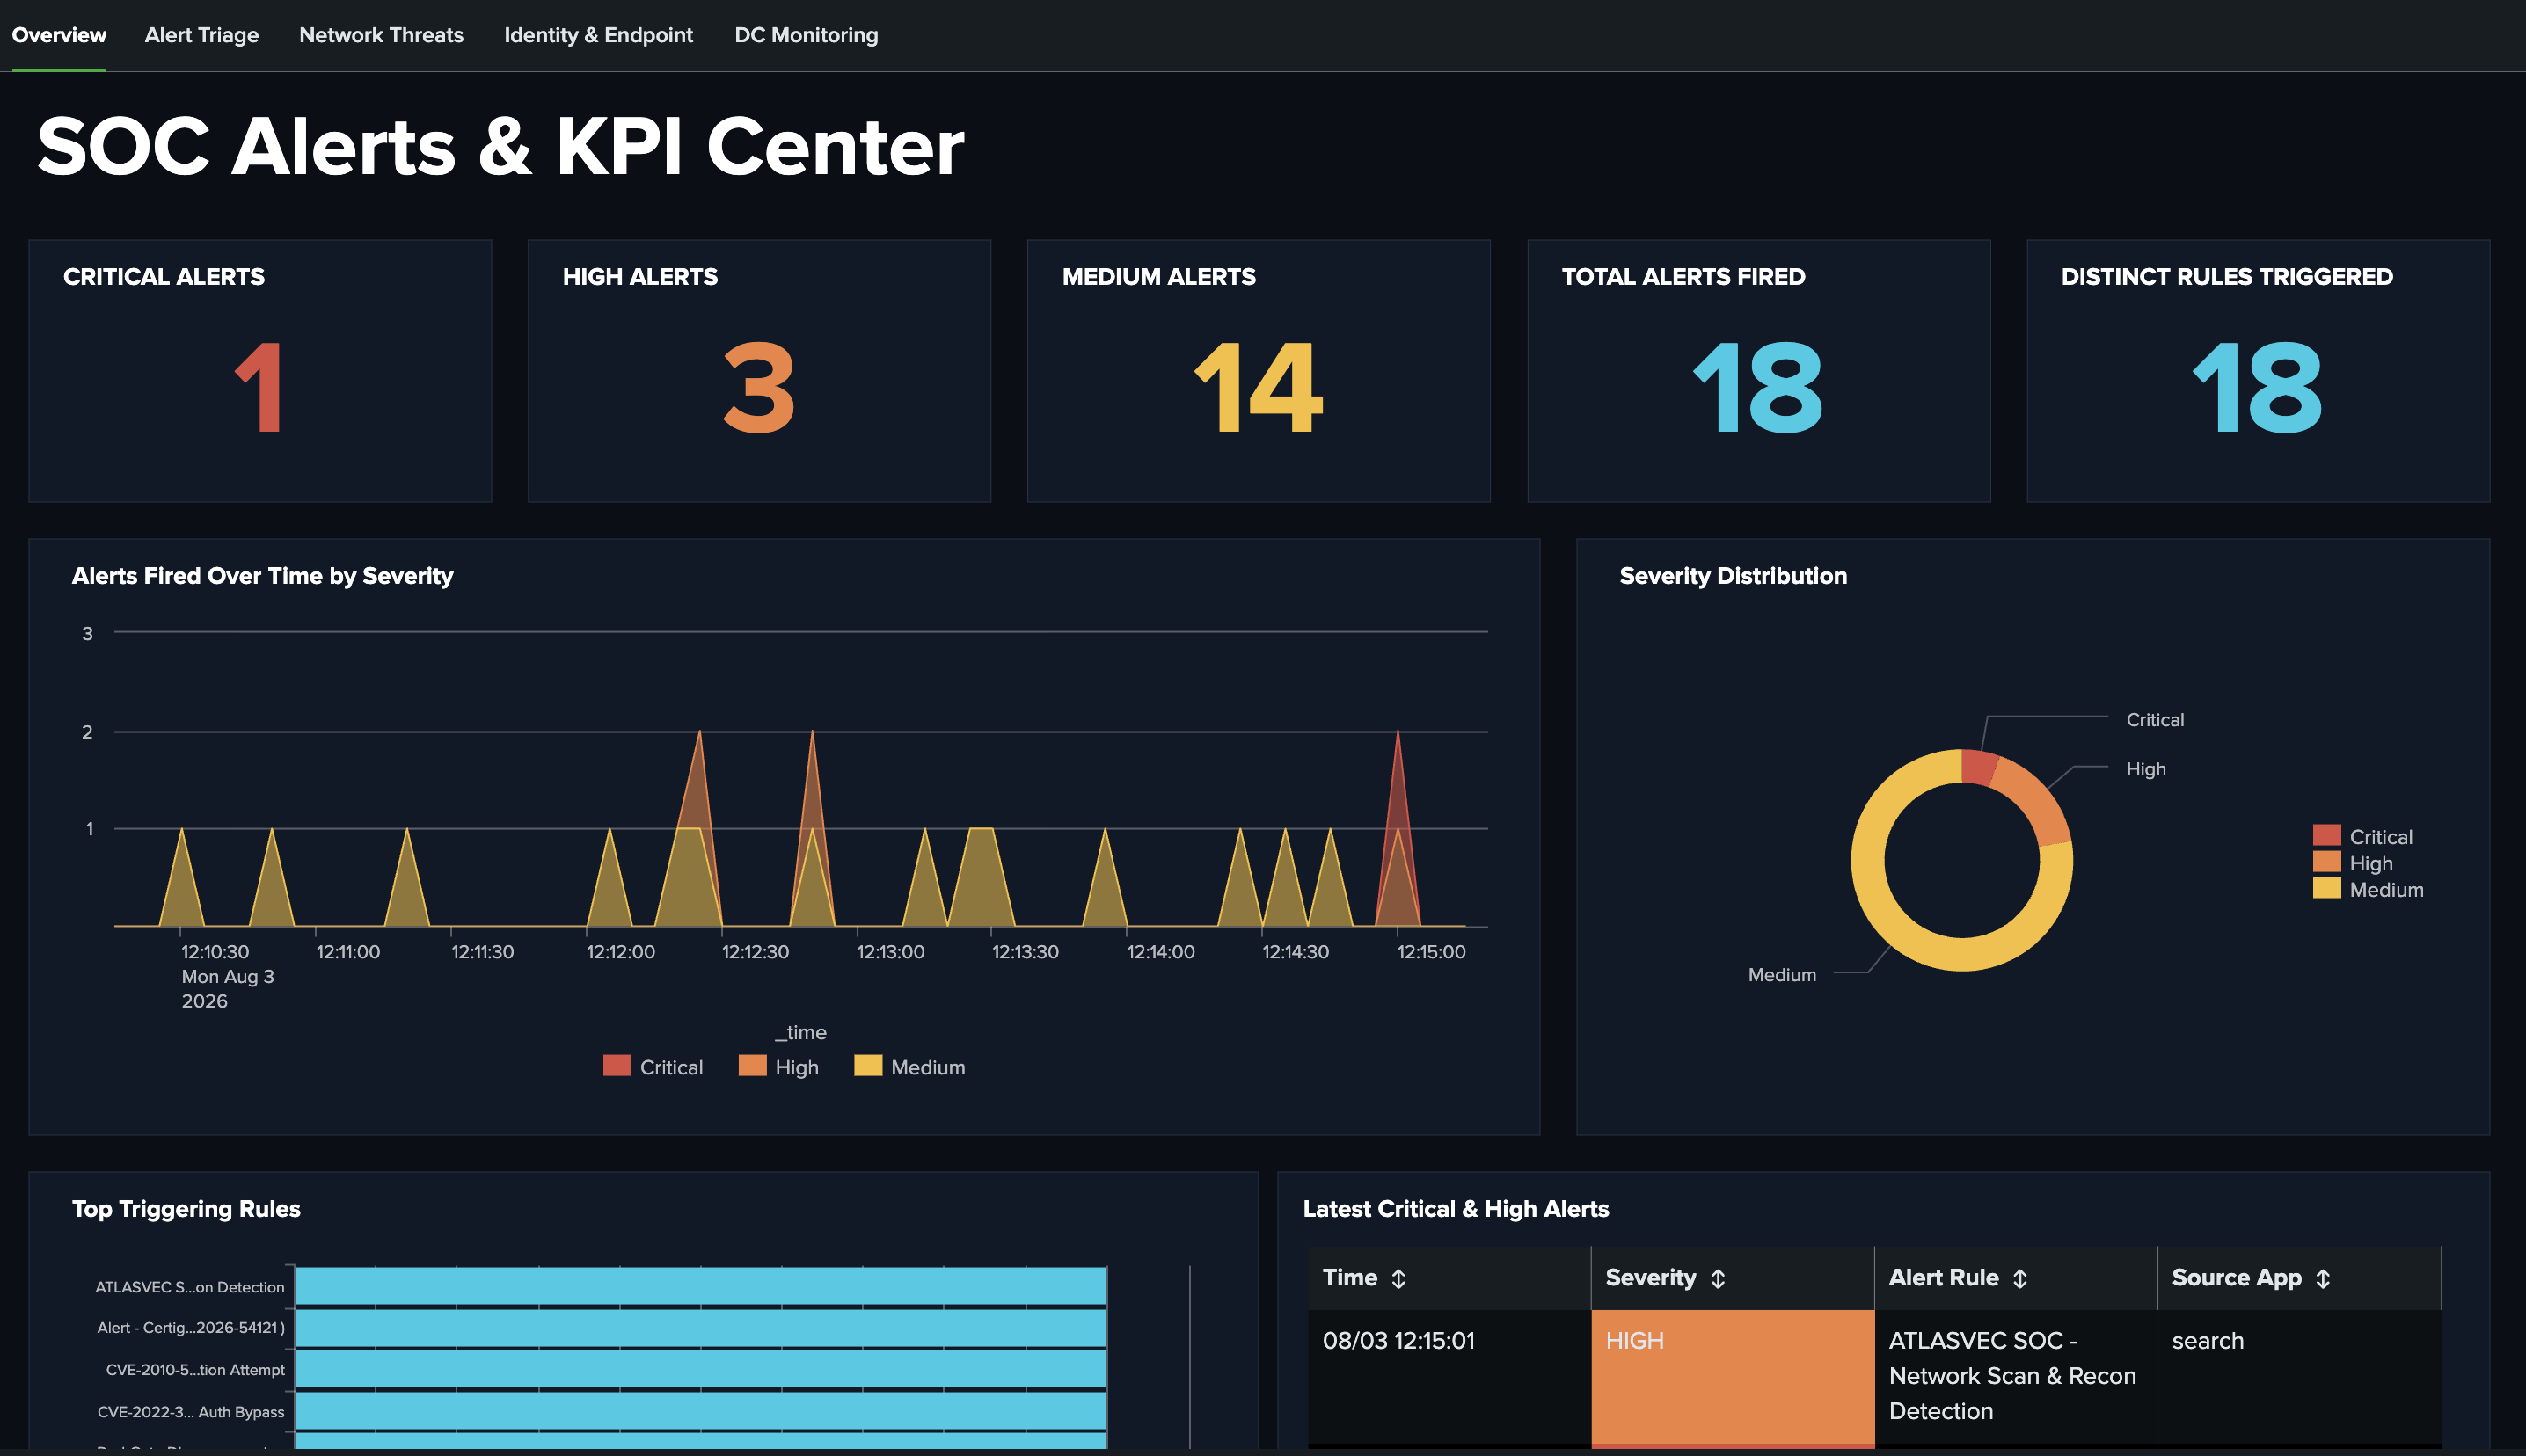 atlasvector/certighost-cve-2026-54121
Splunk detection writeup for CVE-2026-54121 (CertiGhost): AD CS certificate chase abuse leading to full domain compromise. Lab-validated detection,…
 jdormannn/secureops-lab
Performed a live cybersecurity assessment on a university Linux server. During analysis, active attack activity was identified, including brute-force…
 intezer/linux-explorer
Easy-to-use live forensics toolbox for Linux endpoints
 mandiant/citrix-ioc-scanner-cve-2023-3519
Bash-based scanner detecting indicators of compromise from CVE-2023-3519 exploitation on Citrix ADC appliances, supporting live and forensic image…
 kubeshark/kubeshark
eBPF-powered network observability for Kubernetes. Indexes L4/L7 traffic with full K8s context, decrypts TLS without keys. Queryable by AI agents via…
 tsale/awesome-dfir-skills
A curated collection of DFIR skills and workflows for InfoSec practitioners.
 cynative/cynative
Read-only AI agent that queries your cloud, code, and runtime infrastructure to surface misconfigurations, leaked secrets, and privilege escalation…
 withsecurelabs/linuxcatscale
Incident Response collection and processing scripts with automated reporting scripts
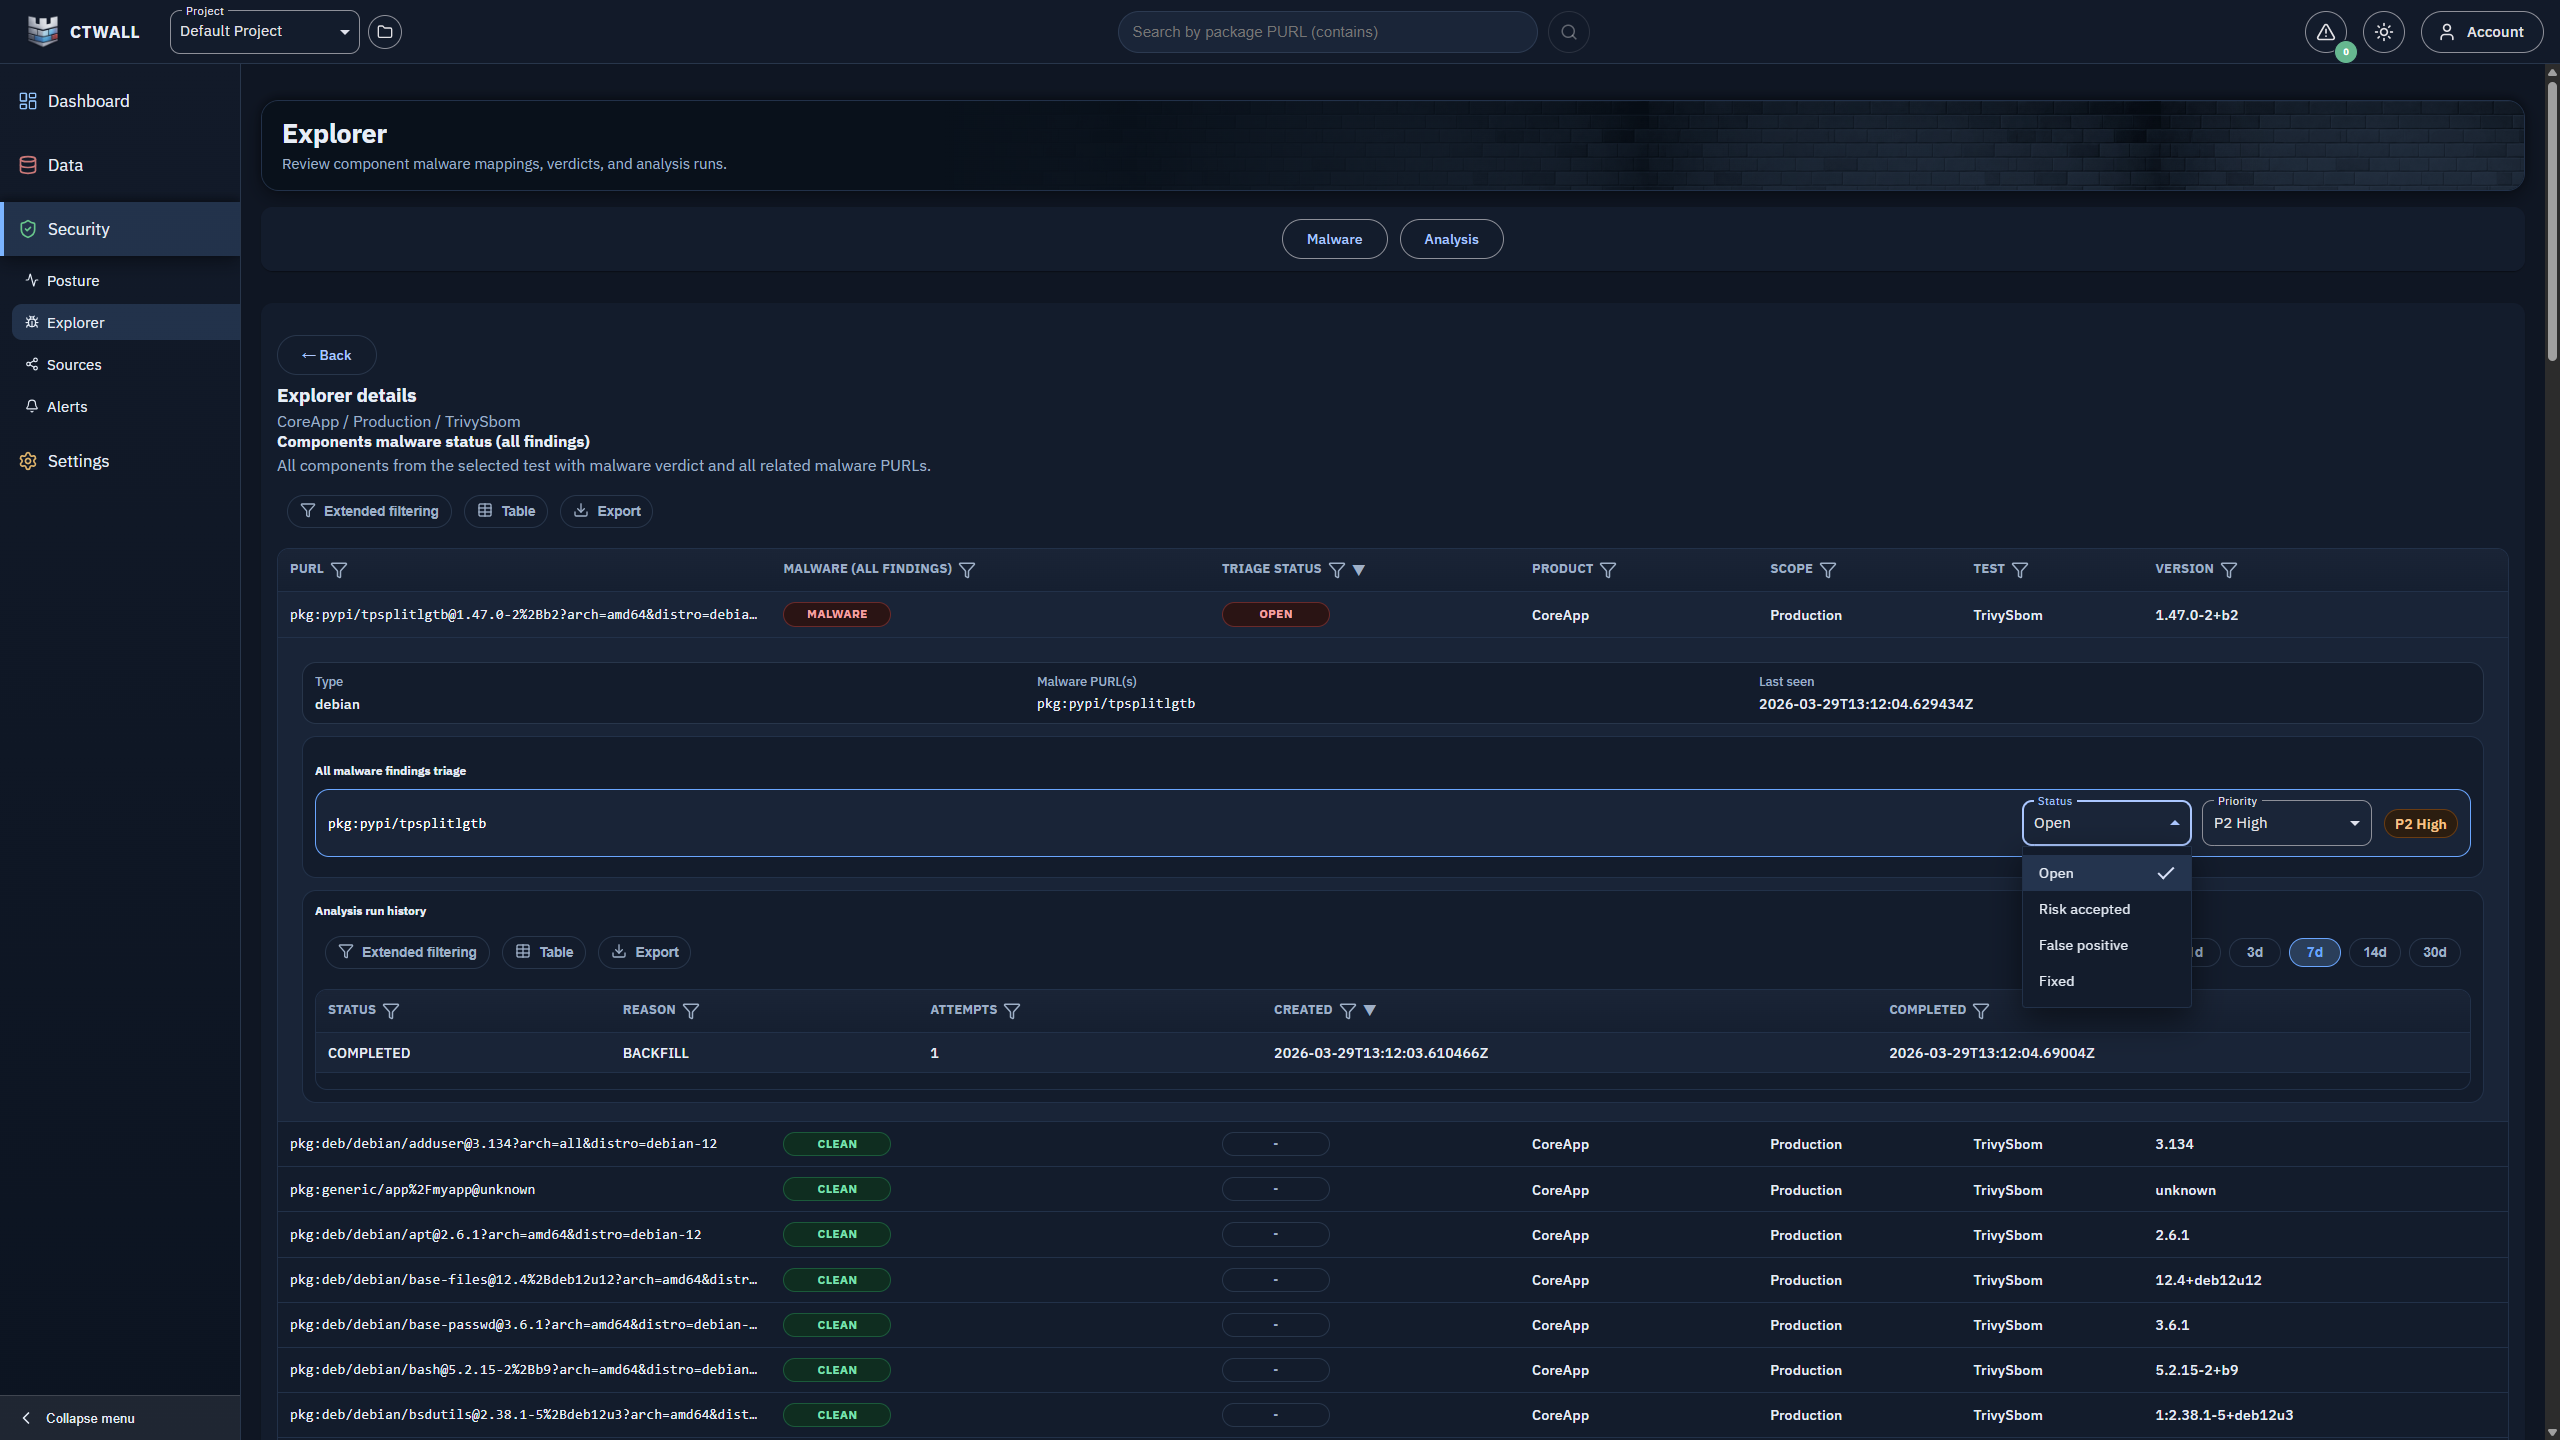 cybergabisoft/ctwall
CTWall (ChainThreatWall) platform helps Security, DevOps, and Product teams make risk decisions faster by using SBOM/BOM data to identify malware in…