

honeypot-data
 0x4d31/honeypot-data
Public honeypot datasets and observation reports with HTTP/TLS fingerprint data (JA3/JA4), pseudonymized source IPs, and exploitation attempt…
incident-responseinformation-gatheringioc-management+4
44
0x4d31/honeypot-dataPublic honeypot datasets and observation reports with HTTP/TLS fingerprint data (JA3/JA4), pseudonymized source IPs, and exploitation attempt…
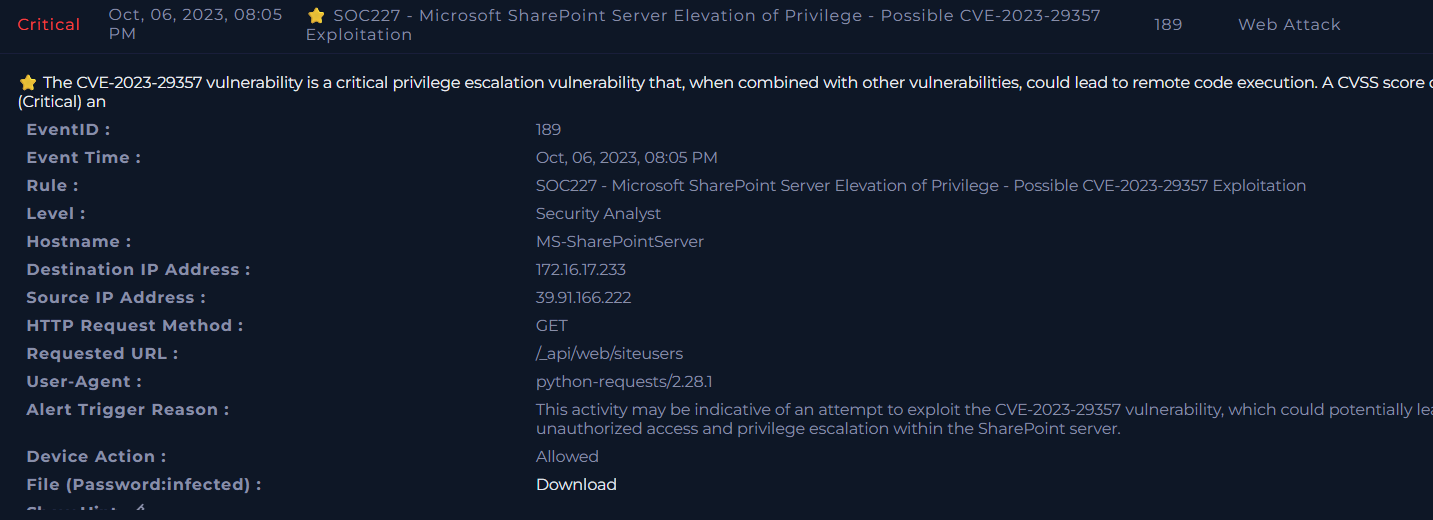 zedocun/sharepoint-cve-2023-29375-incident-response
End-to-end SOC incident analysis and threat hunting playbook targeting Microsoft SharePoint privilege escalation (CVE-2023-29357) using SIEM logs,…
 d3lightfu1/quietphase
Pwsh tool for AD Group Enumeration Auditing
 necr00/credential-hunting
CredsHunter - Credential Hunting scripts for Windows and Linux OS
 backbay-labs/thrunt-god
Threat hunting command system for agentic IDEs
 grayxploit/cve-2026-0257
Automated vulnerability scanner for CVE-2026-0257 (PAN-OS GlobalProtect Authentication Bypass) with TLS certificate enumeration, authentication…
 certtools/intelmq
IntelMQ is a solution for IT security teams for collecting and processing security feeds using a message queuing protocol.
 rootly-ai-labs/rootly-graphify-importer
Turn Rootly incidents, alerts, and teams into a queryable knowledge graph. Visualize service dependencies, on-call coverage gaps, and cross-incident…
 lsecqt/sessionview
A portable C# utility for enumerating local and remote windows sessions
 shadowguardai/ti-a-ti-cveexploitchecker
Determines if public exploits are available for a given CVE. Uses APIs like exploit-db or NVD to ide
 zdhenard42/soc-multitool
A powerful and user-friendly browser extension that streamlines investigations for security professionals.
 niklasmato/fortileak-01-2025-be
This repository contains informaion about the Fortigate firewall vulnerability (CVE-2022-40684) and affected data that were publicly disclosed by the…
 zomato/vinifera
A GitHub recon/monitoring tool for finding internal leaks belonging to your organisation.
 defensepointsecurity/threat_note
DPS' Lightweight Investigation Notebook
 pascalasch/cve-2023-38831-kql
KQL Hunting for WinRAR CVE-2023-38831
 adityaks/melee
Python-based tool to detect ransomware infections and malicious code in MySQL instances. Performs reconnaissance, user enumeration, and deep scans…
 kaansk/shomon
Shodan Monitoring integration for TheHive.
 nccgroup/detectwindowscopyonwriteforapi
Enumerate various traits from Windows processes as an aid to threat hunting