cve_2026_98432_guard

Temporary eBPF/XDP mitigation for CVE-2026-98432 Linux TCP IPv4 header-options vulnerability. Helps protect unpatched systems and custom kernels…

Temporary eBPF/XDP mitigation for CVE-2026-98432 Linux TCP IPv4 header-options vulnerability. Helps protect unpatched systems and custom kernels…

Self-hosted multi-engine Sigma detection for event logs

Automated forensic analysis tool for Google Workspace audit logs. Acquires all log types, maps events to MITRE ATT&CK Cloud Framework, and identifies…

Low-resource honeypot that emulates common network services to detect post-breach attacker activity, with extensible protocol modules and…

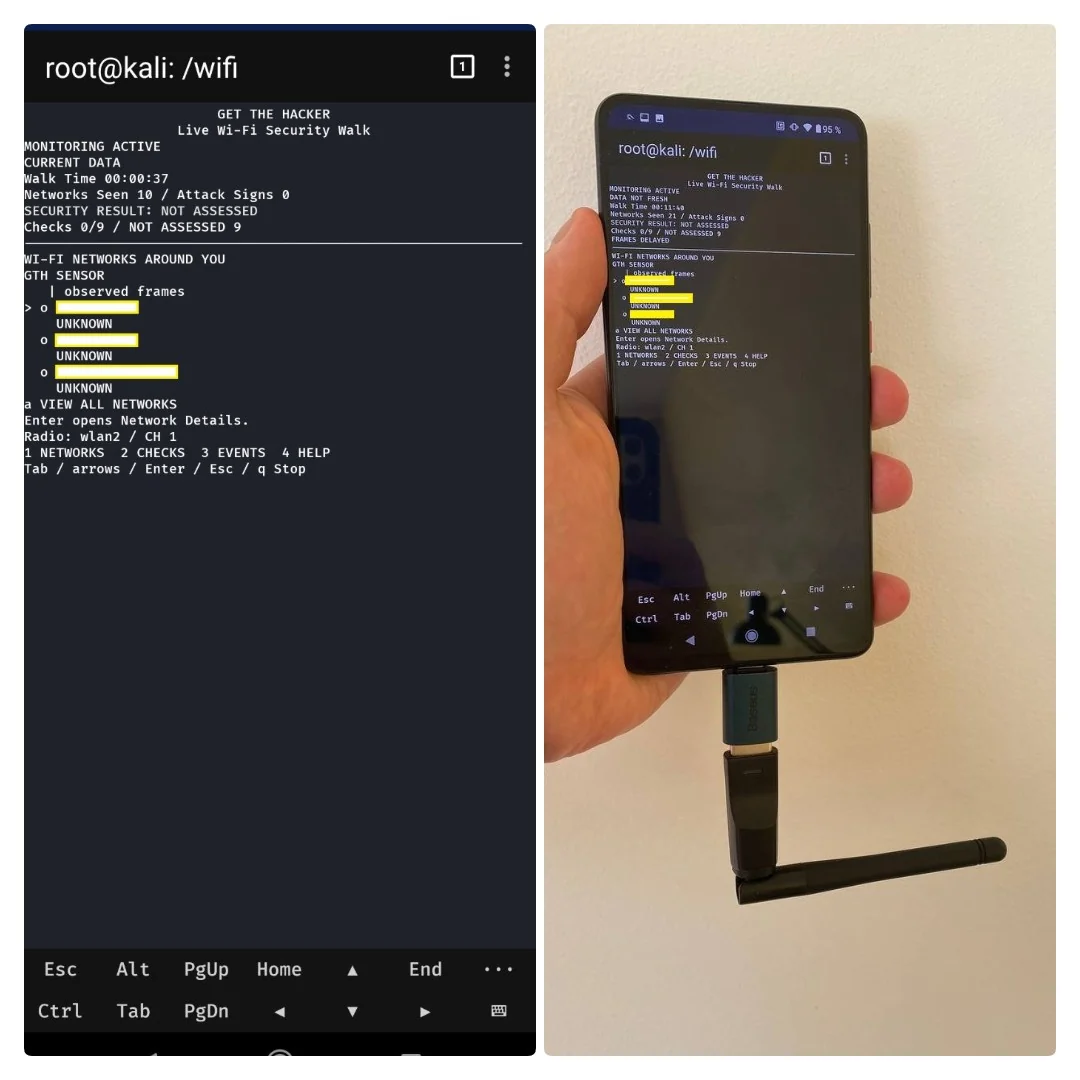
Hunt WiFi threats silently. Catch the hackers.

Hardened Debian-based privacy OS with pre-integrated anonymity stack (Tor, VPN, DNSCrypt), anti-forensic tooling, SOC security center, and standalone…

Archived, moved to codesource/cve-check. Shell script to detect CVE-2026-31431 (Copy Fail) exposure and mitigations on Linux systems: kernel check,…

Docker configuration to quickly setup your own Canarytokens.

Self-contained SSH honeypot for capturing attacker interactions and turning them into structured security intelligence.

Scripts to triage compromised systems (Linux, ESXi, FreeBSD/NetScaler)

A repository of sysmon configuration modules

Exploit and detect CVE-2026-31431 vulnerabilities using a static binary that monitors system integrity and bypasses PAM authentication.

Open-source cybersecurity knowledge base with 400+ notes, labs, and cheat sheets covering offense, defense, cryptography, cloud, and forensics.

Portable, dependency-free incident response tool that automates forensic artifact collection from Unix-like systems, including memory acquisition,…

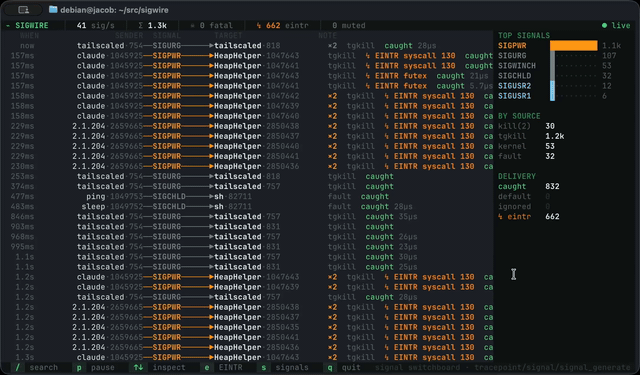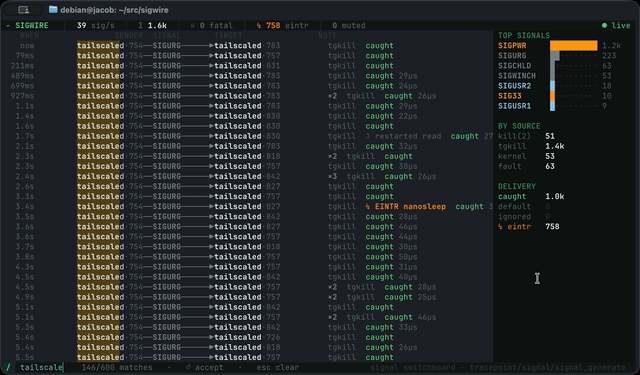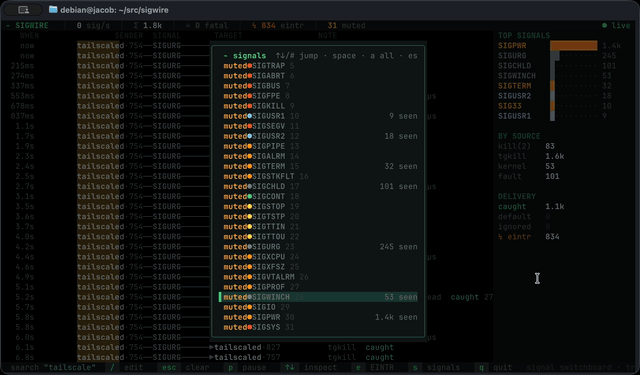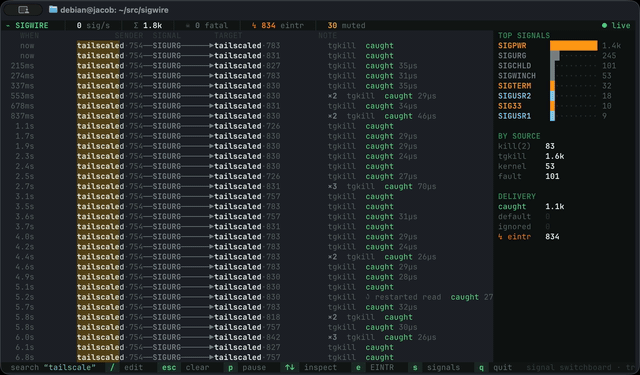
Live kernel signal observability tool using eBPF tracepoints to stream every signal raised on a Linux host, showing sender, target, disposition,…

Curated collection of 200+ cybersecurity interview questions and answers covering Red Team, Blue Team, Web Security, Incident Response, and network…

Technical dossier on the DPRK-linked PolinRider supply-chain attack, documenting obfuscated JS payload injection, git history manipulation, C2…