

Live-Forensicator
 johnng007/live-forensicator
Cross-platform incident response and live forensic artifact collector with built-in detection, structured analysis, and report generation — designed…
incident-response
johnng007/live-forensicatorCross-platform incident response and live forensic artifact collector with built-in detection, structured analysis, and report generation — designed…
 stackrox/stackrox
The StackRox Kubernetes Security Platform performs a risk analysis of the container environment, delivers visibility and runtime alerts, and provides…
 fleetdm/fleet
Open-source platform to secure and manage endpoints via MDM, patch management, software deployment, and osquery-powered visibility with compliance…
 intuitem/ciso-assistant-community
GRC platform for risk management, compliance, and audit with 200+ frameworks, automatic control mapping, vulnerability management, and incident…
 pnwcomputers/ultimate-cybersecurity-master-guide
This repository provides a centralized resource for operational cyber defense and offense, compiling Theory, Tools, Operating Procedures, and…
 a2awais/threat-hunting
Curated collection of threat hunting and detection queries for CrowdStrike Falcon (CQL) and Microsoft Defender XDR (KQL), mapped to MITRE ATT&CK…
 graylog2/graylog2-server
Centralized log management platform for collecting, indexing, and analyzing streaming logs, with alerting and event correlation for security…
 google/timesketch
Collaborative forensic timeline analysis platform for ingesting, searching, and annotating event logs to support incident response and DFIR…

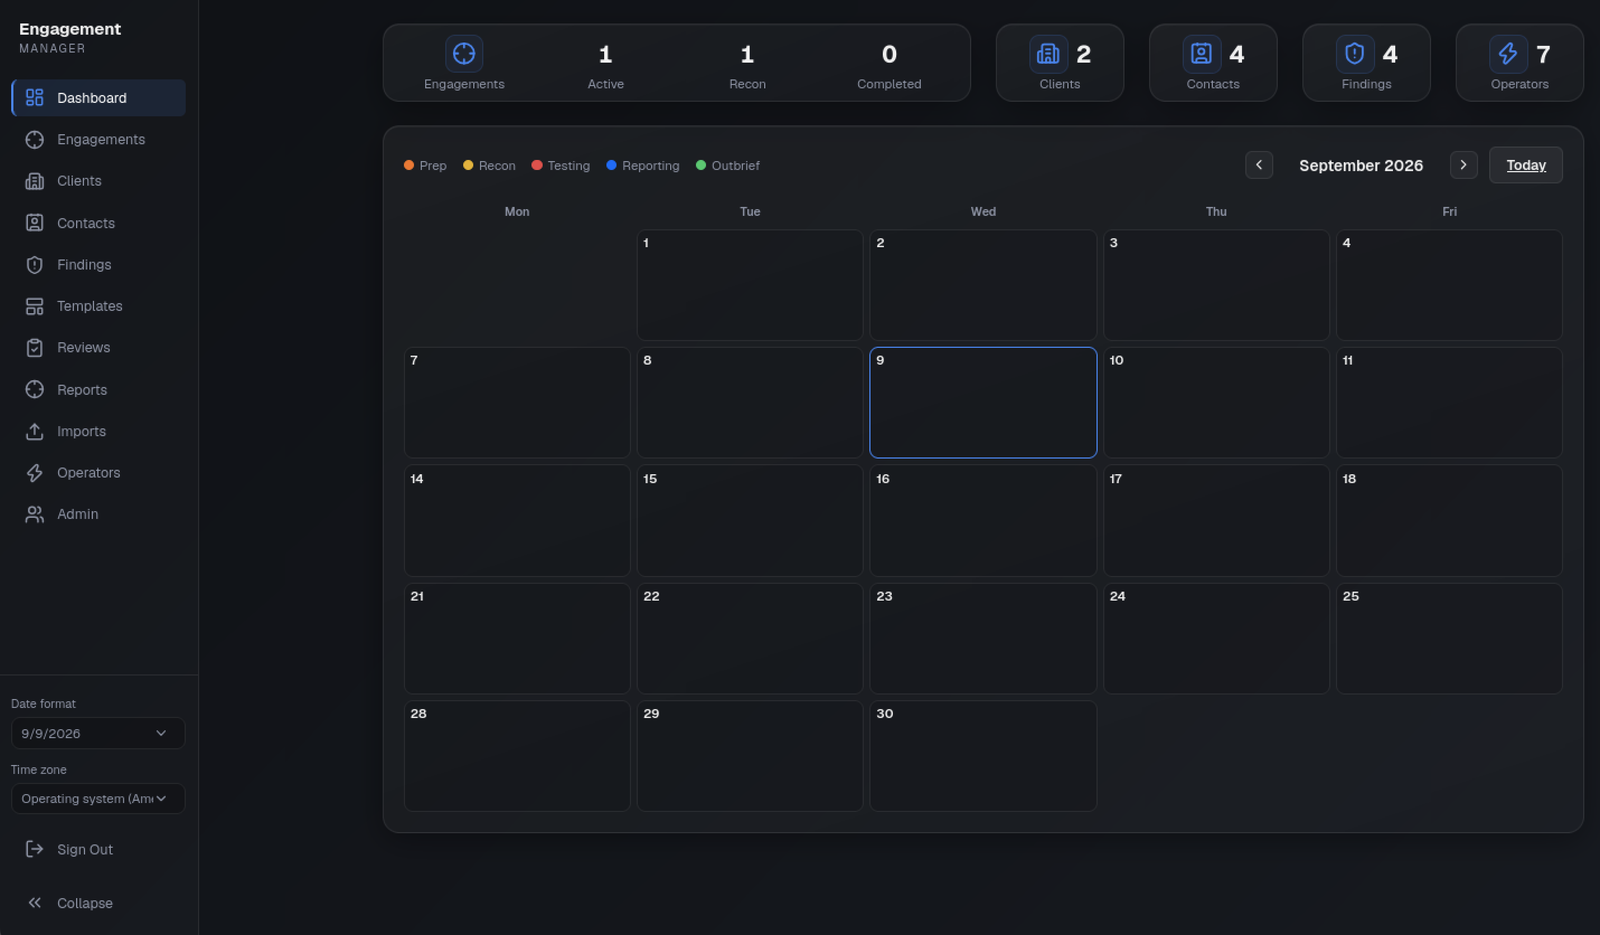 leebaird/engagement-mgr
Engagement Manager is a web application for tracking offensive security engagements. It features a modern UI, built with Next.js, Prisma, and…
 opencve/opencve
Aggregate, filter, and track CVEs from multiple sources with team collaboration, custom dashboards, alerts, and AI-powered analysis for vulnerability…
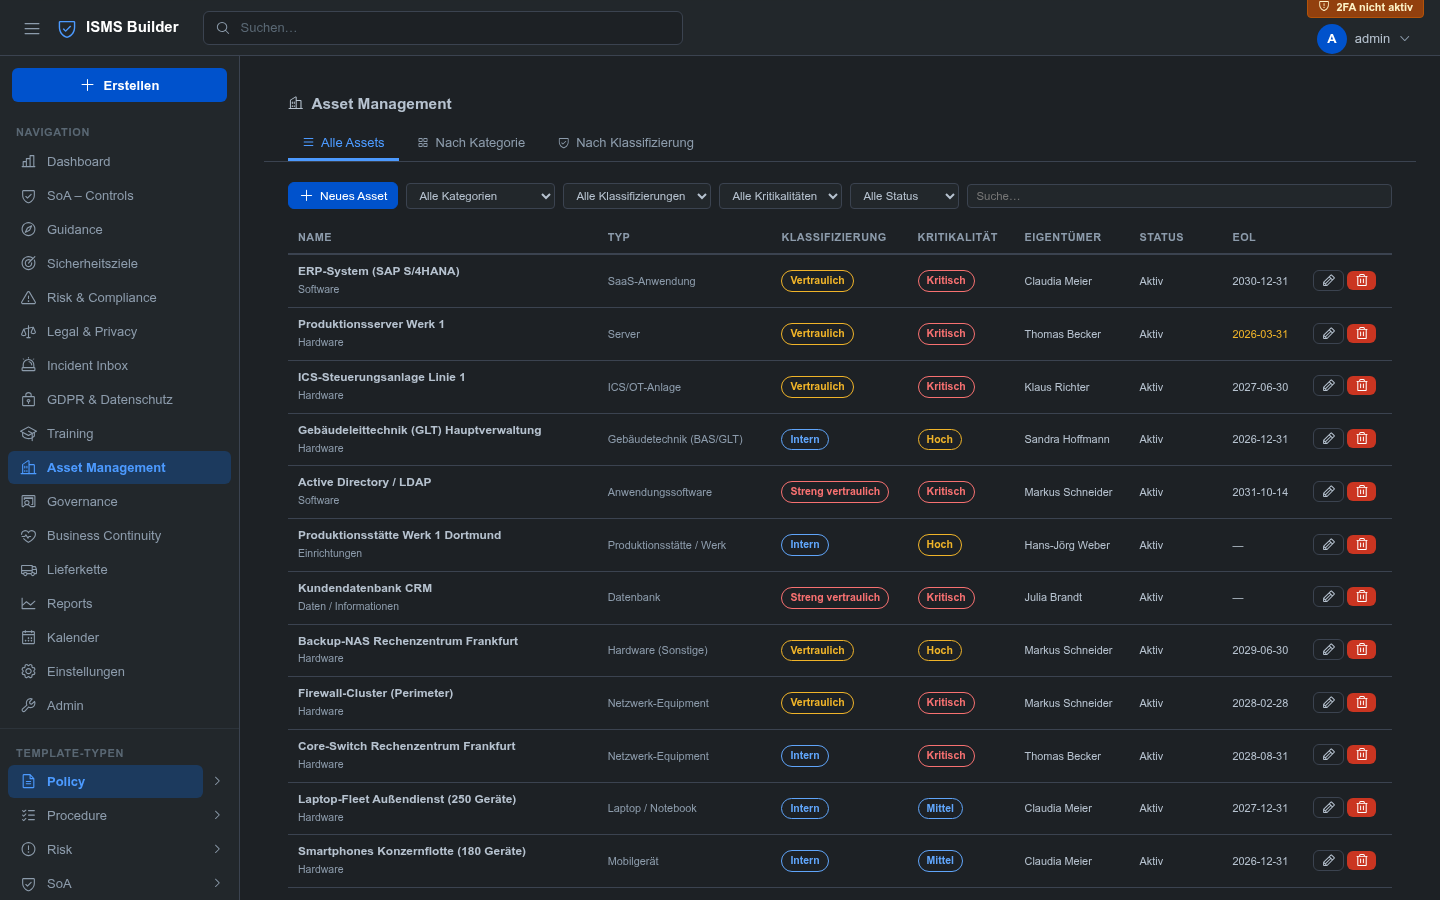 coolstartnow/isms-builder
Self-hosted Information Security Management System — ISO 27001, NIS2, GDPR/DSGVO, BSI IT-Grundschutz
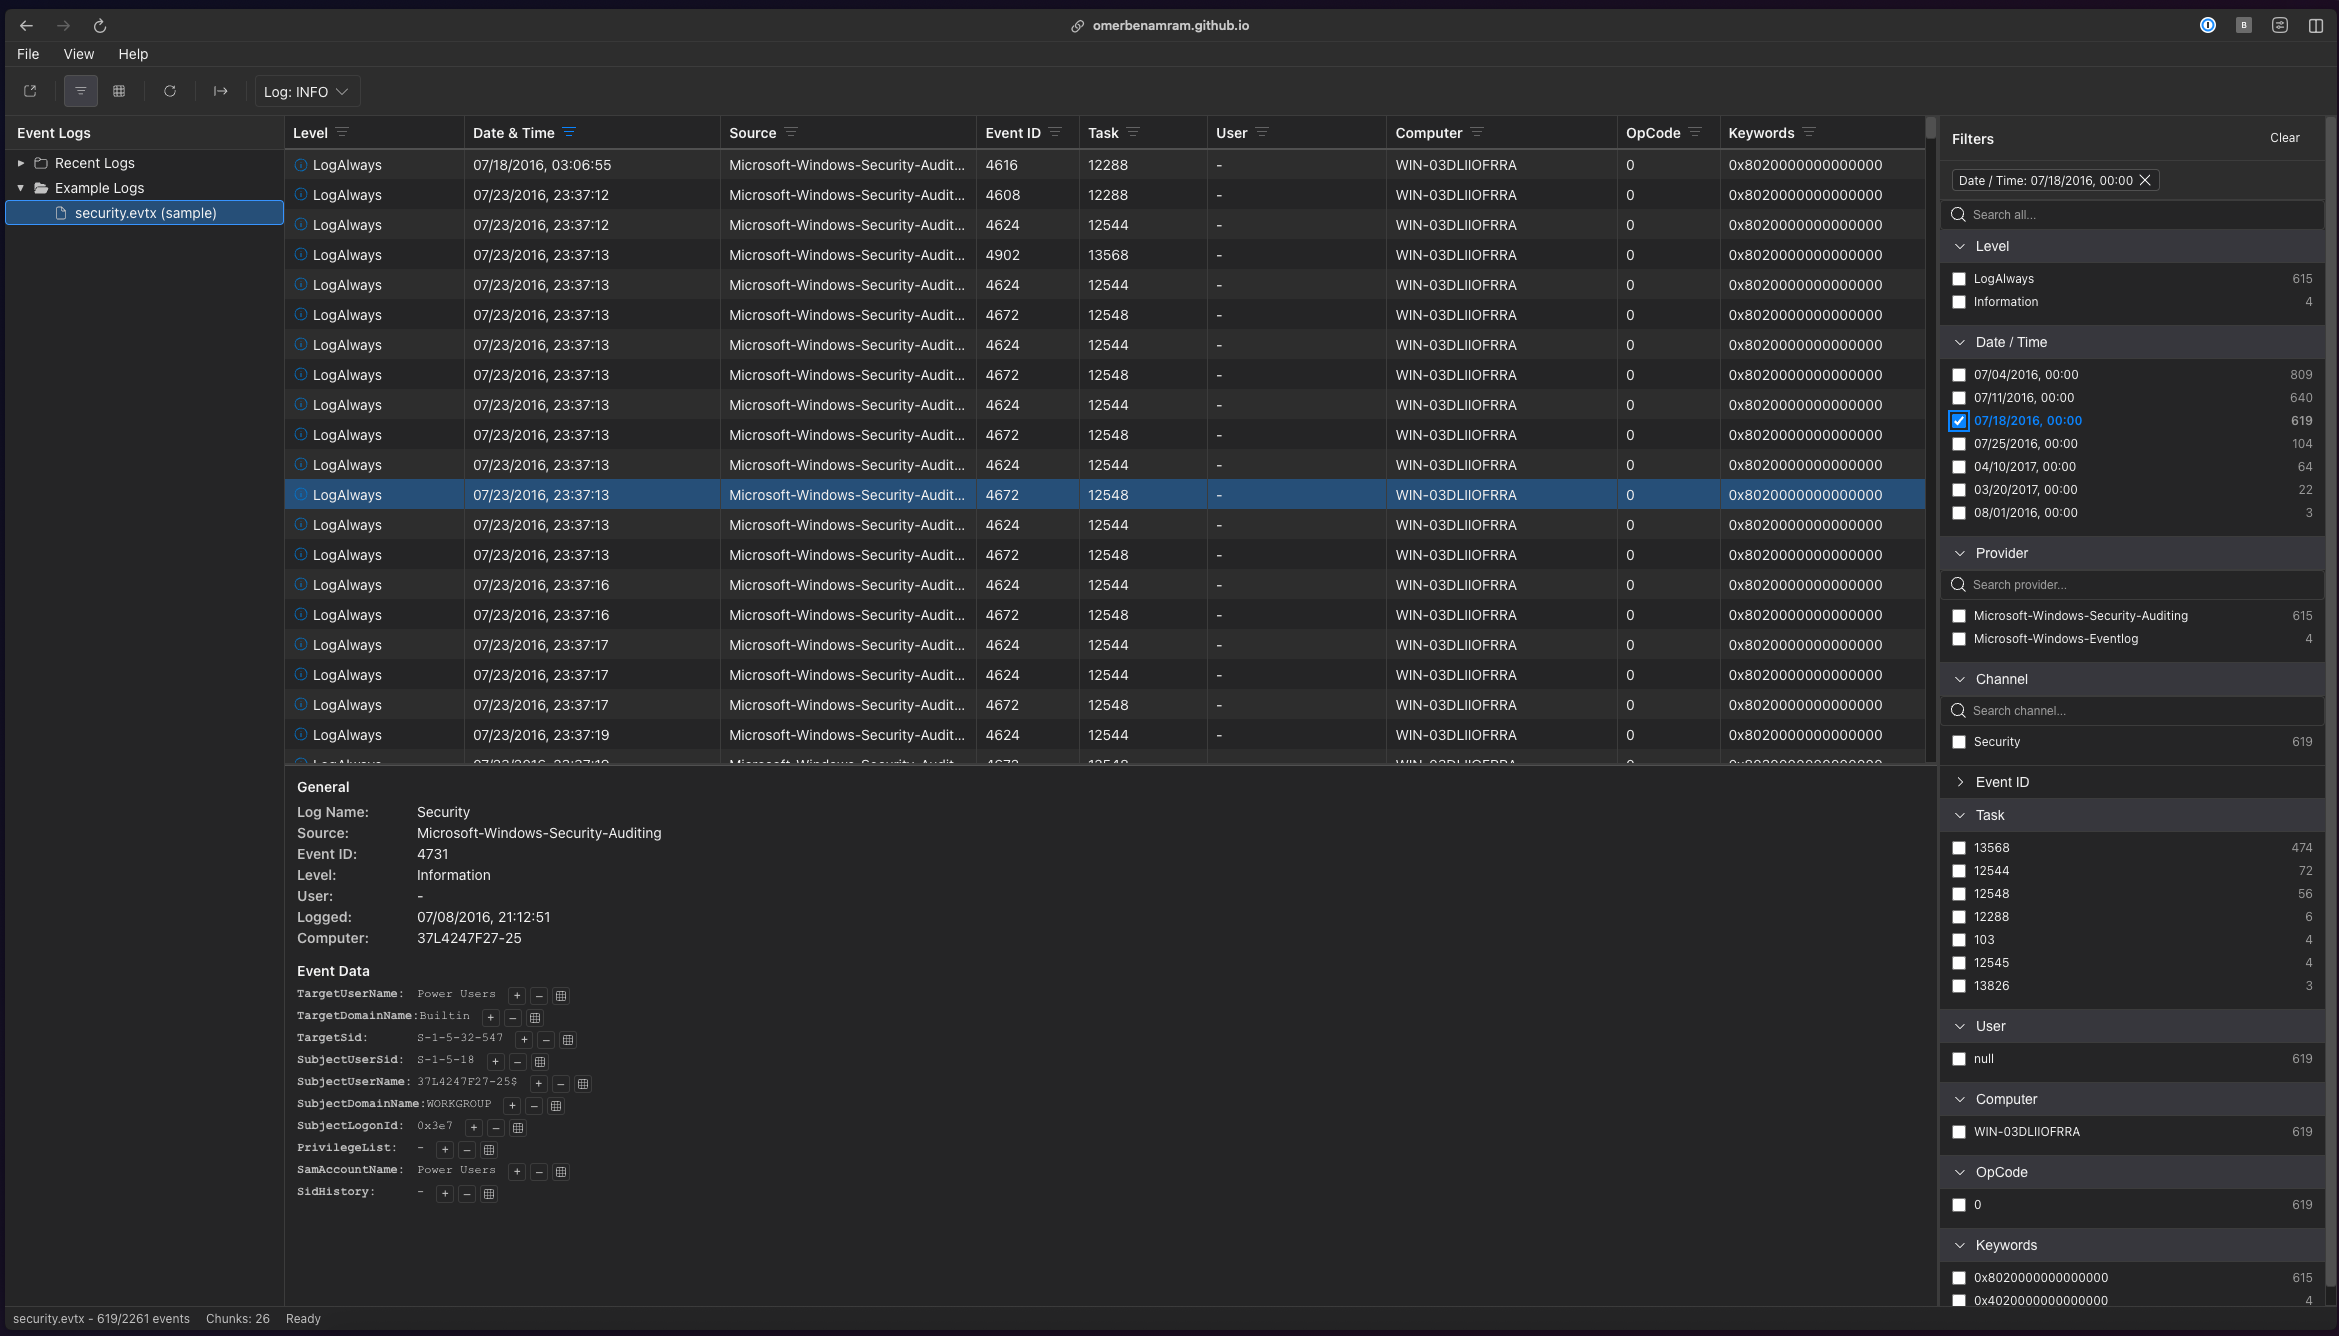 omerbenamram/evtx
A Fast (and safe) parser for the Windows XML Event Log (EVTX) format
 wazuh/wazuh
Open-source XDR and SIEM platform for threat detection, log analysis, file integrity monitoring, vulnerability assessment, and compliance management…
 nebulock-inc/agentic-threat-hunting-framework
ATHF is a framework for agentic threat hunting - building systems that can remember, learn, and act with increasing autonomy.
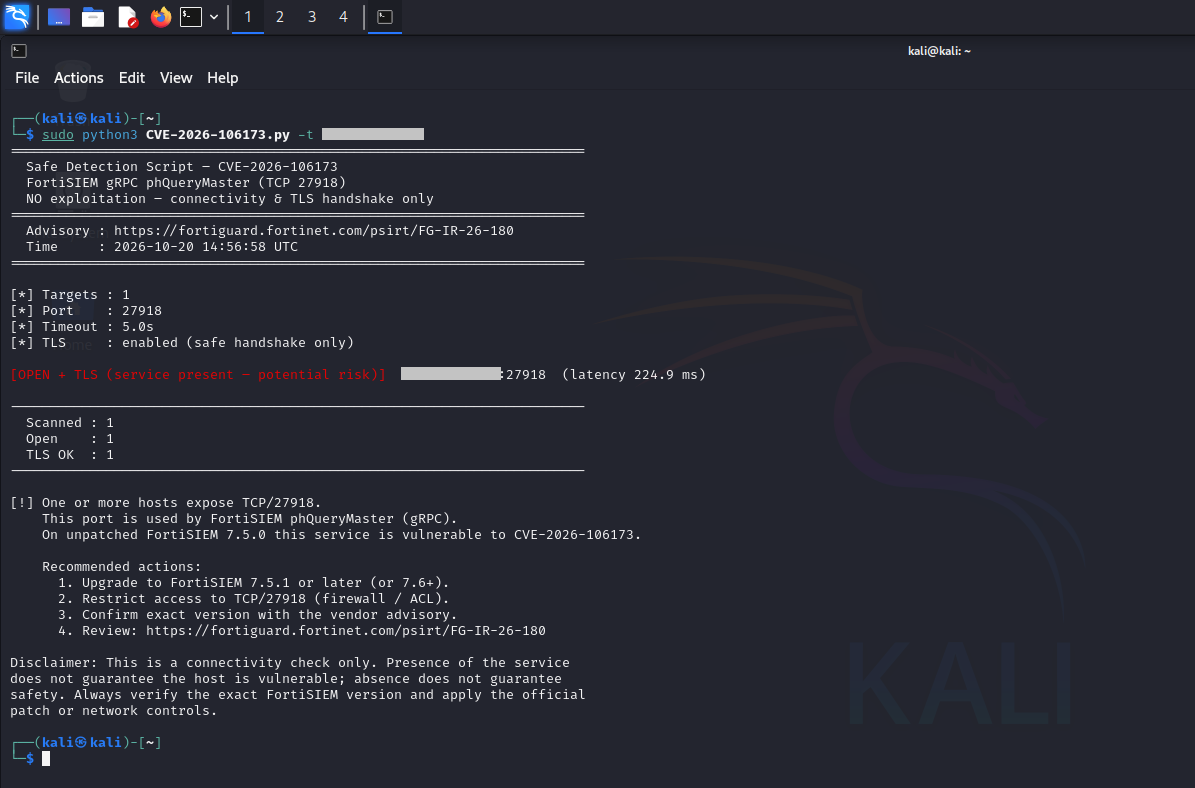 0xblackash/cve-2026-106173
Documents CVE-2026-106173, a path traversal (CWE-22) in Fortinet FortiSIEM, with impact analysis, detection guidance, and mitigation steps for…
 wagga40/zircolite
A standalone SIGMA-based detection tool for EVTX, Auditd and Sysmon for Linux logs