
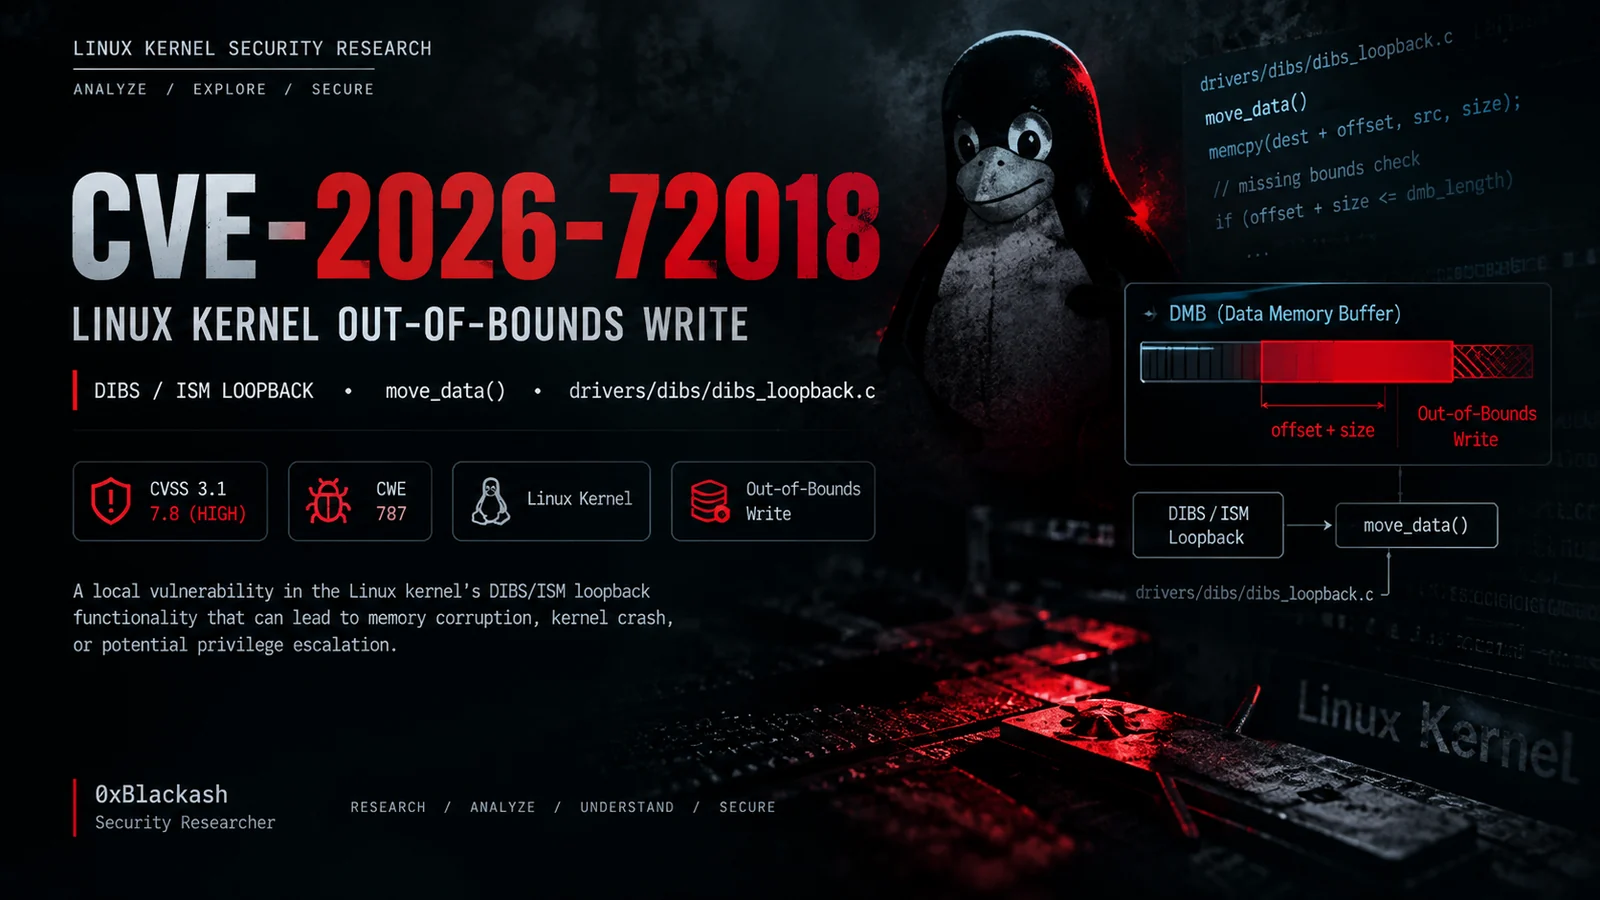
CVE-2026-72018
 0xblackash/cve-2026-72018
Technical analysis of CVE-2026-72018, a Linux kernel out-of-bounds write in DIBS/ISM loopback, covering root cause, affected versions, detection, and…
binary-exploitationdefensive-toolseducation+4
0xblackash/cve-2026-72018Technical analysis of CVE-2026-72018, a Linux kernel out-of-bounds write in DIBS/ISM loopback, covering root cause, affected versions, detection, and…
 devinblack001/ddos-reduction-system
Adaptive two-stage Layer 4 DDoS mitigation gateway using behavioral traffic analysis, Random Forest classification, and kernel-level ipset/iptables…
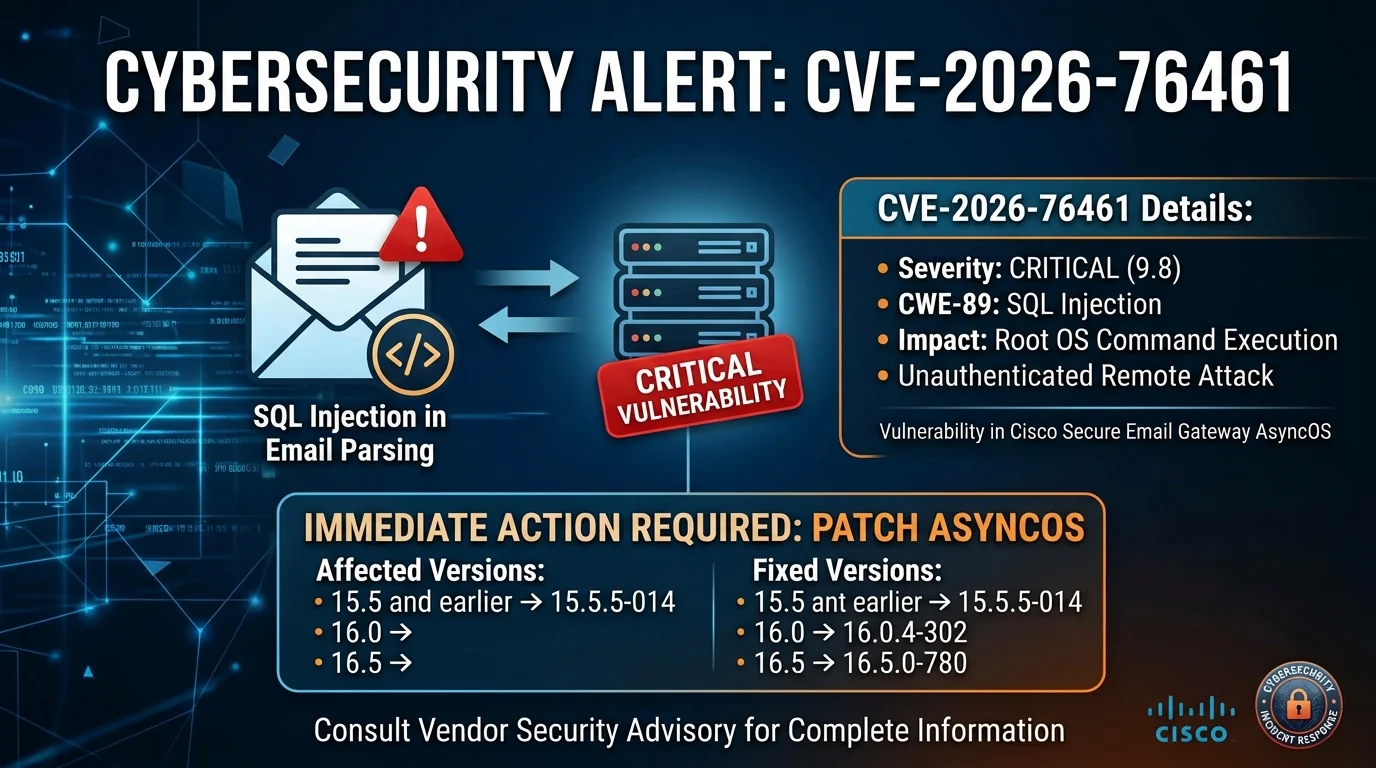 0xblackash/cve-2026-76461
Research repository for CVE-2026-76461, a critical SQL injection in Cisco Secure Email Gateway leading to root RCE, with detection rules, mitigation…
 jithinkrishnanrs/cve-2026-67401-cpanel-emailtrack-sqli
Read-only IOC scanner and mitigation toolkit for cPanel & WHM EmailTrack SQL injection (CVE-2026-67401). Performs version fingerprinting, file…
 zhoucc-cpu/cve-2023-23397-detection-lab
Detection and mitigation research lab for CVE-2023-23397 using network and endpoint security telemetry.
 juliosuas/copyfail-guard
Fast, auditable Linux mitigation for CVE-2026-31431 Copy Fail: algif_aead block, verification, and AF_ALG seccomp hardening.
 execution-py/cve-2026-9055
Defensive analysis of CVE-2026-9055, an unauthenticated privilege escalation in Amelia WordPress booking plugin. Provides root cause breakdown,…
 jwa7470/2025-oracle-sso-ldap-attack-post-incident-written-report
Post-incident report analyzing the Oracle Cloud SSO/LDAP supply chain attack (CVE-2021-35587). Details the exploitation of legacy server…
 kaleth4/cve-2026-64638
Technical analysis and defensive mitigation for a WordPress Core pre-auth XSS-to-RCE chain, including sanitizer bypass, DOM clobbering, JSONP abuse,…
 velessecurity/cve-2021-1675-printnightmare-analysis
Technical write-up and analysis of PrintNightmare (CVE-2021-1675 / CVE-2021-34527), covering RCE/LPE exploitation, detection via Windows event logs,…
 h4cknain/cve-2024-21413-microsoft-outlook-moniker-link-vulnerability
Lab write-up analyzing CVE-2024-21413 Outlook Moniker Link exploitation, NetNTLMv2 credential leakage via SMB, detection with YARA/Wireshark, and…
 joaocalciolari07/copyfail-guard
Defensive detection & mitigation tool for CVE-2026-31431 ("Copy Fail") — Linux kernel algif_aead LPE. No exploit code included.
 karitamw/printnightmare-detection-mitigation-lab
Sanitised Windows security lab demonstrating Active Directory administration, host and network detection, and layered mitigation of CVE-2021-34527.
 sana-404/cve-2026-8838-mitigation-and-detection
Detection and mitigation scripts for CVE-2026-8838, providing vulnerability scanning, configuration auditing, and incident response guidance to…
 sana-404/cve-2026-8388-mitigation-and-detection
Provides mitigation and detection guidance for CVE-2026-8388, including indicators of compromise and remediation steps for security teams.
 anuththara2007-w/cve-2026-20127-exploit-extension
Offline browser extension providing defensive analysis and detection guidance for CVE-2026-20127, with packet visualization, IOC extraction, and…
 sf0rzin/cve-2025-61155
CVE-2025-61155 — arbitrary process termination in GameDriverX64.sys (Tower of Fantasy anti-cheat). Original IDA Pro teardown, PoC, YARA, IOCs,…
 jihwan77/linux-kernel-copy-fail-cve-2026-31431-
Analysis and mitigation of Linux kernel Copy Fail (CVE-2026-31431) vulnerability exploiting AF_ALG/splice page cache mutation, with PoC checker,…