
wolf-tools
 rtkwlf/wolf-tools
Scans Windows, Linux, and macOS hosts for Java packages containing JndiLookup.class to detect Log4Shell (CVE-2021-44228, CVE-2021-45046) exposure and…
configuration-auditingdefensive-toolsincident-response+4
88
rtkwlf/wolf-toolsScans Windows, Linux, and macOS hosts for Java packages containing JndiLookup.class to detect Log4Shell (CVE-2021-44228, CVE-2021-45046) exposure and…
 mcpmark-eval-liuhezi/log4shell-audit
Log4Shell (CVE-2021-44228) security review documentation and advisory triage
 duyduongduyduong/cve-2021-36934-dll-hijacking-dfir-investigation
DFIR investigation resources for CVE-2021-36934, covering DLL hijacking, privilege-escalation detection, and forensic analysis of affected Windows…
 winnpixie/log4noshell
A Java Agent that disables Apache Log4J's JNDI Lookup to mitigate CVE-2021-44228 ("Log4Shell").
 joertx07/printnightmare-detection-lab
Splunk SIEM lab simulating and detecting CVE-2021-34527 (PrintNightmare) exploitation using Sysmon, Windows Event logs, and custom SPL detection…
 karitamw/printnightmare-detection-mitigation-lab
Sanitised Windows security lab demonstrating Active Directory administration, host and network detection, and layered mitigation of CVE-2021-34527.
 jomjosh17/log4shell-cve-2021-44228-
Comprehensive SOC analysis of Log4Shell (CVE-2021-44228) including technical breakdown, detection indicators, remediation strategies, and incident…
 felisha-elmer/sandbox-challenge-log4shell-cve-2021-44228-
Step-by-step walkthrough of the CISA Log4Shell sandbox challenge, covering offensive exploitation via Metasploit and defensive mitigation using a…
 stripe/log4j-remediation-tools
Tools for remediating the recent log4j2 RCE vulnerability (CVE-2021-44228)
 serpilrivas/log4shell-homework9
Log4Shell (CVE-2021-44228) exploit demo for SEAS 8405. Includes a vulnerable Spring Boot app, fake LDAP server, Docker setup, MITRE mapping, incident…
 0xsyr0/log4shell
This repository contains all gathered resources we used during our Incident Reponse on CVE-2021-44228 and CVE-2021-45046 aka Log4Shell.
 corelight/cve-2021-38647-noimages
Zeek package detecting CVE-2021-38647 (OMIGOD) exploit attempts by monitoring OMI/WMI traffic for missing Authorization headers and malicious SOAP…
 digital-dev/log4j-cve-2021-44228-remediation
This powershell script is intended to be used by anyone looking to remediate the Log4j Vulnerability within their environment. It can target multiple…
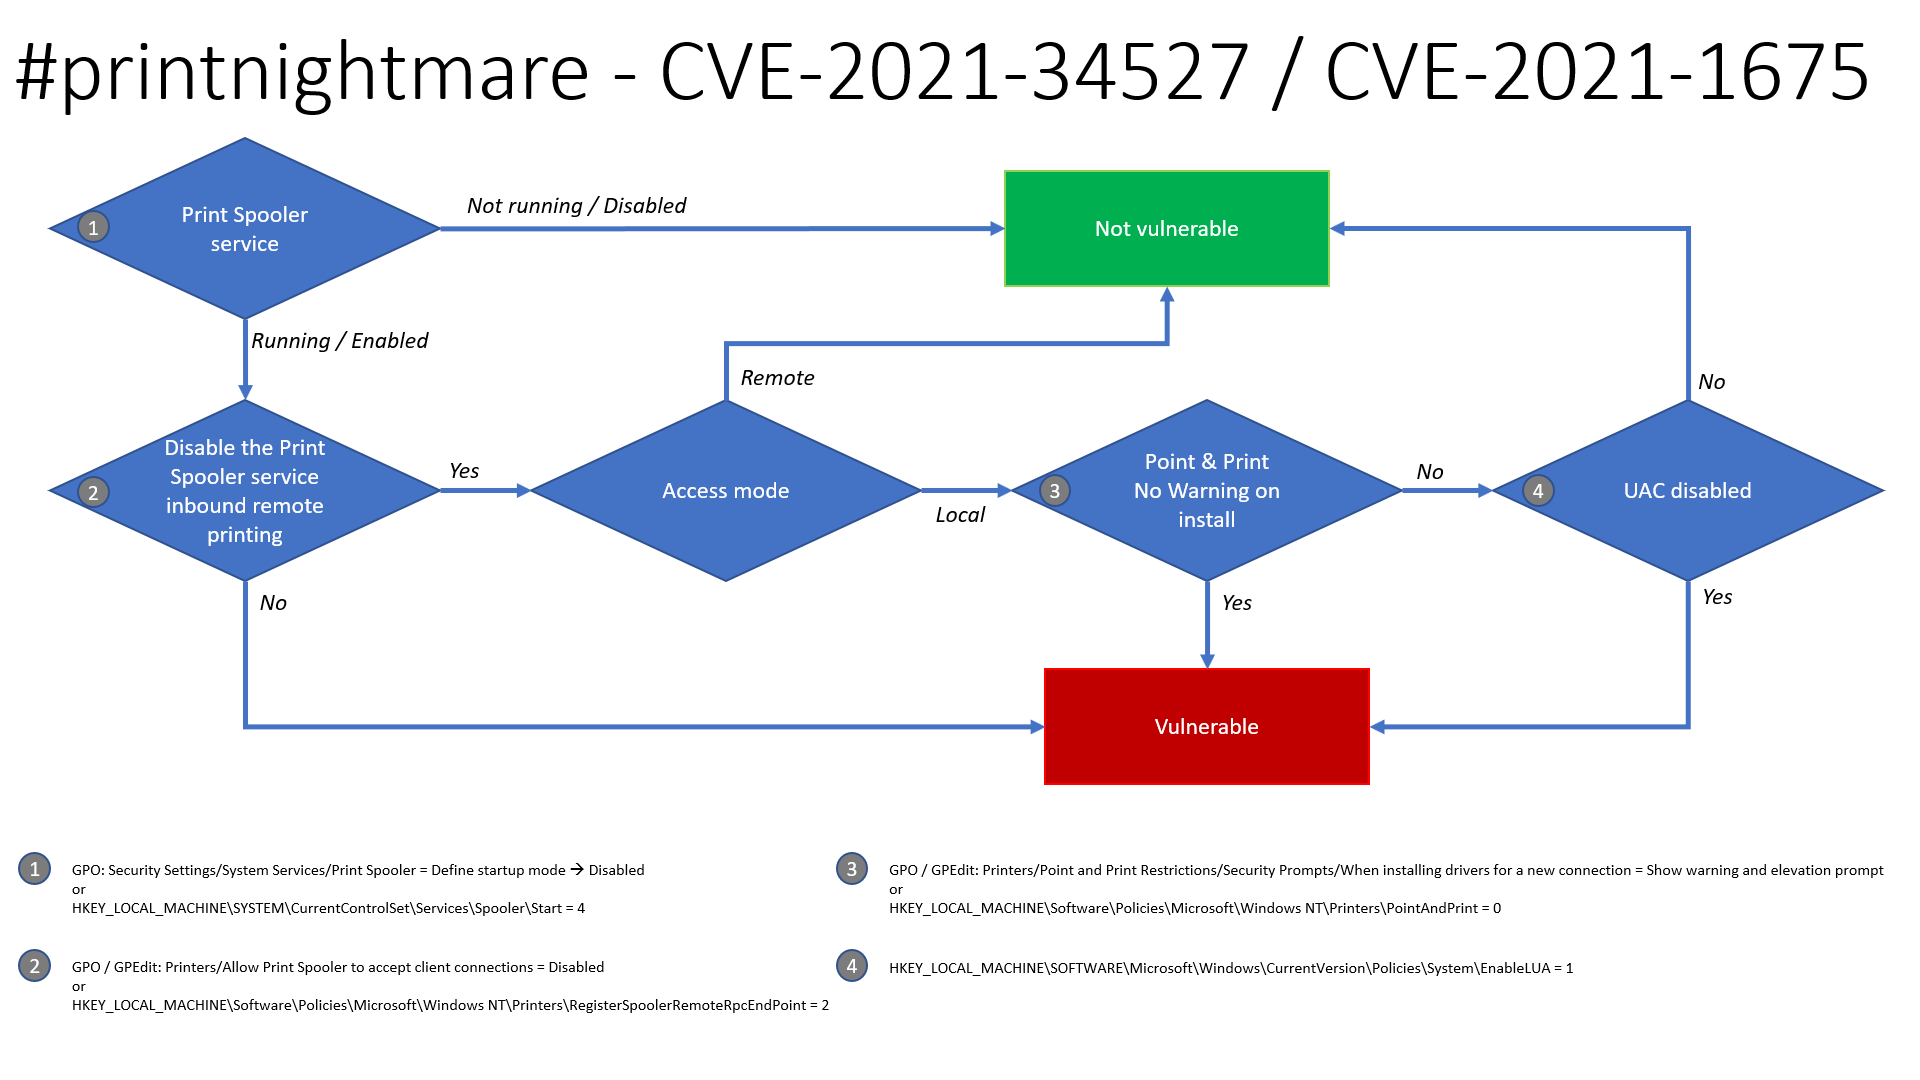 laresllc/cve-2021-1675
CVE-2021-1675 Detection Info
 avwolferen/sitecore.solr-log4j-mitigation
This repository contains a script that you can run on your (windows) machine to mitigate CVE-2021-44228
 pauljrowland/bootholefix
This script will remediate the BootHole bug identified in CVE-2020-25632 and/or CVE-2021-20233.
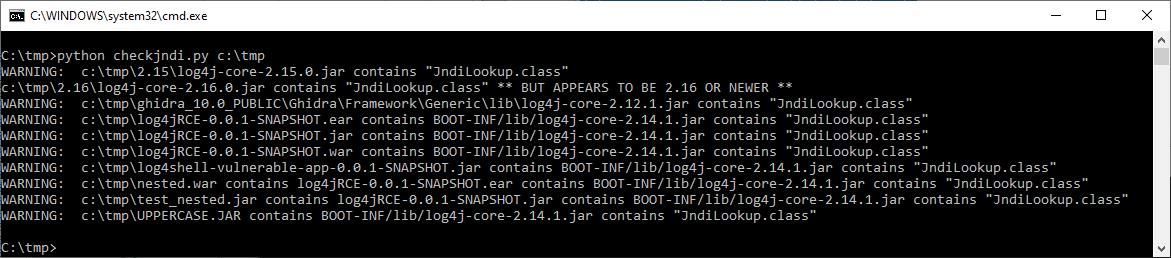 certcc/cve-2021-44228_scanner
Scanners for Jar files that may be vulnerable to CVE-2021-44228
 codeshield-security/log4jshell-bytecode-detector
Local Bytecode Scanner for the Log4JShell Vulnerability (CVE-2021-44228)