
Baskerville
 nccgroup/baskerville
Selective protocol extractor from PCAPs or interfaces
incident-responsenetwork-forensicsnetwork-security+1
512 years ago
nccgroup/baskervilleSelective protocol extractor from PCAPs or interfaces
 logesh-git001/cve-2025-48593
"A single malicious packet can own your device." — Android Security Team, Nov 2025
 harshavmb/fim-ebpf
A lightweight eBPF program to monitor file creation and modification events on Linux. This tool leverages eBPF (Extended Berkeley Packet Filter) to…
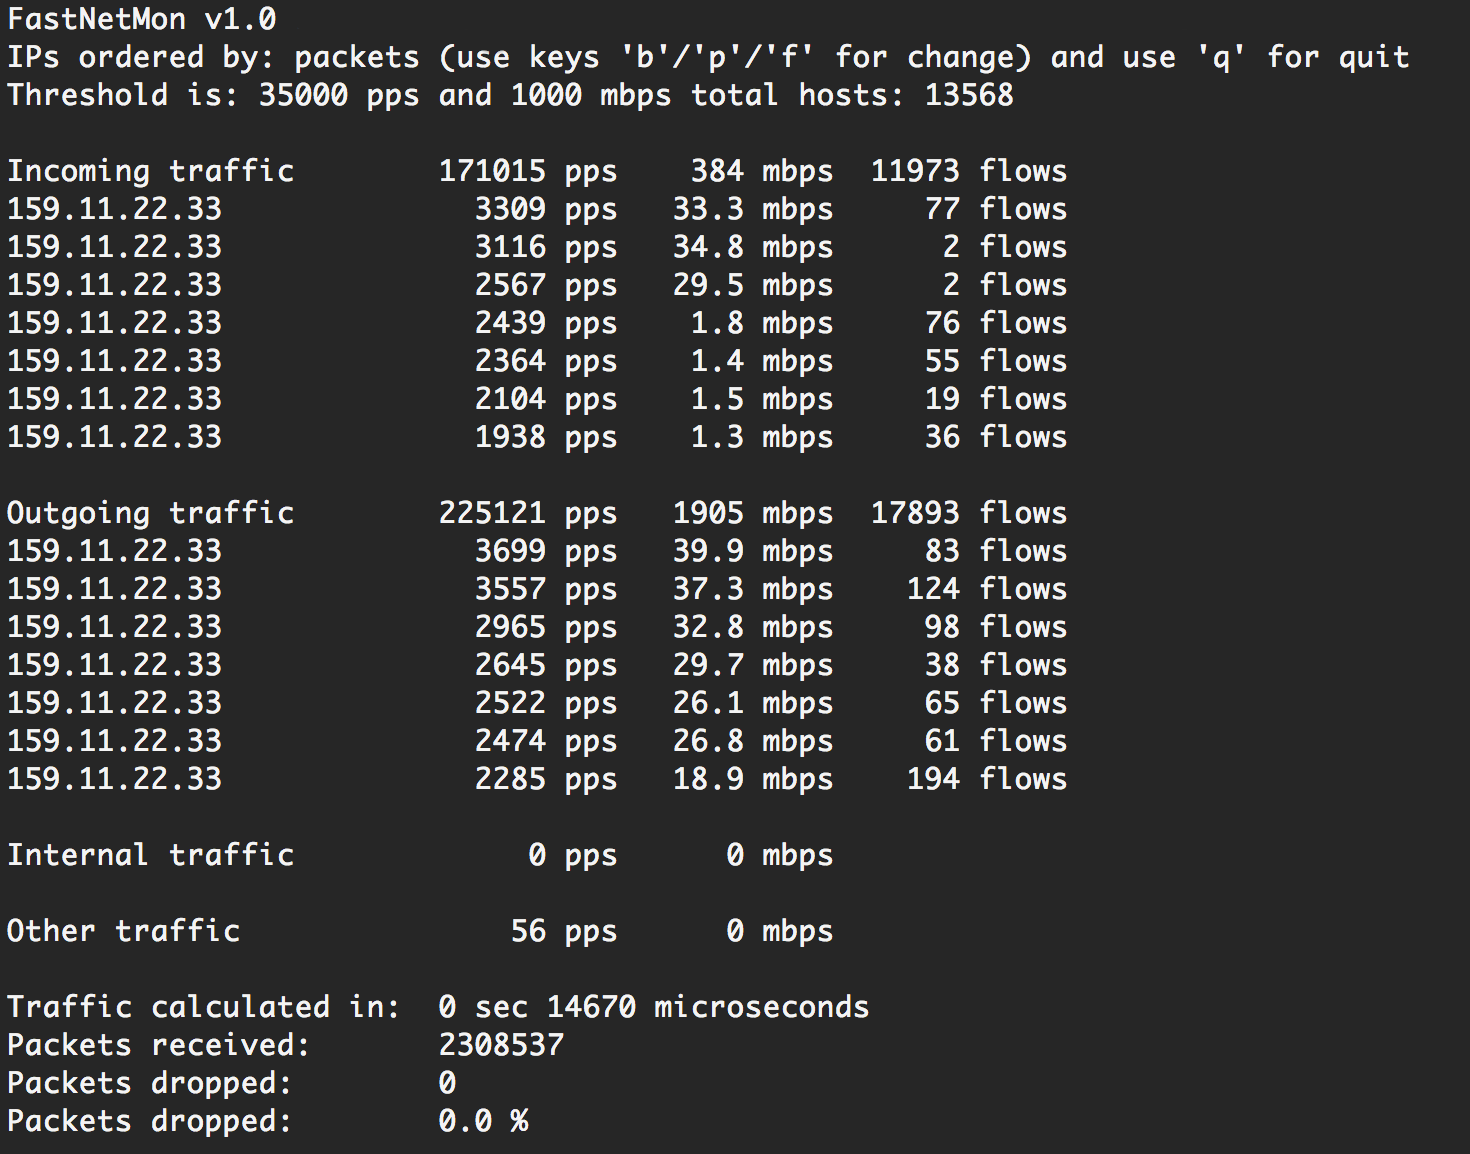 pavel-odintsov/fastnetmon
Very fast DDoS sensor with sFlow/Netflow/IPFIX/SPAN support