
routeros-scanner
 microsoft/routeros-scanner
Tool to scan for RouterOS (Mikrotik) forensic artifacts and vulnerabilities.
configuration-auditingdigital-forensicsembedded-systems-security+8
984
microsoft/routeros-scannerTool to scan for RouterOS (Mikrotik) forensic artifacts and vulnerabilities.
 bert-janp/entratrace
Defensive research tool that documents observable API endpoints and user agents of offensive tooling targeting Microsoft Entra ID, supporting…
 dfir-orc/dfir-orc
Forensics artefact collection tool for systems running Microsoft Windows
 nccgroup/impossibletravelloganalysis
Basic log analysis tool to detect impossible travel via IP address geographic information
 aws-alchemy/squidmagic
analyze a web-based network traffic 🕶 to detect central command and control servers
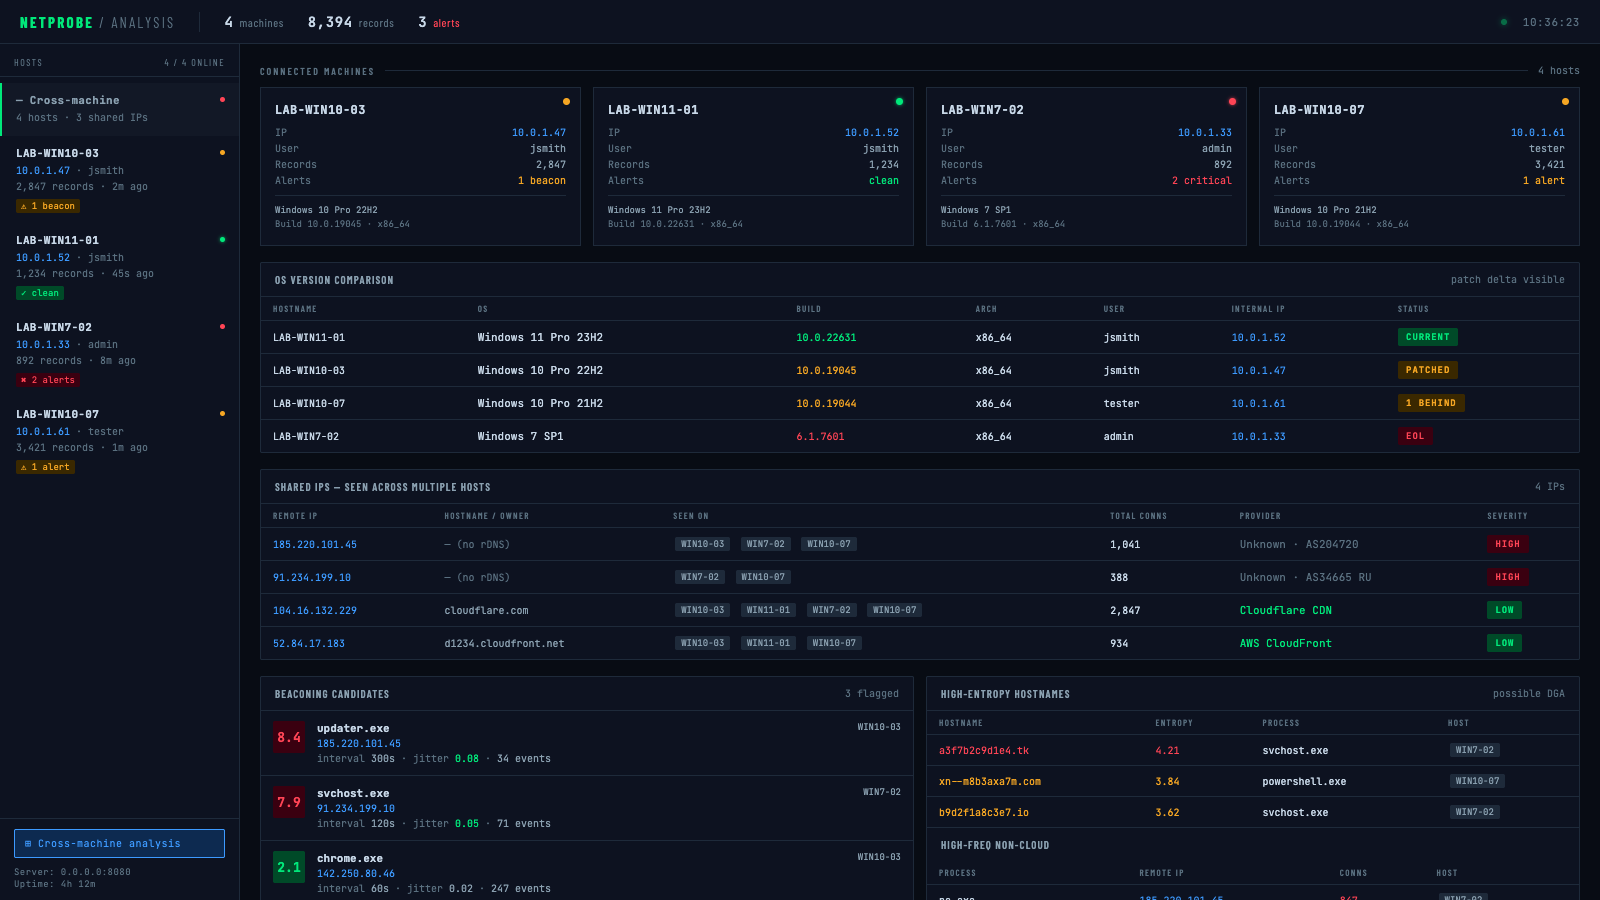
 hackinglz/gibson
Network monitoring tool that maps process-to-network connections, identifies cloud providers, and detects beaconing activity
 sekoialab/fastir_collector
Live Windows forensic acquisition tool that collects system artefacts (registry, memory, disk, files) into CSV/JSON for early compromise detection…
 rushyo/vindicatetool
LLMNR/NBNS/mDNS Spoofing Detection Toolkit
 viralmaniar/remote-desktop-caching-
This tool allows one to recover old RDP (mstsc) session information in the form of broken PNG files. These PNG files allows Red Team member to…
 gamelinux/passivedns
A network sniffer that logs all DNS server replies for use in a passive DNS setup
 naveenrudra/rttm
Real Time Threat Monitoring Tool

 zomato/vinifera
A GitHub recon/monitoring tool for finding internal leaks belonging to your organisation.
 forensicmatt/rswindowsthingies
Rust-based Windows forensic toolkit for real-time MFT monitoring, event log streaming, and channel enumeration, enabling live system analysis and…
 sap8899/reportly
AzureAD/EntraID user activity reporter for blue teams. Input a suspicious user and time frame to receive a detailed report of user info, actions, and…
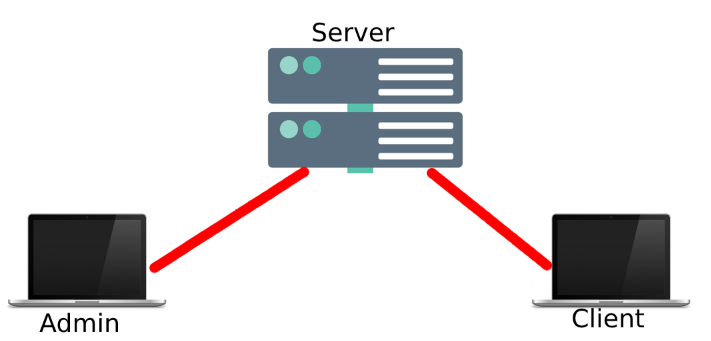 letsdefendio/simple-live-data-collection
Client-server tool for live data collection during incident response. Admin sends requests to clients to gather system information for forensic…
 invictus-ir/microsoft-extractor-suite
A PowerShell module for acquisition of data from Microsoft 365 and Azure for Incident Response and Cyber Security purposes.
 adityaks/melee
Python-based tool to detect ransomware infections and malicious code in MySQL instances. Performs reconnaissance, user enumeration, and deep scans…