CVE-2026-67401-cPanel-EmailTrack-SQLi

Read-only IOC scanner and mitigation toolkit for cPanel & WHM EmailTrack SQL injection (CVE-2026-67401). Performs version fingerprinting, file…

Read-only IOC scanner and mitigation toolkit for cPanel & WHM EmailTrack SQL injection (CVE-2026-67401). Performs version fingerprinting, file…

Proof-of-concept exploit for CVE-2025-31324, an unauthenticated file upload in SAP NetWeaver Visual Composer, with detection guidance, MITRE mapping,…

Collects comprehensive triage data from macOS for incident response, including system logs, file listings, browser data, shell history, and…

Python ctypes wrapper for Event Tracing for Windows (ETW) enabling session control, event capture, and custom callbacks for security monitoring and…

#PaperCut CVE-2026-81578 + CVE-2026-82078 Defense Toolkit 2 3 A **defensive** toolkit to check and understand exposure to the chained

Detection, mitigation, and IOC toolkit for Copy Fail CVE-2026-31431 Linux kernel page-cache privilege escalation

Library and tools to access the Volume Shadow Snapshot (VSS) format

Digital forensics engine that parses logs, files, and system artifacts to build super timelines, enabling chronological event correlation for…

Collaborative forensic timeline analysis platform for ingesting, searching, and annotating event logs to support incident response and DFIR…

Forensic library and CLI toolkit for analyzing disk and file system images, recovering deleted data, generating timelines, and validating evidence…

Walk any memory dump. Find what's hidden. Linux + Windows kernel forensics from a single static Rust binary — no Python required.

Credential and sensitive-data exposure triage for file shares

This repository serves as a place for community created Targets and Modules for use with KAPE.

Builds forensic file hash sets from disk images, packages, and archives across GCP, AWS, and local sources, with deduplication and PostgreSQL/Spanner…

Tools developed by the Zscaler ThreatLabz Threat Intelligence team

Autopsy® is a digital forensics platform and graphical interface to The Sleuth Kit® and other digital forensics tools. It can be used by law…

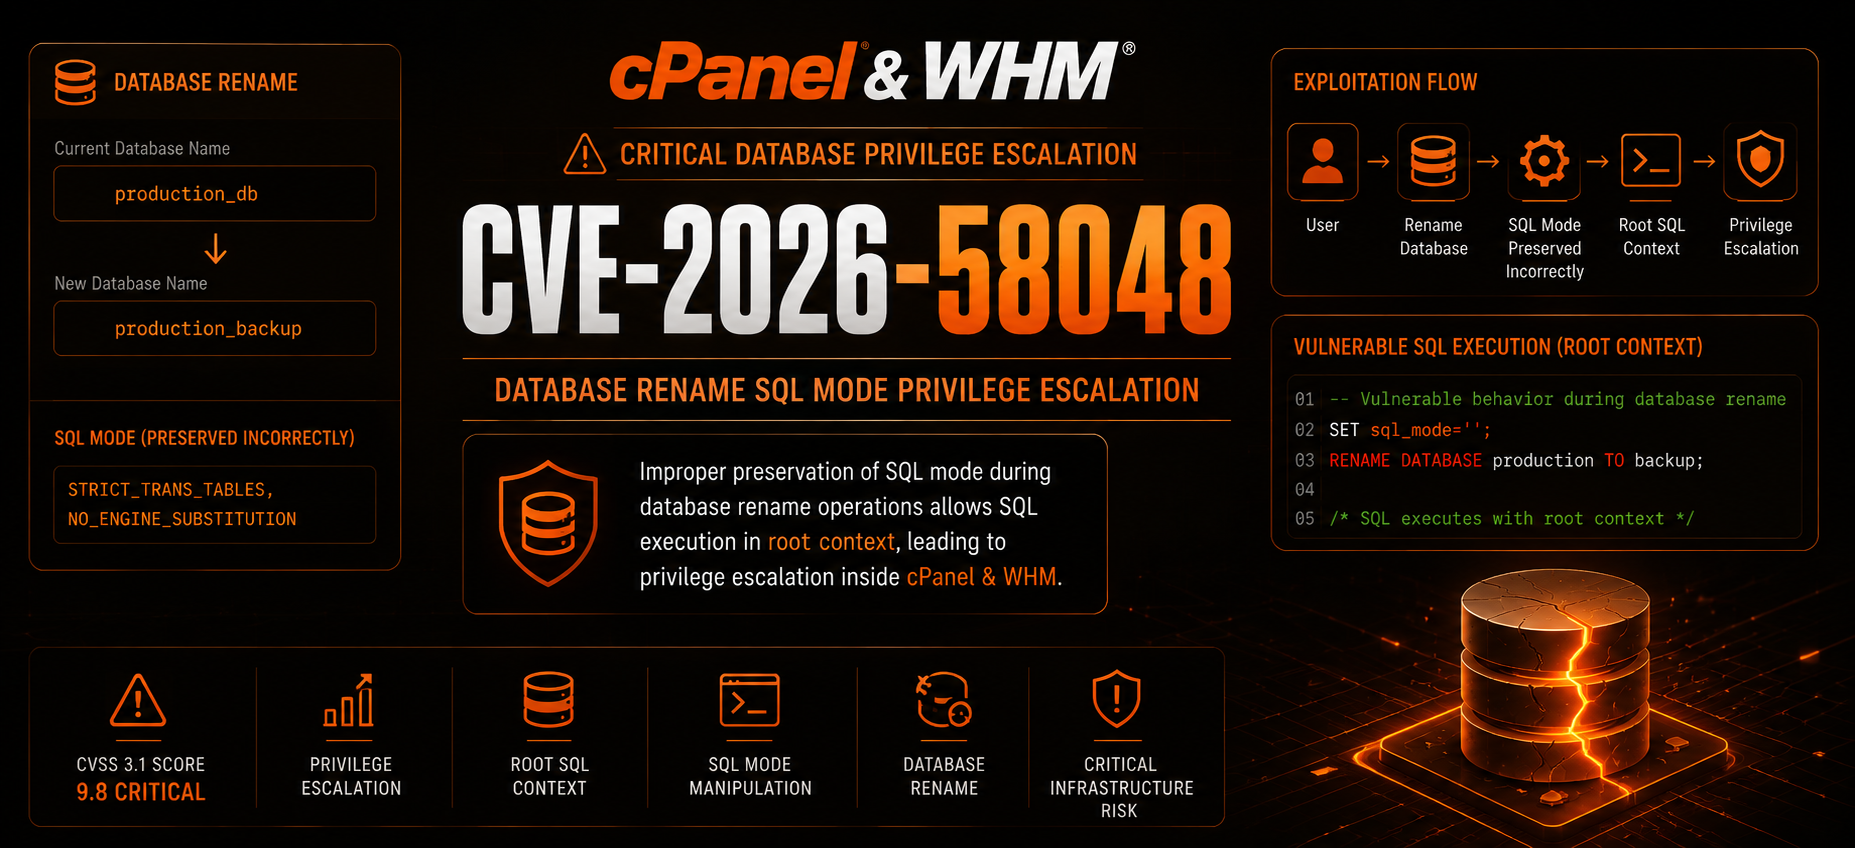
👾 CVE-2026-58048 – cPanel Root SQL Execution Toolkit (CVSS 9.4) | Full Red/Blue Team Toolkit suite for unpatched cPanel & WHM 11.x. 2 tools: Safe…

PowerShell toolkit that extracts locked Windows files (SAM, SYSTEM, NTDS, ...) using MFT parsing and raw disk reads