

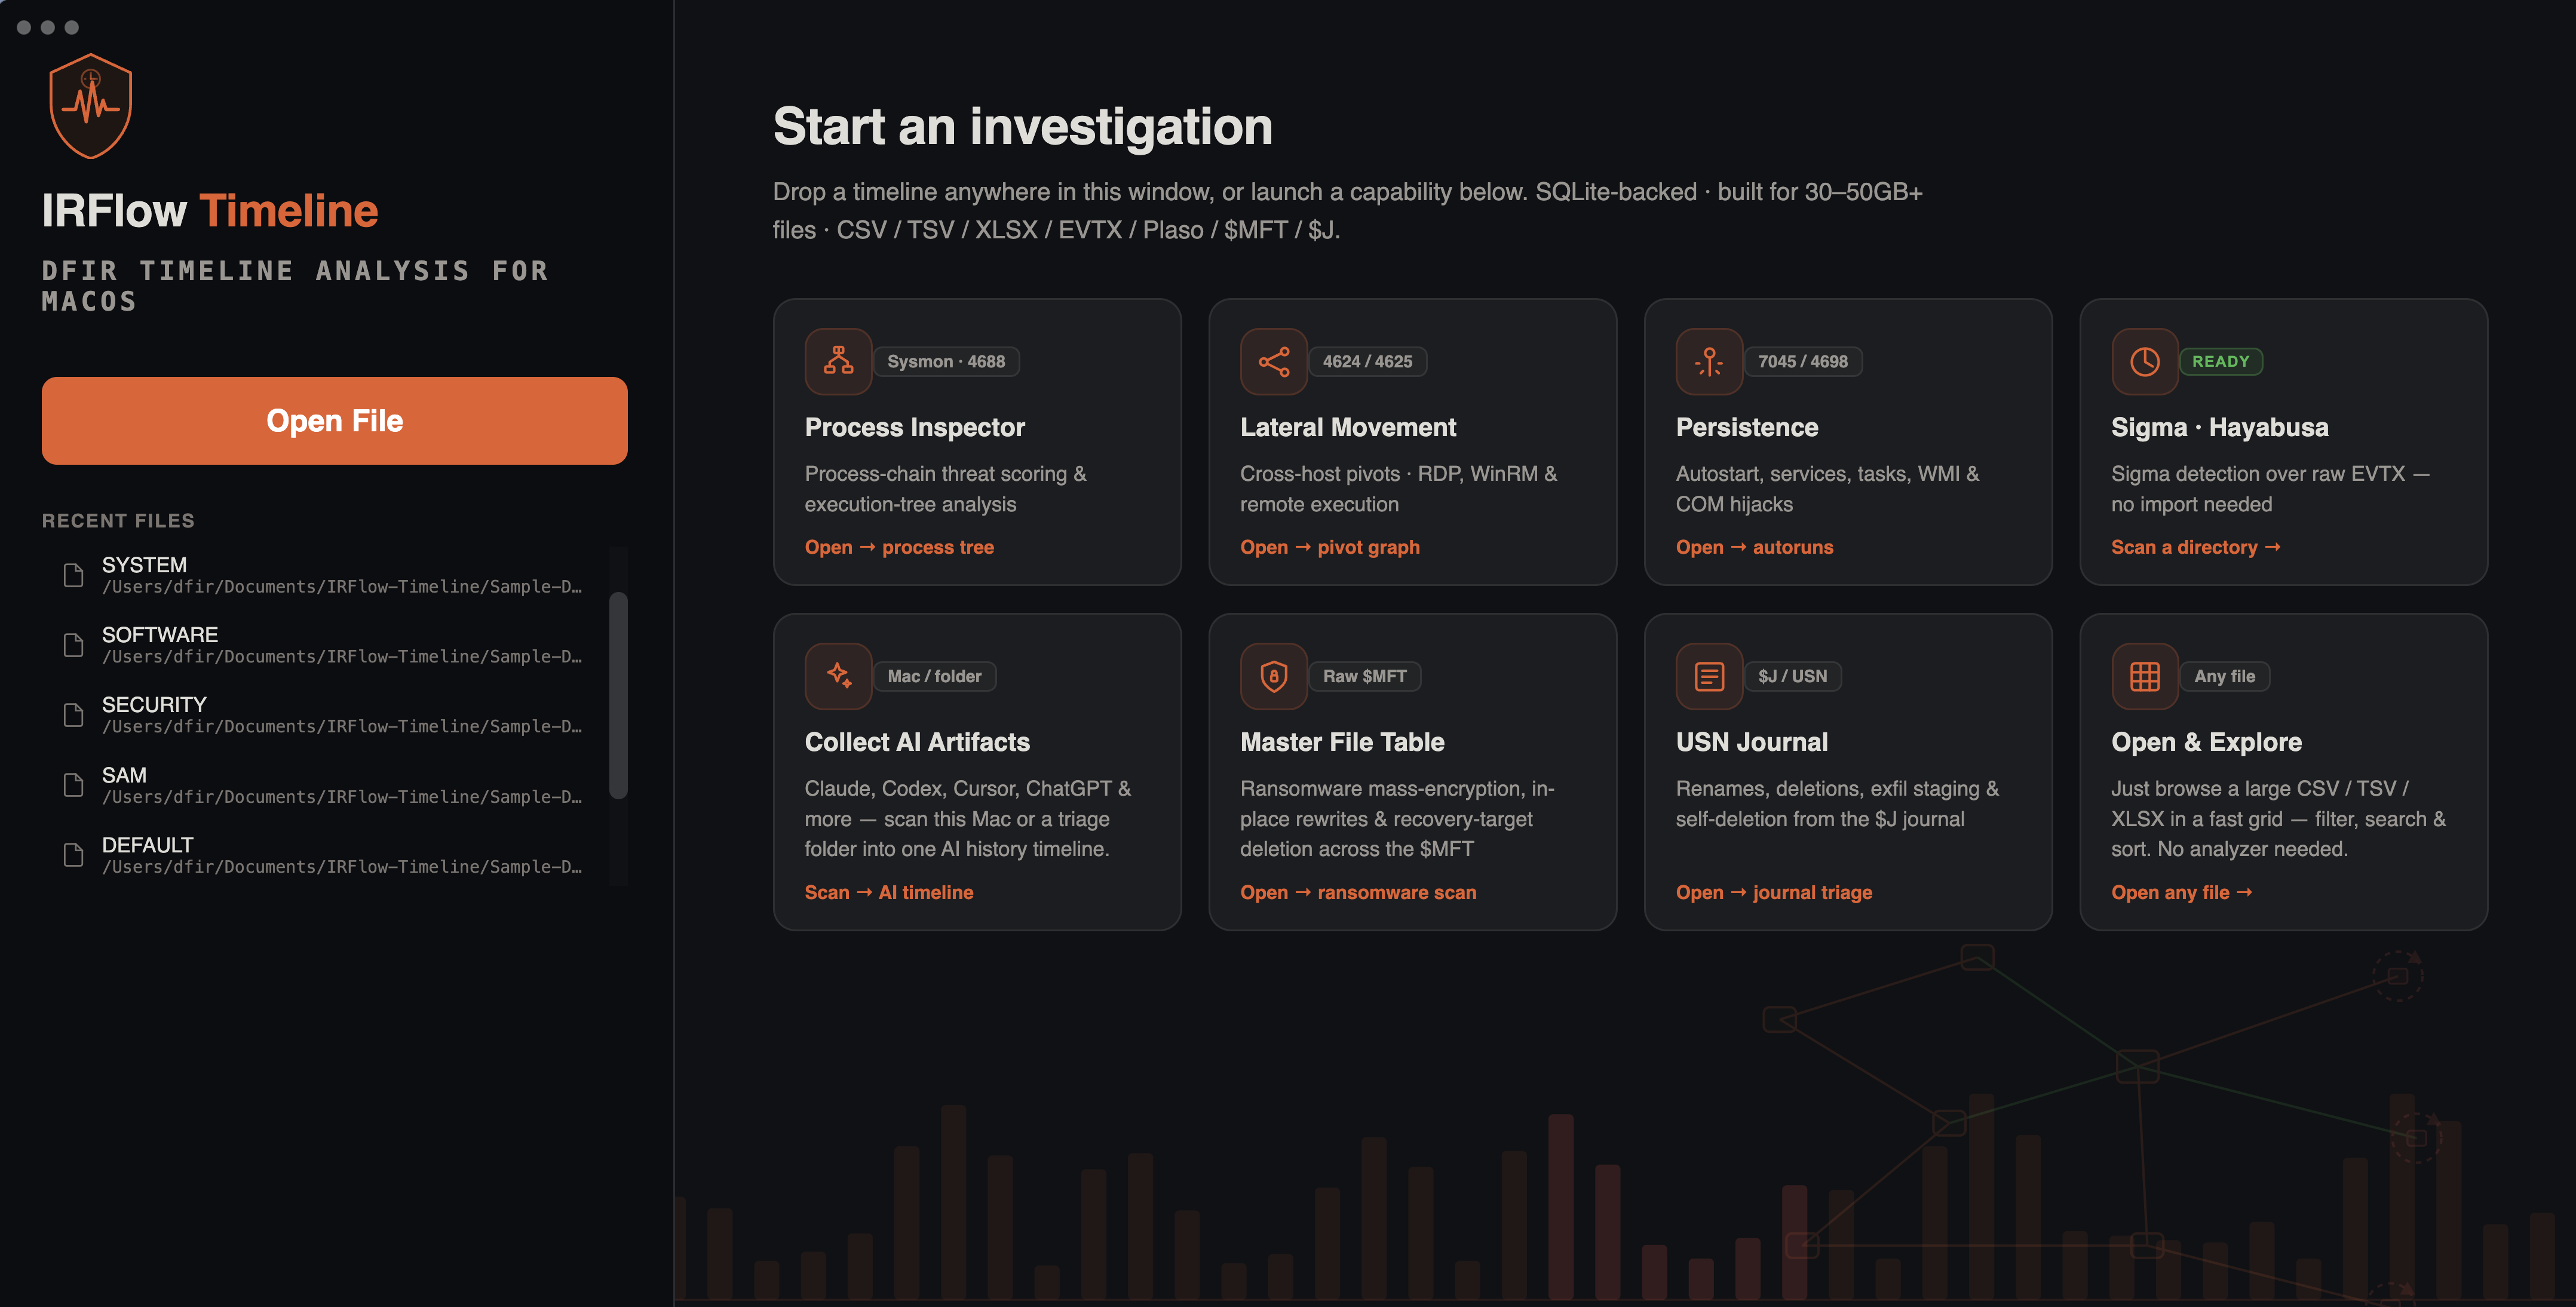
 r3nzsec/irflow-timeline
DFIR Timeline Analysis for macOS — SQLite-backed viewer for CSV, TSV, XLSX, EVTX, Plaso, $MFT, and $J files with AI Artifacts, AI Secret Hunt,…
 stanfrbd/cyberbro
A simple application that extracts your IoCs from garbage input and checks their reputation using multiple CTI services.
 bruneaug/dshield-siem
DShield Sensor Log Collection with ELK
 mukul975/cve-mcp-server
Production-grade MCP server giving Claude 27 security intelligence tools across 21 APIs — CVE lookup, EPSS scoring, CISA KEV, MITRE ATT&CK, Shodan,…
 maliceio/malice
VirusTotal Wanna Be - Now with 100% more Hipster
 corelight/phantom-playbooks
Automated security incident response playbooks for Splunk Phantom, integrating Zeek logs, DNS analysis, and VirusTotal threat intelligence to…
 intezer/linux-explorer
Easy-to-use live forensics toolbox for Linux endpoints
 cristianzsh/amcache-evilhunter
Parse and analyze a Windows Amcache.hve registry hive, VirusTotal integration.
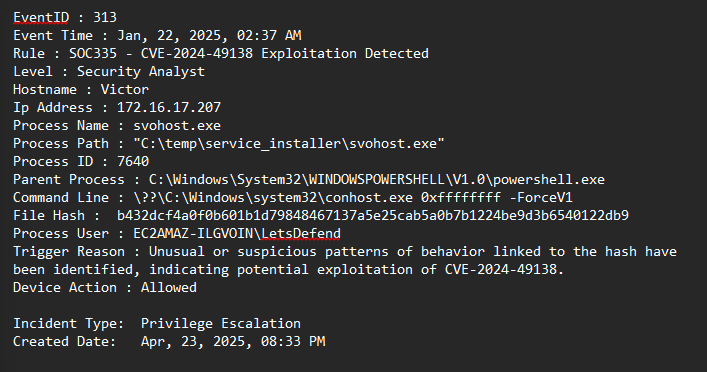 cyprianatsyor/letsdefend-cve-2024-49138-investigation
Hands-on SOC investigation of CVE-2024-49138 using LetsDefend, VirusTotal, Hybrid Analysis, TrueFort, and ChatGPT.
 zavikhttak/follina-msdt-threat-investigation
🔵 Threat analysis writeup for Follina (CVE-2022-30190) — Microsoft MSDT RCE zero-day exploited in the wild. Covers static analysis, VirusTotal,…