
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
150 results
loki preview

loki

GitHubgrafana/loki

Horizontally scalable, multi-tenant log aggregation system that indexes labels instead of full text, integrates with Grafana, and is optimized for…

general-purpose-utilitiesincident-responselog-analysis+1
29.0k1h 11m ago
wazuh preview

wazuh

GitHubwazuh/wazuh

Open-source XDR and SIEM platform for threat detection, log analysis, file integrity monitoring, vulnerability assessment, and compliance management…
anomaly-detectionanti-botcloud-security+12
17.2k1 day ago
ThreatHound preview

ThreatHound

GitHubmazx0p/threathound

Automated threat hunting and incident response tool for Windows Event Logs with Sigma rule integration, real-time detection, and forensic artifact…
digital-forensicsincident-responselog-analysis+1
1592 years ago
cowrie preview

cowrie

GitHubcowrie/cowrie

Cowrie SSH/Telnet Honeypot https://docs.cowrie.org/

defensive-toolsincident-responseinformation-gathering+3
6.6k2 days ago
securityonion preview

securityonion

GitHubsecurity-onion-solutions/securityonion

Open-source security monitoring platform for threat hunting, intrusion detection, log management, incident response, and endpoint visibility with…
anomaly-detectionanti-botdefensive-tools+9
4.9k28 days ago
LogonTracer preview

LogonTracer

GitHubjpcertcc/logontracer

Investigate malicious Windows logon by visualizing and analyzing Windows event log

ai-securitydigital-forensicsincident-response+2
3.3k2 months ago
hayabusa preview

hayabusa

GitHubyamato-security/hayabusa

Multi-threaded Windows event log forensics timeline generator and threat hunting tool with full Sigma rule support, producing CSV/JSON timelines for…

digital-forensicsforensicsincident-response+2
3.4k4 days ago
opencanary preview

opencanary

GitHubthinkst/opencanary

Low-resource honeypot that emulates common network services to detect post-breach attacker activity, with extensible protocol modules and…
defensive-toolsincident-responseintrusion-detection+3
3.1k18 days ago
Sentora preview

Sentora

GitHubd3vhex/sentora

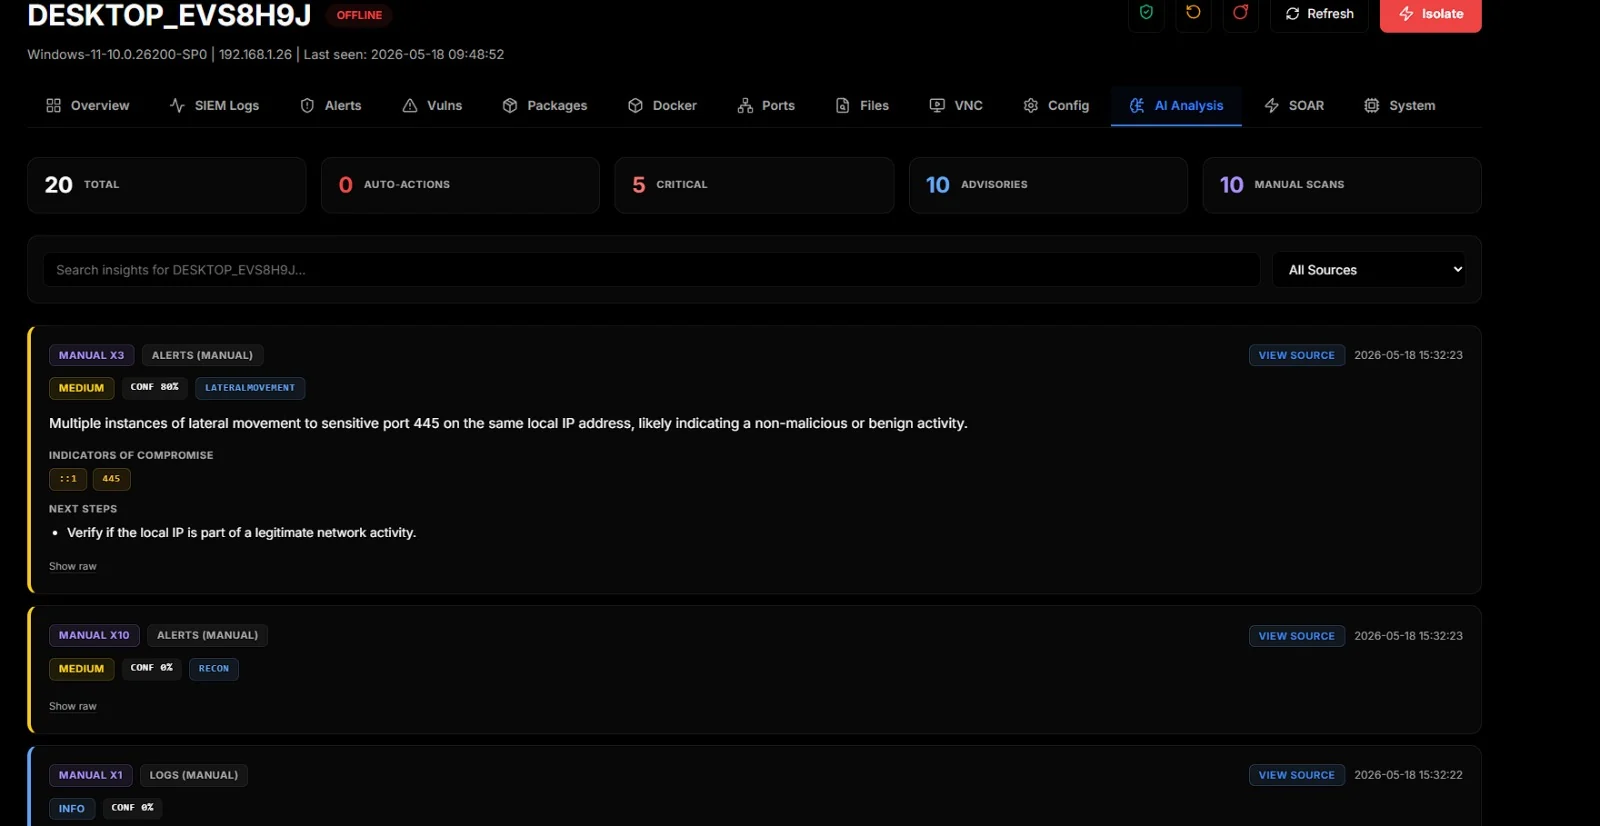
An open-source, self-hosted AI-powered SIEM, EDR and SOAR platform for modern security operations.
ai-securityincident-responseintrusion-detection+3
1019 days ago
CloudGrappler preview

CloudGrappler

GitHubpermiso-io-tools/cloudgrappler

Query high-fidelity cloud detections for known threat actors across AWS, Azure, and GCP using CloudTrail logs and custom threat intelligence rules.
cloud-securitydefensive-toolsincident-response+2
26510 months ago
fastnetmon preview

fastnetmon

GitHubpavel-odintsov/fastnetmon

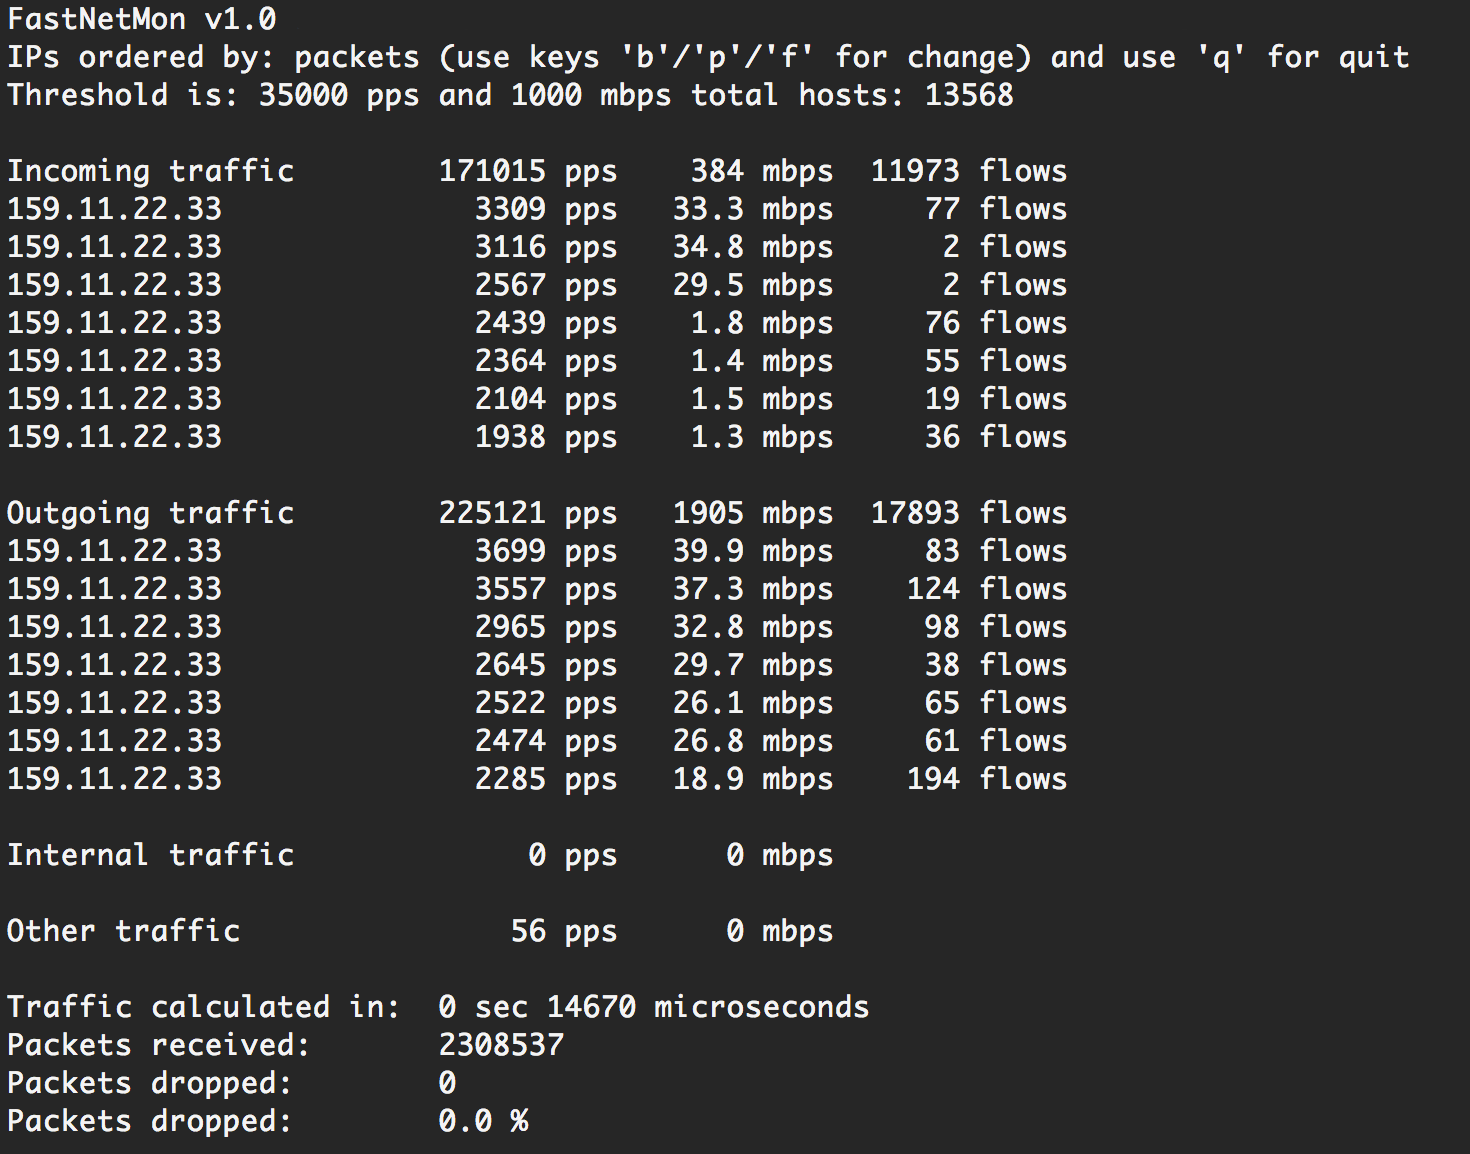
Very fast DDoS sensor with sFlow/Netflow/IPFIX/SPAN support

anomaly-detectionincident-responselog-analysis+5
3.7k1 month ago
awesome-incident-response preview

awesome-incident-response

GitHubmeirwah/awesome-incident-response

Curated index of incident response and DFIR tools, including memory and disk forensics, evidence collection, log analysis, playbooks, and educational…
curated-resourcesdigital-forensicsdisk-forensics+9
9.4k2 months ago
Microsoft-Sentinel-SecOps preview

Microsoft-Sentinel-SecOps

GitHubeshlomo1/microsoft-sentinel-secops

SOC operations content for Microsoft Sentinel, including hunting queries, incident response playbooks, and security event analysis for Azure cloud…
cloud-securityincident-responselog-analysis+1
2692 months ago
ALEAPP preview

ALEAPP

GitHubabrignoni/aleapp

Android Logs Events And Protobuf Parser
digital-forensicsincident-responselog-analysis+1
9788h 45m ago
SSHintel preview

SSHintel

GitHubsonitbahl/sshintel

Self-contained SSH honeypot for capturing attacker interactions and turning them into structured security intelligence.
incident-responseintrusion-detectionlog-analysis+2
318 days ago
SOC274---Palo-Alto-Networks-PAN-OS-Command-Injection-Vulnerability-Exploitation-CVE-2024-3400- preview

SOC274---Palo-Alto-Networks-PAN-OS-Command-Injection-Vulnerability-Exploitation-CVE-2024-3400-

GitHubcyberbibs/soc274---palo-alto-networks-pan-os-command-injection-vulnerability-exploitation-cve-2024-3400-

Step-by-step SOC analyst walkthrough for investigating and remediating CVE-2024-3400 (PAN-OS command injection). Covers detection, log analysis,…
digital-forensicseducationincident-response+6
1 year ago
QLOG preview

QLOG

GitHubthreathunters-io/qlog

ETW-based Windows process creation logger that enriches events with file hashes, signatures, and parent process details, outputting to Windows…

defensive-toolsforensicsincident-response+1
444 years ago
RDP-Guard preview

RDP-Guard

GitLabsiberanka/rdp-guard

Monitors Windows Security logs for failed RDP attempts and automatically blocks abusive IPs via Windows Firewall, with configurable thresholds and…

configuration-auditingdefensive-toolsincident-response+2
1 month ago
Previous12…9Next