
TBP-NETWORK
 philippeabraxas-jpg/tbp-network
Theory and implemantation of the TBP protocol to secure networked AI in small to open web networks
authentication-authorizationconfiguration-auditingcryptography+5
philippeabraxas-jpg/tbp-networkTheory and implemantation of the TBP protocol to secure networked AI in small to open web networks
 kontext-security/kontext-cli
Runtime security for AI agents: discover agents, map their permissions, and enforce what they can do.
 philippeabraxas-jpg/responsible-alliance-protocol
Safety cannot be a prompt instruction. TBP provides an external execution-layer boundary for autonomous agents, enforcing hard F/I/W invariants via…
 cred-club/dial
Event-driven AWS security misconfiguration detection framework that monitors multiple accounts in real-time, triggering alerts via Lambda for IAM,…
 qarait/ephemera
Zero-Trust SSH CA
 inverse-inc/packetfence
PacketFence is a fully supported, trusted, Free and Open Source network access control (NAC) solution. Boasting an impressive feature set including a…
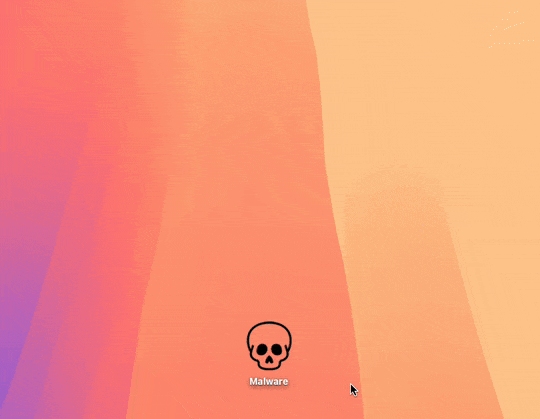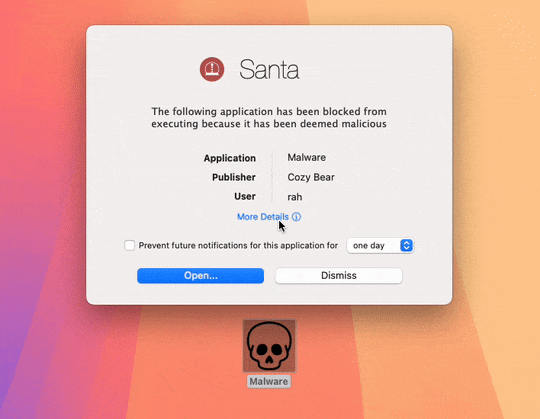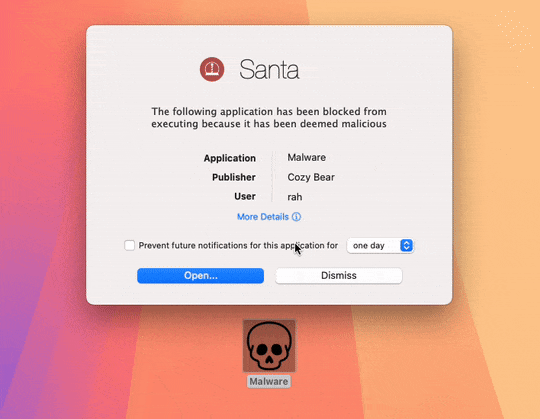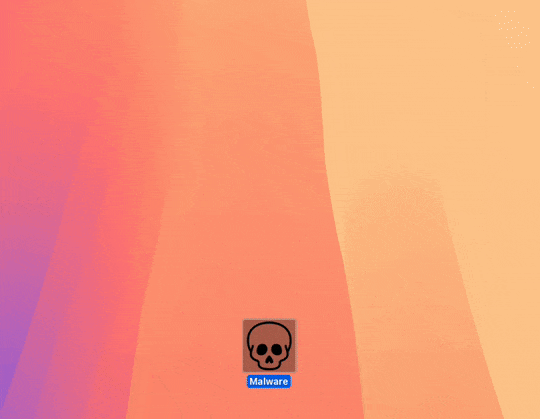 northpolesec/santa
A binary and file access authorization system for macOS.
 oguz-kagan-akar/cve-2026-41940-analysis
Technical analysis of the cPanel/WHM auth bypass
 gmh5225/jataayu
LLM-backed AI agent security — inbound injection detection + outbound privacy protection
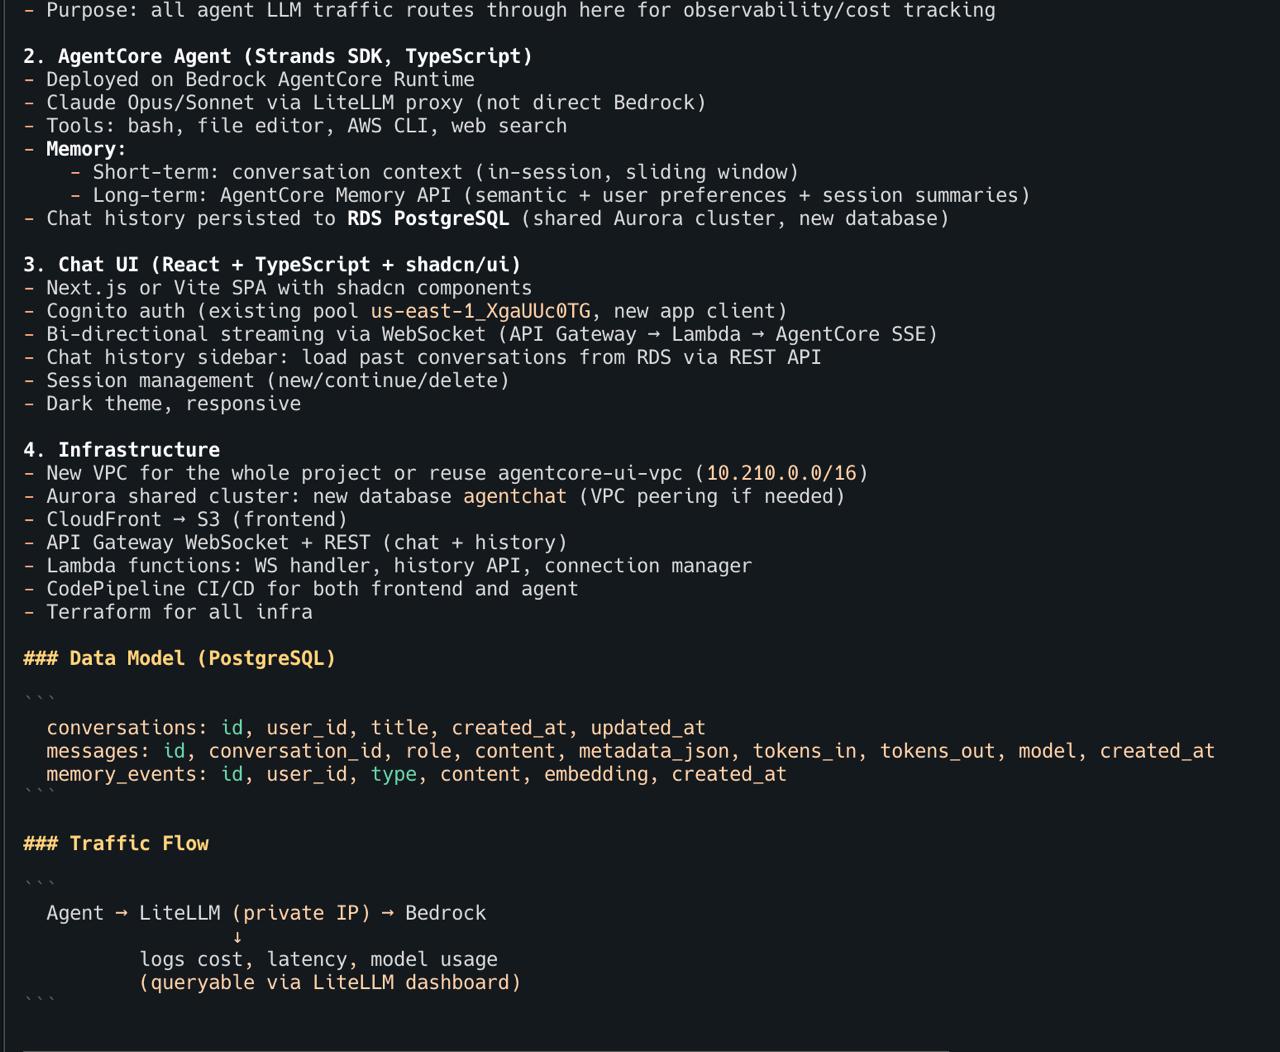 inceptionstack/lowkey
Deploy self-hosted AI coding agents (OpenClaw, Claude Code, Codex) into your AWS account with CloudFormation, IAM profiles, and sandbox isolation for…
 softrams/bulwark
An organizational asset and vulnerability management tool, with Jira integration, designed for generating application security reports.
 mandiant/mandiant-azure-ad-investigator
Read-only PowerShell module for detecting UNC2452 and other threat actor artifacts in Azure AD, auditing federated domains, service principals,…
 skelersecurity/wordpress-skelersecurity-core-security-cve-2026-63030
Temporary WordPress plugin requiring authentication for the Core REST Batch API endpoint to mitigate the wp2shell vulnerability chain…
 wardgate/wardgate
Security gateway for AI agents - credential-isolated API proxying and policy-gated remote execution (conclaves). Reduce the blast radius!
 sap8899/reportly
AzureAD/EntraID user activity reporter for blue teams. Input a suspicious user and time frame to receive a detailed report of user info, actions, and…
 michael-kanda/wp2shell-ioc-scanner
Detects shadow-administrator accounts in WordPress via configurable indicators and heuristics, then removes selected accounts through guarded, logged…
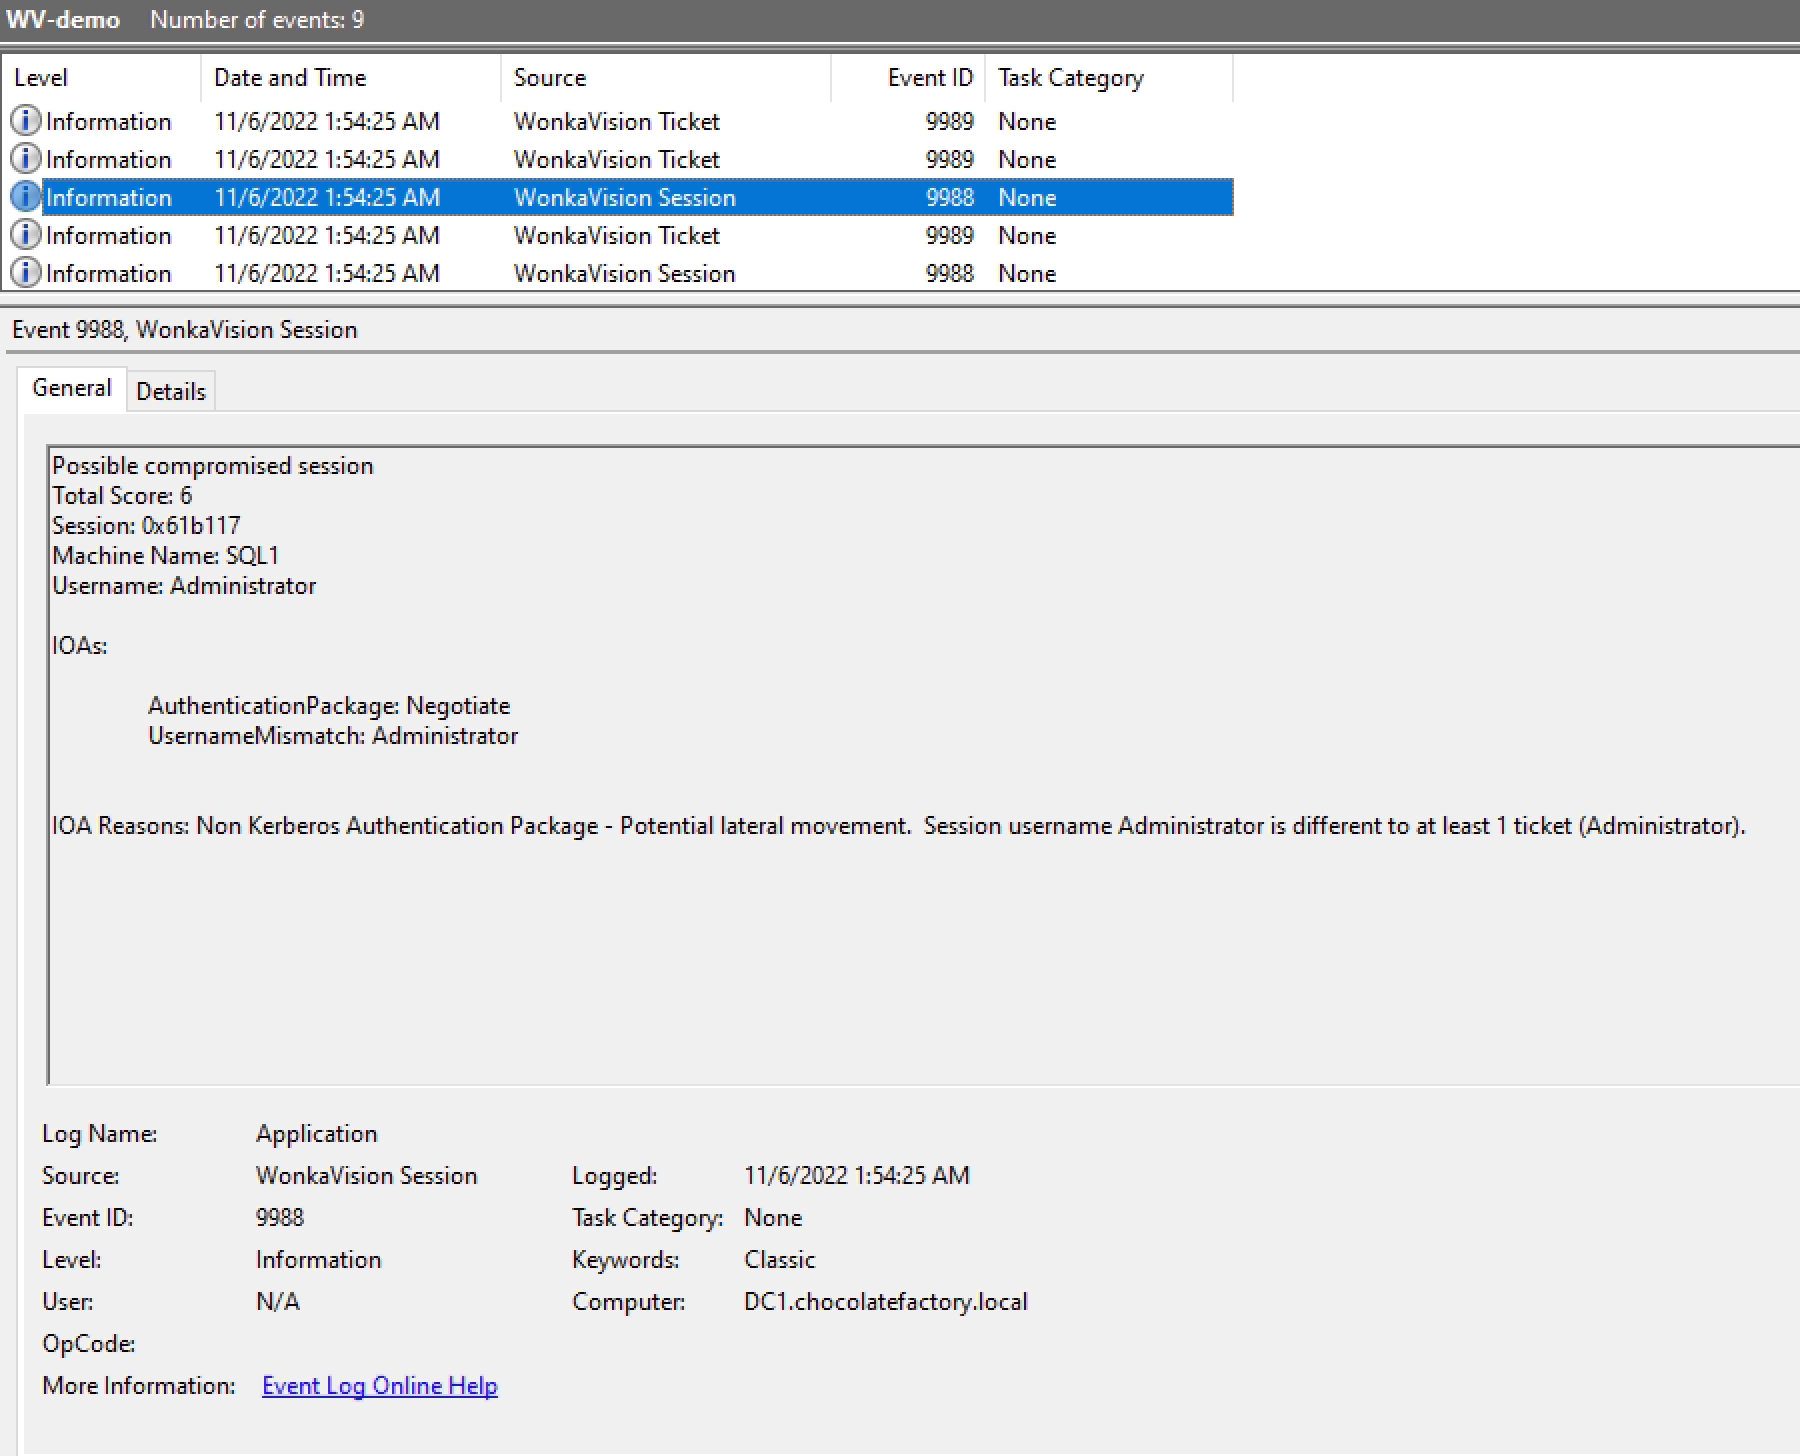 0xe7/wonkavision
Detects forged Kerberos tickets by dumping session and ticket data, scoring anomalies, and generating Windows event-log indicators for SIEM-based…
 canyonroad/agentsh
Execution-Layer Security (ELS) for AI agents — policy-enforced shell with audit.