
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
55 results
kubeshark preview

kubeshark

GitHubkubeshark/kubeshark

eBPF-powered network observability for Kubernetes. Indexes L4/L7 traffic with full K8s context, decrypts TLS without keys. Queryable by AI agents via…

ai-securitycloud-infrastructure-securitycloud-security+9
12.1k
2 days ago
sandbox-runtime preview

sandbox-runtime

GitHubanthropic-experimental/sandbox-runtime

A lightweight sandboxing tool for enforcing filesystem and network restrictions on arbitrary processes at the OS level, without requiring a container.

configuration-auditingcontainer-securitydefensive-tools+4
5.3k5 days ago
ThreatLens preview

ThreatLens

GitHubabdaullahag/threatlens

Python CLI tool for rapid IOC analysis (IPs, Domains, CVEs) using 6 free Threat Intel APIs. Outputs: Color-coded Excel, JSON, CSV. Uses: VT, Shodan,…

defensive-toolsincident-responseinformation-gathering+7
258 days ago
Exploitarium-Detections preview

Exploitarium-Detections

GitHubethan-andrews/exploitarium-detections

KQL detection rules for Microsoft Sentinel and Defender XDR covering the bikini/exploitarium anonymous disclosure — a personal research archive of…
educationincident-responseintrusion-detection+3
5013 days ago
pipelock preview

pipelock

GitHubluckypipewrench/pipelock

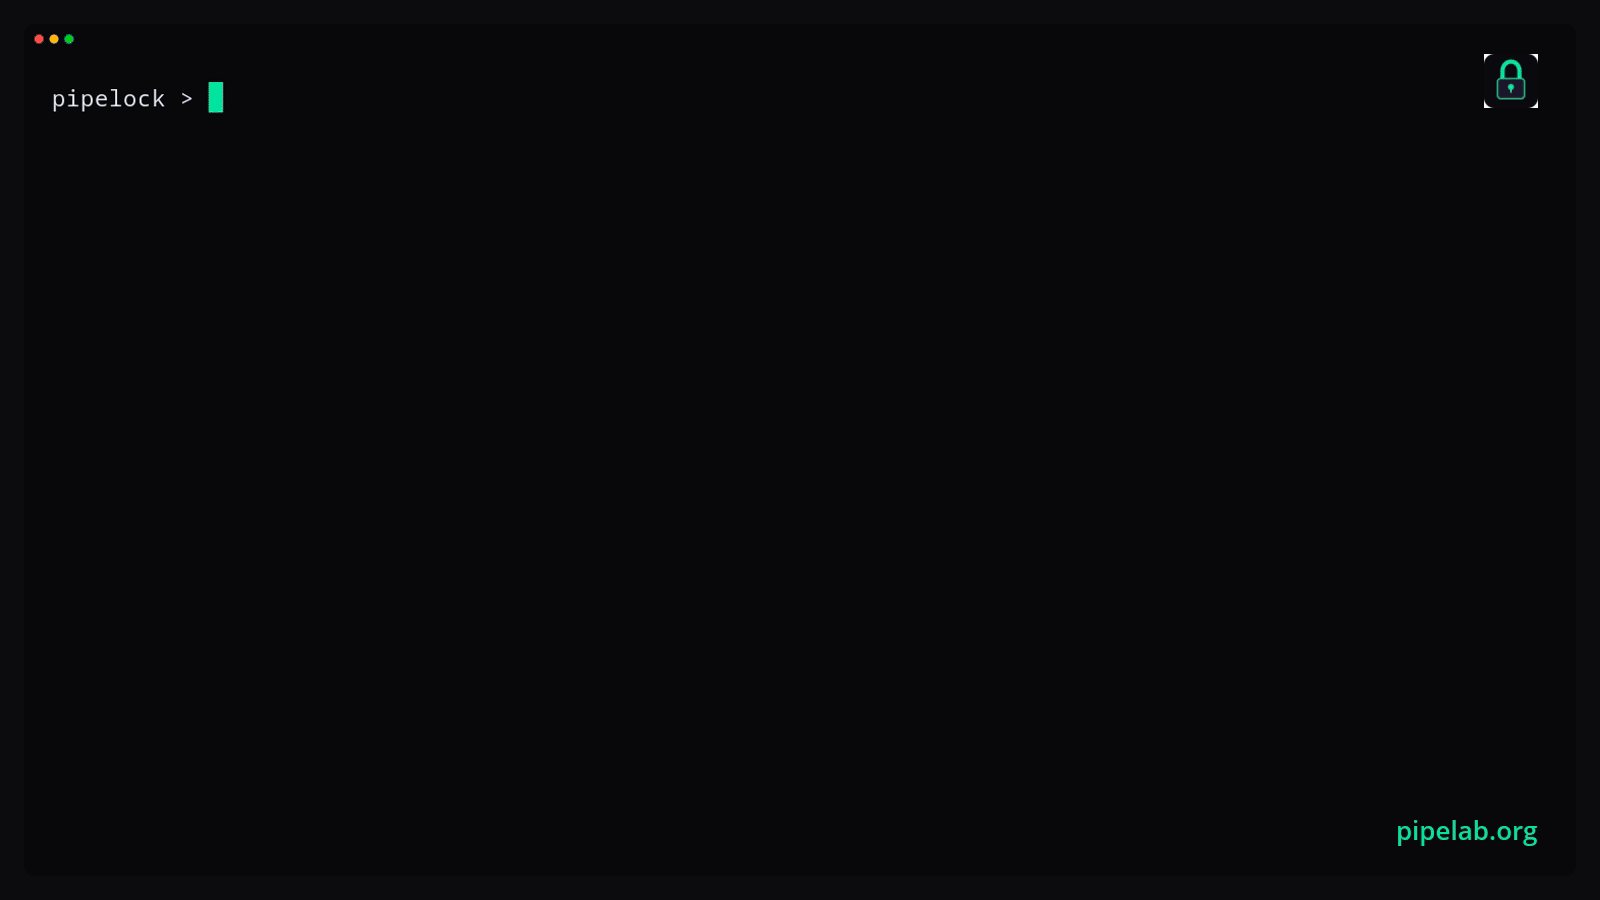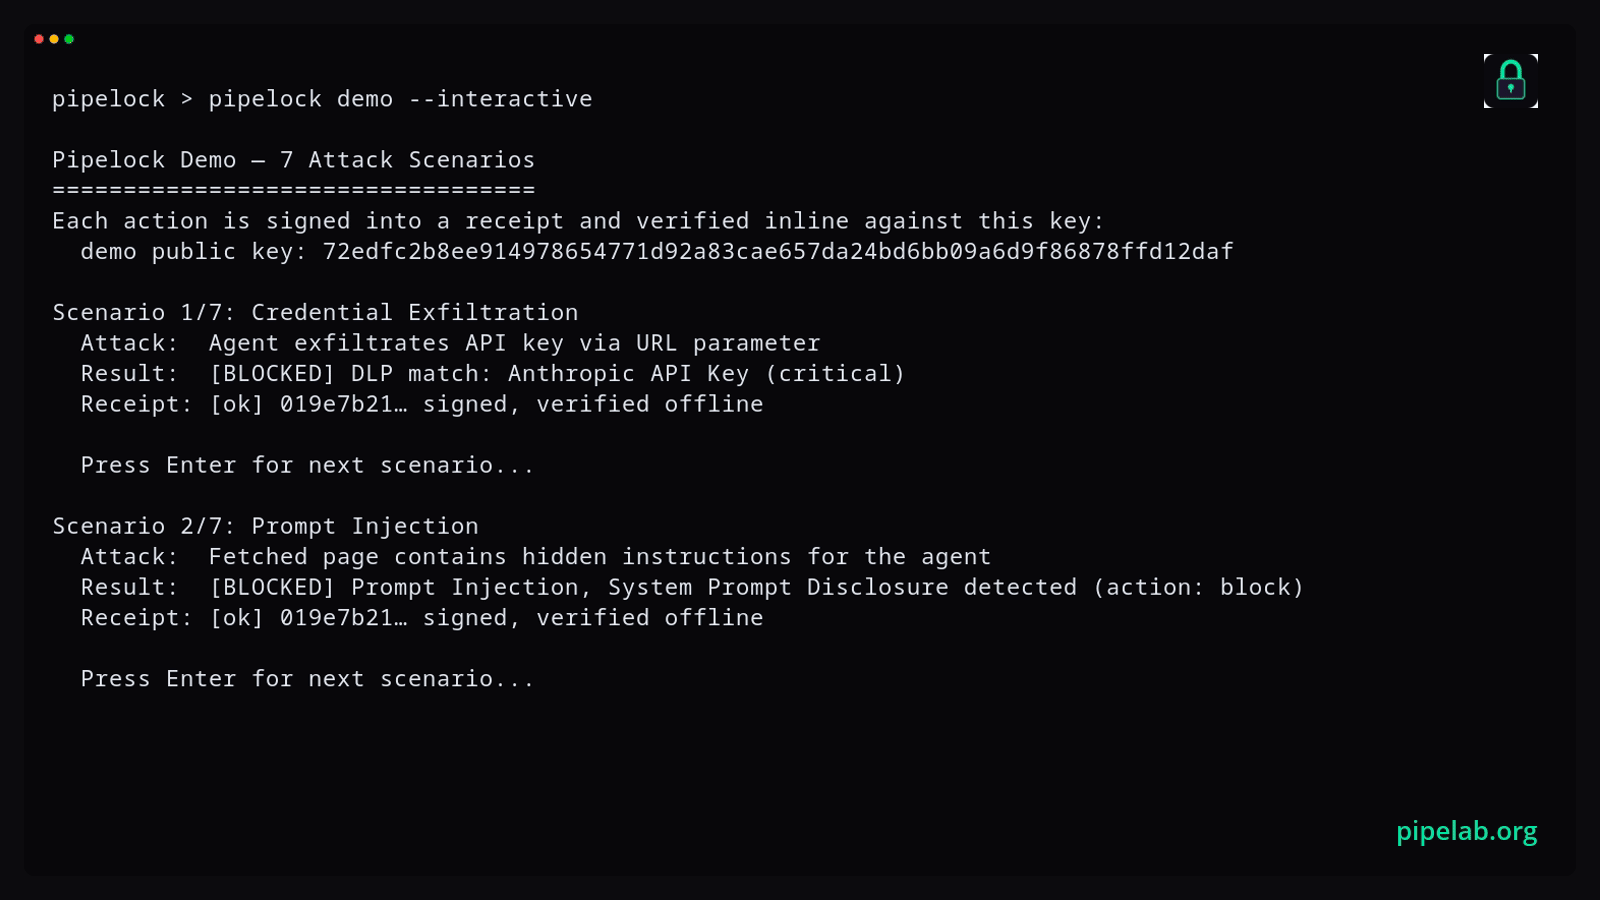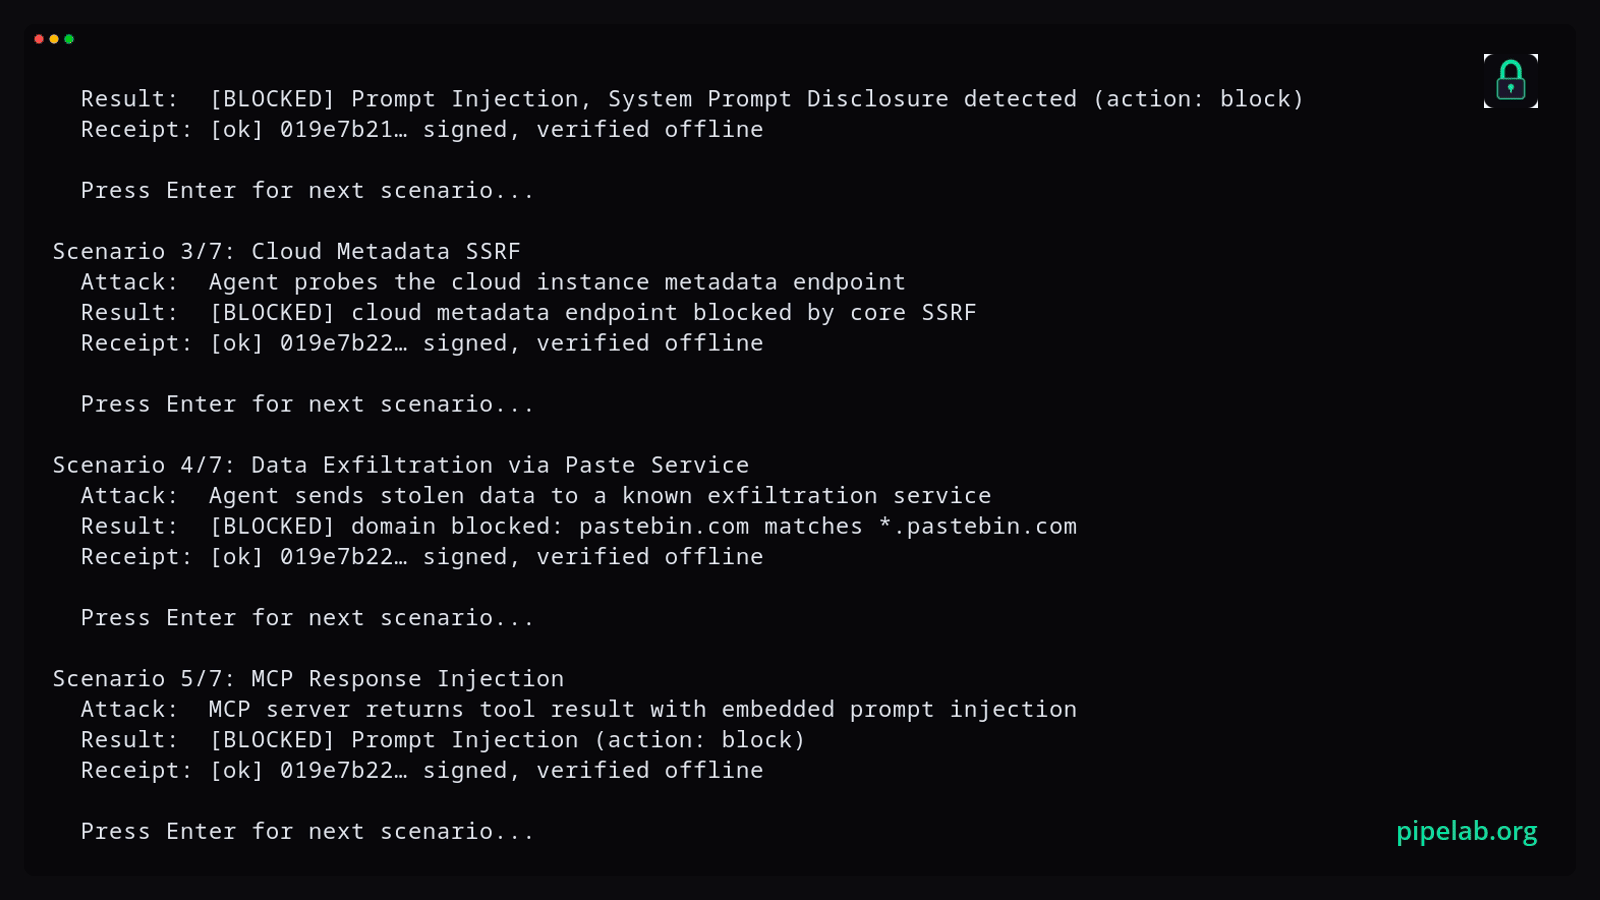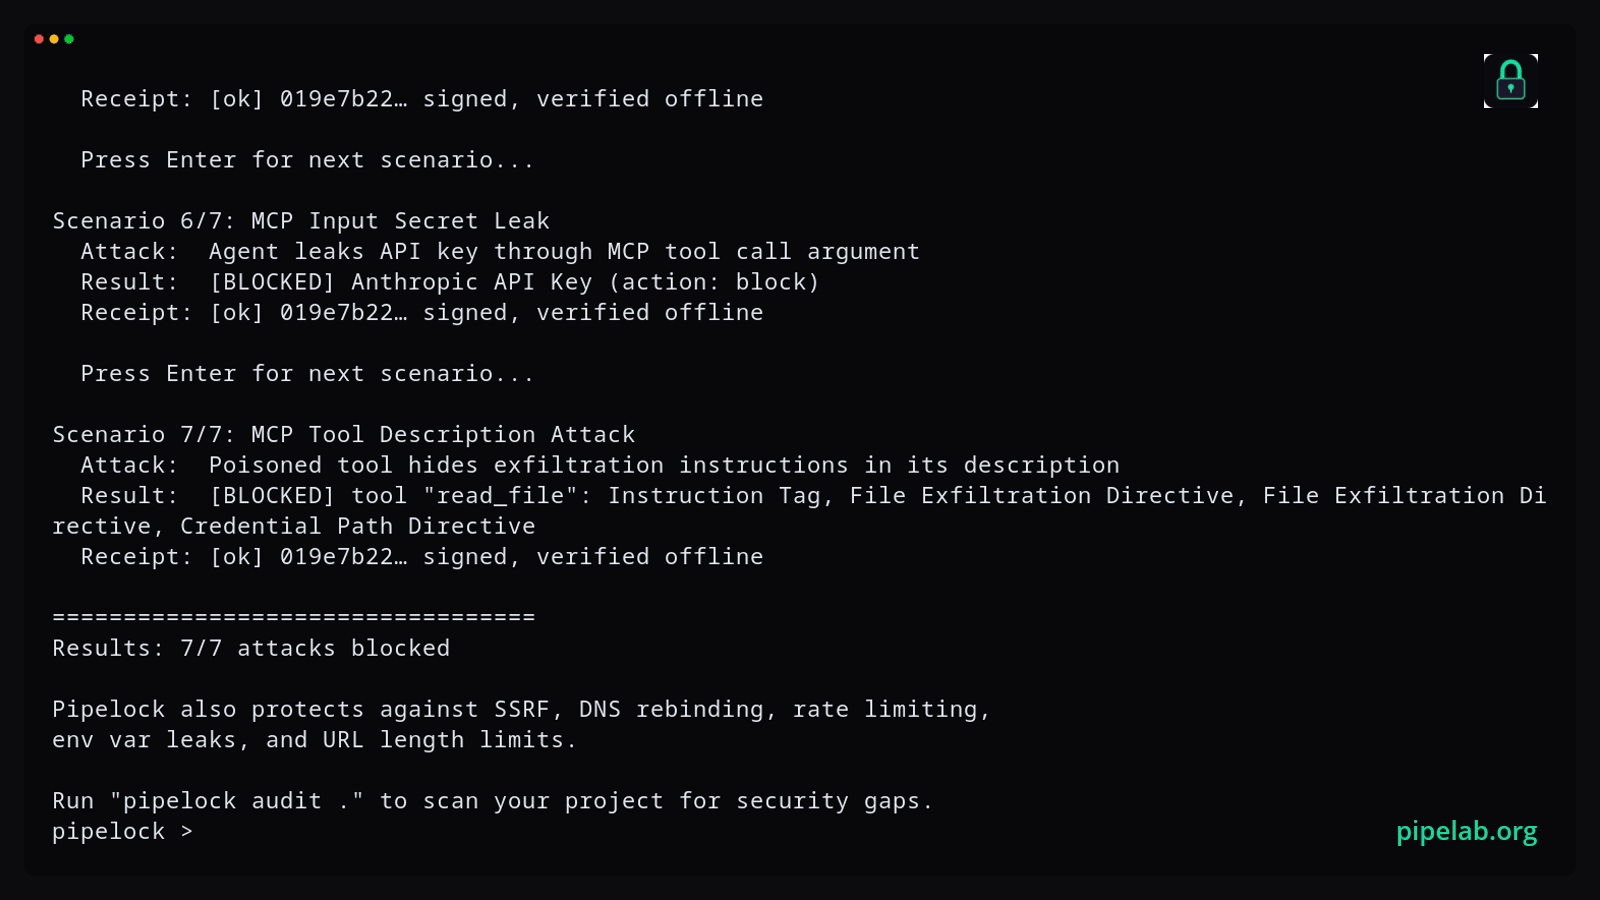
Open-source AI agent firewall that scans HTTP, MCP, A2A, and WebSocket traffic for exfiltration, SSRF, and prompt injection, emitting verifiable…
ai-securityapi-securitycloud-security+8
9077h 59m ago
log4j-finder preview

log4j-finder

GitHubfox-it/log4j-finder

Find vulnerable Log4j2 versions on disk and also inside Java Archive Files (Log4Shell CVE-2021-44228, CVE-2021-45046, CVE-2021-45105)
code-analysisincident-responsestatic-analysis+3
4393 years ago
mediator preview

mediator

GitHublawndoc/mediator

An extensible, end-to-end encrypted reverse shell that works across networks without port forwarding.
command-and-controlencryption-decryption-toolsincident-response+5
1002 years ago
mquire preview

mquire

GitHubtrailofbits/mquire

Zero-dependency Linux memory forensics, leveraging kernel-embedded BTF and kallsyms for type-aware memory analysis without external debug info.
binary-analysisdigital-forensicseducation+8
18520 days ago
Watcher preview

Watcher

GitHubthalesgroup-cert/watcher

AI-powered threat intelligence platform for automated CVE/ransomware monitoring, domain surveillance, data leak detection, and incident response with…
ai-securitydata-exfiltrationdns-subdomain-enumeration+7
1.4k15 days ago
zimbra-cve-2026-73570-ir preview

zimbra-cve-2026-73570-ir

GitHubdahnutz/zimbra-cve-2026-73570-ir

Detection-first incident-response toolkit for Zimbra administrators investigating CVE-2026-73570. Searches logs for exploit indicators, examines…

defensive-toolsdigital-forensicsincident-response+4
11 day ago
paperweight preview

paperweight

GitHubwslyvh/paperweight

Paperweight scans your inbox to map your digital footprint, then helps you take back control and delete your data. Local-first and open source.
data-exfiltrationemail-securityincident-response+5
4561 day ago
react-cve-2025-55182 preview

react-cve-2025-55182

GitHubstonelinks/react-cve-2025-55182

Analysis of malware found on a server compromised via CVE-2025-55182, including obfuscated dropper, C2 communication, persistence mechanisms, and…
command-and-controldata-exfiltrationforensics+6
9 months ago
LockBit-Ransomware-Analysis preview

LockBit-Ransomware-Analysis

GitHubvignesh-hp/lockbit-ransomware-analysis

Threat intelligence and incident response case study on LockBit ransomware exploiting CVE-2023-4966 (Citrix Bleed).

data-exfiltrationdigital-forensicseducation+8
7 months ago
DumpChromeSecrets preview
Archived

DumpChromeSecrets

GitHubmaldev-academy/dumpchromesecrets

Extract data from modern Chrome versions, including refresh tokens, cookies, saved credentials, autofill data, browsing history, and bookmarks
data-exfiltrationdigital-forensicseducation+8
5568 months ago
DeadManSwitch preview

DeadManSwitch

GitHubblacksnufkin/deadmanswitch

DeadManSwitch in rust with several triggers (remote local and network)

data-exfiltrationdefensive-toolsencryption-decryption-tools+4
2710 months ago
log4j_scanner preview

log4j_scanner

GitHubdbzoo/log4j_scanner

Filesystem scanner for Log4Shell (CVE-2021-44228) and related CVEs. Detects vulnerable JAR files via hash matching and class presence. Runs…
code-analysisdevsecopsincident-response+3
44 years ago
copy-fail-CVE-2026-31431-IOC preview

copy-fail-CVE-2026-31431-IOC

GitHubkadir/copy-fail-cve-2026-31431-ioc

Detection, mitigation, and IOC toolkit for Copy Fail CVE-2026-31431 Linux kernel page-cache privilege escalation
forensicsincident-responseintrusion-detection+2
314 months ago
halogen preview
Archived

halogen

GitHubtarget/halogen

Automatically create YARA rules from malicious documents.

forensicsincident-responsemalware-analysis+2
2104 years ago
Previous1234Next