

sleuthkit
 sleuthkit/sleuthkit
Forensic library and CLI toolkit for analyzing disk and file system images, recovering deleted data, generating timelines, and validating evidence…
data-recoverydigital-forensicsdisk-forensics+3
3.2k
sleuthkit/sleuthkitForensic library and CLI toolkit for analyzing disk and file system images, recovering deleted data, generating timelines, and validating evidence…
 microsoft/avml
Portable Linux RAM acquisition tool for forensics and incident response, capturing LiME-compatible images with optional compression and remote…
 google/hashr
Builds forensic file hash sets from disk images, packages, and archives across GCP, AWS, and local sources, with deduplication and PostgreSQL/Spanner…
 freedomofpress/dangerzone
Take potentially dangerous PDFs, office documents, or images and convert them to safe PDFs
 roxanne_ardary/emailxpose
EmailXpose is an open source AI-powered email security system that detects phishing, spam, scams, malware, and social engineering attacks. It goes…
 aradhyacp/secflow
AI-driven automated threat analysis pipeline that routes files, URLs, IPs, domains, or images through specialized security analyzers and generates…
 dtact/divd-2021-00038--log4j-scanner
Recursive vulnerability scanner for Log4j CVEs in archives and Docker images. Detects JndiLookup.class and vulnerable versions via SHA256 hashes,…
 qixils/anticropalypse
Discord bot for mitigating the aCropalypse vulnerability (CVE-2023-21036, CVE-2023-28303) by retroactively deleting vulnerable images
 adem-hosni/mappedimagesdetector
Lightweight native Windows memory scanner for AV/EDR platforms, detecting suspicious mapped images and manual DLL injection techniques by IAT thunk
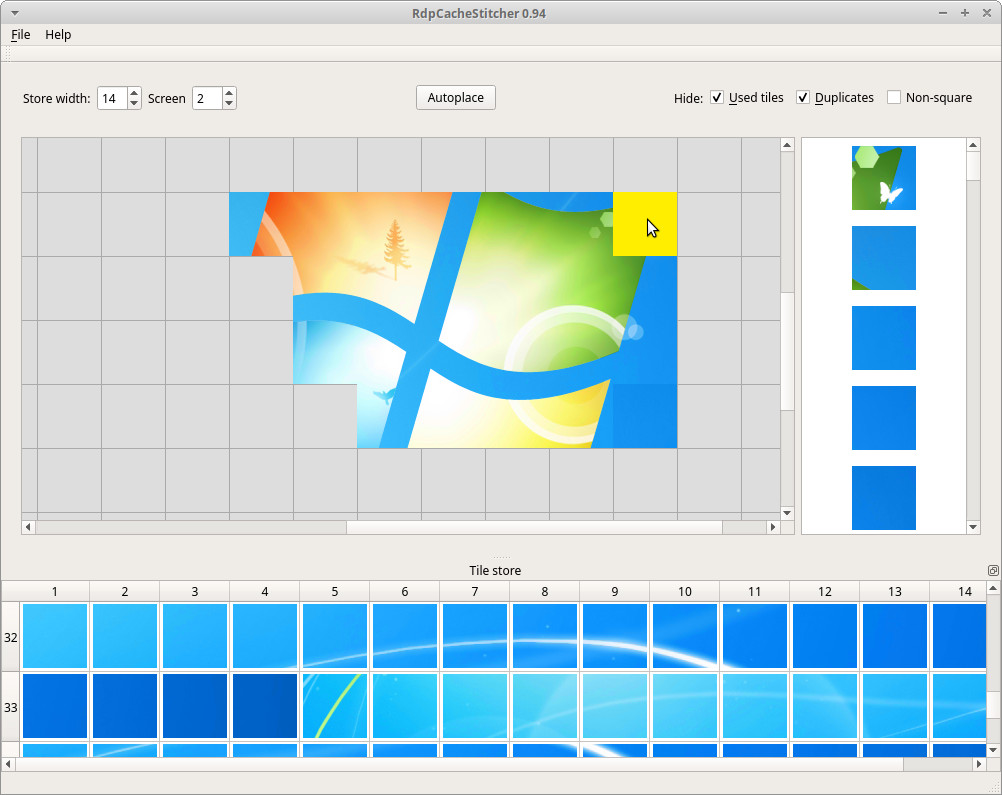 bsi-bund/rdpcachestitcher
RdpCacheStitcher is a tool that supports forensic analysts in reconstructing useful images out of RDP cache bitmaps.
 ncsc-nl/citrix-2025
Digital forensics and incident response tool using YARA rules to scan Citrix NetScaler core dumps, disk images, and live hosts for signs of…
 crowdstrike/supermem
A python script developed to process Windows memory images based on triage type.
 skelsec/adiskreader-secretsdump
Extract registry and NTDS secrets from local or remote disk images
 kamalsrini/sentinel-cve
CLI tool that explains CVEs in plain English and scans repos for impact. Powered by Claude.
 knqyf263/aqua-checksums
Monitors cryptographic integrity of container images, releases, and Git tags for supply chain security, verifying Sigstore cosign signatures with…
 everest90909/yellowkey-winre-remediation
PowerShell-based Intune remediation package that detects and removes the vulnerable autofstx.exe BootExecute entry from offline WinRE images, then…