
WhacAMole
 ignacioj/whacamole
Live memory analysis detecting malware IOCs in processes, modules, handles, tokens, threads, .NET assemblies, memory address space and environment…
binary-analysisdebuggersdigital-forensics+9
ignacioj/whacamoleLive memory analysis detecting malware IOCs in processes, modules, handles, tokens, threads, .NET assemblies, memory address space and environment…
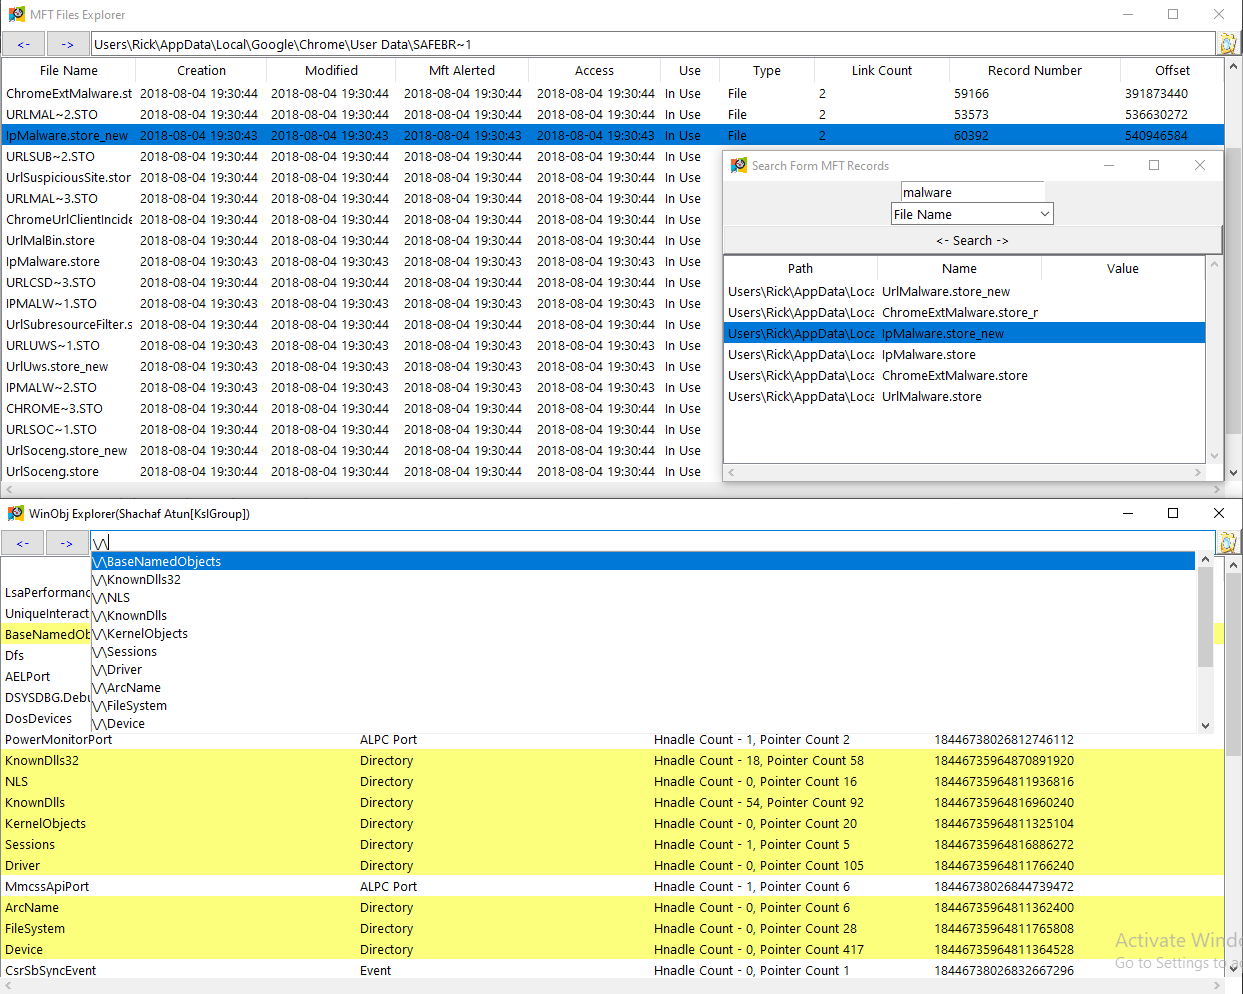 memoryforensics1/volexp
volatility explorer (volatility 2)
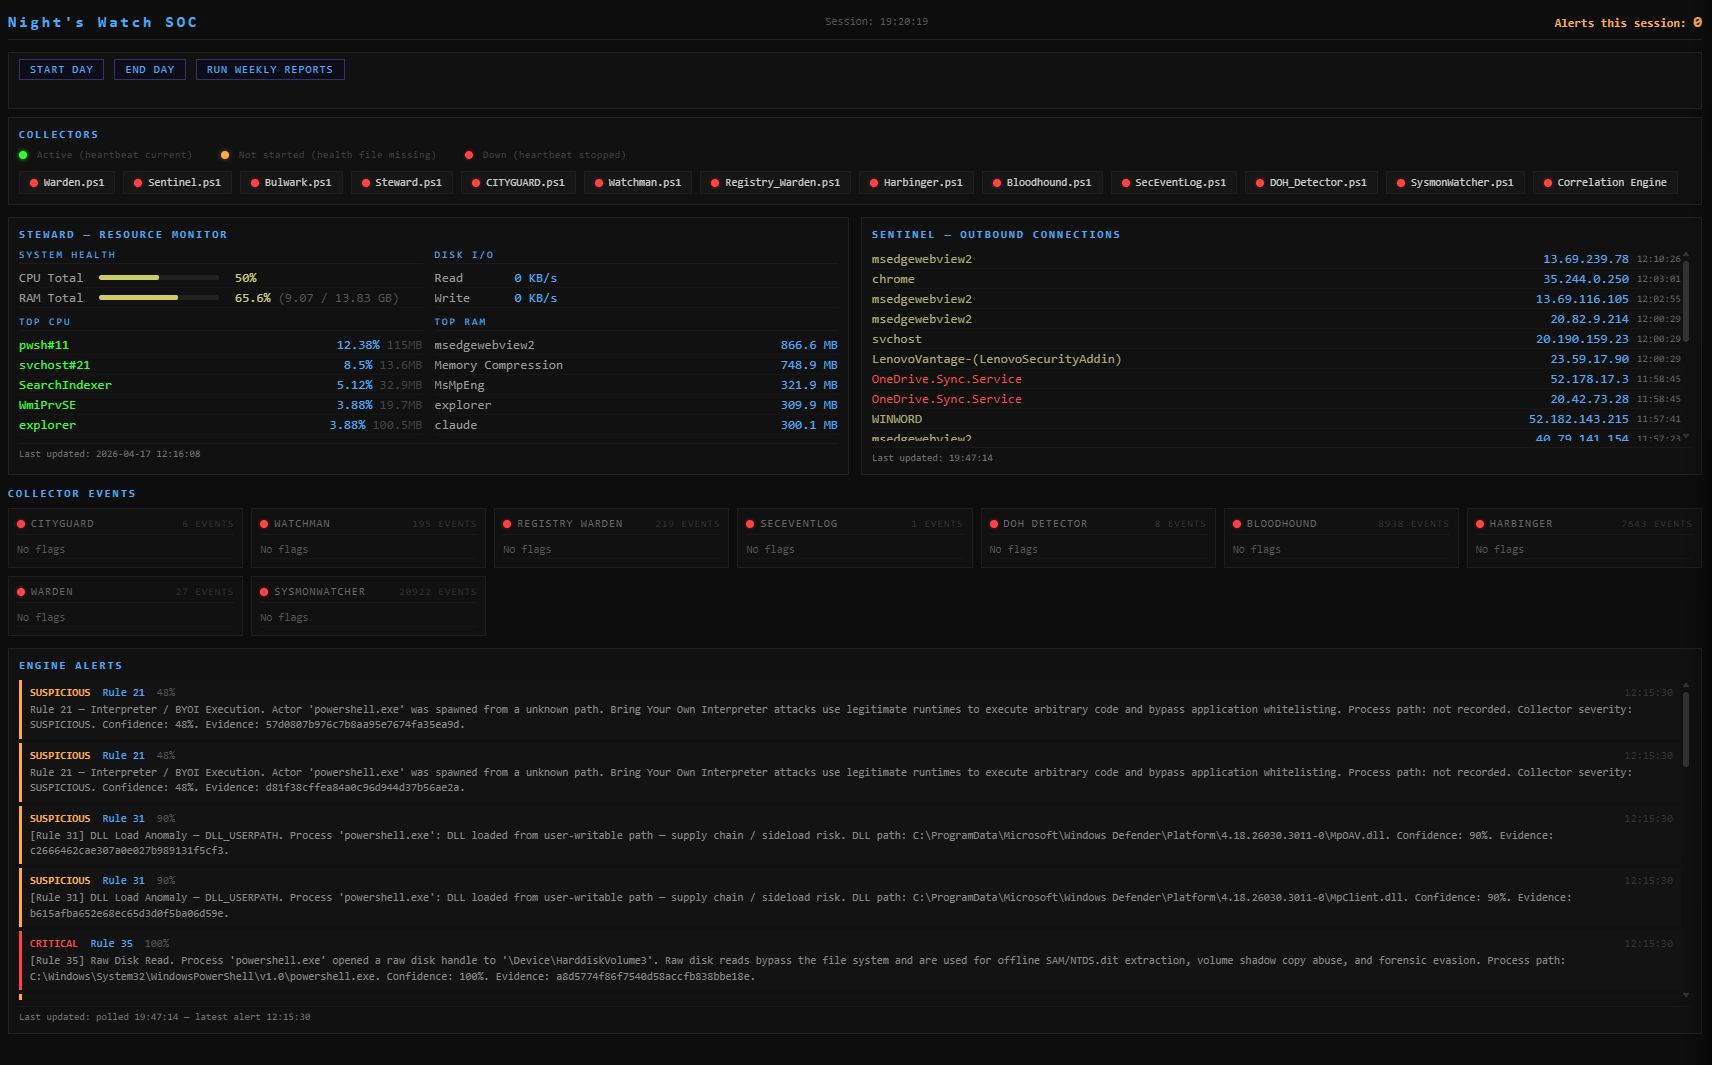 nate-ryan-7690/home_soc_suite
A personal Windows SOC suite built in PowerShell — monitors network connections, resource usage, scheduled tasks and power events with severity…
 harshavmb/fim-ebpf
A lightweight eBPF program to monitor file creation and modification events on Linux. This tool leverages eBPF (Extended Berkeley Packet Filter) to…
 suenerve/cve-2022-30190-follina-patch
The CVE-2022-30190-follina Workarounds Patch
 bontchev/whodunit
Recognizing the most likely APT groups responsible for an incident