
cowrie
 cowrie/cowrie
Cowrie SSH/Telnet Honeypot https://docs.cowrie.org/
defensive-toolsincident-responseinformation-gathering+3
6.5k6 days ago
cowrie/cowrieCowrie SSH/Telnet Honeypot https://docs.cowrie.org/
 gamelinux/passivedns
A network sniffer that logs all DNS server replies for use in a passive DNS setup
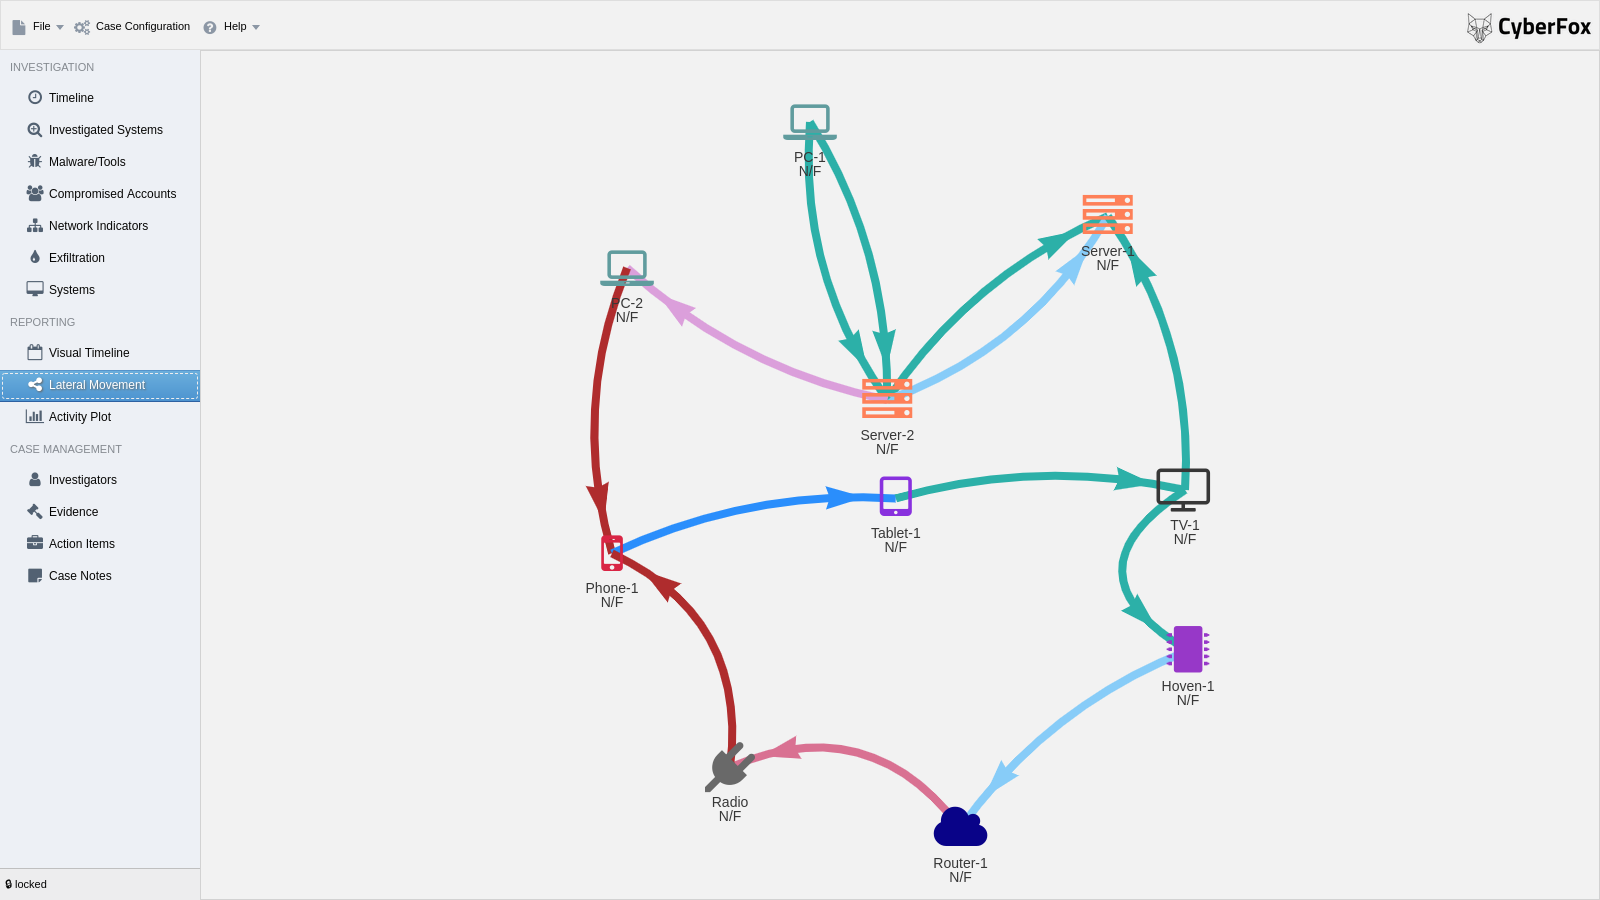 cyb3rfox/aurora-incident-response
Incident Response Documentation made easy. Developed by Incident Responders for Incident Responders
 backbay-labs/thrunt-god
Threat hunting command system for agentic IDEs
 abdaullahag/threatlens
Python CLI tool for rapid IOC analysis (IPs, Domains, CVEs) using 6 free Threat Intel APIs. Outputs: Color-coded Excel, JSON, CSV. Uses: VT, Shodan,…
 zdhenard42/soc-multitool
A powerful and user-friendly browser extension that streamlines investigations for security professionals.
 ab2pentest/macosthreattrack
Bash tool used for proactive detection of malicious activity on macOS systems.
 pjlantz/hale
Botnet command & control monitor
 zomato/vinifera
A GitHub recon/monitoring tool for finding internal leaks belonging to your organisation.
 adrecon/adrecon
PowerShell tool that extracts Active Directory artifacts via LDAP or ADWS and generates Excel reports for auditing, DFIR, and penetration testing.
 viralmaniar/remote-desktop-caching-
This tool allows one to recover old RDP (mstsc) session information in the form of broken PNG files. These PNG files allows Red Team member to…
 tclahr/uac
Portable, dependency-free incident response tool that automates forensic artifact collection from Unix-like systems, including memory acquisition,…
 hackinghippo/log4shell_ioc_ips
log4j / log4shell IoCs from multiple sources put together in one big file (IPs) more coming soon (CVE-2021-44228)
 perplexityai/bumblebee
Read-only developer endpoint scanner for on-disk package, extension, and developer-tool metadata, built to check exposure to known software…
 silverfort-open-source/latma
Collects and analyzes AD and Azure AD authentication logs to detect lateral movement attacks using graph-based anomaly detection, visualizing…
 foospidy/honeypy
A low to medium interaction honeypot.
 captaingeech42/ransomwatch
Ransomware leak site monitoring
 xephora/threat-remediation-scripts
This repository contains a list of new remediation scripts.