
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
44 results
TTPForge preview

TTPForge

GitHubfacebookincubator/ttpforge

The TTPForge is a Cybersecurity Framework for developing, automating, and executing attacker Tactics, Techniques, and Procedures (TTPs).

adversarial-attackincident-responsepenetration-testing-frameworks+2
444
1 month ago
grr preview

grr

GitHubgoogle/grr

Remote live forensics and incident response framework with Python agent for collecting forensic data from endpoints, including memory, disk, and…
digital-forensicsdisk-forensicsforensics+4
5.1k4 months ago
aiiroverlay preview

aiiroverlay

GitHubjacobideji/aiiroverlay

AI IR Overlay™ — practical incident response framework for AI agents in production. Built on NIST SP 800-61 r3, mapped to NIST AI RMF, NIST CSF 2.0,…
ai-securitycloud-securitycurated-resources+4
32 months ago
attackgen preview

attackgen

GitHubmrwadams/attackgen

AttackGen is a cybersecurity incident response testing tool that leverages the power of large language models and the comprehensive MITRE ATT&CK…
ai-securityctfeducation+5
1.2k3 days ago
ics-forensics-tools preview

ics-forensics-tools

GitHubmicrosoft/ics-forensics-tools

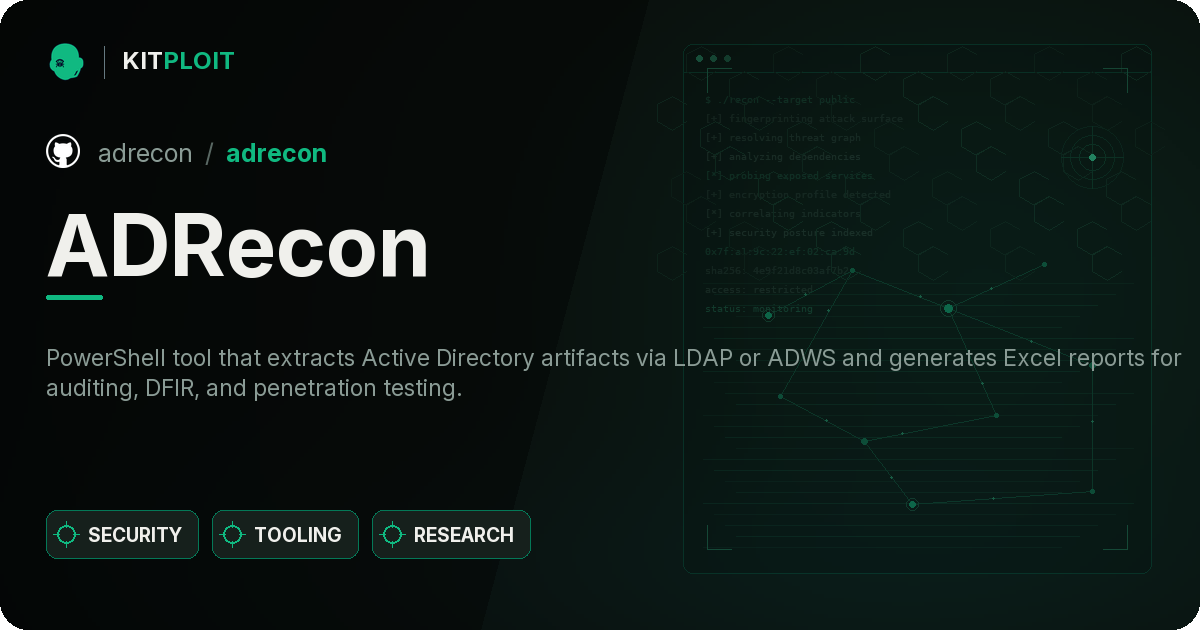
Open-source forensics framework for analyzing Industrial PLC metadata and project files. Scans for suspicious artifacts in ICS environments to…
digital-forensicsforensicsincident-response+2
3741 year ago
ADRecon preview

ADRecon

GitHubadrecon/adrecon

PowerShell tool that extracts Active Directory artifacts via LDAP or ADWS and generates Excel reports for auditing, DFIR, and penetration testing.

defensive-toolsdigital-forensicsincident-response+6
9811 year ago
rita preview

rita

GitHubactivecm/rita

Real Intelligence Threat Analytics (RITA) is a framework for detecting command and control communication through network traffic analysis.

anomaly-detectioncommand-and-controldns-analysis+4
6423 months ago
DIAL preview

DIAL

GitHubcred-club/dial

Event-driven AWS security misconfiguration detection framework that monitors multiple accounts in real-time, triggering alerts via Lambda for IAM,…
cloud-infrastructure-securitycloud-securitydefensive-tools+2
954 years ago
LEAF preview

LEAF

GitHubalex-cart/leaf

Linux Evidence Acquisition Framework

digital-forensicsdisk-forensicsforensics+5
1201 year ago
vol-rs preview

vol-rs

GitHubdaffainfo/vol-rs

Volatility 3 ported to Rust. Same output, much faster.

digital-forensicsforensicsincident-response+3
18513 days ago
Crescendo preview

Crescendo

GitHubsuprhackersteve/crescendo

Crescendo is a swift based, real time event viewer for macOS. It utilizes Apple's Endpoint Security Framework.
defensive-toolsincident-response
1.1k6 years ago
volatility preview
Archived

volatility

GitHubvolatilityfoundation/volatility

An advanced memory forensics framework

digital-forensicsforensicsincident-response+4
8.1k1 year ago
osquery preview

osquery

GitHubosquery/osquery

SQL powered operating system instrumentation, monitoring, and analytics.
anomaly-detectiondefensive-toolsemail-security+8
23.6k18h 57m ago
aftermath preview

aftermath

GitHubjamf/aftermath

Swift-based macOS incident response framework for collecting and analyzing host artifacts, including filesystem timestamps, browser data, unified…

digital-forensicsforensicsincident-response+3
5991 year ago
volatility3 preview

volatility3

GitHubvolatilityfoundation/volatility3

Advanced framework for extracting digital artifacts from volatile memory (RAM) samples, enabling deep forensic analysis of system runtime state…
digital-forensicsforensicsincident-response+2
4.4k7 days ago
cynative preview

cynative

GitHubcynative/cynative

Read-only AI agent that queries your cloud, code, and runtime infrastructure to surface misconfigurations, leaked secrets, and privilege escalation…
ai-securitycloud-securitycontainer-security+7
20720h 15m ago
beelzebub preview

beelzebub

GitHubbeelzebub-labs/beelzebub

A secure low code deception runtime framework, leveraging AI for System Virtualization.
ai-securityapi-securitycontainer-security+7
2.2k4 days ago
agentic-threat-hunting-framework preview

agentic-threat-hunting-framework

GitHubnebulock-inc/agentic-threat-hunting-framework

ATHF is a framework for agentic threat hunting - building systems that can remember, learn, and act with increasing autonomy.

ai-securityeducationincident-response+7
37819h 1m ago
Previous123Next