

bettercap
 bettercap/bettercap
The Swiss Army knife for 802.11, BLE, HID, CAN-bus, IPv4 and IPv6 networks reconnaissance and MITM attacks.
bluetooth-securitydata-exfiltrationfingerprint-spoofing+16
19.8k
bettercap/bettercapThe Swiss Army knife for 802.11, BLE, HID, CAN-bus, IPv4 and IPv6 networks reconnaissance and MITM attacks.
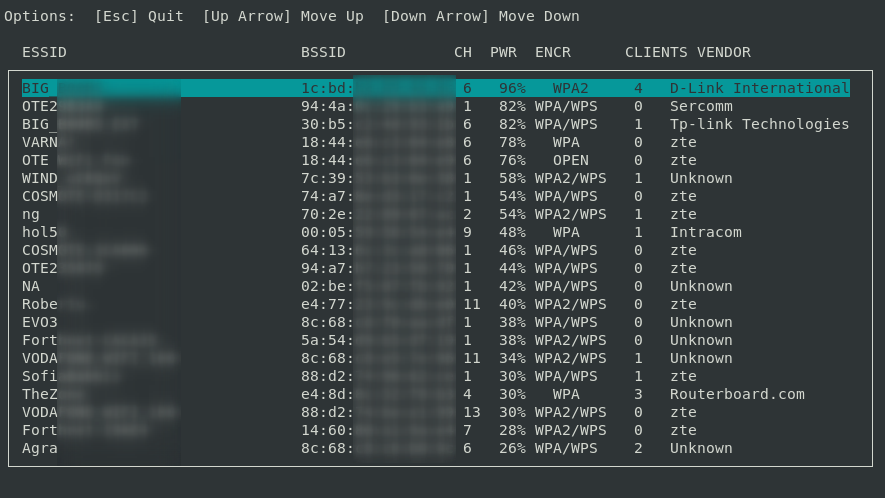 wifiphisher/wifiphisher
Rogue Access Point framework for red team engagements and Wi-Fi security testing. Performs Evil Twin, KARMA, and Known Beacons attacks to achieve…
 venomous/cloudscraper
A Python module to bypass Cloudflare's anti-bot page.
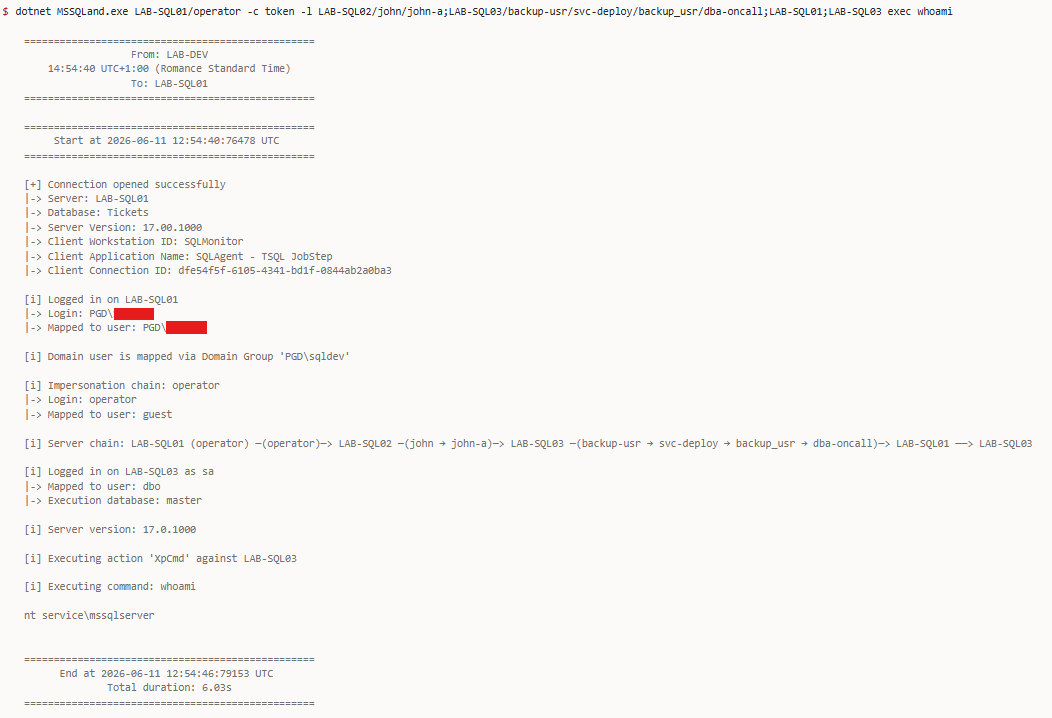 n3rada/mssqland
In-target C# post-exploitation and exploitation tool for Microsoft SQL Server (MS SQL / MSSQL) traversing linked-server chains of any depth with…
 0x574r/darkcloak
Linux process identity cloaking tool that spoofs comm, argv, cmdline, environ, exe path, and VMAs via an 11-phase prctl pipeline to impersonate…
 priyankvadaliya/hack-captive-portal
This script helps to pass through the captive portals in public Wi-Fi networks. It hijacks IP and MAC from somebody who is already connected and…
 kernelfl00d/incriminator
Incriminator is an OpenSource Project with educational purposes that allows you to incriminate other devices during a cybercrime.
 cappricio-securities/camjacking
CamJacking is a tool designed for use in human penetration testing tool. It is intended to simulate potential security threats by testing the…
 paulpierre/informer
A Telegram Mass Surveillance Bot in Python
 breakfix/sharpscom
A C# utility for interacting with SCOM
 dtrecherel/dnsspoof
A DNS spoofer tool written in Python3.
 kevin-robertson/inveighzero
.NET IPv4/IPv6 machine-in-the-middle tool for penetration testers
 gar-re/cve-2022-27438
Proof-of-concept exploit for CVE-2022-27438, demonstrating remote code execution via spoofed update server in Advanced Installer 19.3. Includes DNS…
 eliangonzi00/pockeycloakcve-2023-0264
Proof-of-concept exploit for CVE-2023-0264 (Keycloak OIDC session hijacking) with a frontend for session_id substitution and an agent that detects…
 initstring/evil-ssdp
Spoof SSDP replies and create fake UPnP devices to phish for credentials and NetNTLM challenge/response.

 alperenugurlu/nac_bypass_agent
This function combines all the above functions and takes necessary information from the user to change the IP and MAC address, start the responder…