
TamperingSyscalls
 rad9800/tamperingsyscalls
C++ library that retrieves and spoofs Windows syscall arguments using hardware breakpoints and exception handlers to subvert EDR telemetry.
ids-ips-evasionpayload-developmentpost-exploitation+1
508
rad9800/tamperingsyscallsC++ library that retrieves and spoofs Windows syscall arguments using hardware breakpoints and exception handlers to subvert EDR telemetry.
 xyrem/hyperdeceit
HyperDeceit is the ultimate all-in-one library that emulates Hyper-V for Windows, giving you the ability to intercept and manipulate operating system…
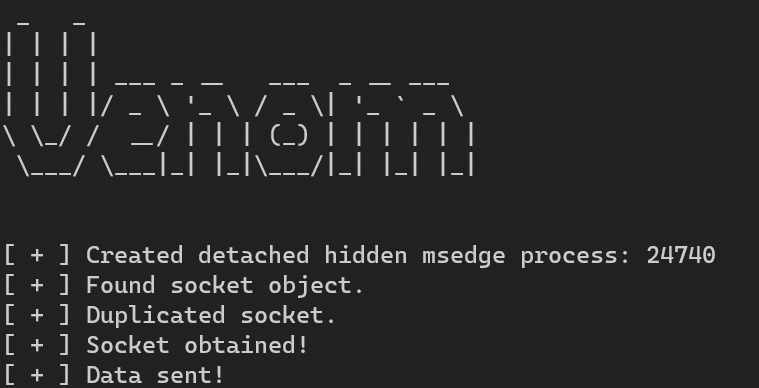 idov31/venom
Venom is a library that meant to perform evasive communication using stolen browser socket
 hwbp/lazyhook
Evade behavioral analysis by executing malicious code within trusted Microsoft call stacks, patchless hooking library IAT/EAT.