
nimvoke
 nbaertsch/nimvoke
Indirect syscalls + DInvoke made simple.
ids-ips-evasionpayload-developmentpost-exploitation+2
nbaertsch/nimvokeIndirect syscalls + DInvoke made simple.
 initconf/cve-2021-1675-printnightmare
Zeek package to detect CVE-2021-1675 (PrintNightmare) by monitoring named pipes and RPC operations for spoolss exploitation attempts.
 lloydlabs/process-enumeration-stealth
Stealth Windows process enumeration PoC that lists PIDs using NTFS via NtQueryInformationFile, bypassing standard monitoring APIs and enabling EDR…
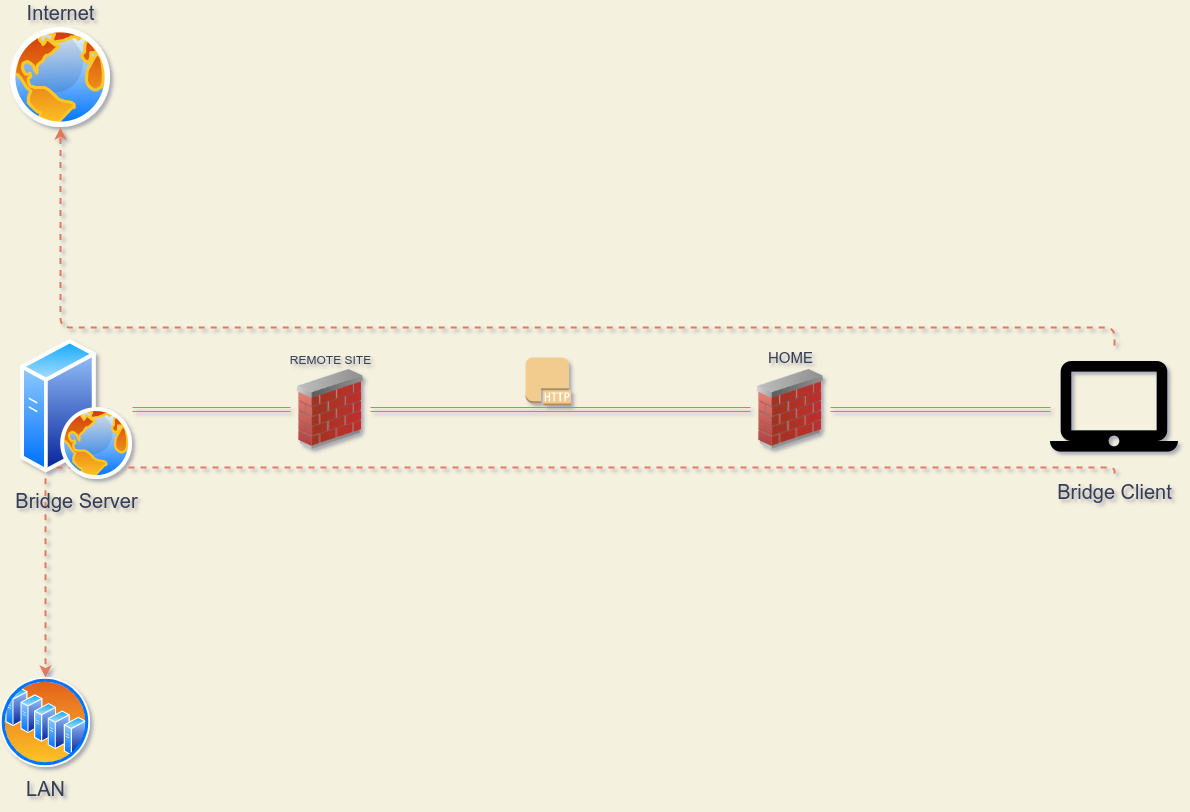 alejandro-llanes/http_bridge
SOCKS5-to-HTTP proxy bridge that tunnels arbitrary TCP streams (SSH, SMTP, TLS) through standard HTTP requests, enabling network traffic obfuscation…
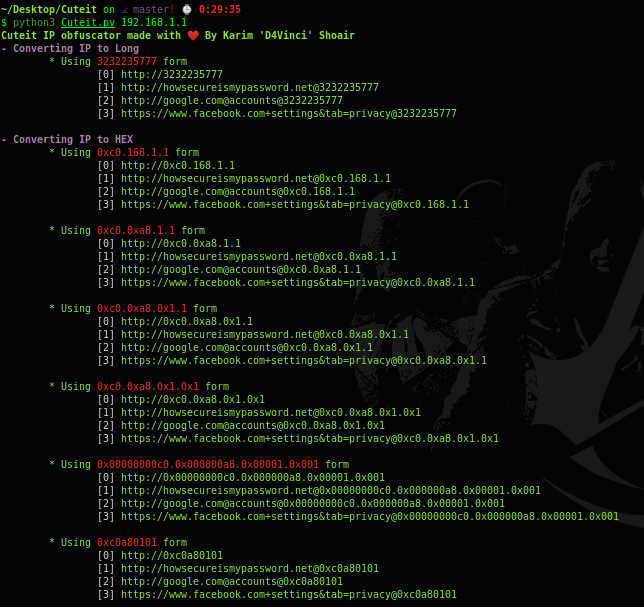 d4vinci/cuteit
IP obfuscator made to make a malicious ip a bit cuter
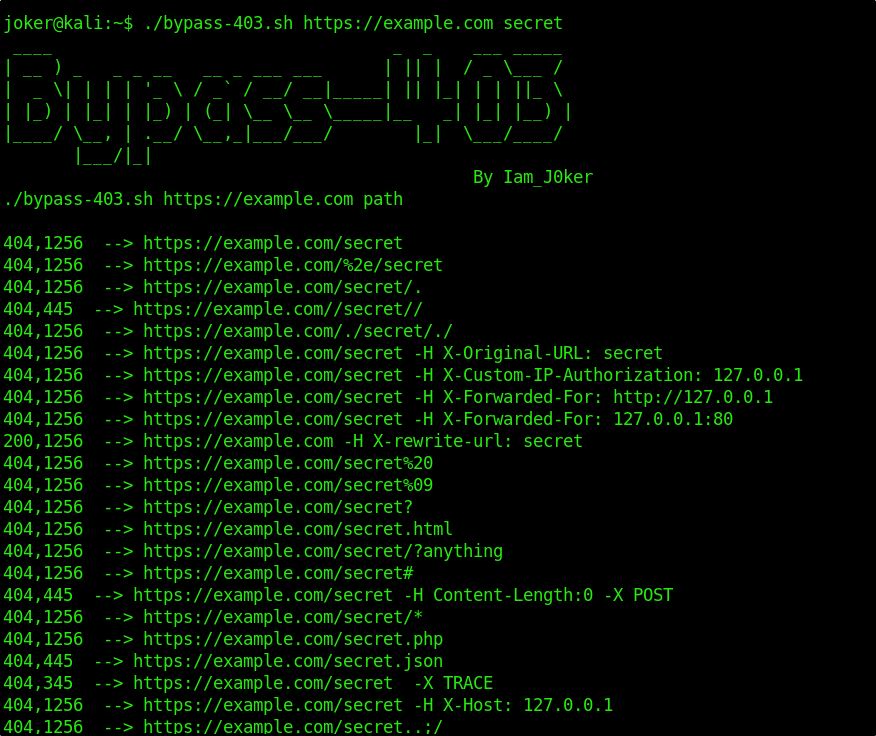 iamj0ker/bypass-403
A simple script just made for self use for bypassing 403
 s4ntiagop/freebokuloader
A simple BOF that frees UDRLs
 nicholasadamou/minipwner
A script to configure a TP-Link MR3040 running OpenWRT into a simple, yet powerful penetration-testing "dropbox".
 pard0p/callstackspoofingpoc
C++ self-Injecting dropper based on various EDR evasion techniques.
 v-p-b/pecloakcapstone
Platform independent peCloak fork based on Capstone
 nullsection/chisel-ng
Chisel new generation, written in rust. SSH under WSS with some customization.
 aiexz/cve-2025-66478-kinda-waf
Let's help websites stay safe until they are properly patched!
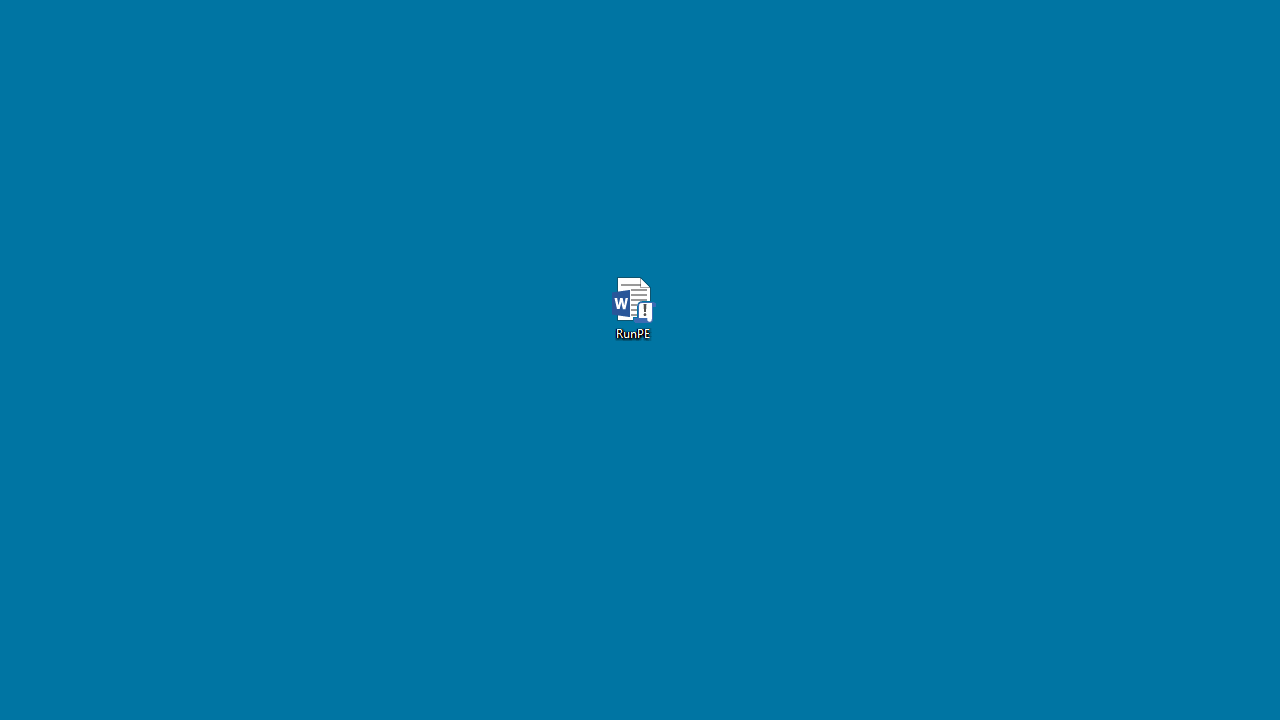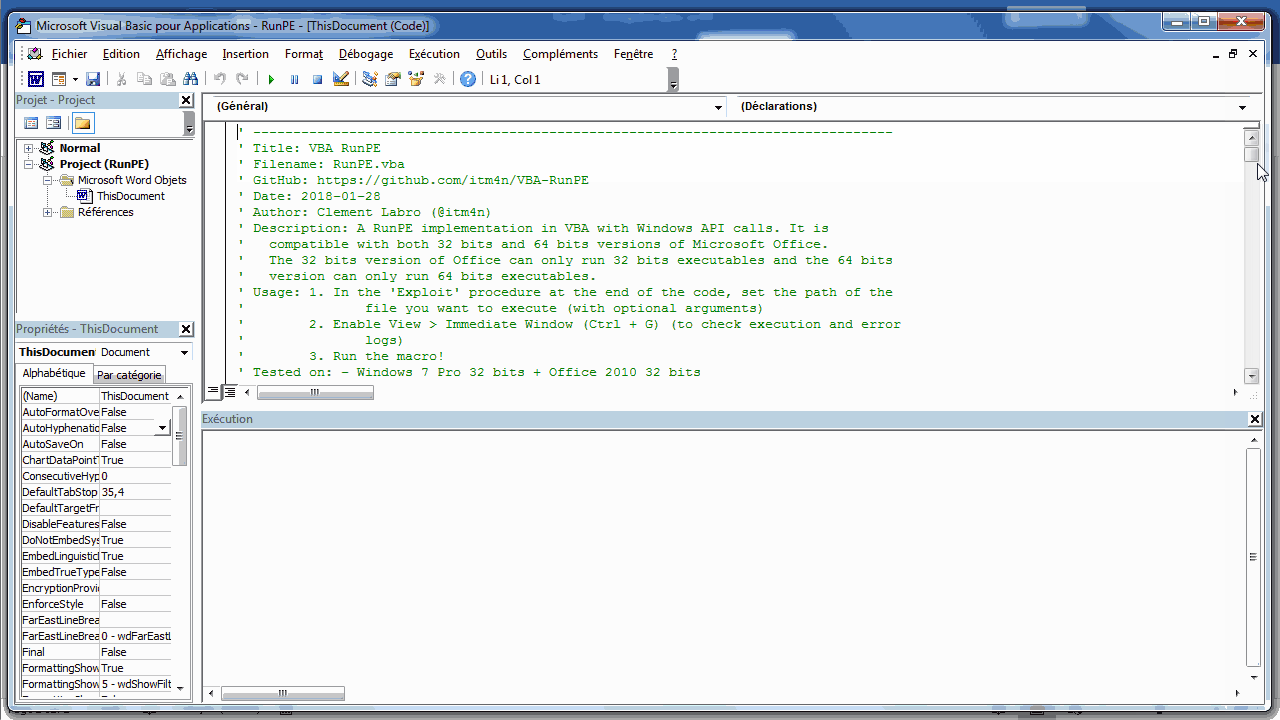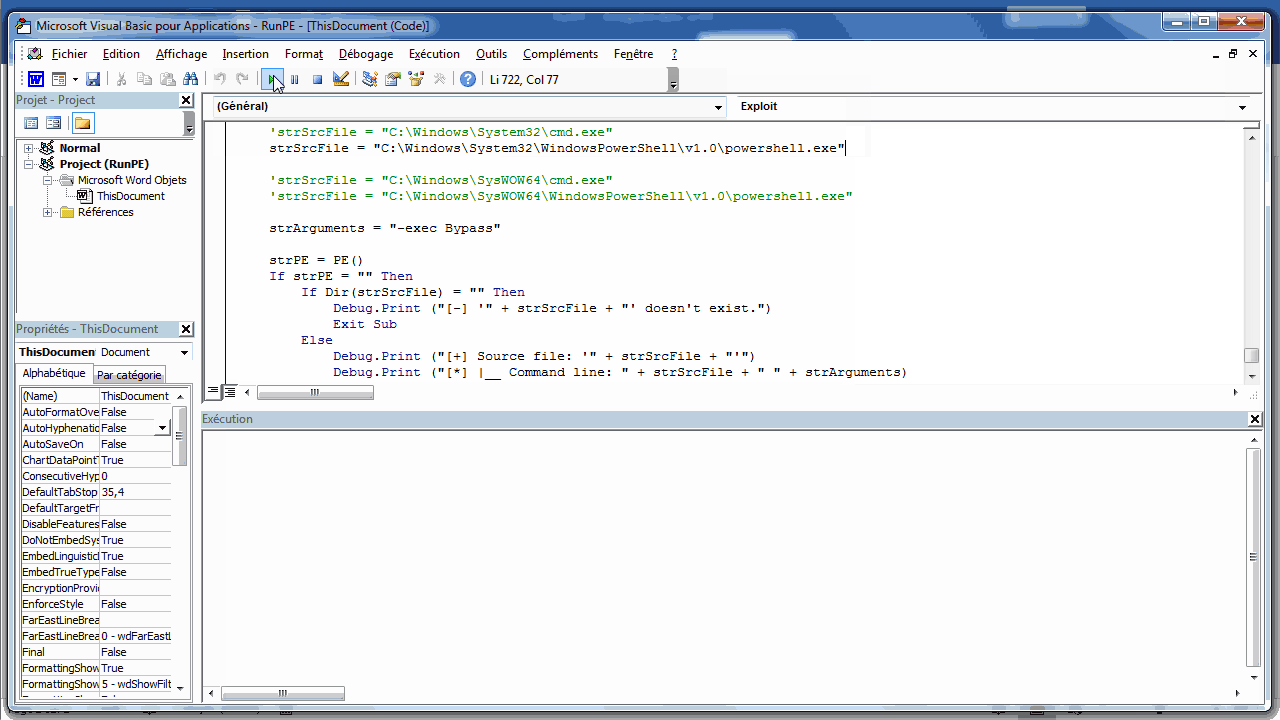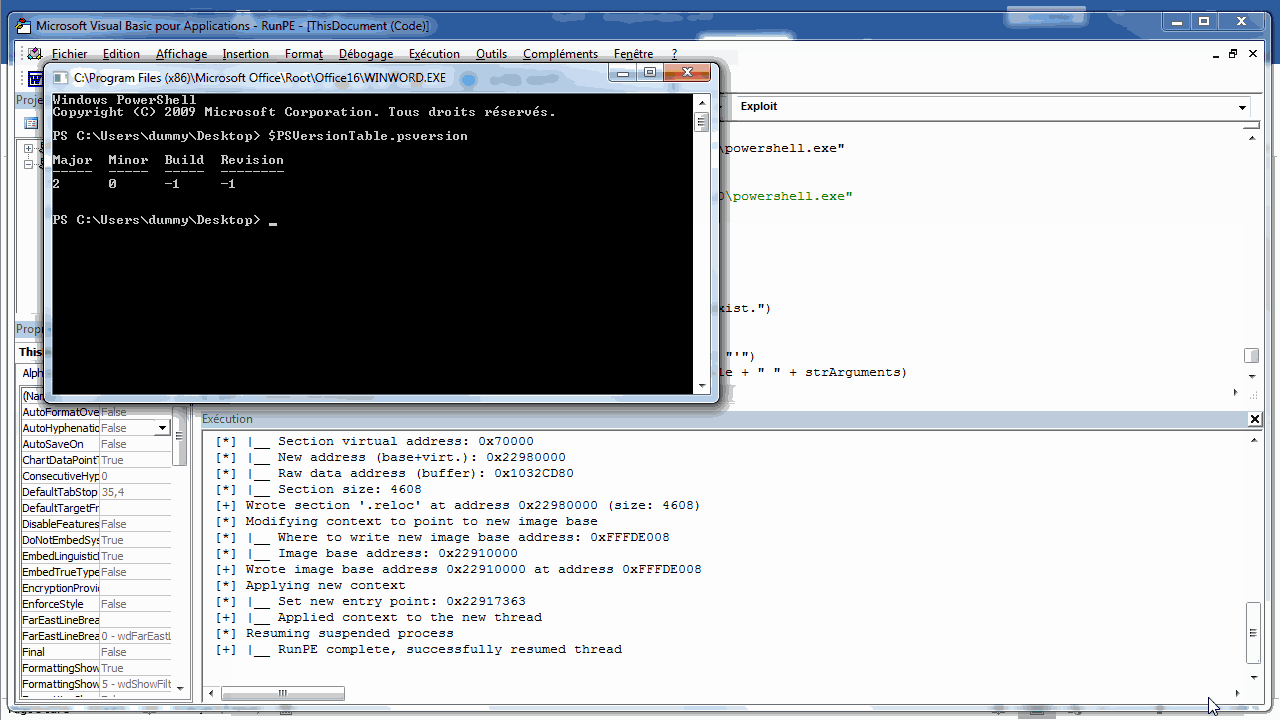 itm4n/vba-runpe
A VBA implementation of the RunPE technique or how to bypass application whitelisting.
 opnsense/core
OPNsense GUI, API and systems backend
 0xpthree/next.js_cve-2025-29927
Reproduces CVE-2025-29927 middleware authorization bypass in Next.js 14.2.24 and demonstrates exploitation with curl to bypass authentication and…
 nyan-x-cat/lime-rat
LimeRAT | Simple, yet powerful remote administration tool for Windows (RAT)
 wecooperate/imonitorsdk
The world's most powerful System Activity Monitor Engine · 一款功能强大的终端行为采集防御开发套件 ~ 旨在帮助EDR、零信任、数据安全、审计管控等终端安全软件可以快速实现产品功能,…
 ekamsinghwalia/detection-and-mitigation-script-for-cve-2021-42717
Detection and Mitigation script for CVE-2021-42717 -> ModSecurity DoS Vulnerability in JSON Parsing