
sniffles
 petabi/sniffles
Sniffles: Packet Capture Generator for IDS and Regular Expression Evaluation
fuzzingids-ips-evasionintrusion-detection+3
66
petabi/snifflesSniffles: Packet Capture Generator for IDS and Regular Expression Evaluation
 4n4s4zi/tfo-connect-bypass
Using TCP Fast Open to bypass syscall-based networking rules (CVE-2026-63828/CVE-2026-72243 PoC)
 x011/smtp-tunnel-proxy
A high-speed covert tunnel that disguises TCP traffic as SMTP email communication to bypass Deep Packet Inspection (DPI) firewalls.
 secdev/scapy
Python-based interactive packet manipulation library for forging, decoding, sending, capturing, and analyzing network packets across a wide range of…
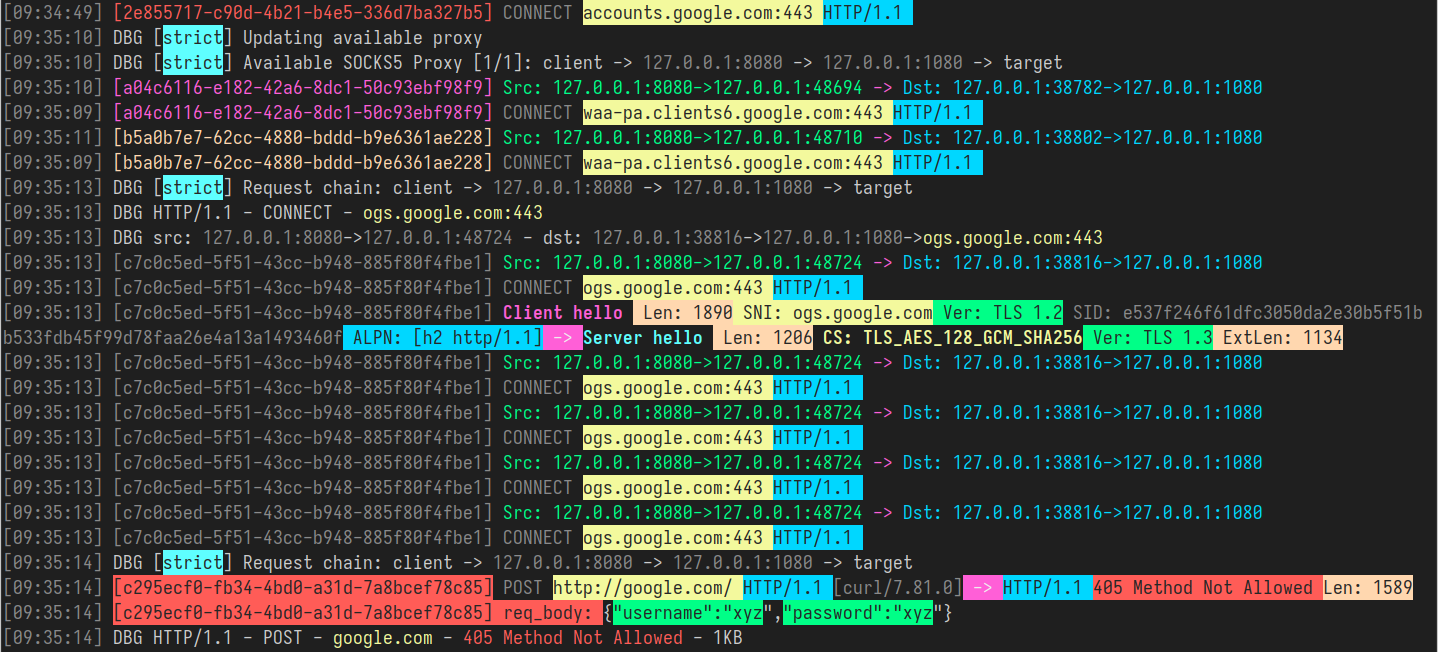 shadowy-pycoder/go-http-proxy-to-socks
CLI MITM proxy that converts SOCKS4/SOCKS5 into HTTP/HTTPS/HTTP2/HTTP3 proxy with transparent TCP/UDP redirection, ARP/NDP/DNS spoofing, traffic…
 dovecoteescapee/byedpiandroid
Android VPN-based local proxy that bypasses Deep Packet Inspection (DPI) and censorship by redirecting all traffic through a SOCKS5 tunnel without…
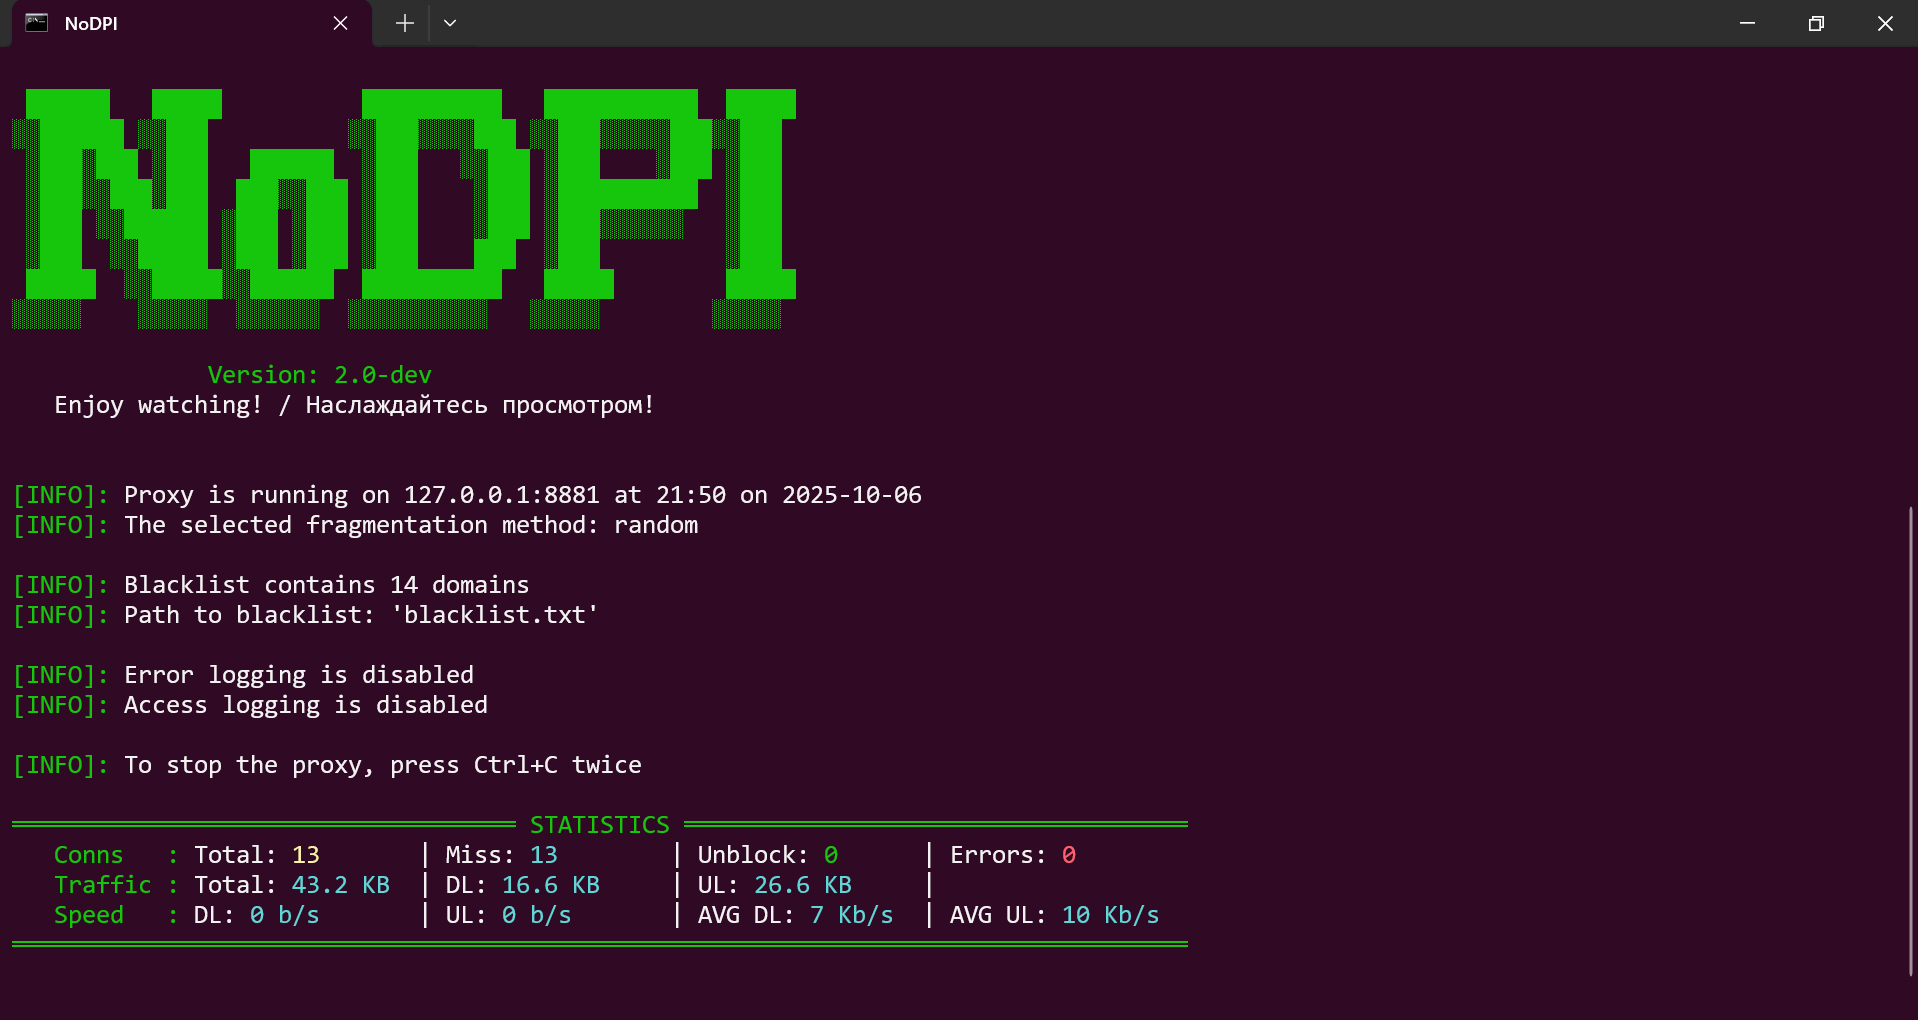 gvcoder09/nodpi
Local proxy that bypasses Deep Packet Inspection by fragmenting TLS ClientHello packets, enabling access to blocked websites without requiring…
 aircrack-ng/mdk4
IEEE 802.11 Wi-Fi testing tool for protocol weakness exploitation, including beacon flooding, deauthentication, packet fuzzing, and IDS evasion.…
 tcstool/fireaway
Next Generation Firewall Audit and Bypass Tool
 rafael-santiago/pig
A Linux packet crafting tool.
 dowrighttv/dnxfirewall
DNXFIREWALL® and DAD'S NEXT-GEN FIREWALL™, a C/CPython hybrid next generation firewall built on top of Linux and bound to kernel/ netfilter hooks for…
 mgeeky/redwarden
Cobalt Strike C2 Reverse proxy that fends off Blue Teams, AVs, EDRs, scanners through packet inspection and malleable profile correlation
 simoesctt/-ctt-nsp-convergent-time-theory---network-stack-projection-cve-2026-24858-
A Proof-of-Concept demonstrating the application of 3D Navier-Stokes CTT formulations to packet flow optimization and defensive bypass.