
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
18 results
donut preview

donut

GitHubthewover/donut

Generates x86, x64, or AMD64+x86 position-independent shellcode that loads .NET Assemblies, PE files, and other Windows payloads from memory and runs…

exploitationids-ips-evasionmemory-forensics+7
4.7k
1 year ago
r77-rootkit preview

r77-rootkit

GitHubbytecode77/r77-rootkit

Fileless ring 3 rootkit with installer and persistence that hides processes, files, network connections, etc.
command-and-controldefensive-toolsids-ips-evasion+6
2.2k2 months ago
ExecIT preview

ExecIT

GitHubflorylsk/execit

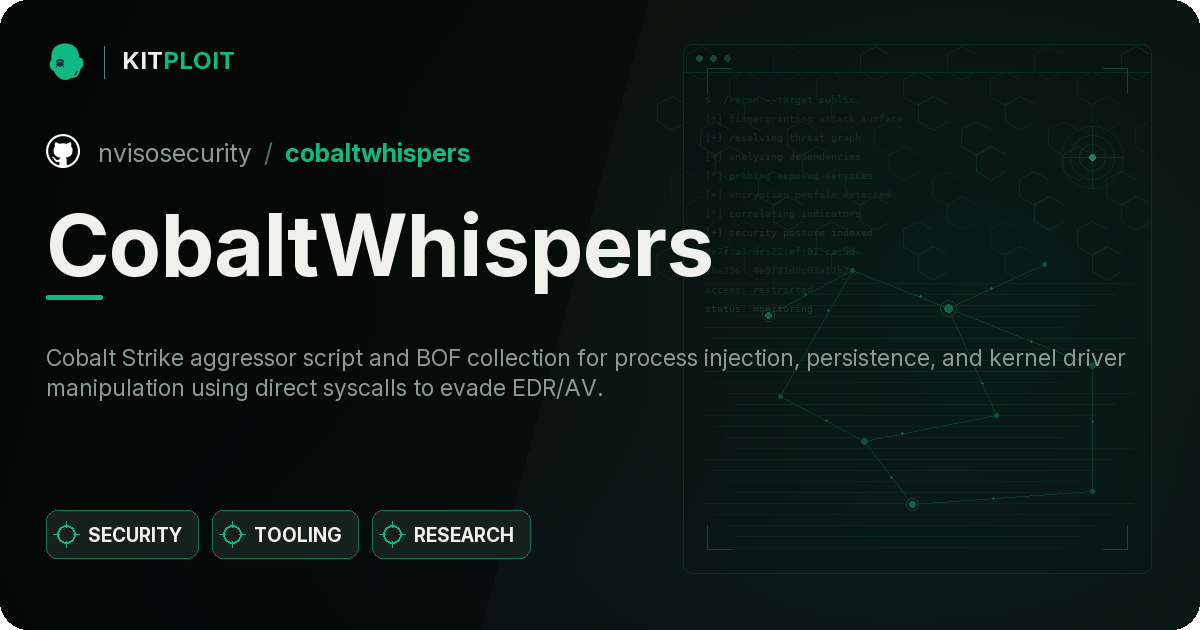
Execute shellcode files with rundll32
ids-ips-evasionmalware-analysispayload-development+4
2272 years ago
CobaltWhispers preview

CobaltWhispers

GitHubnvisosecurity/cobaltwhispers

CobaltWhispers is an aggressor script that utilizes a collection of Beacon Object Files (BOF) for Cobalt Strike to perform process injection,…
adversarial-attackcommand-and-controlids-ips-evasion+4
2413 years ago
recomposer preview

recomposer

GitHubsecretsquirrel/recomposer

Randomly changes Win32/64 PE Files for 'safer' uploading to malware and sandbox sites.
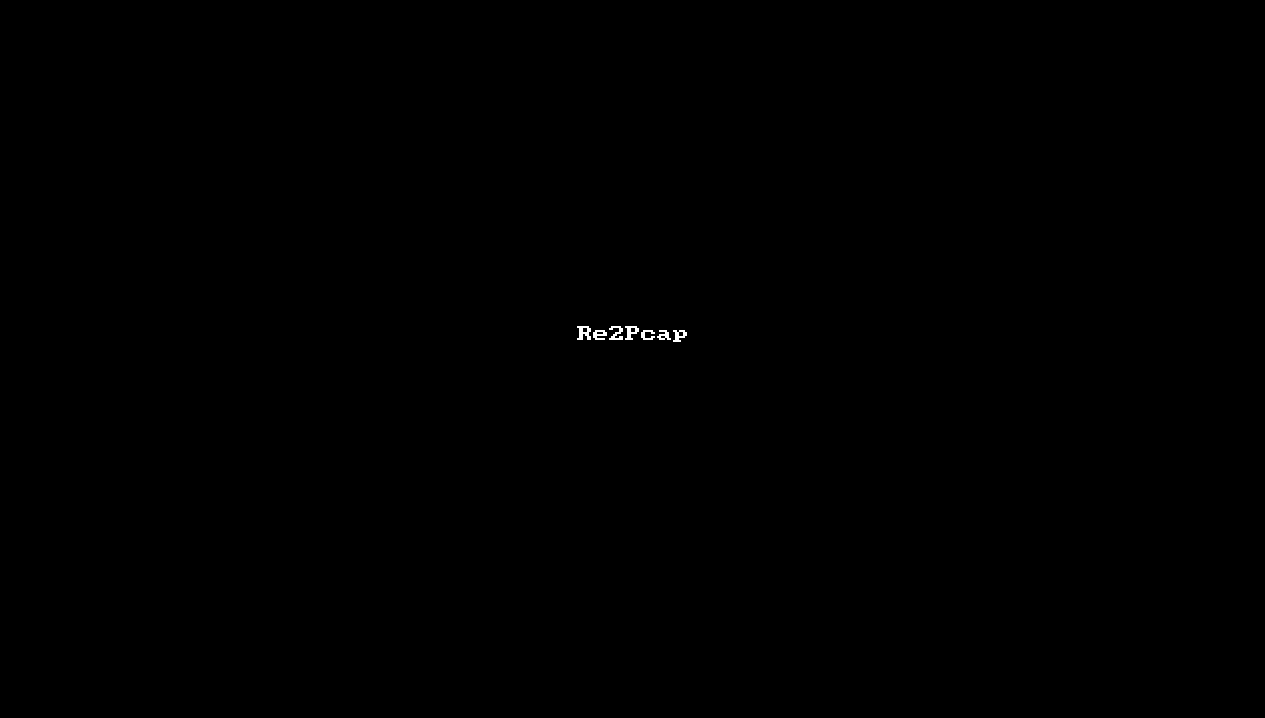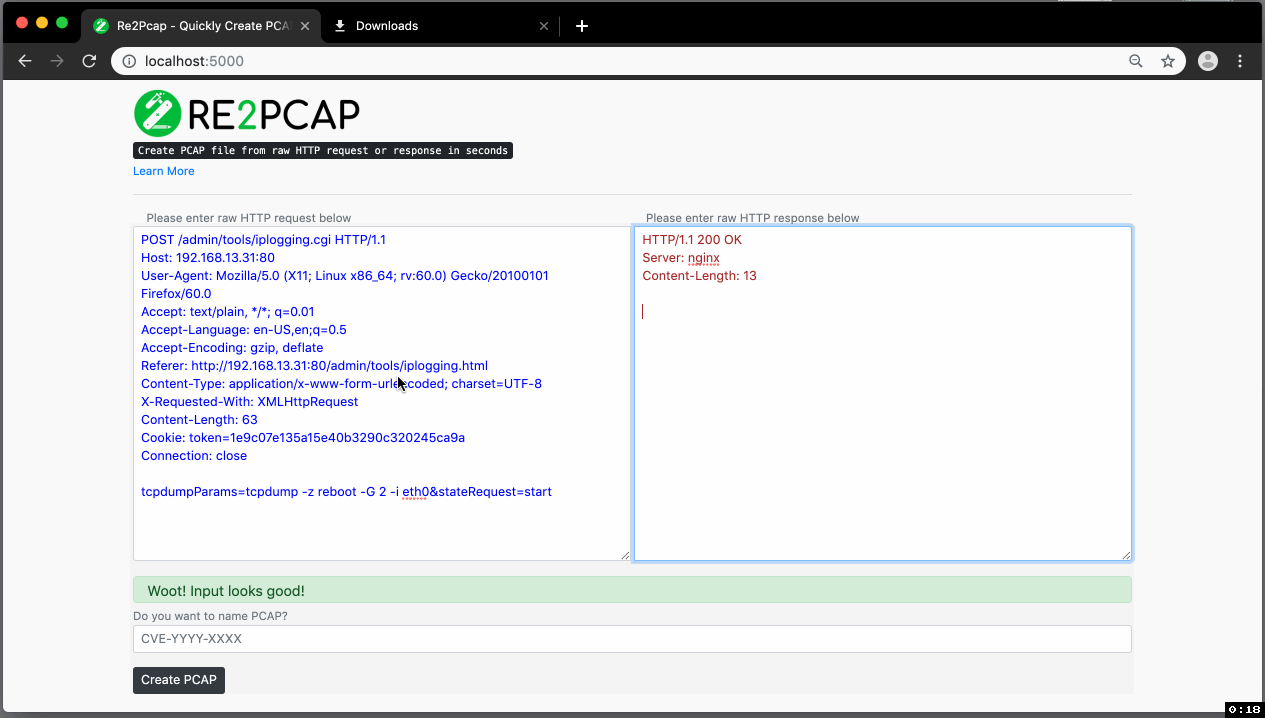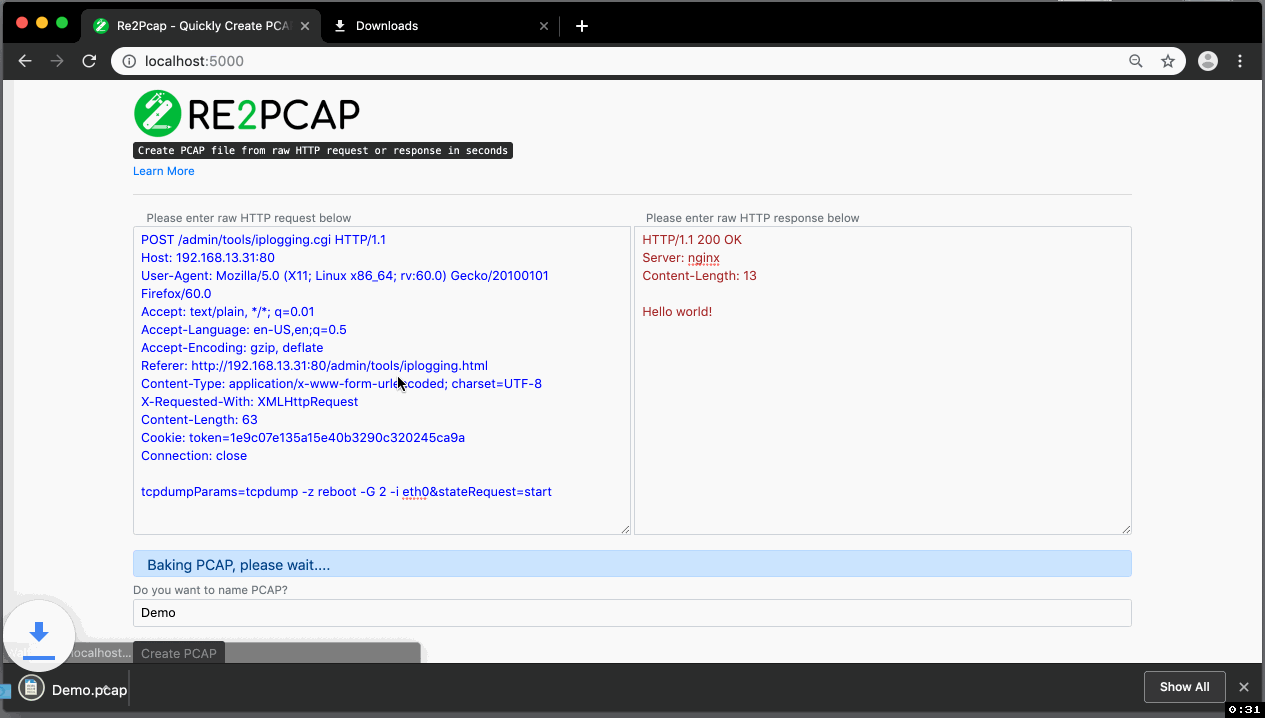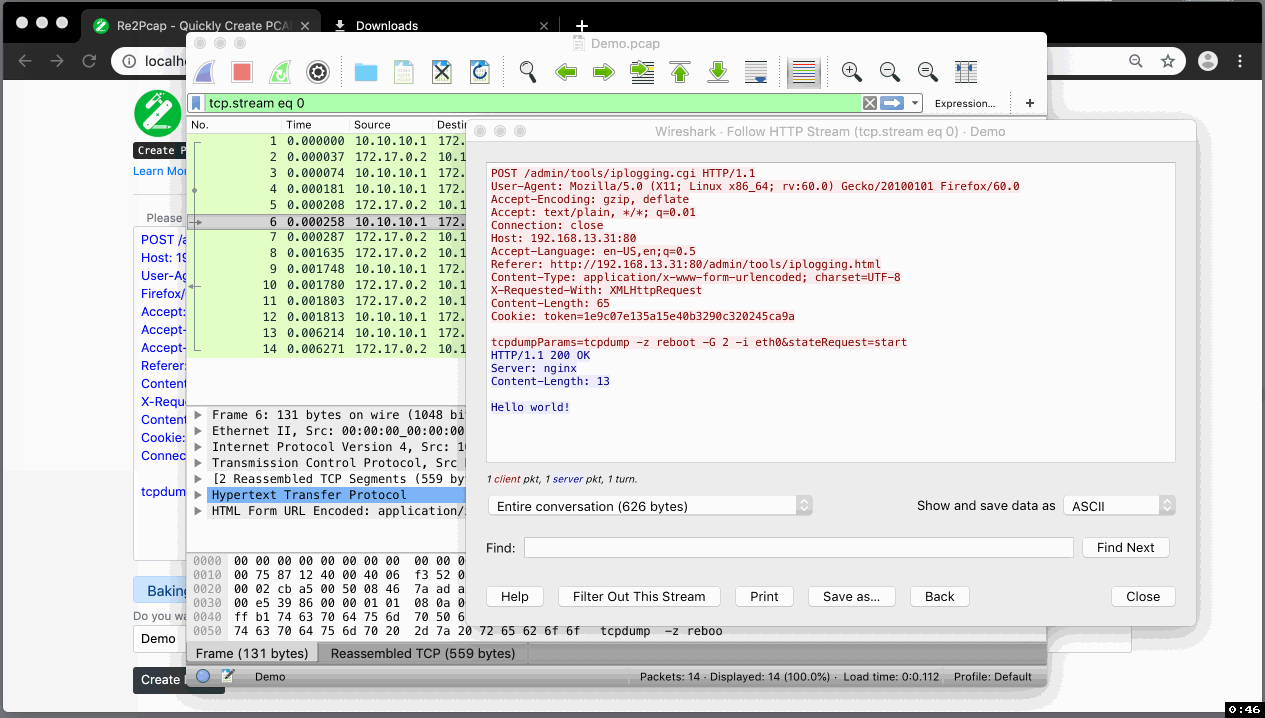
anti-botbinary-analysisids-ips-evasion+2
13212 years ago
Re2Pcap preview

Re2Pcap

GitHubcisco-talos/re2pcap

Convert raw HTTP requests/responses into PCAP files for testing Snort IDS rules and network security analysis. Supports Docker deployment and…
ids-ips-evasionnetwork-securitypacket-sniffing-analysis+1
605 years ago
macos_app_structure preview

macos_app_structure

GitHubyo-yo-yo-jbo/macos_app_structure

Educational deep dive into macOS app bundles, plist files, and launchd process behavior, with offensive security notes on packaging payloads as .app…
educationids-ips-evasionpayload-development+2
472 months ago
CVE-2025-50165-x64-Exploit preview

CVE-2025-50165-x64-Exploit

GitHubencrypter15/cve-2025-50165-x64-exploit

Generates weaponized JPEG files exploiting CVE-2025-50165 (Windows Graphics RCE) with custom x64 shellcode, heap spray, ROP chain, and AV/EDR evasion…
binary-exploitationexploitationids-ips-evasion+5
79 months ago
sRDI preview

sRDI

GitHubmonoxgas/srdi

Shellcode implementation of Reflective DLL Injection. Convert DLLs to position independent shellcode
exploitationids-ips-evasionmemory-forensics+7
2.5k4 years ago
SysWhispers preview

SysWhispers

GitHubjthuraisamy/syswhispers

AV/EDR evasion via direct system calls.
exploitationids-ips-evasionpayload-development+3
2.0k5 years ago
SysWhispers2 preview

SysWhispers2

GitHubjthuraisamy/syswhispers2

AV/EDR evasion via direct system calls.

binary-exploitationdefensive-toolsids-ips-evasion+5
1.8k4 years ago
MaldevAcademyLdr.2 preview

MaldevAcademyLdr.2

GitHubmaldev-academy/maldevacademyldr.2

RunPE implementation with multiple evasive techniques (2)
cryptographyids-ips-evasionpayload-development+3
2860 years ago
NyxInvoke preview

NyxInvoke

GitHubblacksnufkin/nyxinvoke

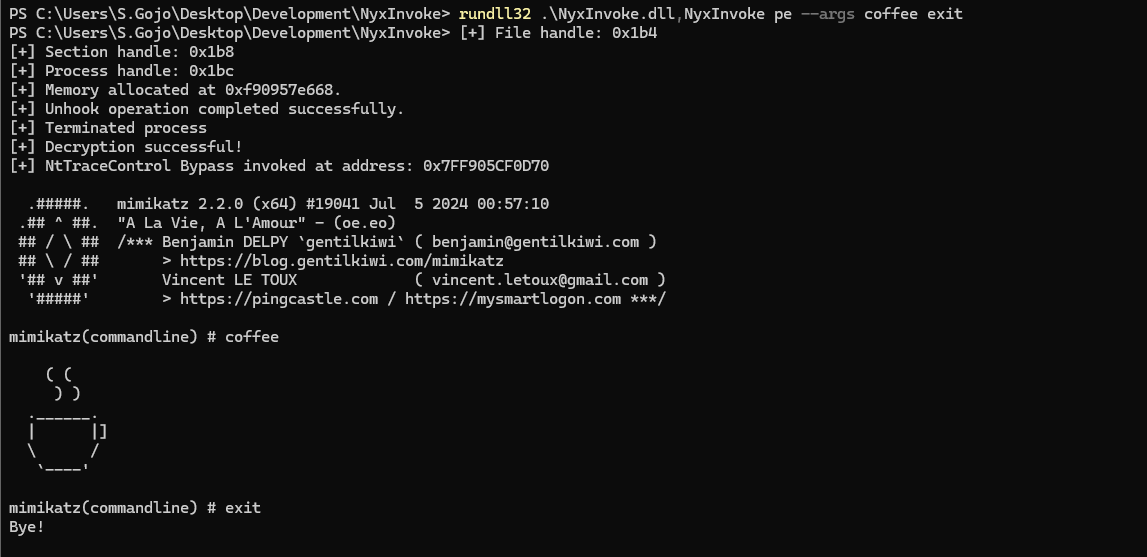
NyxInvoke is a Rust CLI tool for running .NET assemblies, PowerShell, and BOFs with Patchless AMSI and ETW bypass features. with Dual-build support
command-and-controlexploitationids-ips-evasion+6
2411 year ago
skyhook preview

skyhook

GitHubblackhillsinfosec/skyhook

A round-trip obfuscated HTTP file transfer setup built to bypass IDS detections.
data-exfiltrationids-ips-evasionred-teaming+1
2892 years ago
MoveEdr preview

MoveEdr

GitHubduhirsch/moveedr

Permanently disable EDRs as local admin
anti-botdefensive-toolsids-ips-evasion+5
1319 months ago
Nodejs-Tracer preview

Nodejs-Tracer

GitHubcheckpointsw/nodejs-tracer

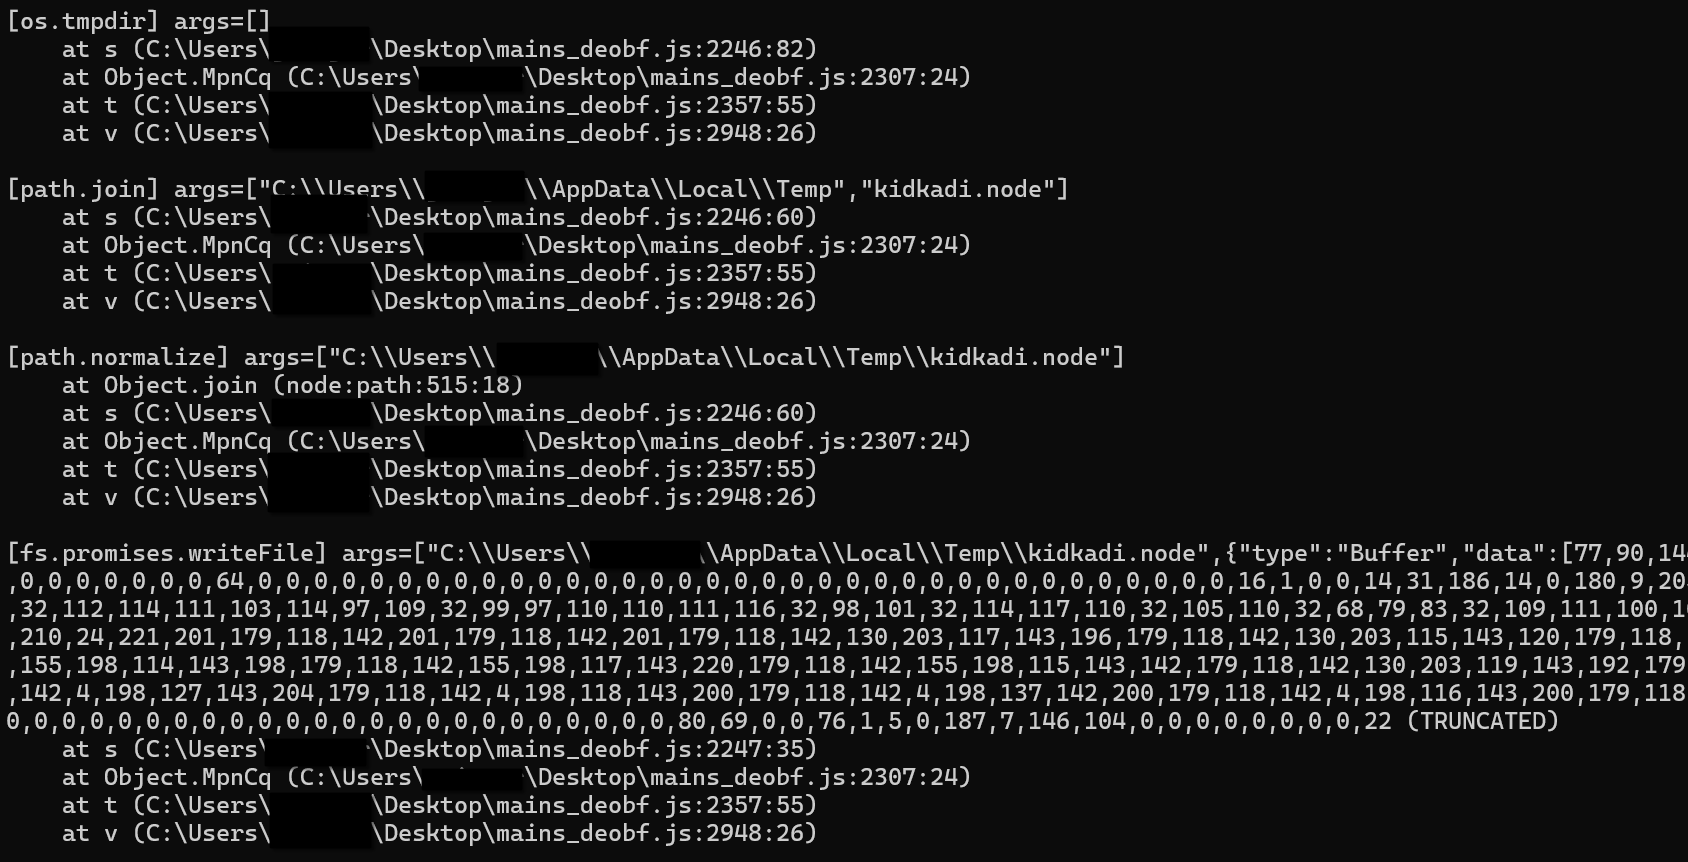
Runtime tracer for Node.js malware analysis that hooks core modules, logs calls, spoofs anti-analysis checks, and captures file writes and HTTP…
anti-botdynamic-analysis-sandboxingids-ips-evasion+3
818 months ago
zipbrk preview

zipbrk

GitHubkvesel/zipbrk

Zip file format fuzzer and multi-tool.
binary-analysiscryptographyencryption-decryption-tools+4
124 months ago
blackpill preview
Archived

blackpill

GitHubshard77/blackpill

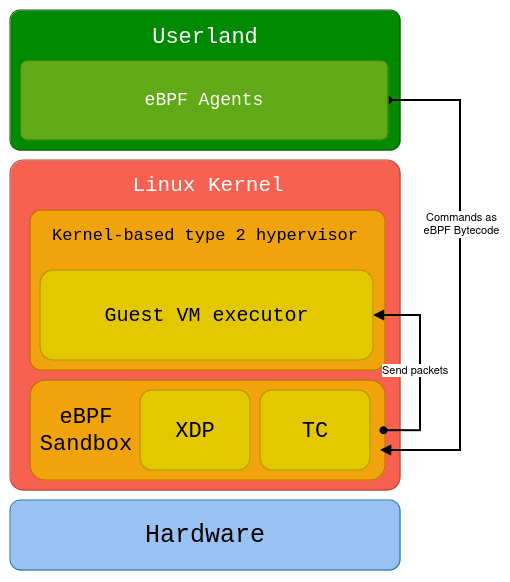
A Linux kernel rootkit in Rust using a custom made type-2 hypervisor, eBPF XDP and TC programs

binary-exploitationcommand-and-controlids-ips-evasion+7
3386 months ago