

wireless-ids
 syworks/wireless-ids
Ability to detect suspicious activity such as (WEP/WPA/WPS) attack by sniffing the air for wireless packets.
anomaly-detectionids-ips-evasionintrusion-detection+3
276
syworks/wireless-idsAbility to detect suspicious activity such as (WEP/WPA/WPS) attack by sniffing the air for wireless packets.
 abacus-group-rto/legion
Legion is an open source, easy-to-use, super-extensible and semi-automated network penetration testing tool that aids in discovery, reconnaissance…
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 bishopfox/sliver
Adversary Emulation Framework
 bunkerity/bunkerweb
🛡️ Open-source and cloud-native Web Application Firewall (WAF)
 wietze/invoke-argfuscator
Invoke-ArgFuscator is an open-source, cross-platform PowerShell module that helps generate obfuscated command-lines for common system-native…
 division-36/z-jail
A lightweight, multi-layer Linux sandbox combining namespaces, pivot_root, seccomp-bpf, capability dropping, and an evidence-based verdict engine…
 nullsection/chisel-ng
Chisel new generation, written in rust. SSH under WSS with some customization.
 zedeldi/cve-2025-47827
PoC and vulnerability report for CVE-2025-47827.
 u1tr0nex/cve-2022-30190-follina-lab
Full exploit chain lab and Suricata IDS detection for CVE-2022-30190 (Follina) - MSDT RCE
 owerdogan/whoami-project
Whoami provides enhanced privacy, anonymity for Debian and Arch based linux distributions
 k4yt3x/scutum
Linux Automatic ARP (TCP / UDP / ICMP) Firewall
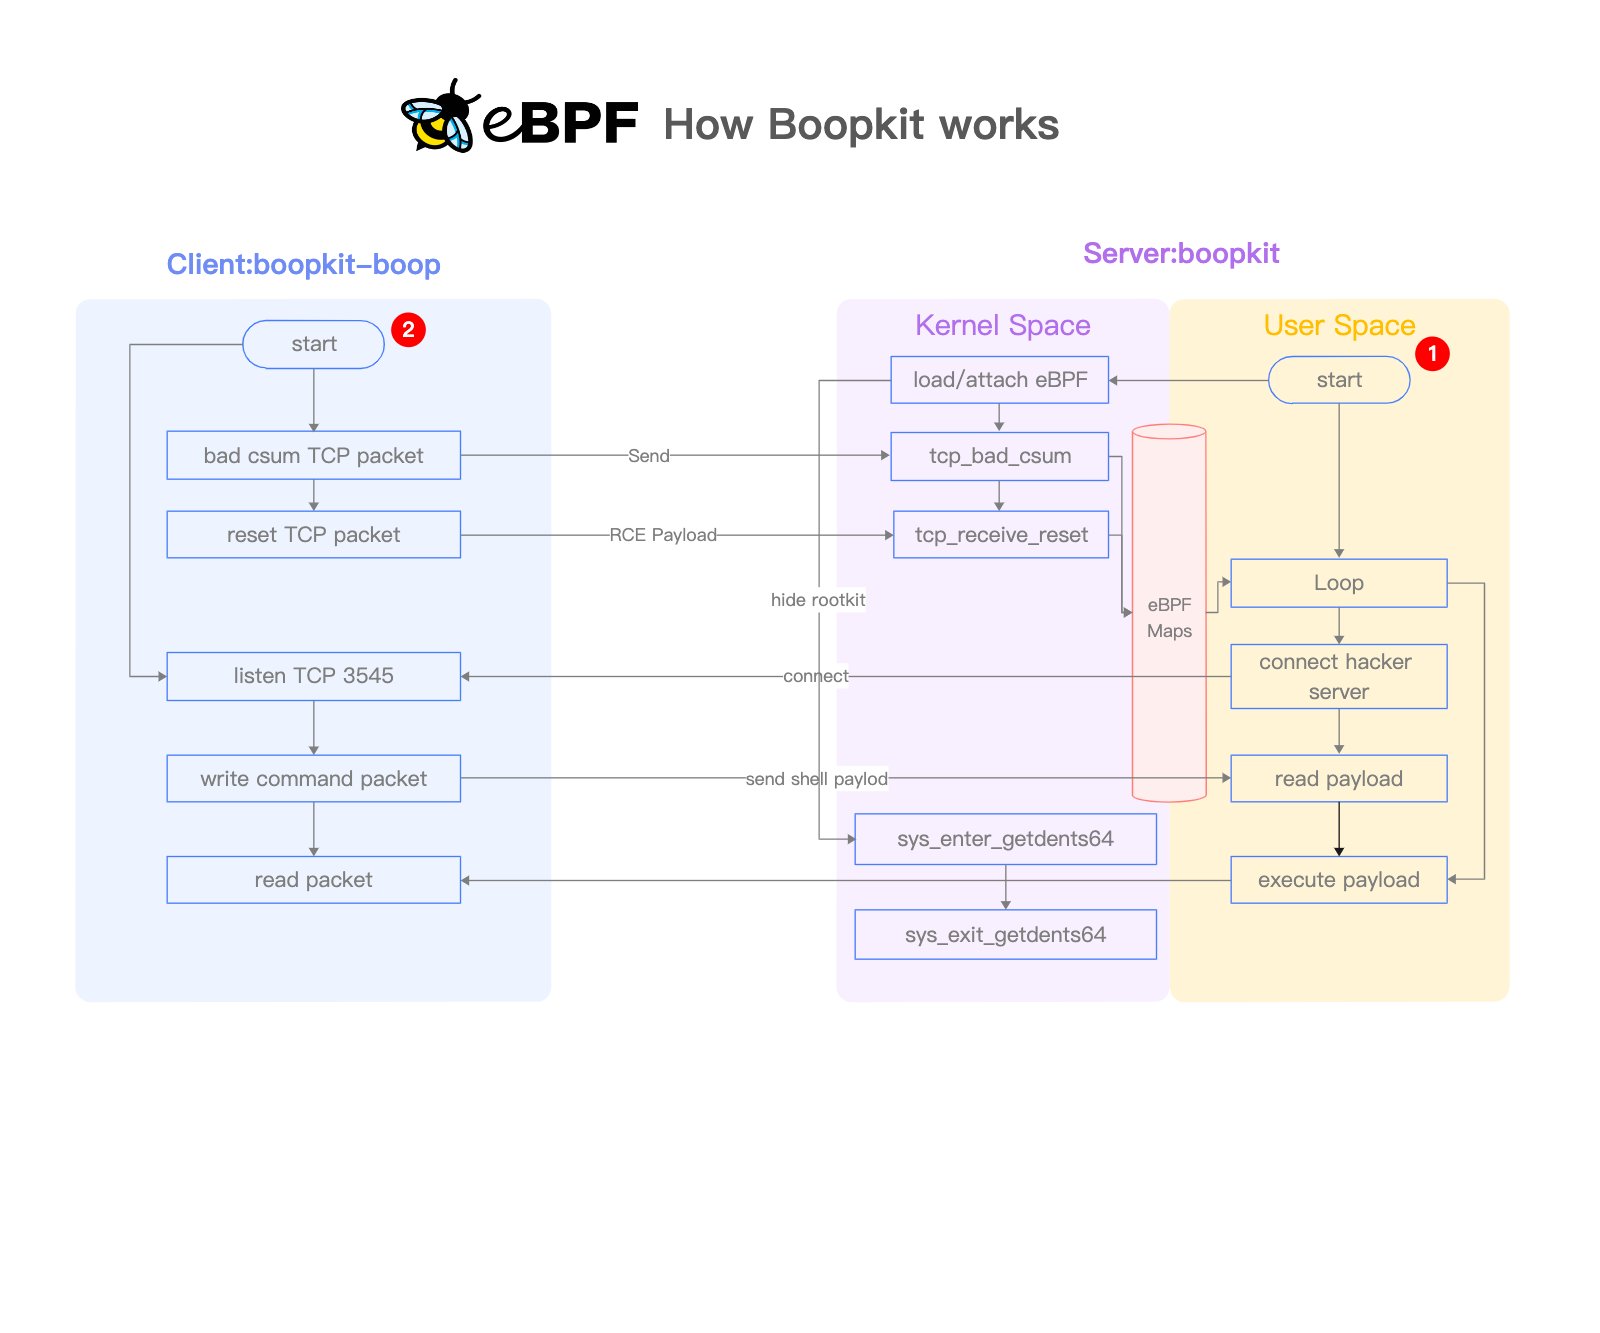 krisnova/boopkit
Linux eBPF backdoor over TCP. Spawn reverse shells, RCE, on prior privileged access. Less Honkin, More Tonkin.
 emptymonkey/mimic
Hide processes as a normal user in Linux.
 cryptolok/ghostinthenet
Ultimate Network Stealther that makes Linux a Ghost In The Net and protects from MITM/DOS/scan
 r00t-3xp10it/trojanizer
Trojanize your payload - WinRAR (SFX) automatization - under Linux distros
 matheuzsecurity/ringreaper
Linux post-exploitation agent that uses io_uring to stealthily bypass EDR detection by avoiding traditional syscalls.
 rafael-santiago/pig
A Linux packet crafting tool.