
Umbra
 h3xduck/umbra
A LKM rootkit targeting 4.x and 5.x kernel versions which opens a backdoor that can spawn a reverse shell to a remote host, launch malware and more.
command-and-controleducationencryption-decryption-tools+6
135
h3xduck/umbraA LKM rootkit targeting 4.x and 5.x kernel versions which opens a backdoor that can spawn a reverse shell to a remote host, launch malware and more.
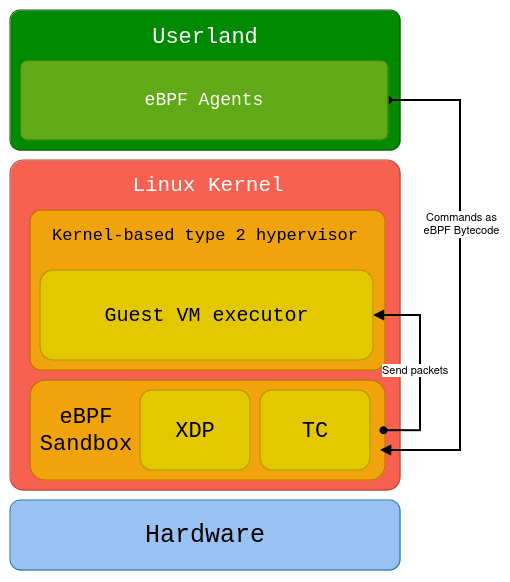 shard77/blackpill
A Linux kernel rootkit in Rust using a custom made type-2 hypervisor, eBPF XDP and TC programs
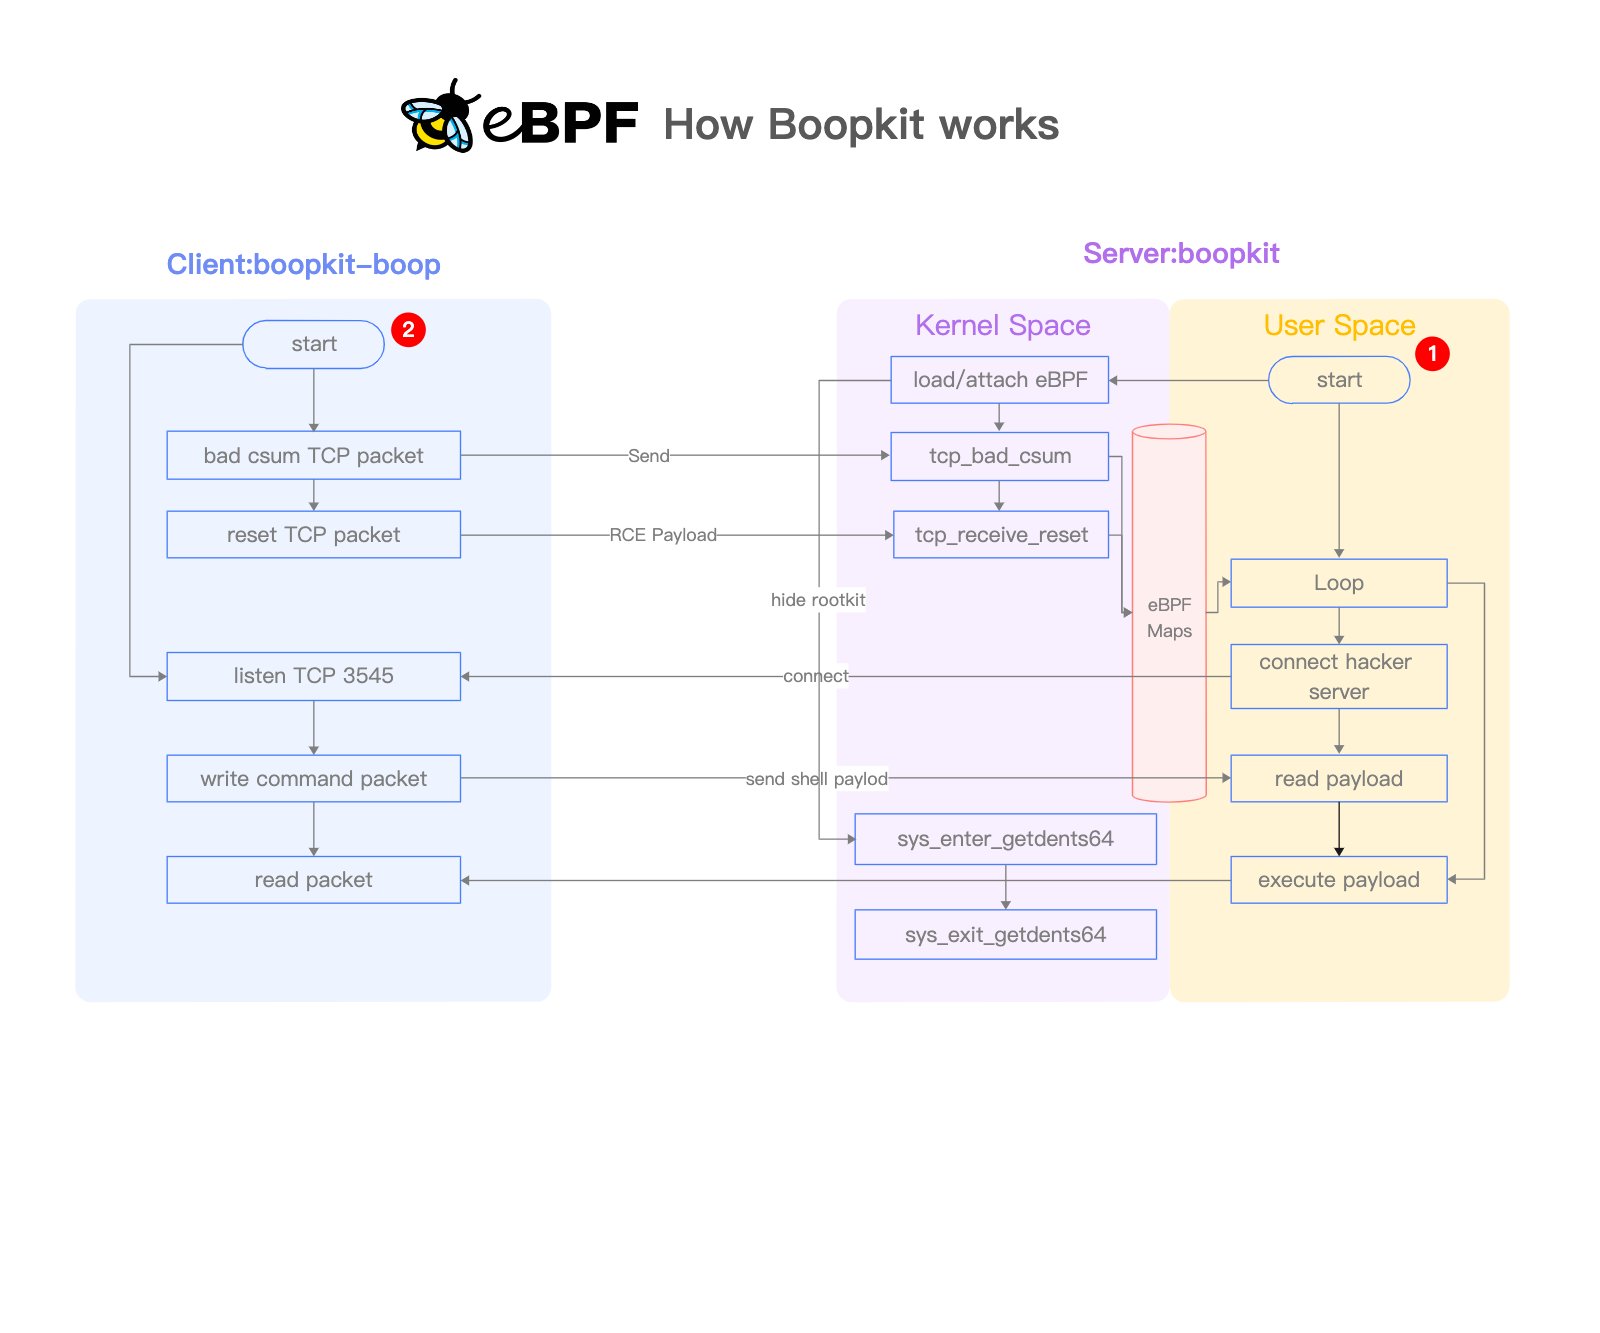 krisnova/boopkit
Linux eBPF backdoor over TCP. Spawn reverse shells, RCE, on prior privileged access. Less Honkin, More Tonkin.
 asekon/rootkit
A rootkit for ubuntu-16.04.6 (Linux 4.4). Can hide a process, give root access and hide itself
 dowrighttv/dnxfirewall
DNXFIREWALL® and DAD'S NEXT-GEN FIREWALL™, a C/CPython hybrid next generation firewall built on top of Linux and bound to kernel/ netfilter hooks for…
 azqzazq1/lid
LID — Linux Integrity Drift: Bypassing AppArmor via eBPF pathname rewriting. Pre-LSM syscall argument manipulation with zero audit footprint. "Linux…
 wecooperate/imonitorsdk
The world's most powerful System Activity Monitor Engine · 一款功能强大的终端行为采集防御开发套件 ~ 旨在帮助EDR、零信任、数据安全、审计管控等终端安全软件可以快速实现产品功能,…
 cenobyte-vincit/encrypted-linux-kernel-modules
encrypted-linux-kernel-modules