
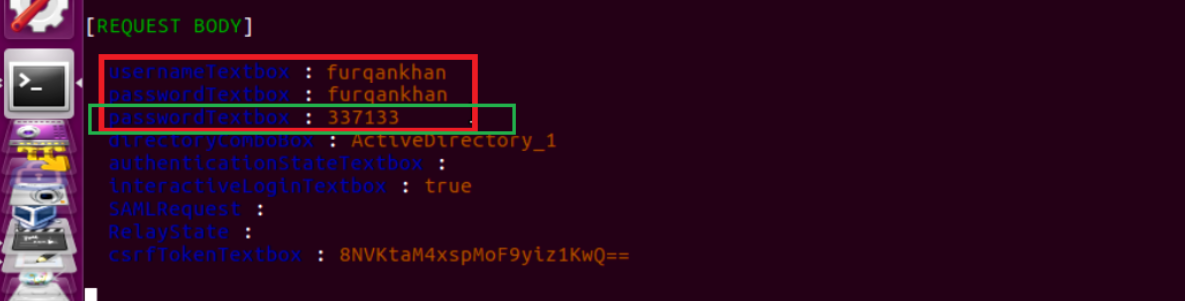
CVE-2019-13498
 furqankhan1/cve-2019-13498
CVE-2019-13498
exploitationids-ips-evasionimpersonation-tools+3
furqankhan1/cve-2019-13498CVE-2019-13498
 division-36/z-jail
A lightweight, multi-layer Linux sandbox combining namespaces, pivot_root, seccomp-bpf, capability dropping, and an evidence-based verdict engine…
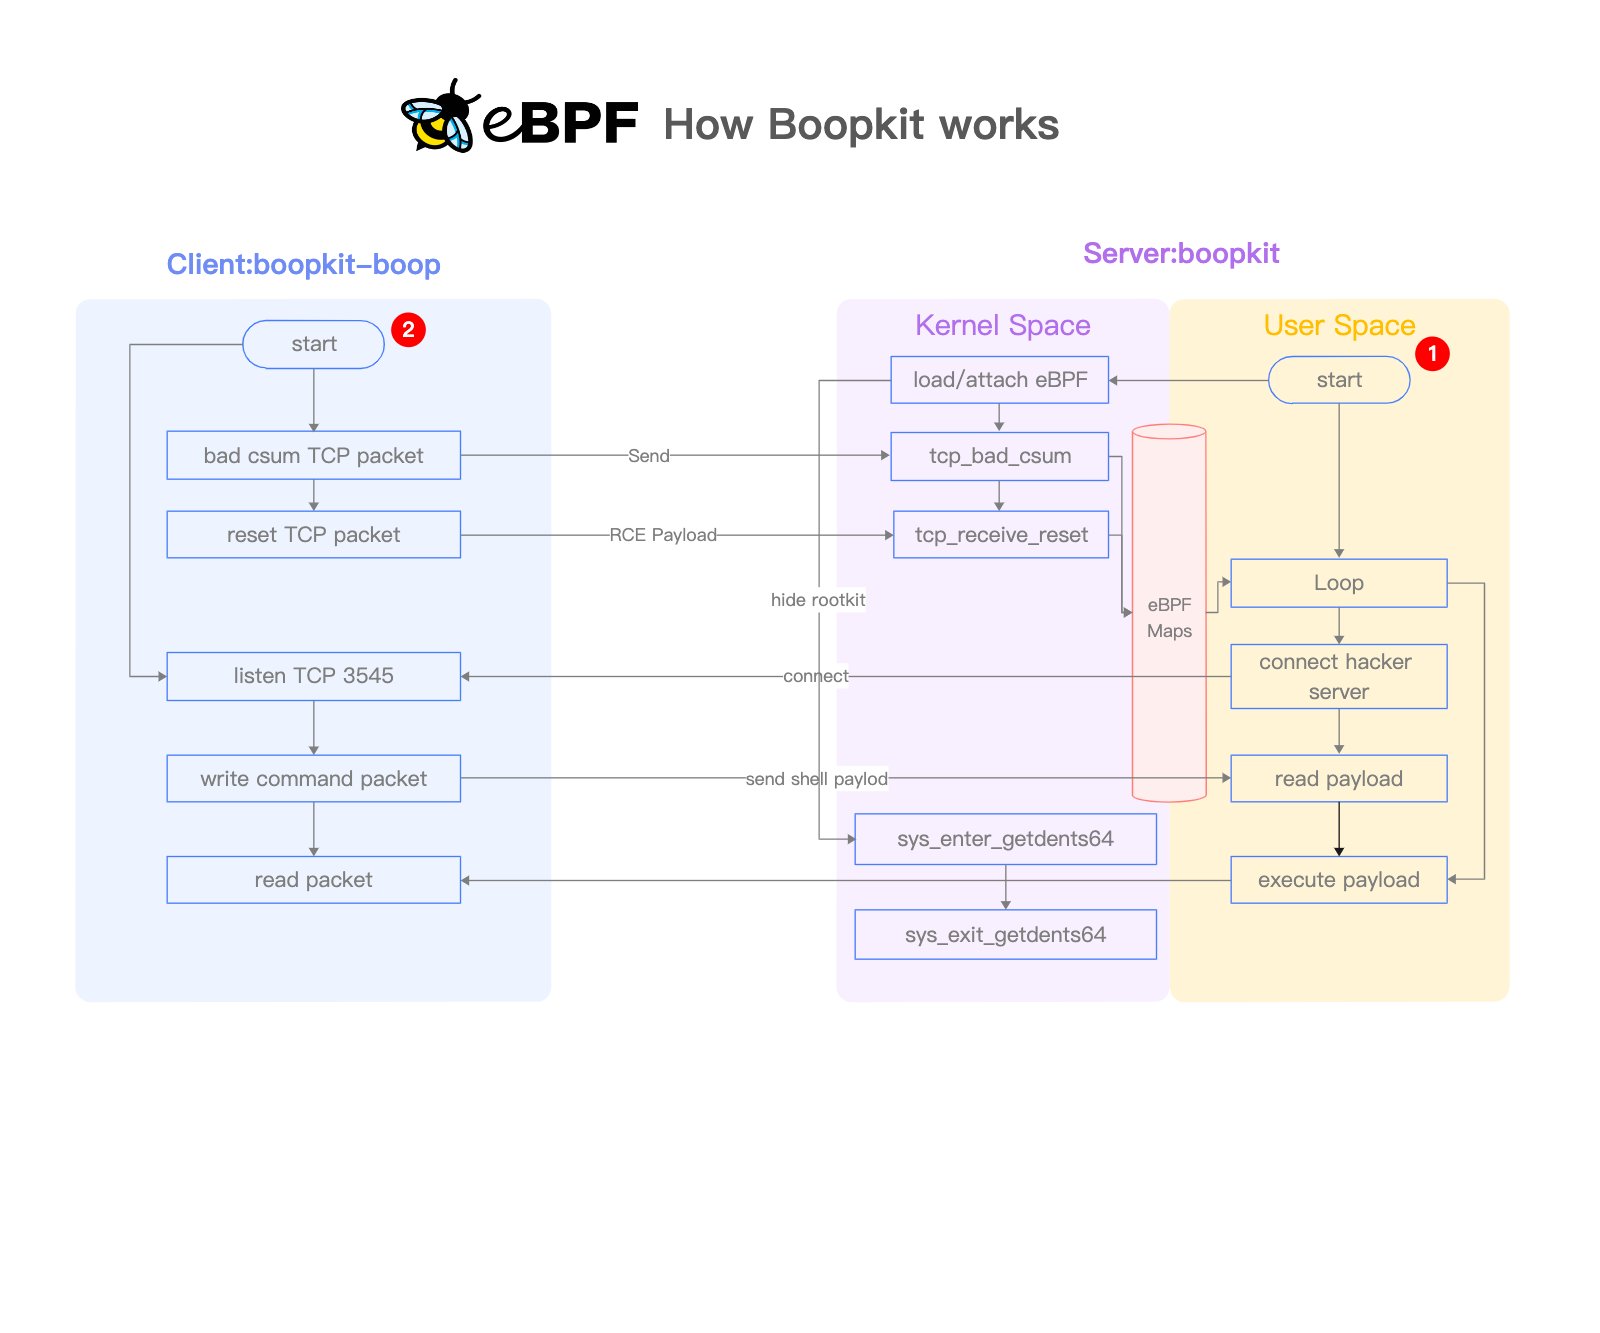 krisnova/boopkit
Linux eBPF backdoor over TCP. Spawn reverse shells, RCE, on prior privileged access. Less Honkin, More Tonkin.
 r00t-3xp10it/trojanizer
Trojanize your payload - WinRAR (SFX) automatization - under Linux distros
 matheuzsecurity/ringreaper
Linux post-exploitation agent that uses io_uring to stealthily bypass EDR detection by avoiding traditional syscalls.
 voidsecsoftwares/voidsyscall
Cross-platform syscall-powered implant & C2 — direct syscalls (Win), raw syscalls (Linux), HTTPS/DNS/ICMP channels. No winapi layer.
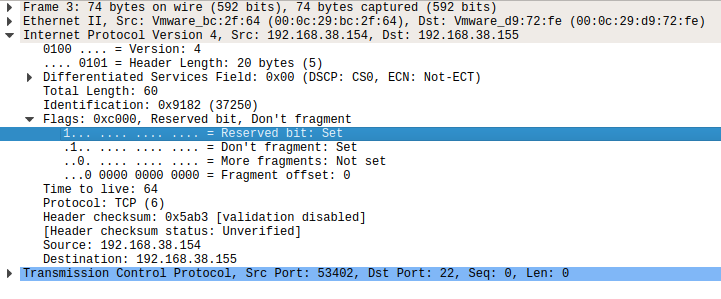 flamingspork/iptable_evil
Kernel-level iptables backdoor that accepts all packets with the RFC 3514 evil bit set, bypassing firewall rules. Includes in-tree and out-of-tree…
 magisterquis/lutlol
Living Under the Land on Linux ~ Bsides Belfast/Vienna 2025
 mephistolist/soviet
A Runtime Crypter in C for Linux ELF binaries.
 azqzazq1/lid
LID — Linux Integrity Drift: Bypassing AppArmor via eBPF pathname rewriting. Pre-LSM syscall argument manipulation with zero audit footprint. "Linux…
 0x574r/darkcloak
Linux process identity cloaking tool that spoofs comm, argv, cmdline, environ, exe path, and VMAs via an 11-phase prctl pipeline to impersonate…
 asekon/rootkit
A rootkit for ubuntu-16.04.6 (Linux 4.4). Can hide a process, give root access and hide itself
 armircetaj/tetragon-dirtyfrag
Blocking the DirtyFrag Linux LPE chain (CVE-2026-43284 / CVE-2026-43500) at runtime with a Cilium Tetragon TracingPolicy
 shard77/blackpill
A Linux kernel rootkit in Rust using a custom made type-2 hypervisor, eBPF XDP and TC programs
 r00t-3xp10it/morpheus
Morpheus - Automating Ettercap TCP/IP (MITM-hijacking Tool)
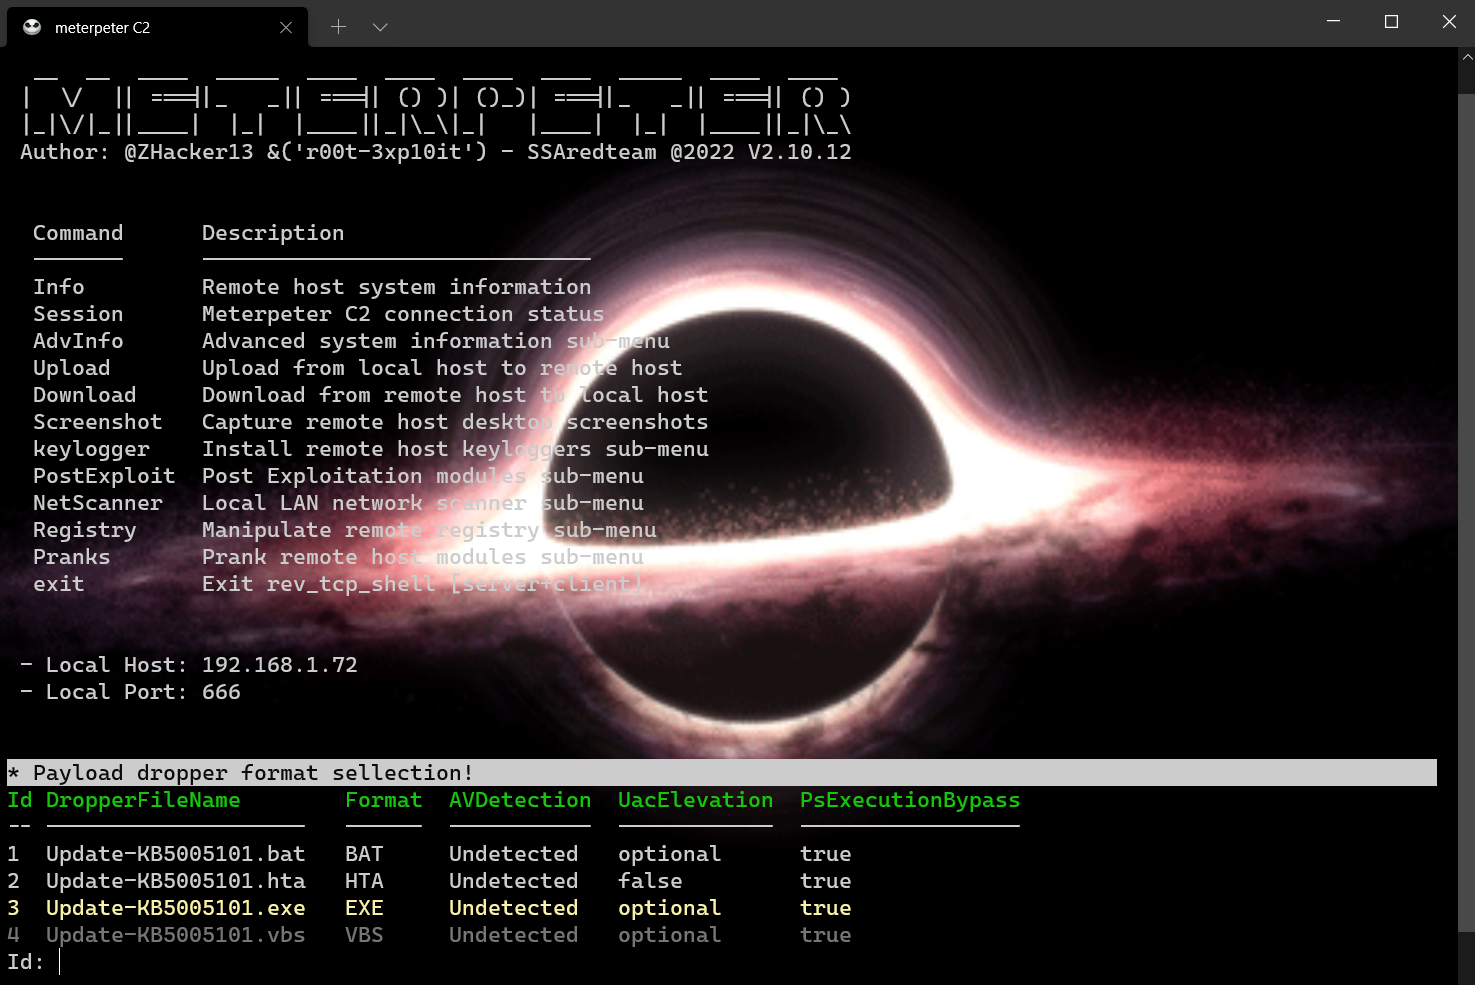 r00t-3xp10it/meterpeter
C2 Powershell Command & Control Framework with BuiltIn Commands
 silverfoxx/pwnstar
PwnSTAR (Pwn SofT-Ap scRipt) - for all your fake-AP needs!
 haplessidiot/ageverificationbypass
Bypass age verification service from redhat