

EDRs
 mr-un1k0d3r/edrs
Red team tool for EDR evasion: dynamically resolves syscall IDs, patches ntdll stubs, unhooks IAT hooks, and lists hooked APIs from major EDR vendors.
binary-analysiscurated-resourcesids-ips-evasion+3
mr-un1k0d3r/edrsRed team tool for EDR evasion: dynamically resolves syscall IDs, patches ntdll stubs, unhooks IAT hooks, and lists hooked APIs from major EDR vendors.
 kvesel/zipbrk
Zip file format fuzzer and multi-tool.
 daem0nc0re/atomicsyscall
Tools and PoCs for Windows syscall investigation.
 therealdreg/anticuckoo
A tool to detect and crash Cuckoo Sandbox
 zeromemoryex/bypass-sandbox-evasion
C++ tool that patches Windows API calls to bypass sandbox RAM size checks, enabling malware to evade detection in isolated analysis environments.
 mephistolist/soviet
A Runtime Crypter in C for Linux ELF binaries.
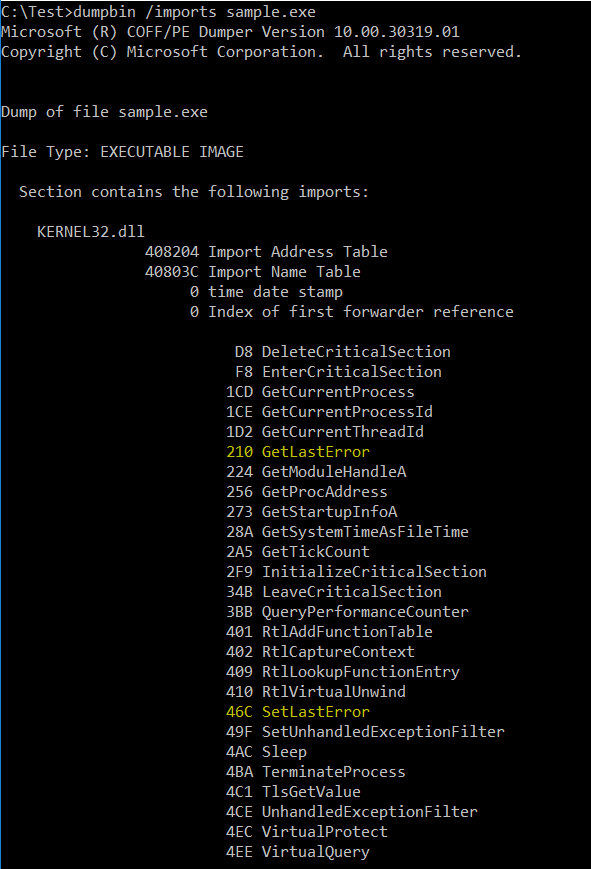 d35ha/callobfuscator
Obfuscate specific windows apis with different apis
 iamsopotatoe-coder/tinyload
Open source Windows x64 PE packer and crypter. Compresses and encrypts executables with a custom virtual machine into a self extracting stub.
 gpoulios/ropinjector
Patching ROP-encoded shellcodes into PEs
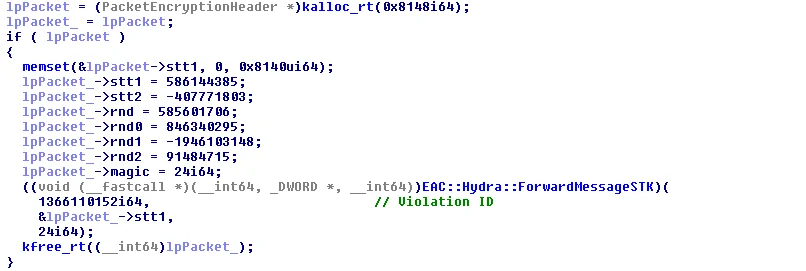 gmh5225/eac-kernel-packet-fucker
Reverse-engineered Easy Anti-Cheat kernel driver bypass that intercepts memory allocation to suppress violation packets, with report decryption…