
PowerShdll
 p3nt4/powershdll
Run PowerShell with rundll32. Bypass software restrictions.
code-analysisdefensive-toolsids-ips-evasion+3
p3nt4/powershdllRun PowerShell with rundll32. Bypass software restrictions.
 reverseclabs/wepwnise
WePWNise generates architecture independent VBA code to be used in Office documents or templates and automates bypassing application control and…
 loosehose/silentbutdeadly
SilentButDeadly is a network communication blocker specifically designed to neutralize EDR/AV software by preventing their cloud connectivity using…
 iomoath/powershx
Run Powershell without software restrictions.
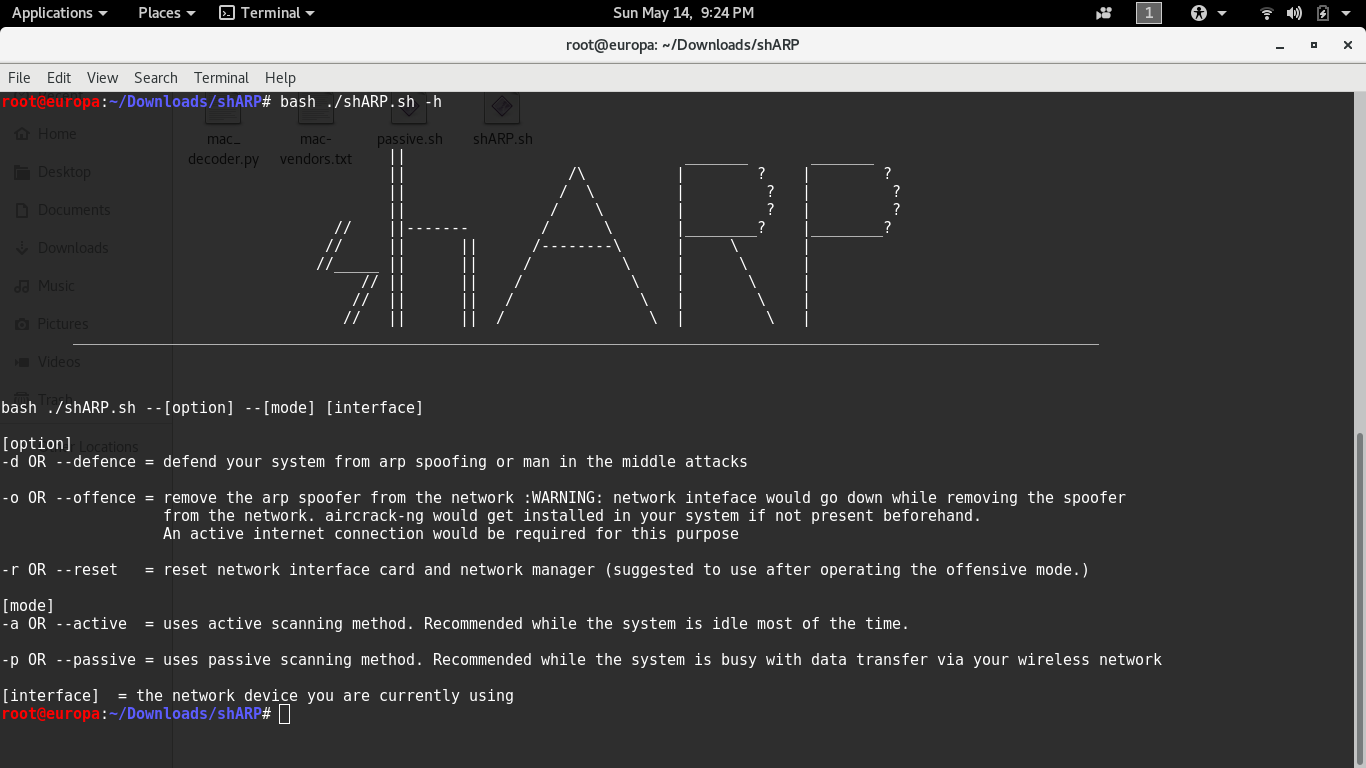 europa502/sharp
An anti-ARP-spoofing application software that use active and passive scanning methods to detect and remove any ARP-spoofer from the network.
 nuclearphoenixx/fake-sandbox
👁🗨 This script will simulate fake processes of analysis sandbox/VM software that some malware will try to avoid.
 azurit/modsecurity-backdoor
This is a proof-of-concept of malicious software running inside of ModSecurity WAF.
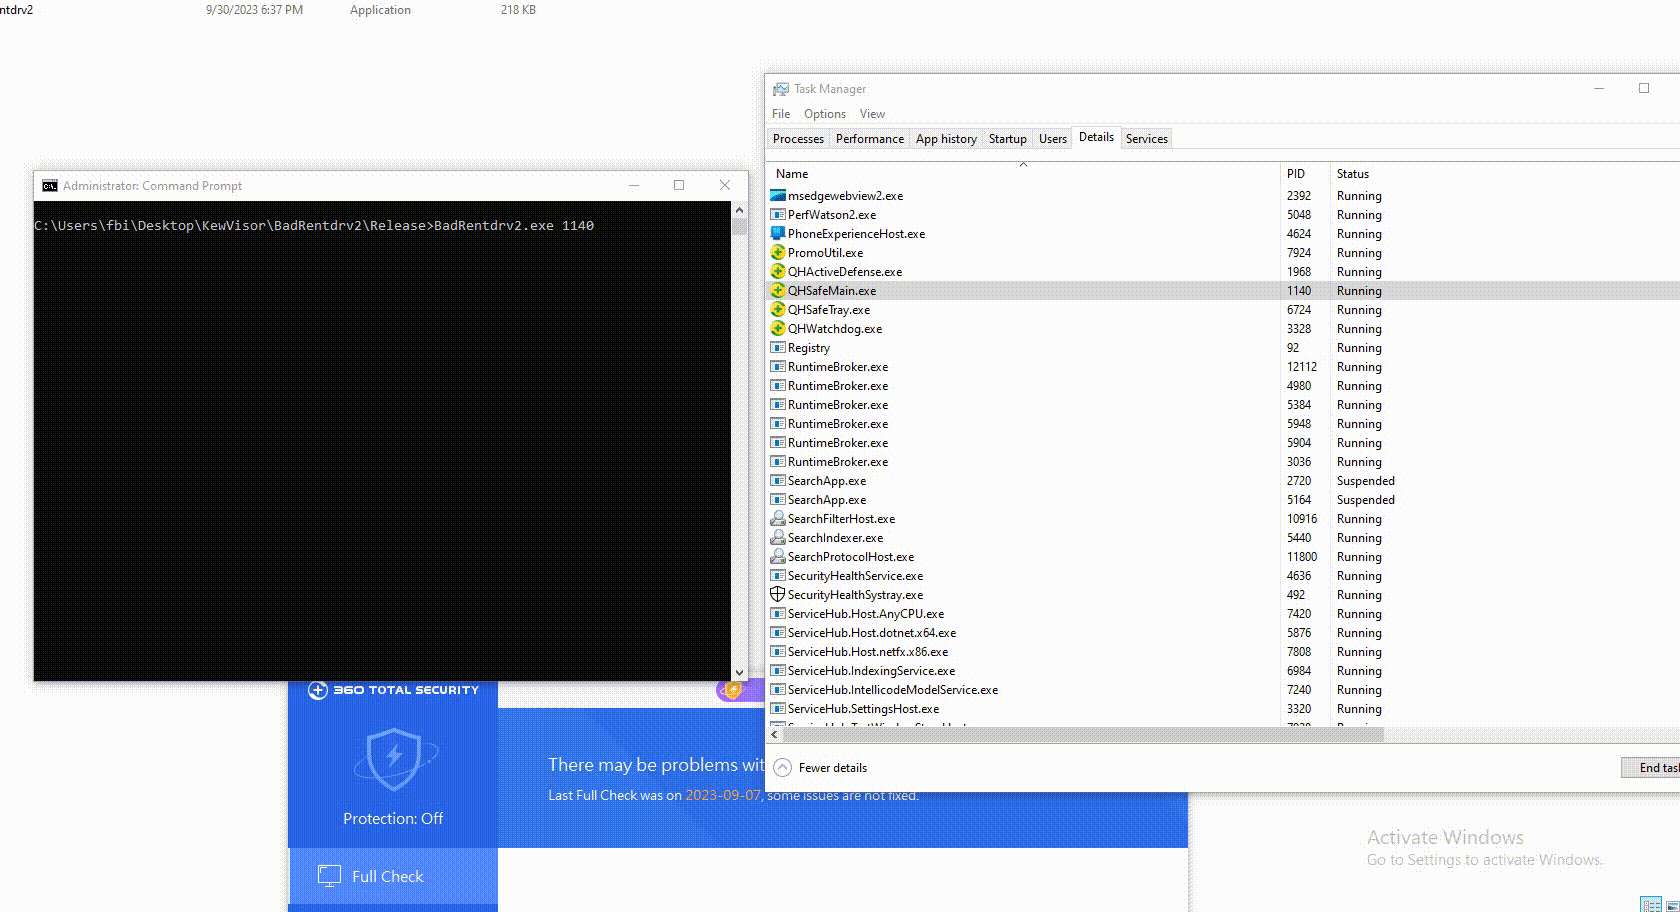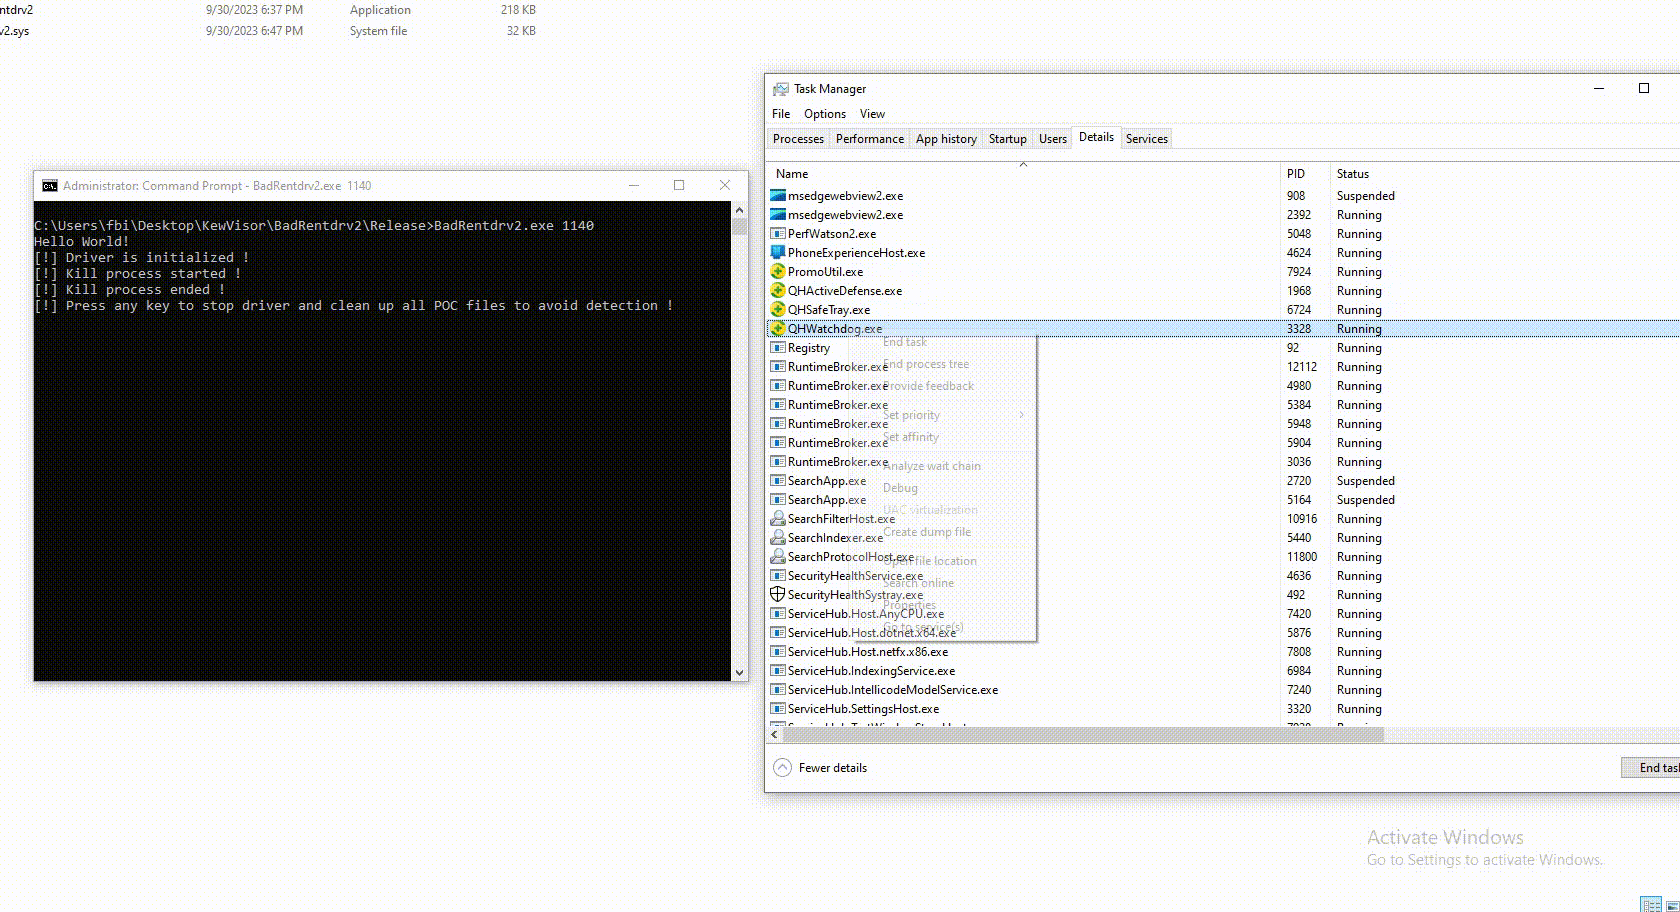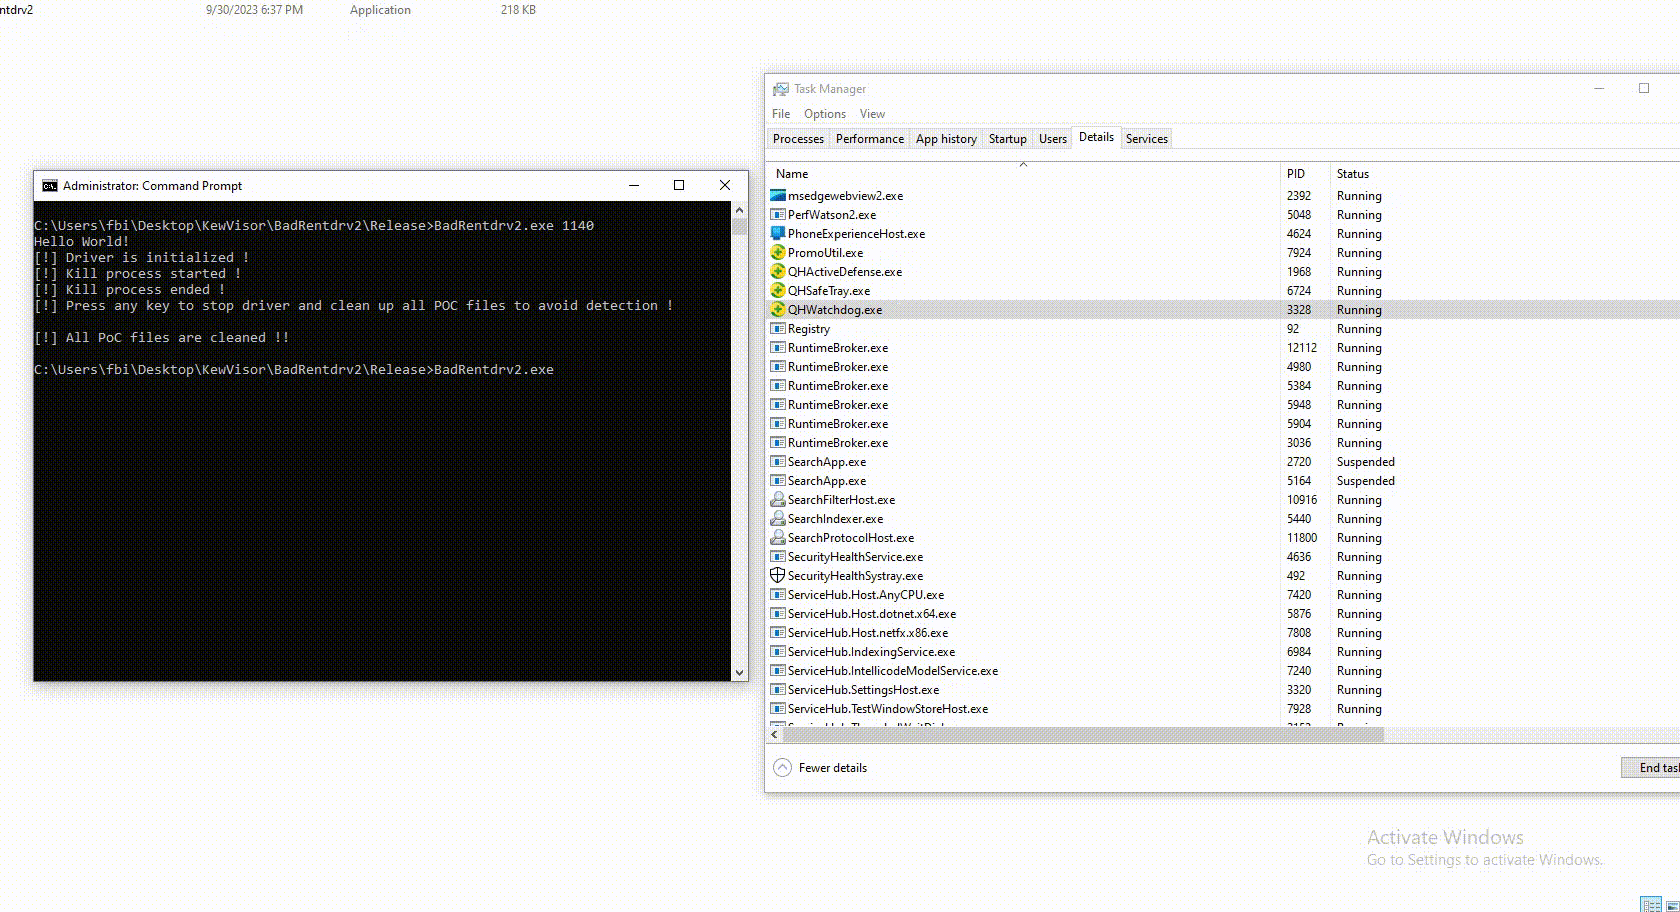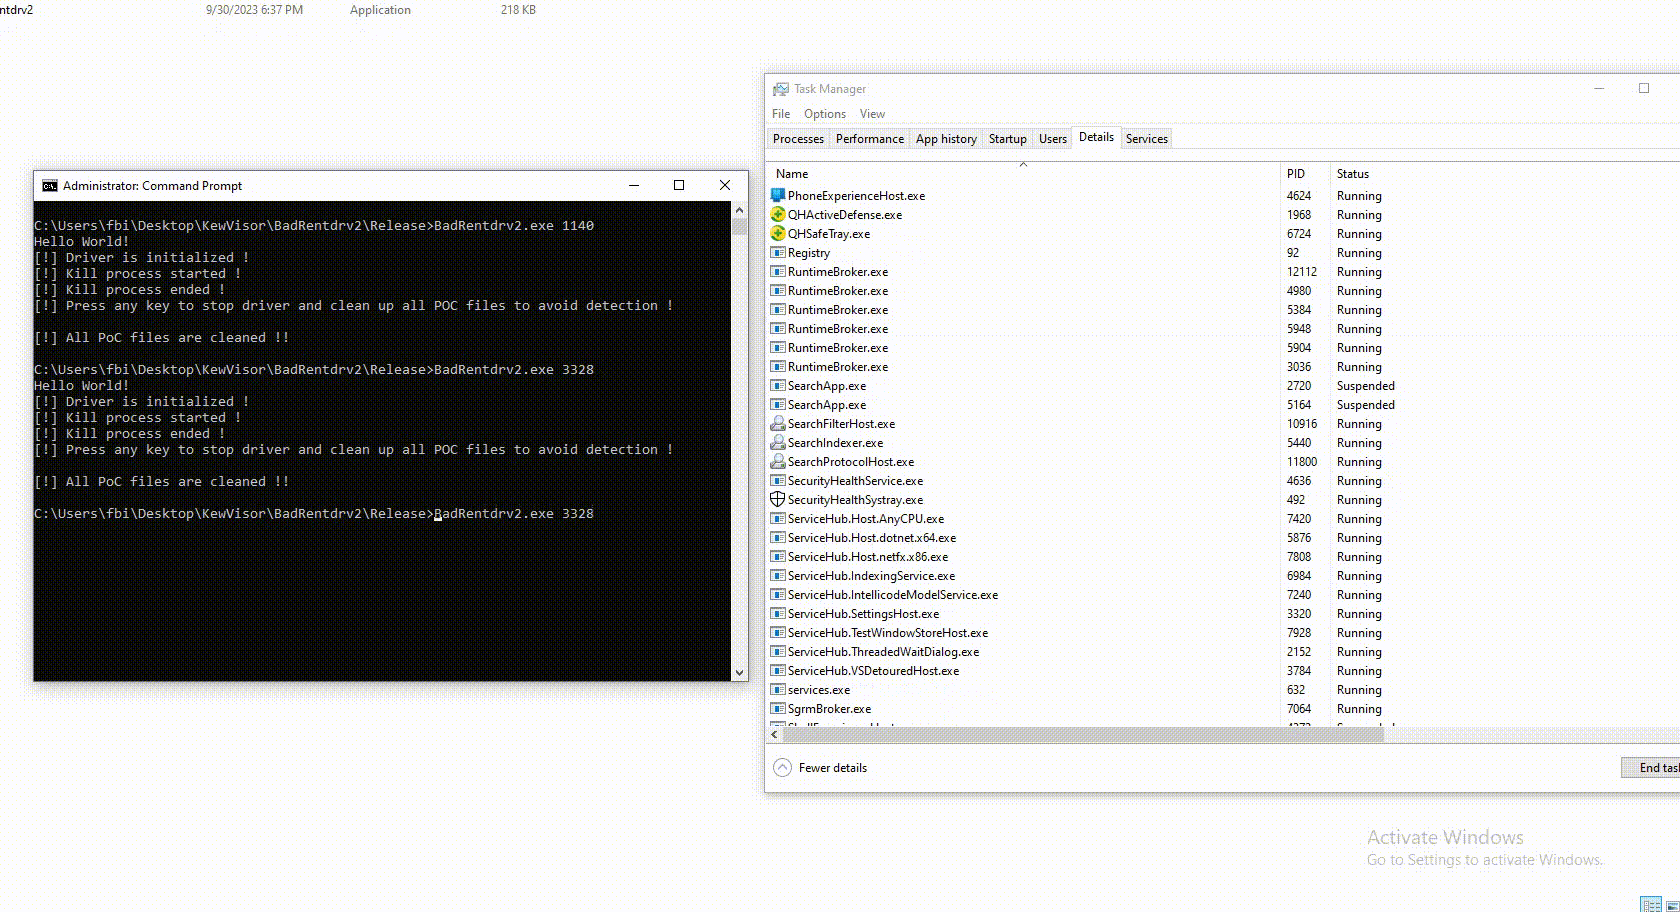 keowu/badrentdrv2
A vulnerable driver exploited by me (BYOVD) that is capable of terminating several EDRs and antivirus software in the market, rendering them…
 yarrick/iodine
Tunnel IPv4 data through DNS servers to bypass firewall restrictions and provide covert network access for penetration testing.
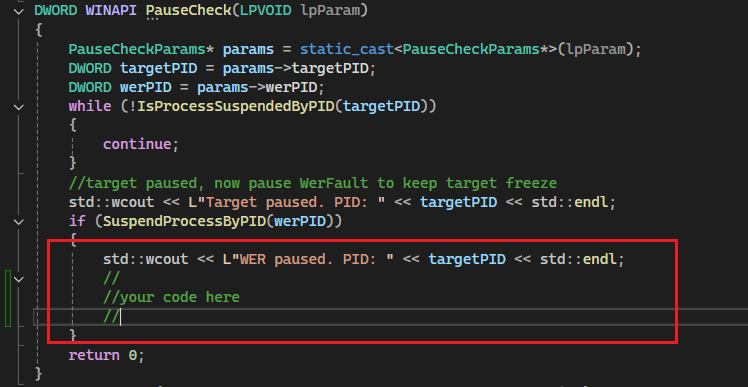 twosevenonet/edr-freeze
EDR-Freeze is a tool that puts a process of EDR, AntiMalware into a coma state.
 pmsosa/duckhunt
:dart: Prevent RubberDucky (or other keystroke injection) attacks
 hkl1x/bypass_av
Evades AV and sandboxes on Windows using anti-sandbox checks, ntdll unhooking, dynamic API resolution, and multi-layer shellcode obfuscation…
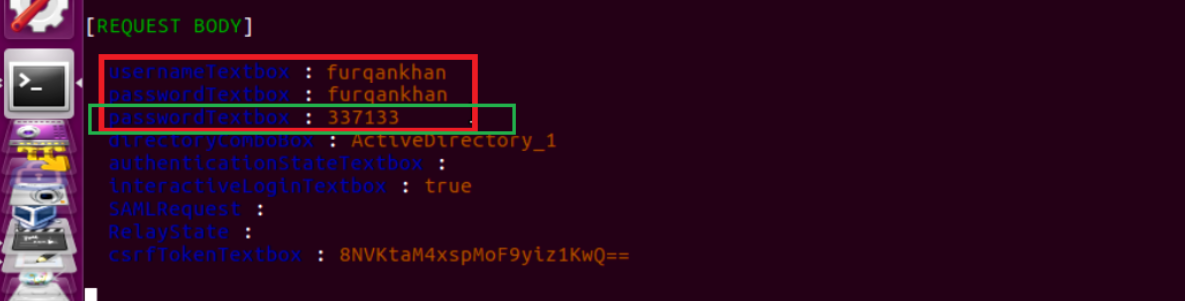 furqankhan1/cve-2019-13498
CVE-2019-13498
 ak3zaidan/trust-decision-security
Reverse Engineer of Trust Decision Chinese Security