
core
 opnsense/core
OPNsense GUI, API and systems backend
api-securitycaptcha-bypassconfiguration-auditing+4
opnsense/coreOPNsense GUI, API and systems backend
 rofl0r/proxychains-ng
proxychains ng (new generation) - a preloader which hooks calls to sockets in dynamically linked programs and redirects it through one or more…
 b3rt1ng/koi
Multi-session reverse shell handler with PTY upgrade, post-exploitation modules, Layer 3 tunneling, payload obfuscation for EDR evasion, session…
 davidsonrafaelk/evillimiter
Tool that monitors, analyzes and limits the bandwidth of devices on the local network without administrative access
 cifertech/esp32-div
ESP32DIV is a multi-purpose wireless offensive and defensive toolkit powered by an ESP32
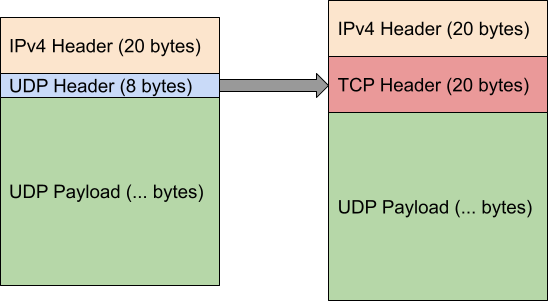 dndx/phantun
Transforms UDP stream into (fake) TCP streams that can go through Layer 3 & Layer 4 (NAPT) firewalls/NATs.
 shredzwho/ig-detective
OSINT tool researched and designed to hunt down IG handles
 umidguluzada/cyberdefense-lab
A complete Blue Team Cybersecurity Lab featuring pfSense, Suricata, and ELK Stack for network monitoring and threat detection.
 mtaha-sec/bash-apocalypse
Recreating Shellshock (CVE-2014-6271) - the bash vulnerability that endangered millions of servers. Automated exploitation toolkit + Burp Suite…
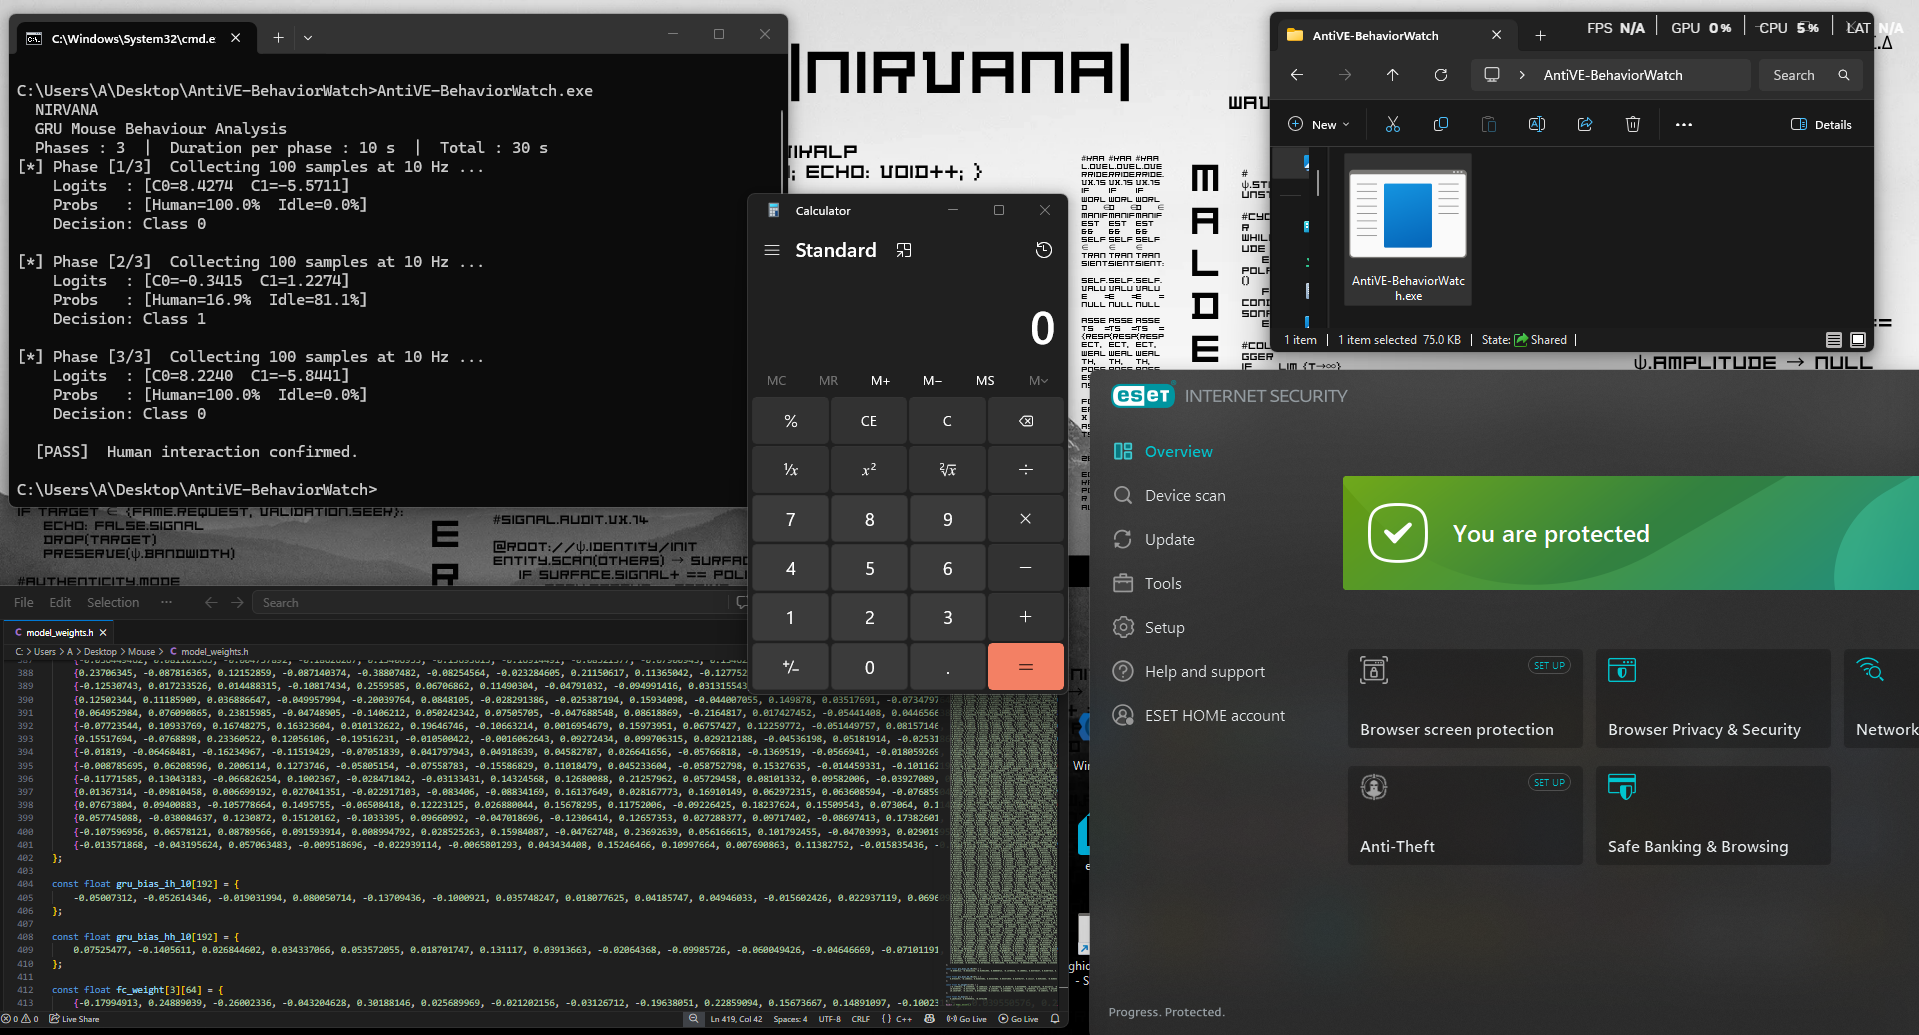 nirvanaon/antive-behaviorwatch
Embedded GRU neural network for real-time human behavior verification via mouse movement analysis, detecting automated analysis systems, sandboxes,…
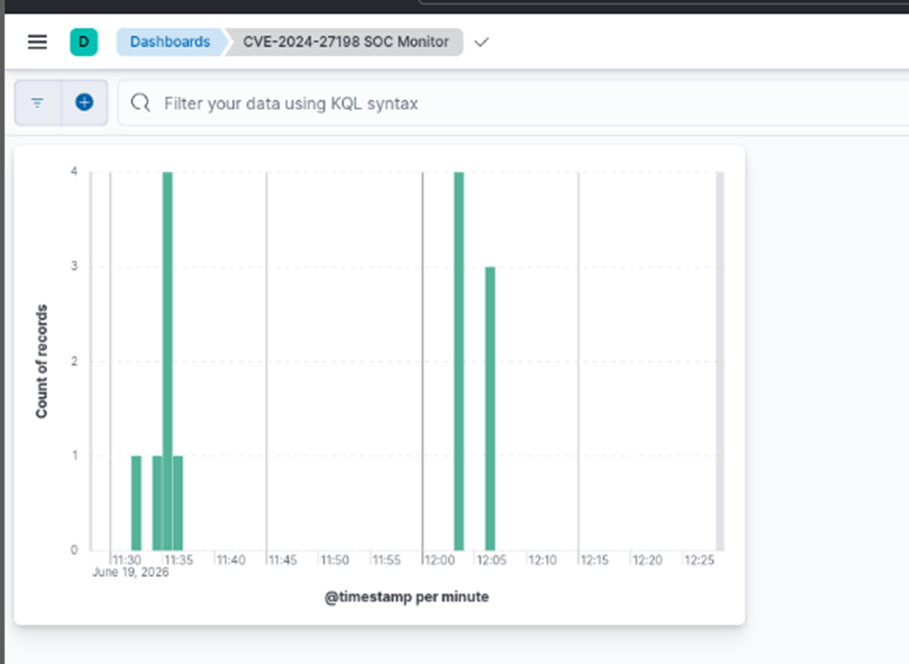 ptd200110/cve-2024-27198-soc-lab
SOC detection and incident response lab simulating CVE-2024-27198 authentication bypass in JetBrains TeamCity. Includes ELK SIEM, Suricata IDS, Sigma…
 aircrack-ng/mdk4
IEEE 802.11 Wi-Fi testing tool for protocol weakness exploitation, including beacon flooding, deauthentication, packet fuzzing, and IDS evasion.…
 the-snek-initiative/snek_equinox
Repository hosting a hypothetical EDR Spoofer, as discovered originally by Nightmare-Eclipse
 trnguyen03/activemq-ids-ips-lab
IDS/IPS lab for detecting and preventing Apache ActiveMQ RCE (CVE-2023-46604) using GVM, Nmap, Snort, iptables, and UFW.
 xm0kht4r/av-edr-killer
AV/EDR processes termination by exploiting a vulnerable driver (BYOVD)
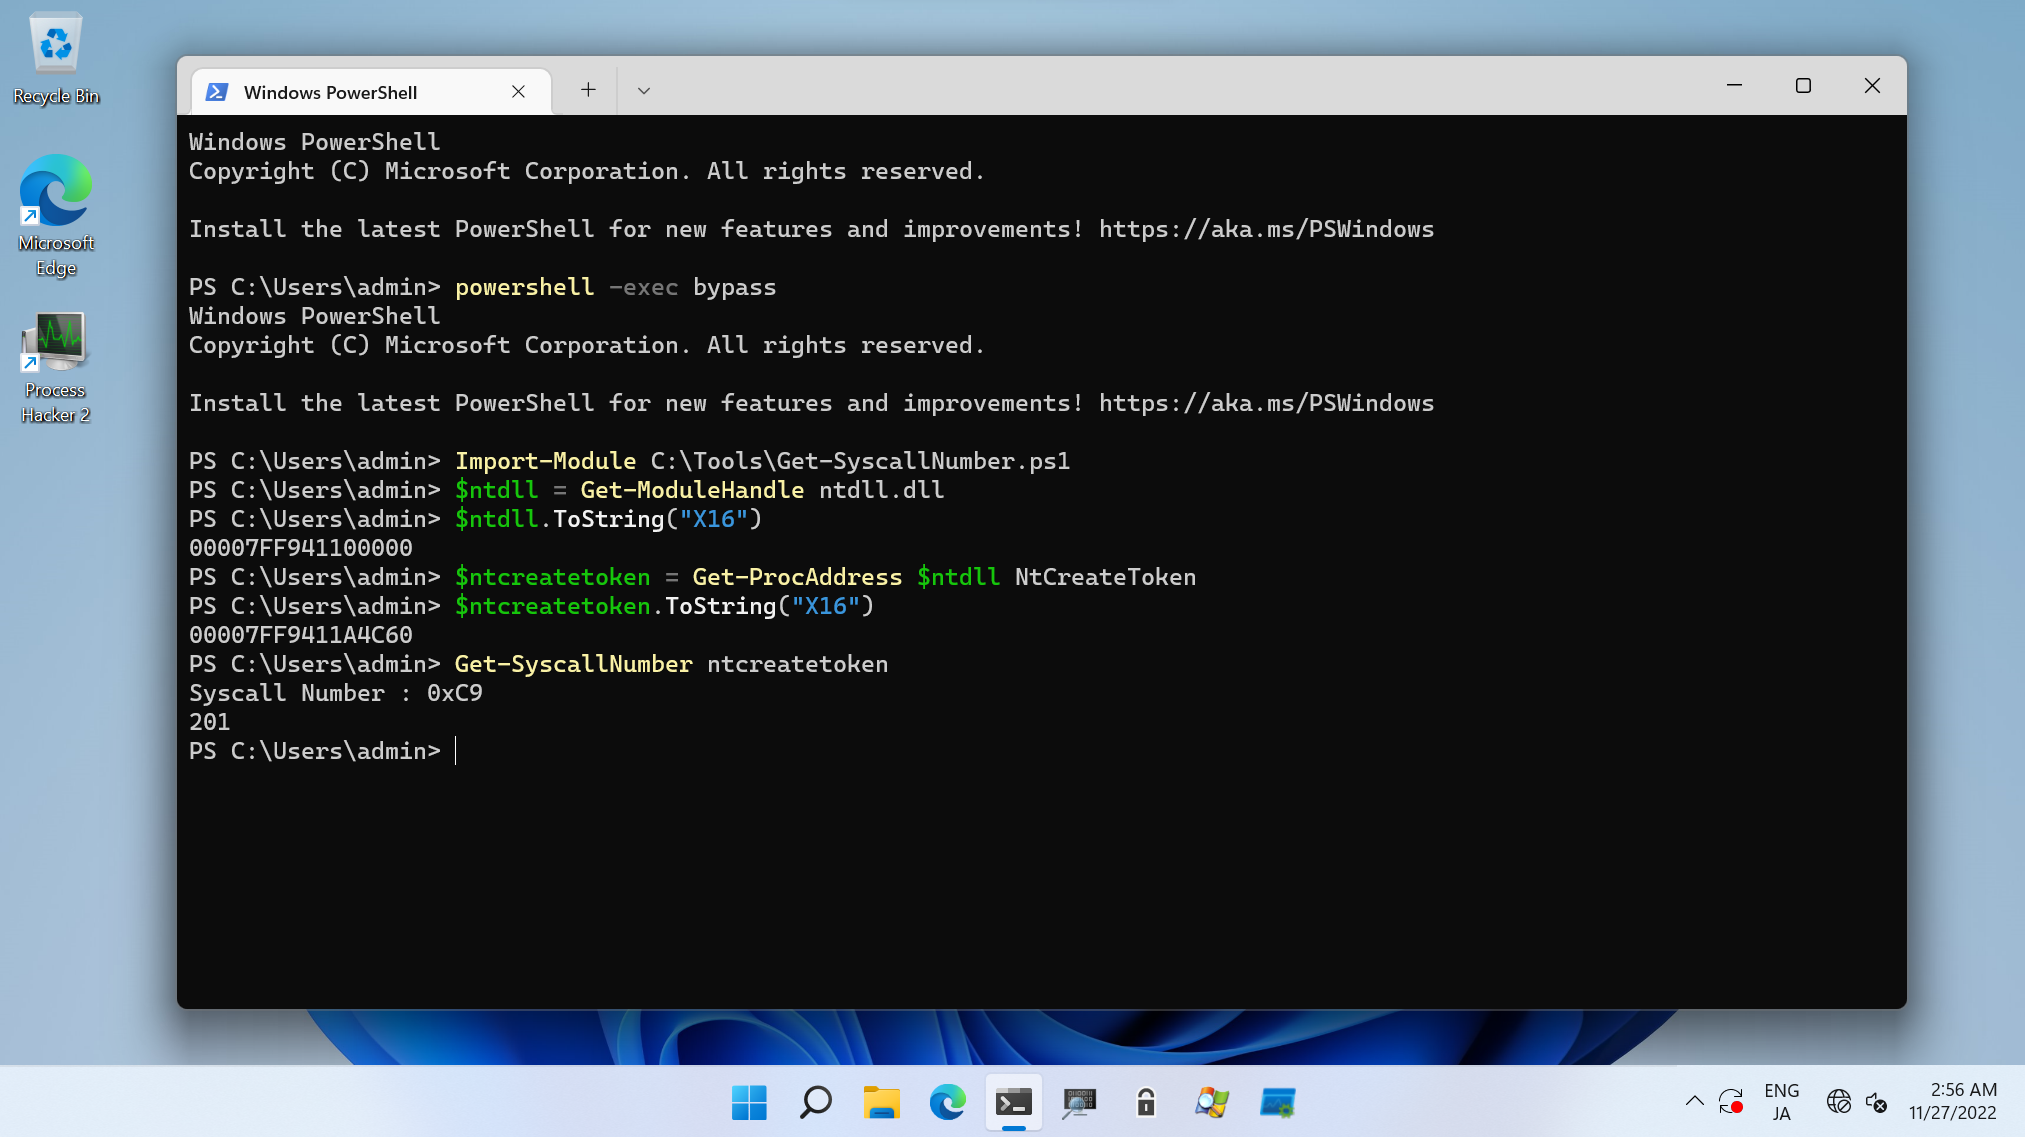 daem0nc0re/atomicsyscall
Tools and PoCs for Windows syscall investigation.
 xkiian/awswaf
AWS WAF Solver, full reverse implemented in 100% Python & Golang.
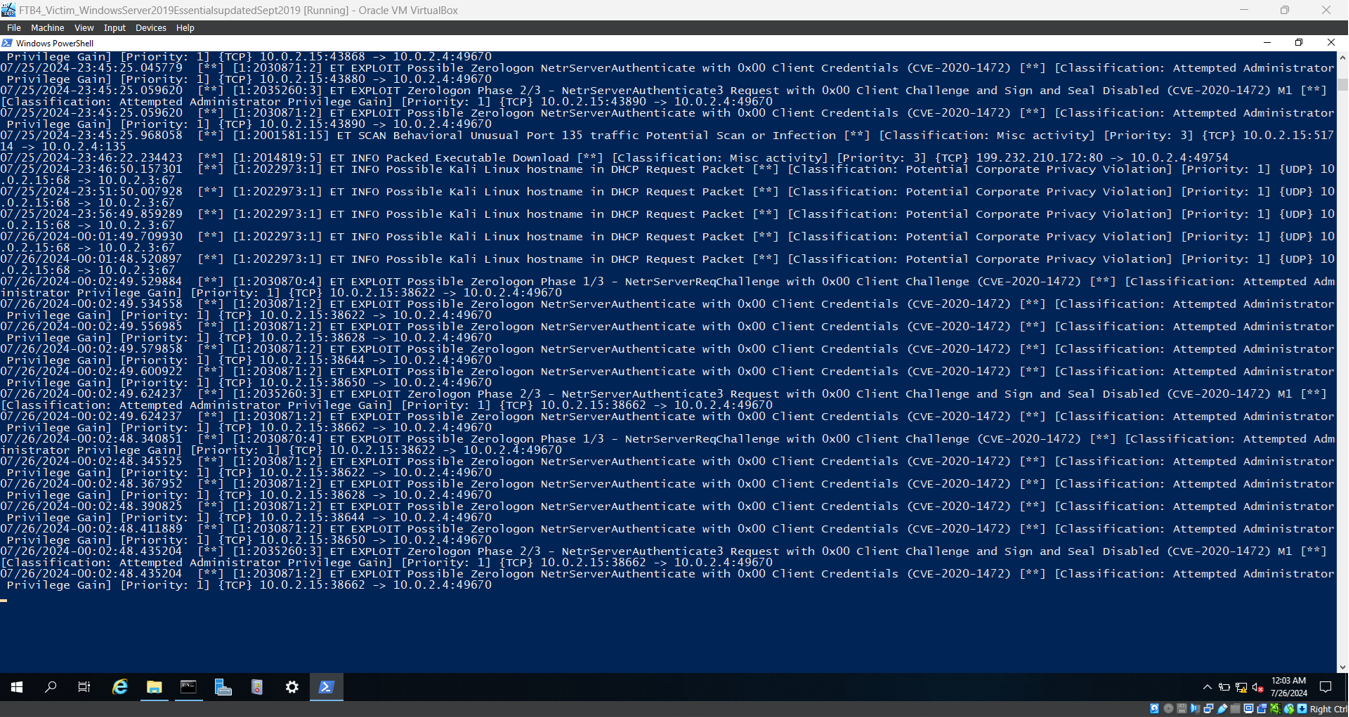 tdevworks/cve-2020-1472-zerologon-demo-detection-mitigation
Educational demo of CVE-2020-1472 (ZeroLogon) detection using Windows Event Logs and Suricata IDS, plus mitigation via Windows Updates. Includes…