

RC4Decryption
 weedhashpeddler/rc4decryption
Abuses the Microsoft-signed tlscsp.dll LOLBin to run RC4 encrypt/decrypt via LsCsp_EncryptHwid, patching the hardcoded key in memory for BYOK…
binary-analysiscryptographydefensive-tools+6
37
weedhashpeddler/rc4decryptionAbuses the Microsoft-signed tlscsp.dll LOLBin to run RC4 encrypt/decrypt via LsCsp_EncryptHwid, patching the hardcoded key in memory for BYOK…
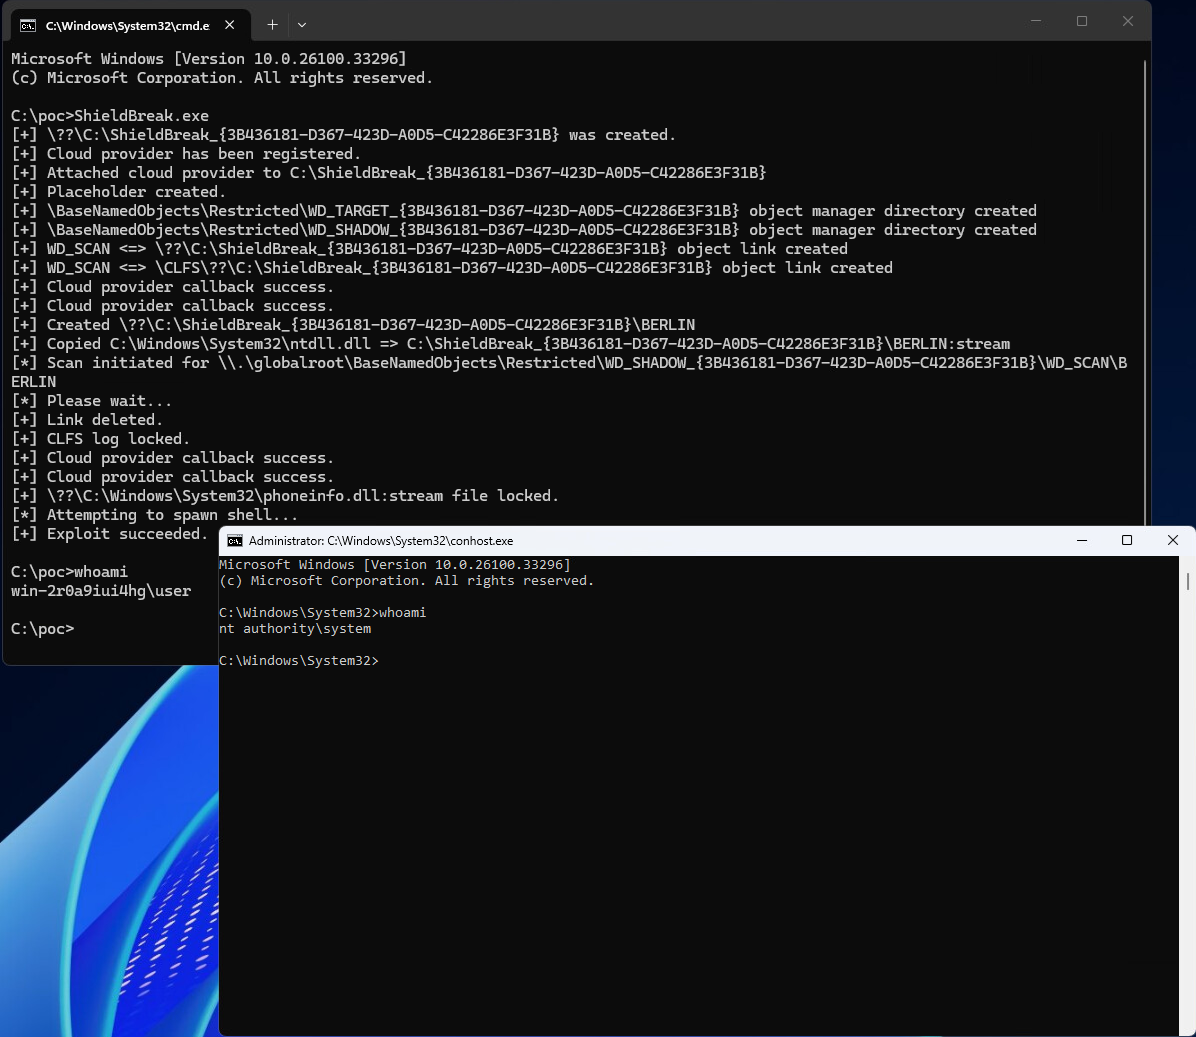 1neptune/shieldbreak
Windows Defender 0day proof-of-concept demonstrating a patch bypass for CVE-2026-69414, targeting Windows 11 25H2 and Server 2025 to evade endpoint…
 u1tr0nex/cve-2022-30190-follina-lab
Full exploit chain lab and Suricata IDS detection for CVE-2022-30190 (Follina) - MSDT RCE
 bhatbhupendra/moniker-link--cve-2024-21413-
Educational guide on CVE-2024-21413, the Outlook zero-click Moniker Link vulnerability, covering attack flow, NTLM credential capture, detection with…
 xm0kht4r/ven0m-ransomware
Fully undetectable and evasive ransomware written in Rust, leveraging a BYOVD technique to disable AV/EDR solutions on the infected systems.
 simoesctt/ctt-exchange-rce-v1.0---microsoft-exchange-exploit-cvss-10.0-critical-cve-2021-26855-cve-2021-27065
CTT-enhanced version of the Microsoft Exchange Server SSRF to RCE exploit (ProxyShell/ProxyLogon), another CVSS 10.0 critical vulnerability that…
 hwbp/lazyhook
Evade behavioral analysis by executing malicious code within trusted Microsoft call stacks, patchless hooking library IAT/EAT.
 exfil0/cve-2025-53770
A sophisticated, wizard-driven Python exploit tool targeting CVE-2025-53770, a critical (CVSS 9.8) unauthenticated remote code execution (RCE)…
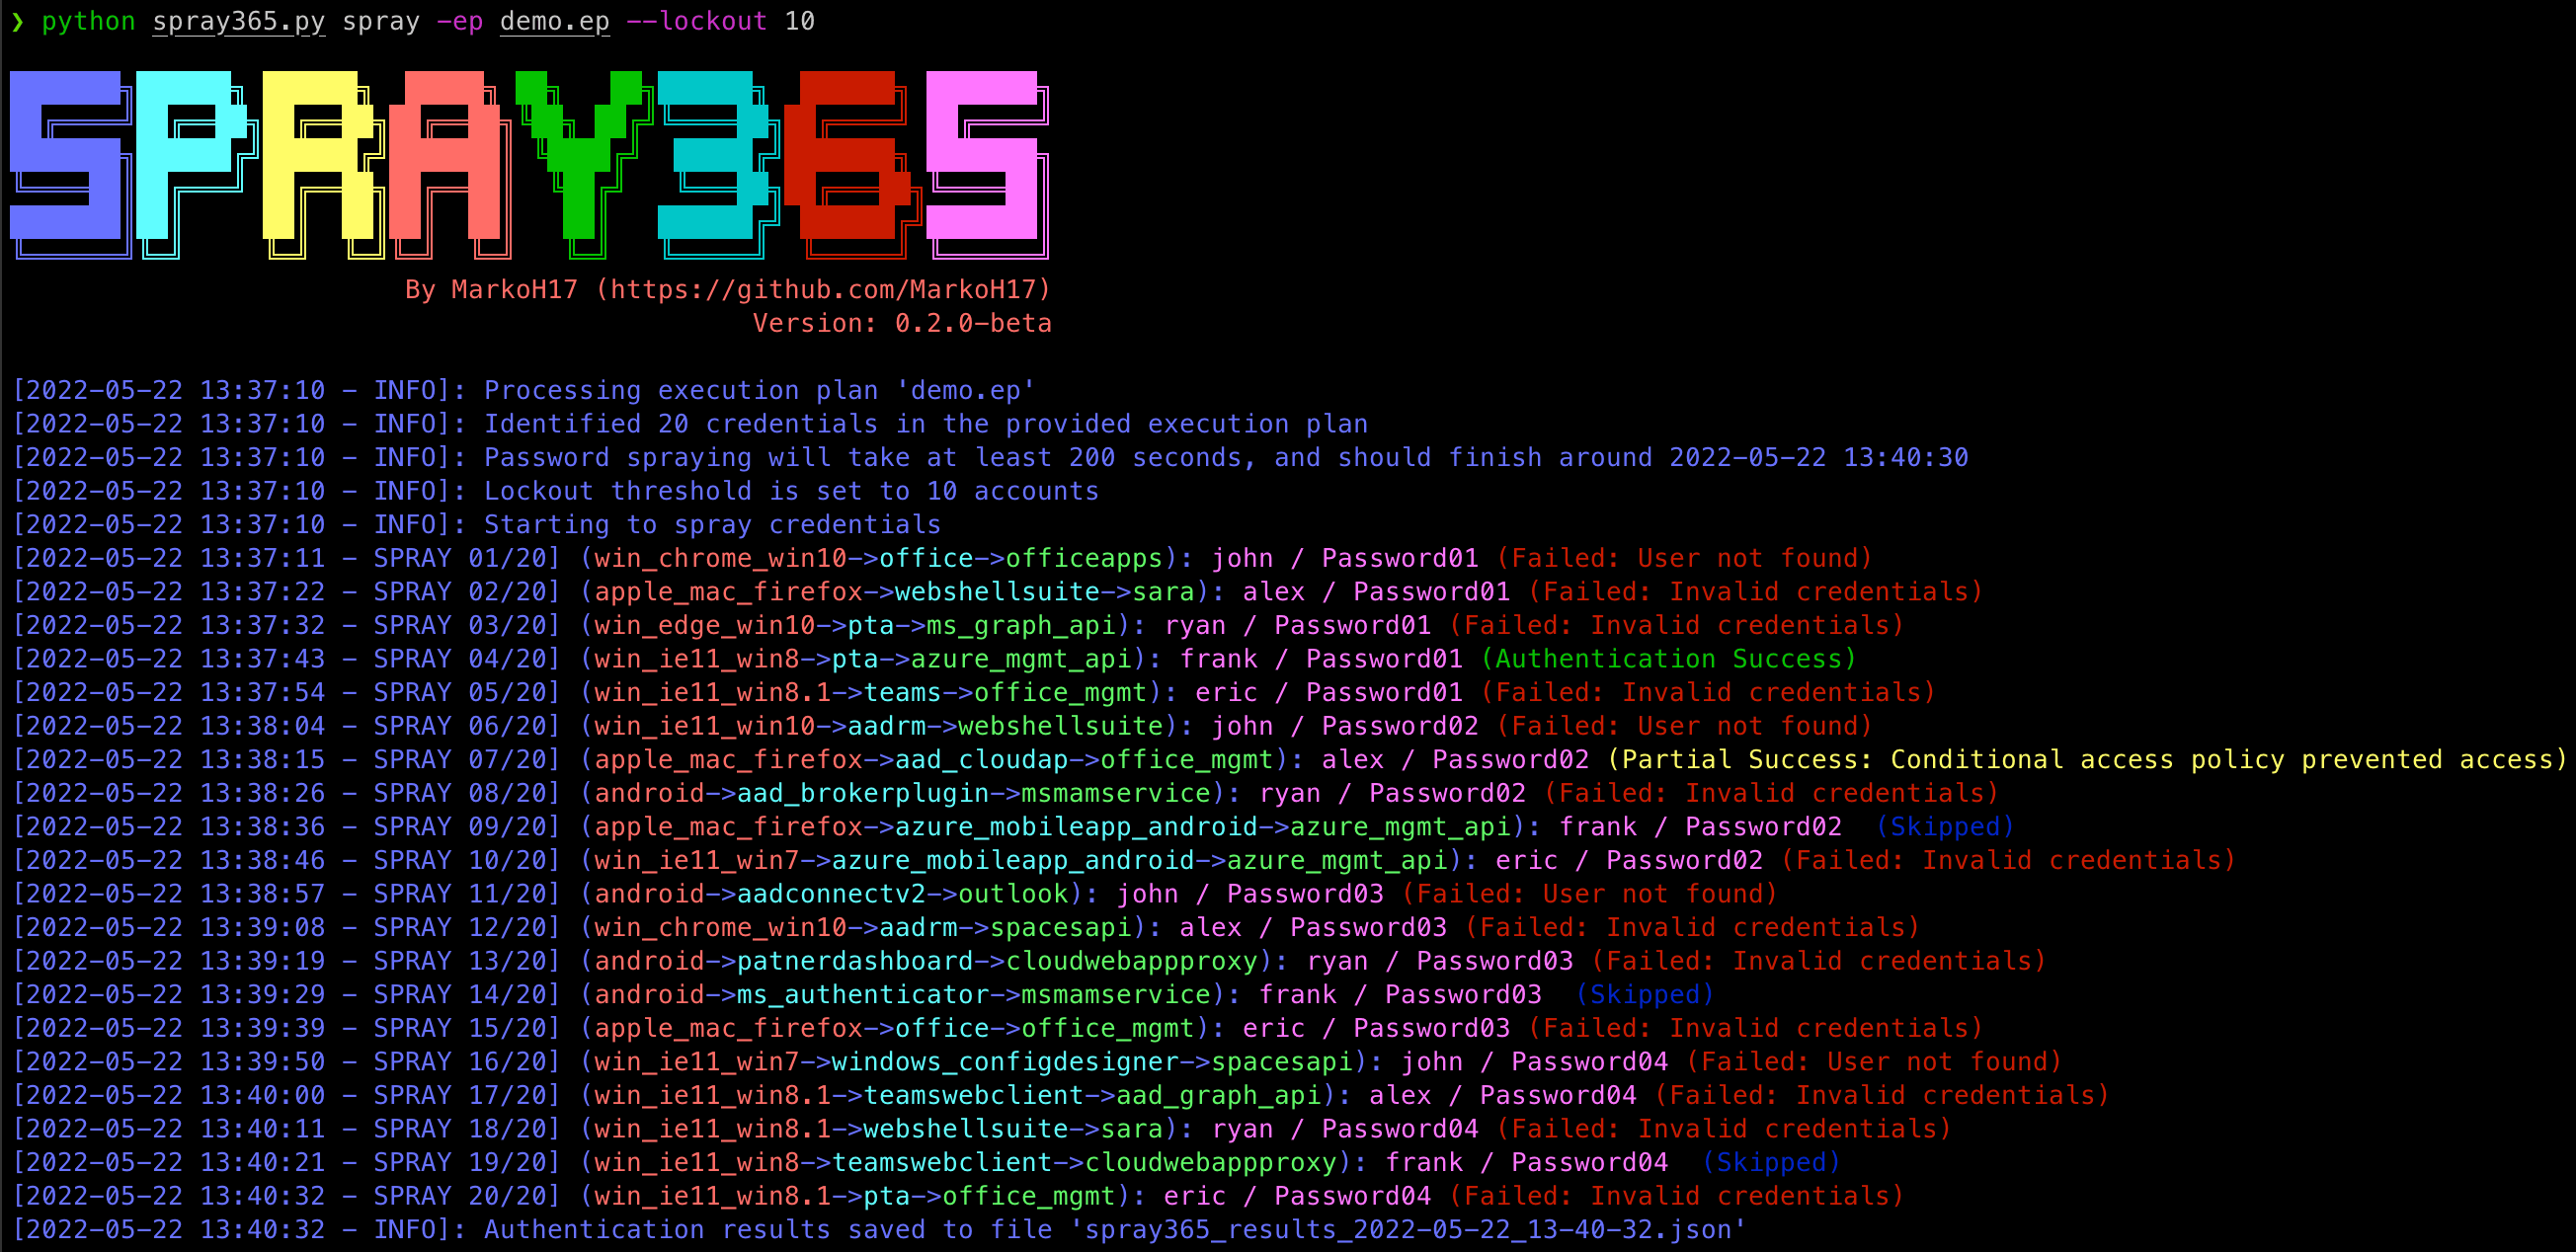 markoh17/spray365
Spray365 makes spraying Microsoft accounts (Office 365 / Azure AD) easy through its customizable two-step password spraying approach. The built-in…
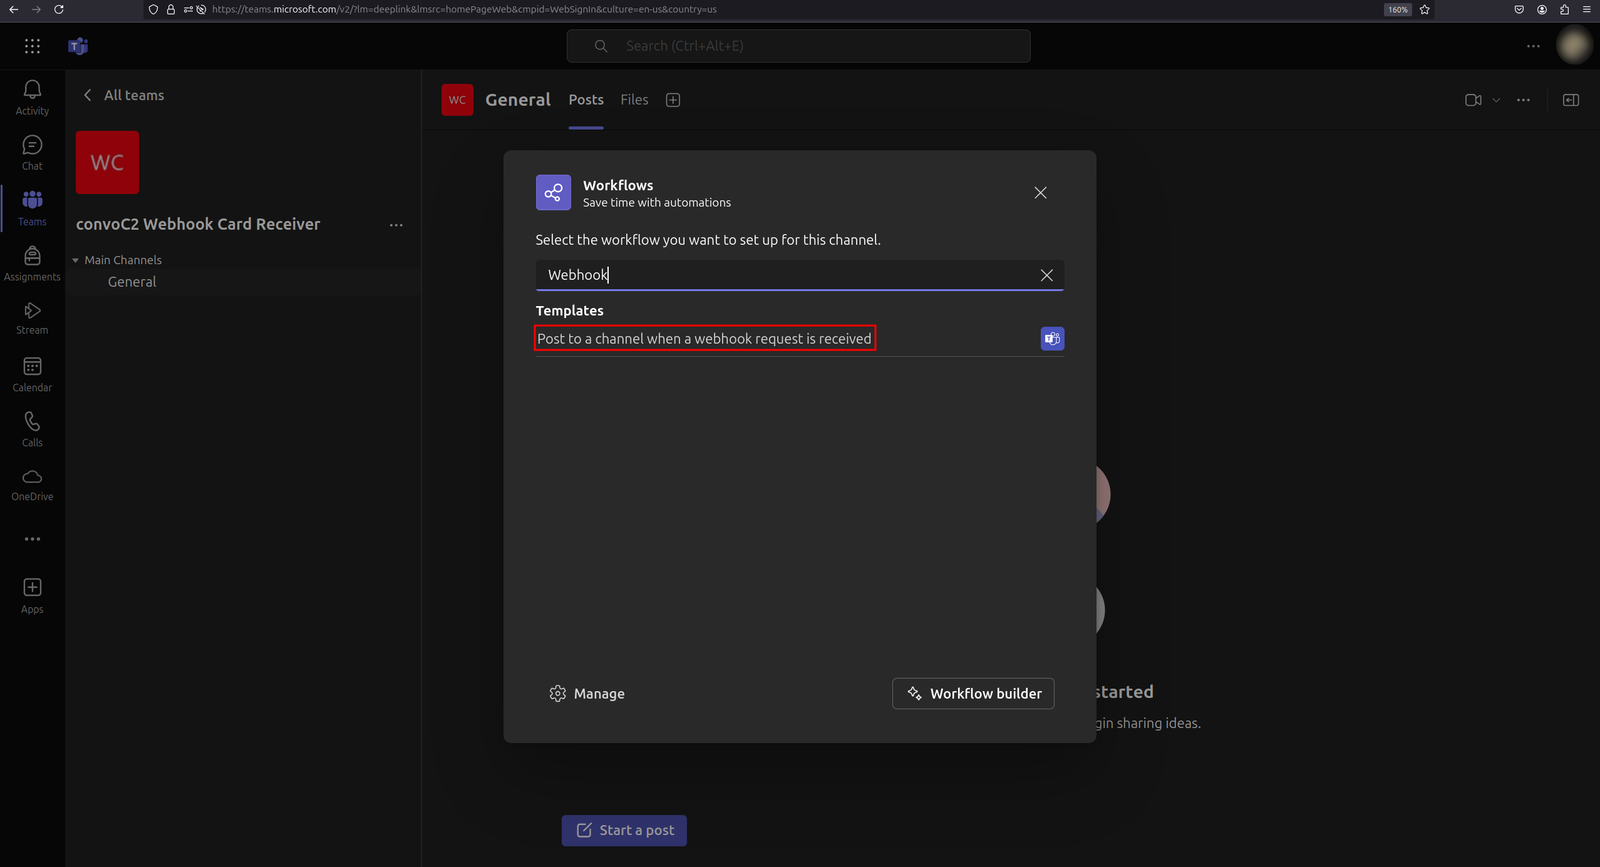 cxnturi0n/convoc2
C2 infrastructure over Microsoft Teams.
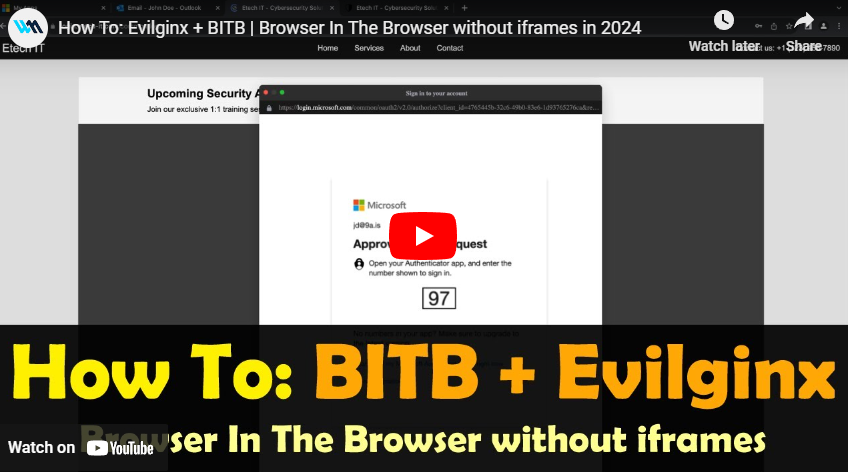 waelmas/frameless-bitb
A new approach to Browser In The Browser (BITB) without the use of iframes, allowing the bypass of traditional framebusters implemented by login…
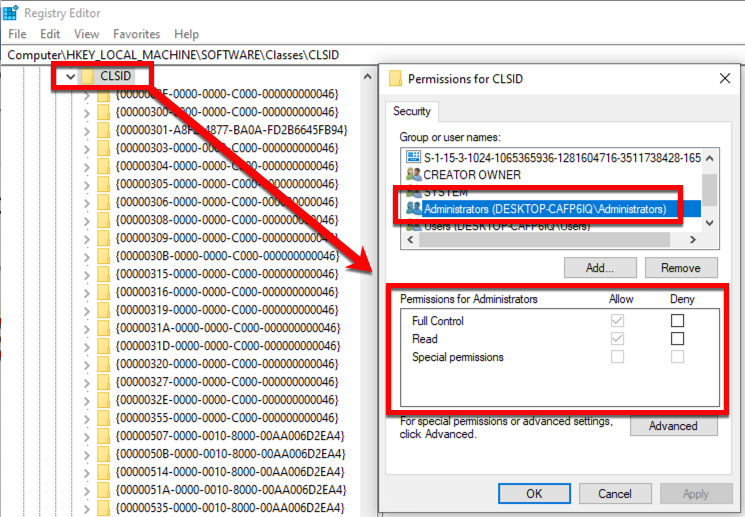 optiv/dent
A framework for creating COM-based bypasses utilizing vulnerabilities in Microsoft's WDAPT sensors.
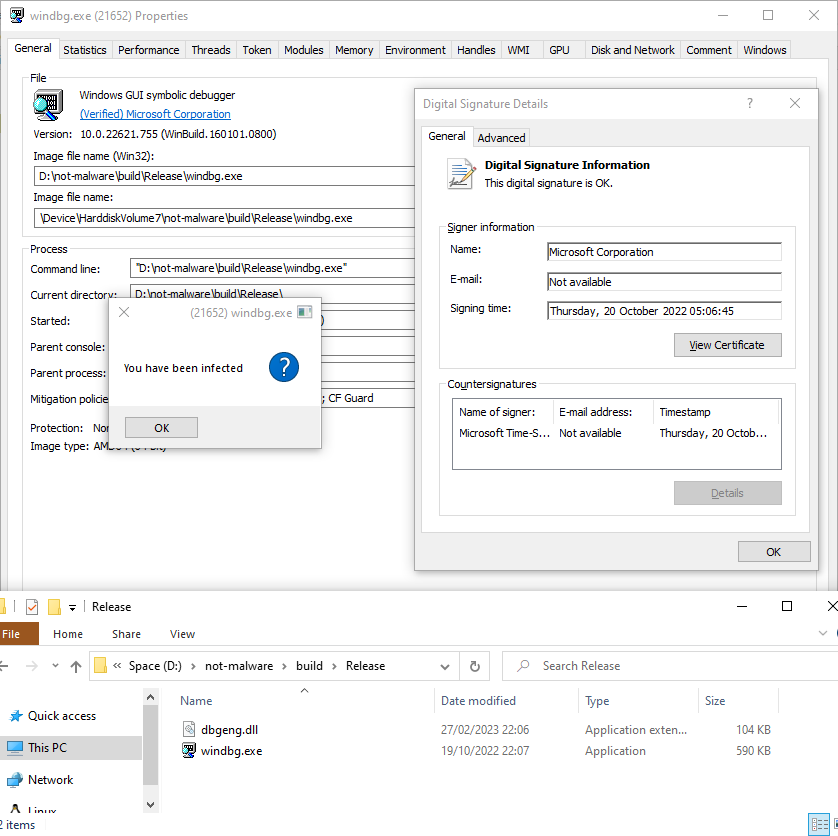 mrexodia/lolbin-poc
Small PoC of using a Microsoft signed executable as a lolbin.
 nvisosecurity/cobaltwhispers
CobaltWhispers is an aggressor script that utilizes a collection of Beacon Object Files (BOF) for Cobalt Strike to perform process injection,…
 advanced-threat-research/cve-2020-16899
CVE-2020-16899 - Microsoft Windows TCP/IP Vulnerability Detection Logic and Rule
 nu11secur1ty/iis-backdoor
Stealthy IIS backdoor using hidden ISAPI filter for persistent remote access, data exfiltration, and on-the-fly exploit injection via custom HTTP…