
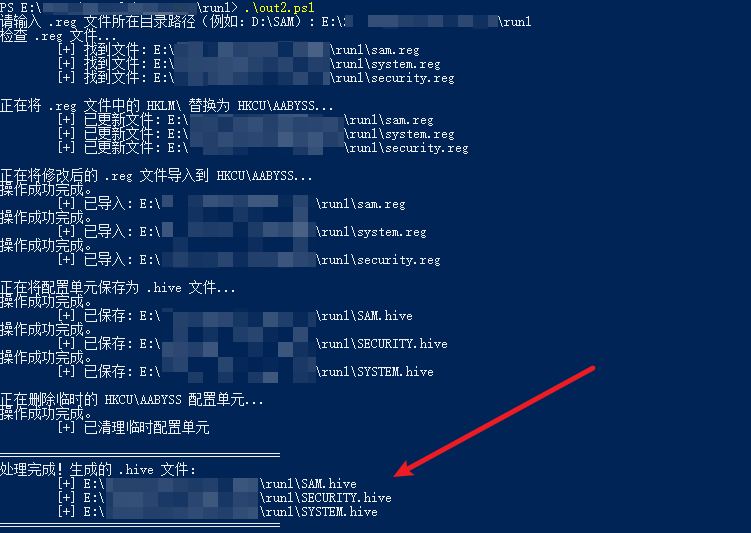
HashDump-BypassEDR
 aabysszg/hashdump-bypassedr
Windows绕过EDR实现DumpHash
hash-analysisids-ips-evasionpassword-attacks+3
2621 month ago
aabysszg/hashdump-bypassedrWindows绕过EDR实现DumpHash
 malwareapilib/malwareapilibrary
collection of apis used in malware development
 mr-un1k0d3r/windows-signedbinary
Mutates signed Windows binaries to retain valid catalog signatures while changing file hashes, bypassing hash-based endpoint blocks and exposing…
 secretsquirrel/recomposer
Randomly changes Win32/64 PE Files for 'safer' uploading to malware and sandbox sites.