CobaltWhispers
 nvisosecurity/cobaltwhispers
CobaltWhispers is an aggressor script that utilizes a collection of Beacon Object Files (BOF) for Cobalt Strike to perform process injection,…
adversarial-attackcommand-and-controlids-ips-evasion+4
243
nvisosecurity/cobaltwhispersCobaltWhispers is an aggressor script that utilizes a collection of Beacon Object Files (BOF) for Cobalt Strike to perform process injection,…
 yo-yo-yo-jbo/macos_app_structure
Educational deep dive into macOS app bundles, plist files, and launchd process behavior, with offensive security notes on packaging payloads as .app…
 florylsk/execit
Execute shellcode files with rundll32
 maldev-academy/maldevacademyldr.2
RunPE implementation with multiple evasive techniques (2)
 blacksnufkin/nyxinvoke
NyxInvoke is a Rust CLI tool for running .NET assemblies, PowerShell, and BOFs with Patchless AMSI and ETW bypass features. with Dual-build support
 duhirsch/moveedr
Permanently disable EDRs as local admin
 encrypter15/cve-2025-50165-x64-exploit
Generates weaponized JPEG files exploiting CVE-2025-50165 (Windows Graphics RCE) with custom x64 shellcode, heap spray, ROP chain, and AV/EDR evasion…
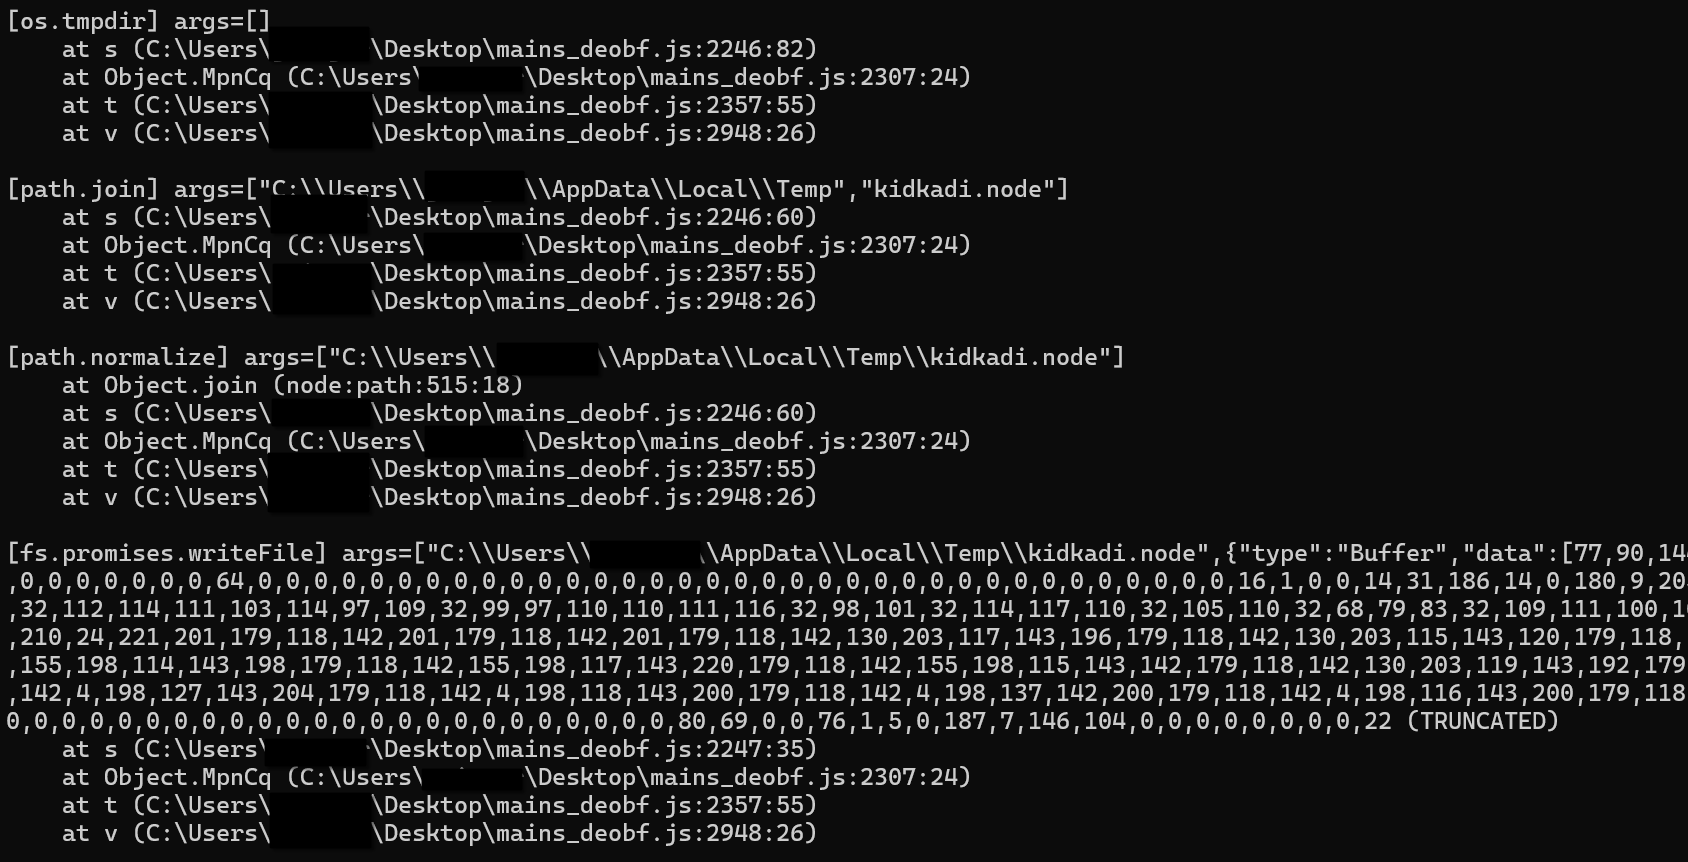 checkpointsw/nodejs-tracer
Runtime tracer for Node.js malware analysis that hooks core modules, logs calls, spoofs anti-analysis checks, and captures file writes and HTTP…
 monoxgas/srdi
Shellcode implementation of Reflective DLL Injection. Convert DLLs to position independent shellcode
 kvesel/zipbrk
Zip file format fuzzer and multi-tool.
 secretsquirrel/recomposer
Randomly changes Win32/64 PE Files for 'safer' uploading to malware and sandbox sites.
 thewover/donut
Generates x86, x64, or AMD64+x86 position-independent shellcode that loads .NET Assemblies, PE files, and other Windows payloads from memory and runs…
 jthuraisamy/syswhispers
AV/EDR evasion via direct system calls.
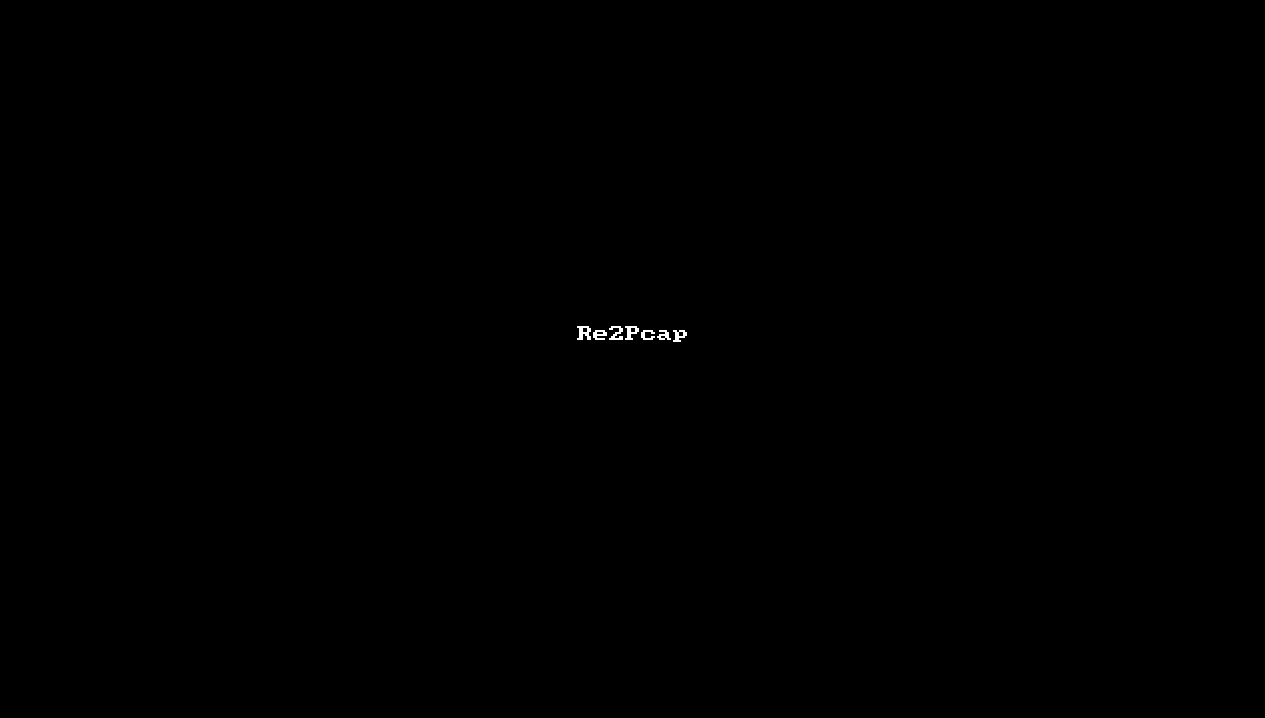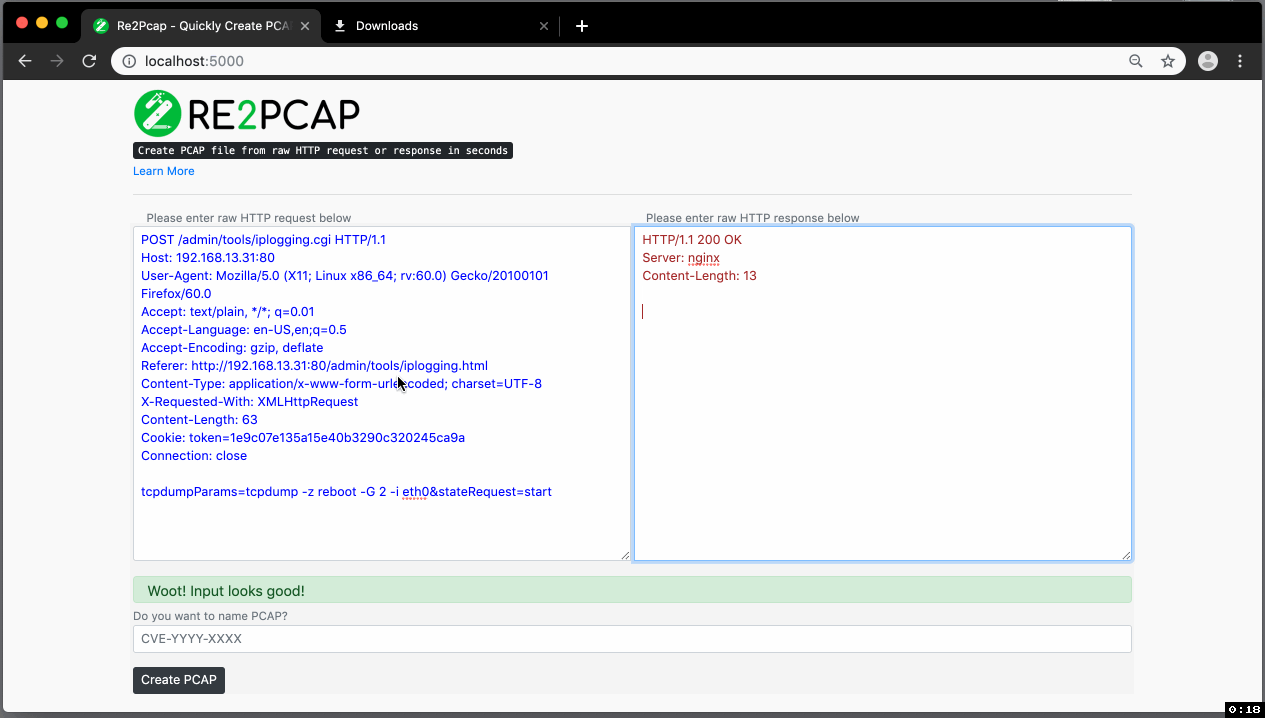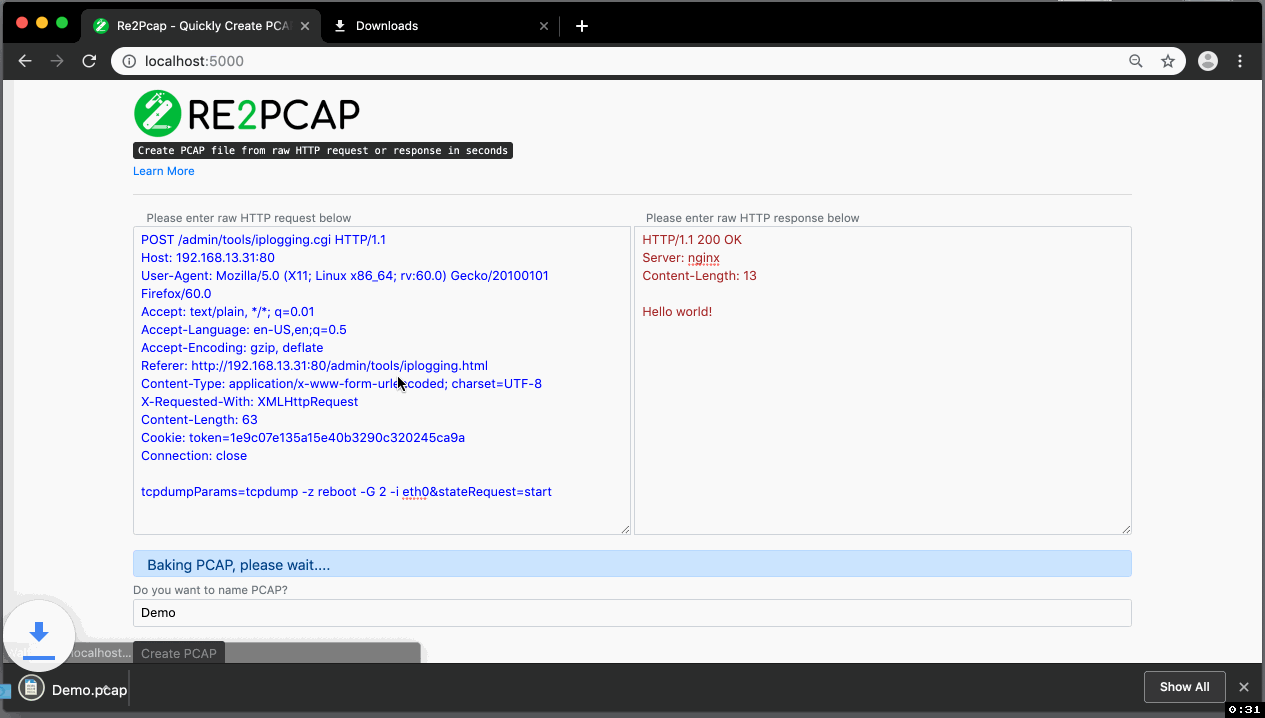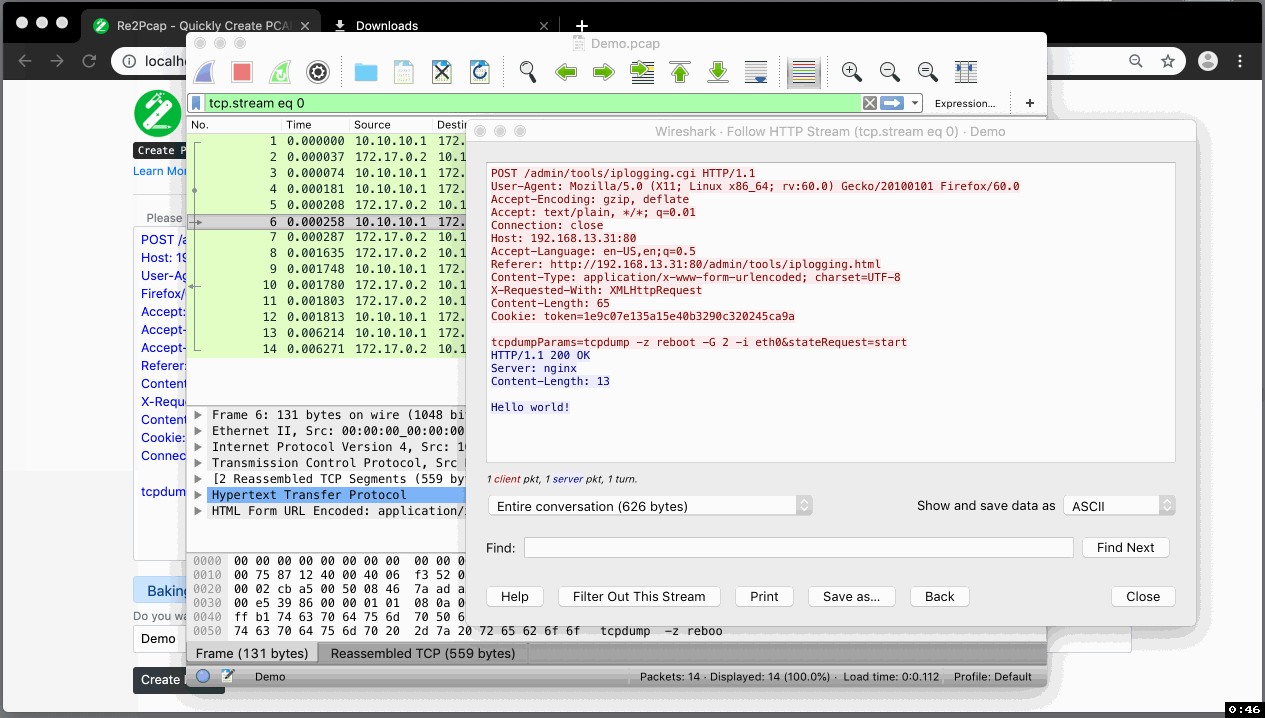 cisco-talos/re2pcap
Convert raw HTTP requests/responses into PCAP files for testing Snort IDS rules and network security analysis. Supports Docker deployment and…
 jthuraisamy/syswhispers2
AV/EDR evasion via direct system calls.
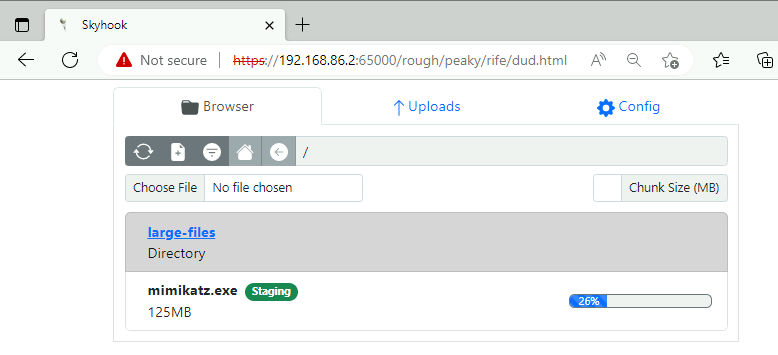 blackhillsinfosec/skyhook
A round-trip obfuscated HTTP file transfer setup built to bypass IDS detections.
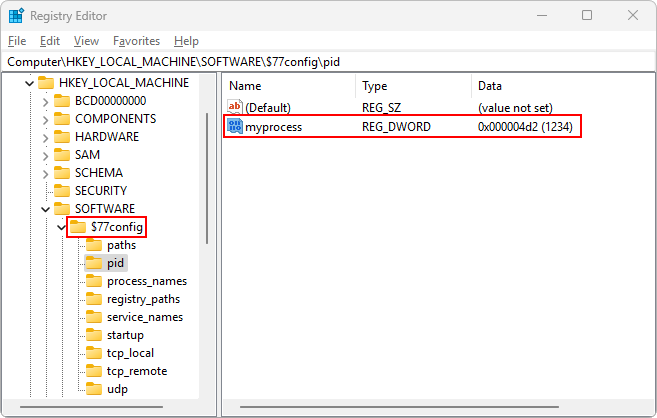 bytecode77/r77-rootkit
Fileless ring 3 rootkit with installer and persistence that hides processes, files, network connections, etc.