
Darkcloak
 0x574r/darkcloak
Linux process identity cloaking tool that spoofs comm, argv, cmdline, environ, exe path, and VMAs via an 11-phase prctl pipeline to impersonate…
binary-analysisfingerprint-spoofingids-ips-evasion+6
11
0x574r/darkcloakLinux process identity cloaking tool that spoofs comm, argv, cmdline, environ, exe path, and VMAs via an 11-phase prctl pipeline to impersonate…
 gmh5225/f31
Tool for hiding Kali Linux on the network
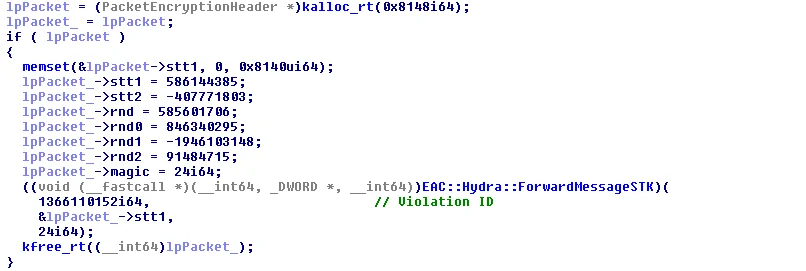 gmh5225/eac-kernel-packet-fucker
Reverse-engineered Easy Anti-Cheat kernel driver bypass that intercepts memory allocation to suppress violation packets, with report decryption…
 voidsecsoftwares/voidsyscall
Cross-platform syscall-powered implant & C2 — direct syscalls (Win), raw syscalls (Linux), HTTPS/DNS/ICMP channels. No winapi layer.
 davidsonrafaelk/evillimiter
Tool that monitors, analyzes and limits the bandwidth of devices on the local network without administrative access
 hika-sec/terminator_killer
Kernel-mode process killer exploiting CVE-2026-0828 (BYOVD) to terminate protected processes via a vulnerable signed driver, bypassing PPL and…
 kudaes/dumpy
Reuse open handles to dynamically dump LSASS.
 mr-un1k0d3r/edrs
Red team tool for EDR evasion: dynamically resolves syscall IDs, patches ntdll stubs, unhooks IAT hooks, and lists hooked APIs from major EDR vendors.
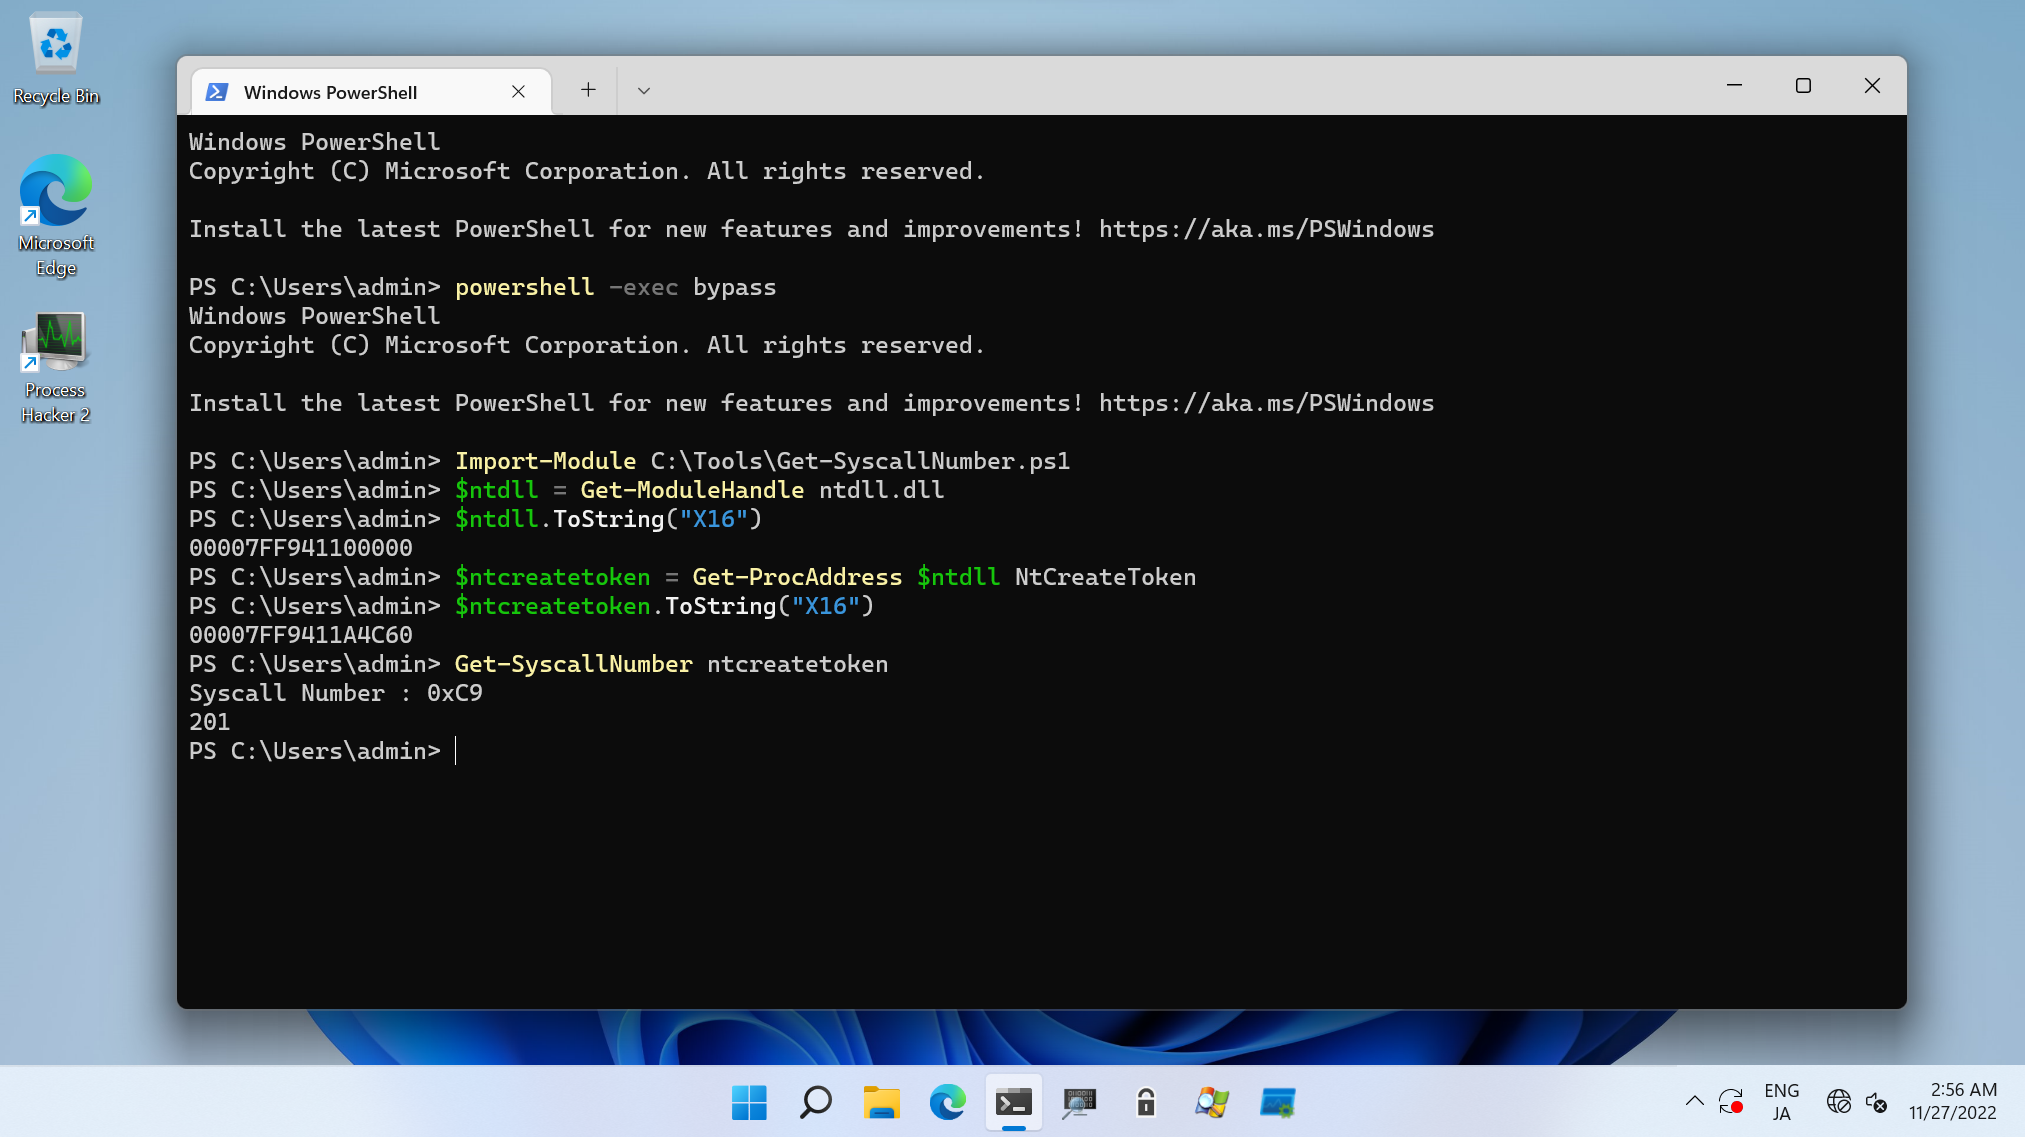 daem0nc0re/atomicsyscall
Tools and PoCs for Windows syscall investigation.
 saadahla/shellcode-hide
This repo contains : simple shellcode Loader , Encoders (base64 - custom - UUID - IPv4 - MAC), Encryptors (AES), Fileless Loader (Winhttp, socket)
 susmdt/effective-waffle
yet another sleep encryption thing. also used the default github repo name for this one.
 lleon1435/kernel_vadinjector
Windows 10 DLL Injector via Driver utilizing VAD and hiding the loaded driver
 netero1010/edrsilencer
A tool uses Windows Filtering Platform (WFP) to block Endpoint Detection and Response (EDR) agents from reporting security events to the server.
 yolop0wn/echodrv
Exploitation of echo_driver.sys
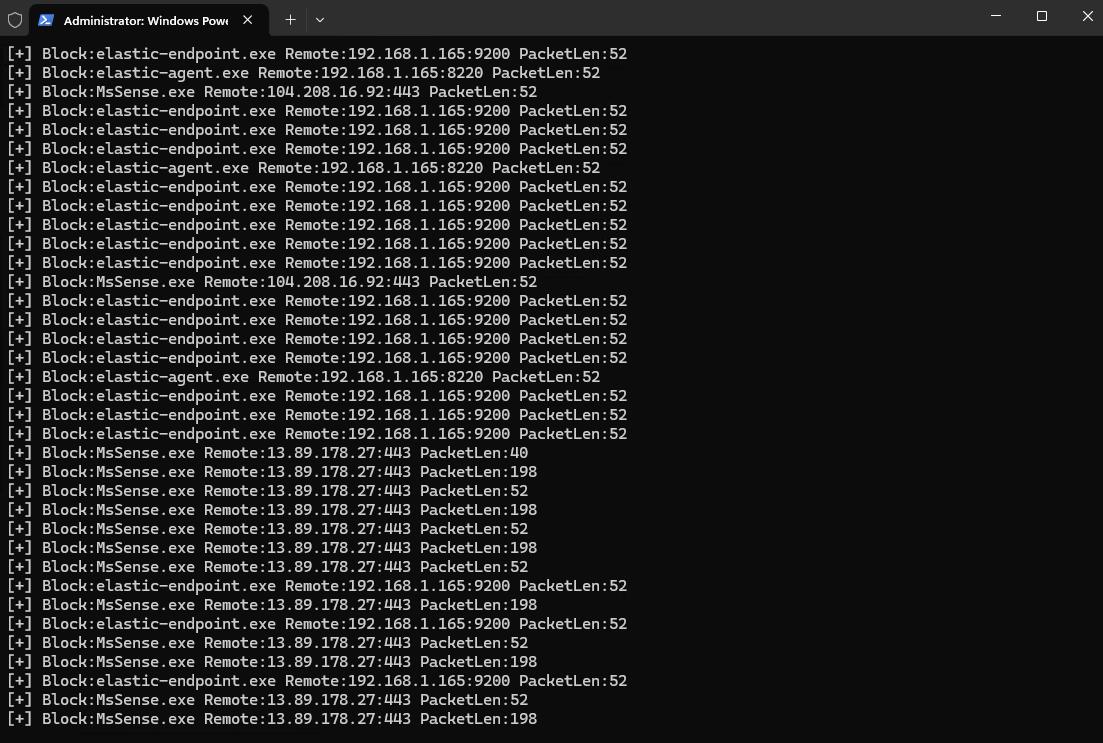 senzee1984/edrprison
Leverage a legitimate WFP callout driver to prevent EDR agents from sending telemetry
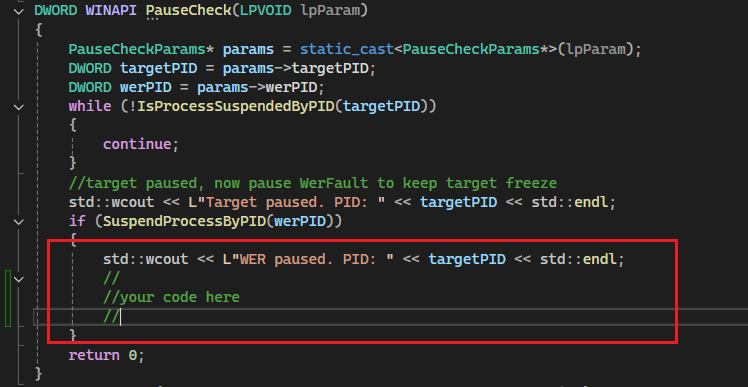 twosevenonet/edr-freeze
EDR-Freeze is a tool that puts a process of EDR, AntiMalware into a coma state.
 0xdea/blindsight
Red teaming tool to dump LSASS memory, bypassing basic countermeasures.
 vxfemboy/ghostport
A high-performance port spoofing tool built in Rust. Confuse port scanners with dynamic service emulation across all ports. Features customizable…