
TinyLoad
 iamsopotatoe-coder/tinyload
Open source Windows x64 PE packer and crypter. Compresses and encrypts executables with a custom virtual machine into a self extracting stub.
binary-analysisencryption-decryption-toolsexploitation+5
188
iamsopotatoe-coder/tinyloadOpen source Windows x64 PE packer and crypter. Compresses and encrypts executables with a custom virtual machine into a self extracting stub.
 bishopfox/sliver
Adversary Emulation Framework
 bhdresh/dejavu
DejaVU - Open Source Deception Framework
 rapid7/metasploit-framework
Open-source exploitation framework with modular payload, encoder, and auxiliary system for penetration testing, vulnerability validation, and…
 crowdsecurity/crowdsec
Open-source IDS/IPS and WAF engine that analyzes logs and HTTP requests to detect and block malicious IPs, leveraging a crowdsourced community…
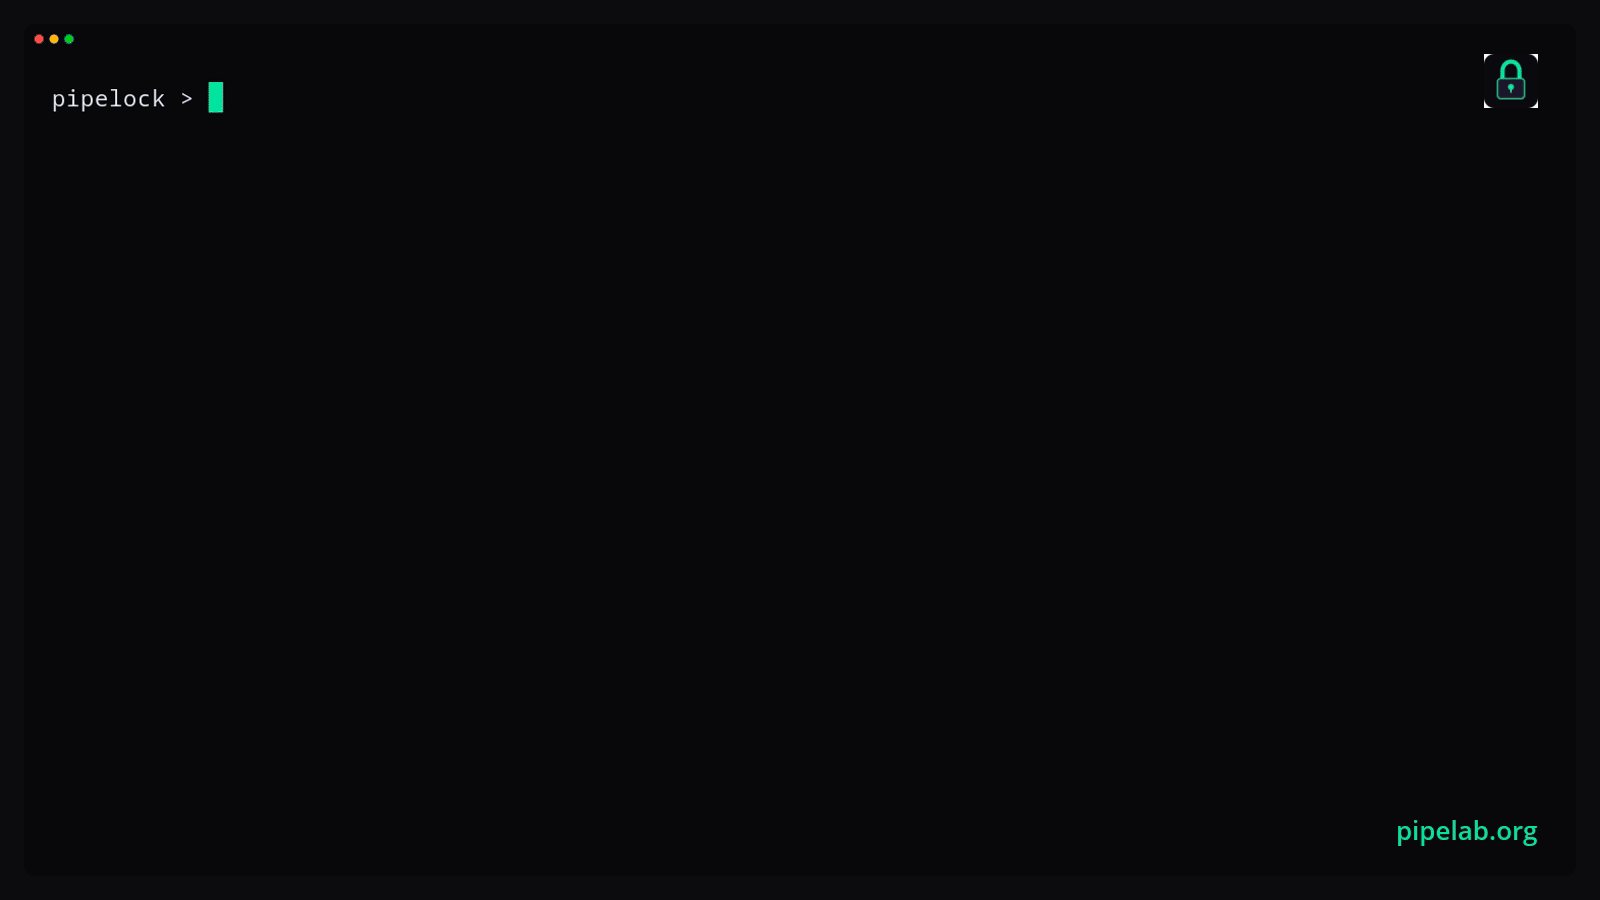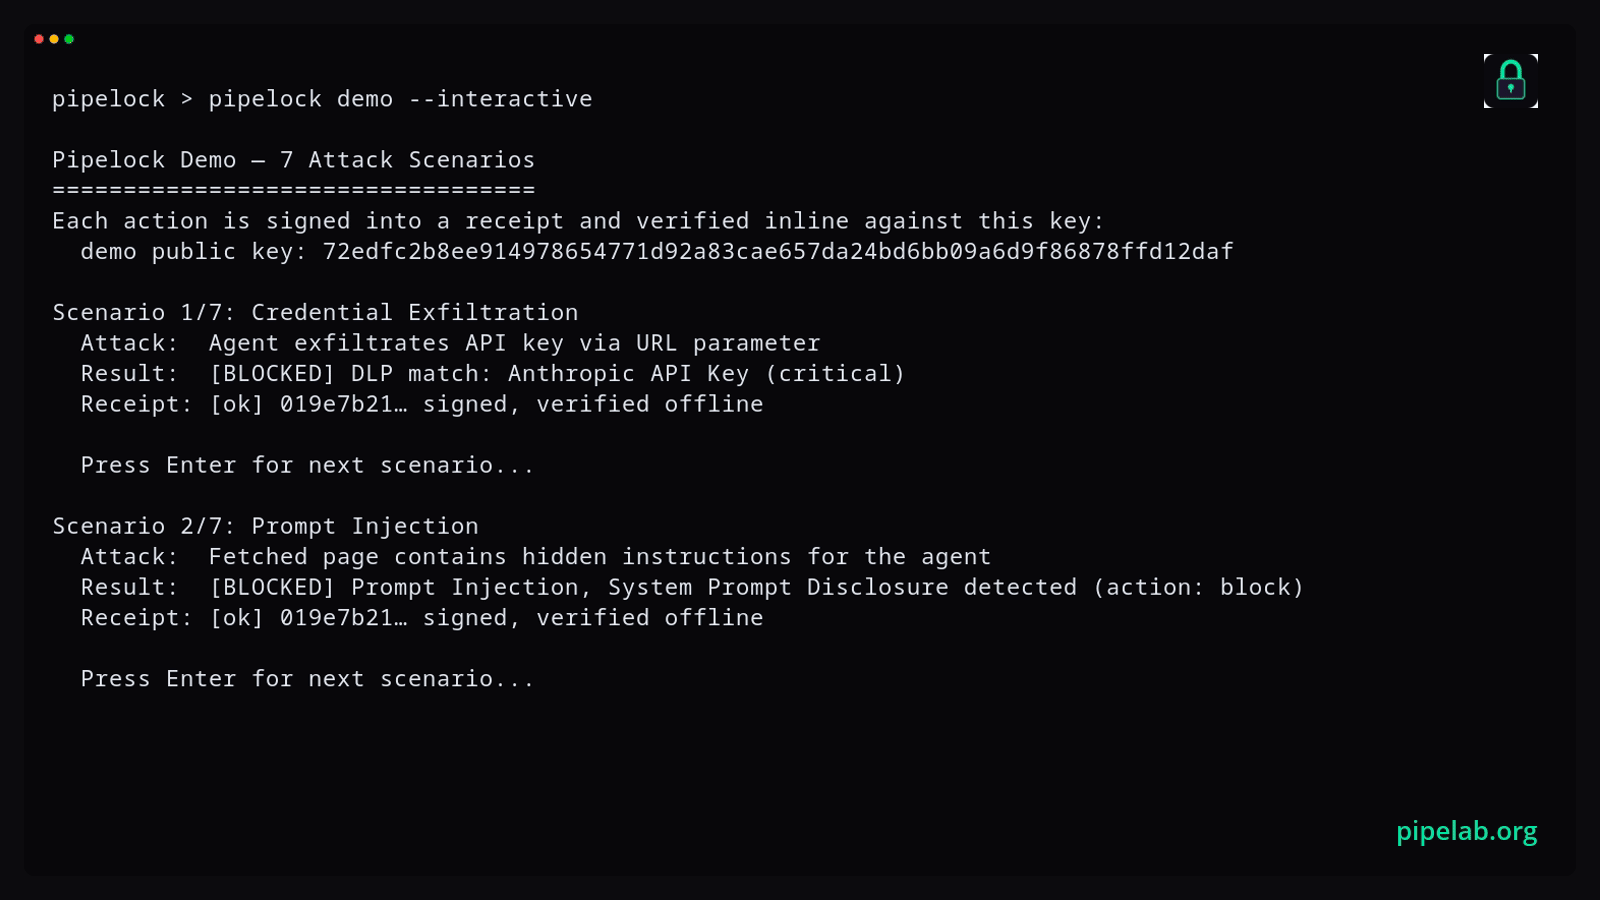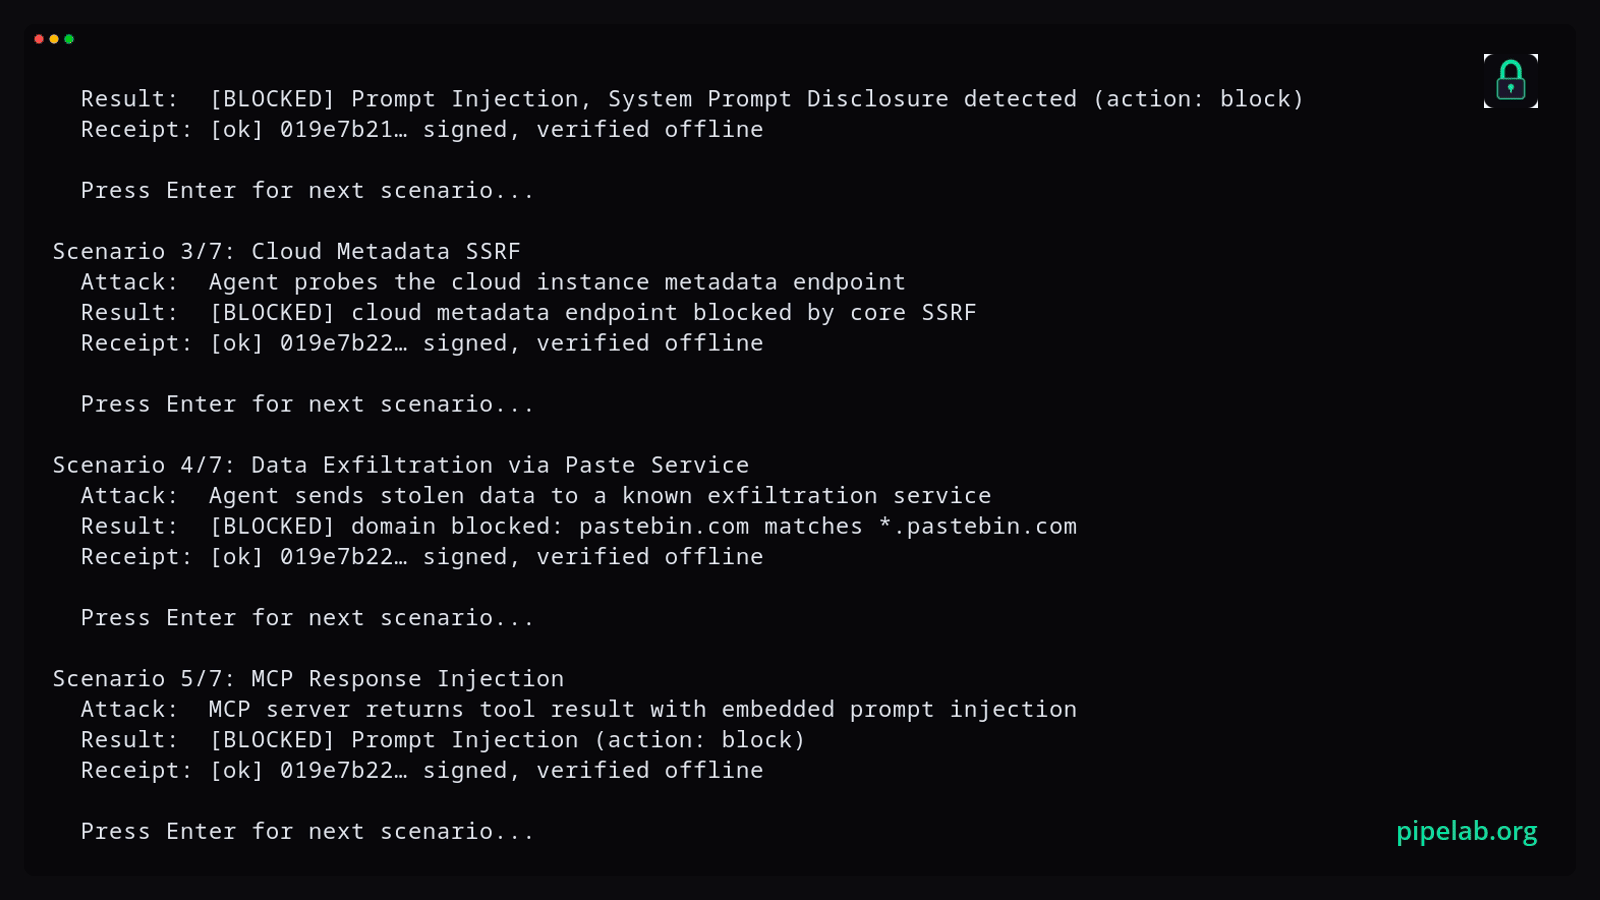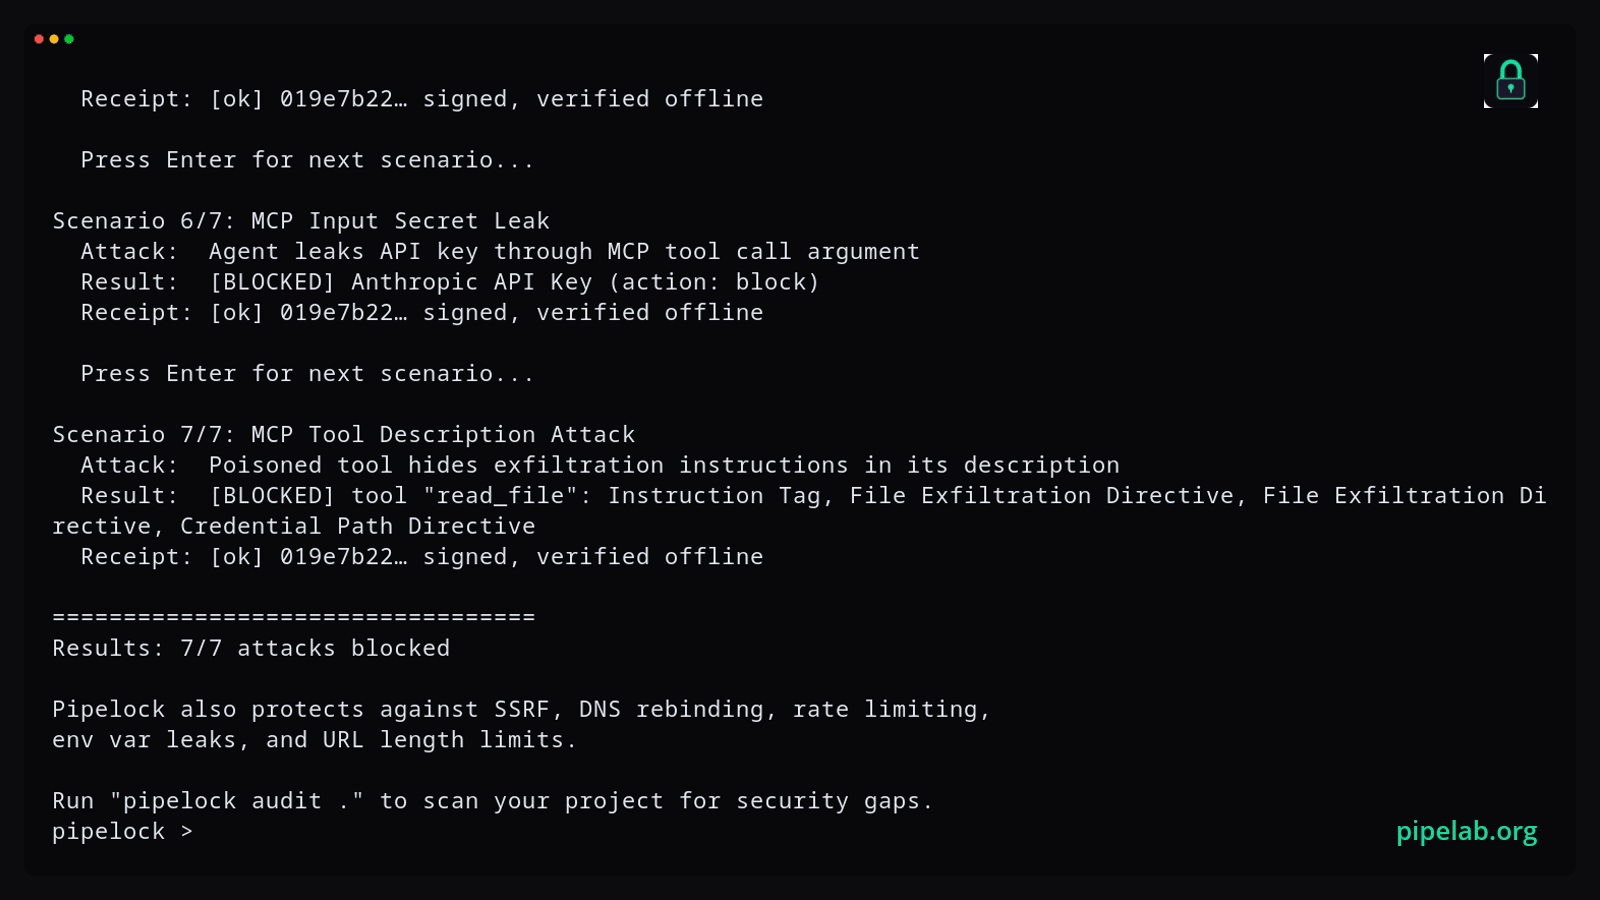 luckypipewrench/pipelock
Open-source AI agent firewall that scans HTTP, MCP, A2A, and WebSocket traffic for exfiltration, SSRF, and prompt injection, emitting verifiable…
 shredzwho/ig-detective
OSINT tool researched and designed to hunt down IG handles
 julioliraup/antiphishing
Advanced Phishing Protection: Suricata rulesets open and free
 corazawaf/coraza
Go-based Web Application Firewall library compatible with ModSecurity SecLang rules and OWASP Core Rule Set v4, providing real-time HTTP traffic…
 nccgroup/demiguise
HTA encryption tool for RedTeams
 c0oki3s/veilgate
Asymmetric defense against adversarial AI agents. VeilGate evaluates each incoming request, redirects suspected agents into a per-IP-consistent…
 matro7sh/bypassav
This map lists the essential techniques to bypass anti-virus and EDR
 abacus-group-rto/legion
Legion is an open source, easy-to-use, super-extensible and semi-automated network penetration testing tool that aids in discovery, reconnaissance…
 syworks/wireless-ids
Ability to detect suspicious activity such as (WEP/WPA/WPS) attack by sniffing the air for wireless packets.
 wietze/invoke-argfuscator
Invoke-ArgFuscator is an open-source, cross-platform PowerShell module that helps generate obfuscated command-lines for common system-native…
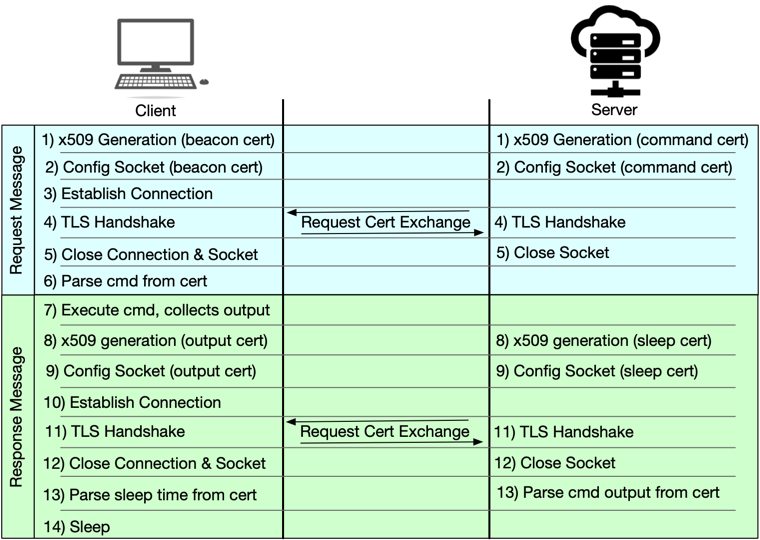 jconwell/secret_handshake
A prototype malware C2 channel using x509 certificates over mTLS