
ROADtools
 dirkjanm/roadtools
A collection of Azure AD/Entra tools for offensive and defensive security purposes
authenticationcloud-infrastructure-securitycloud-security+5
2.7k
dirkjanm/roadtoolsA collection of Azure AD/Entra tools for offensive and defensive security purposes
 fabacab/awesome-cybersecurity-blueteam
:computer:🛡️ A curated collection of awesome resources, tools, and other shiny things for cybersecurity blue teams.
 freeipa/freeipa
Centralizes identity, authentication, and access control for Linux/UNIX environments using LDAP, Kerberos, PKI, DNS, and Active Directory trust.
 cyberark/skywrapper
SkyWrapper helps to discover suspicious creation forms and uses of temporary tokens in AWS
 logisek/evilmist
EvilMist is a collection of scripts and utilities designed to support cloud penetration testing & red teaming. The toolkit helps identify…
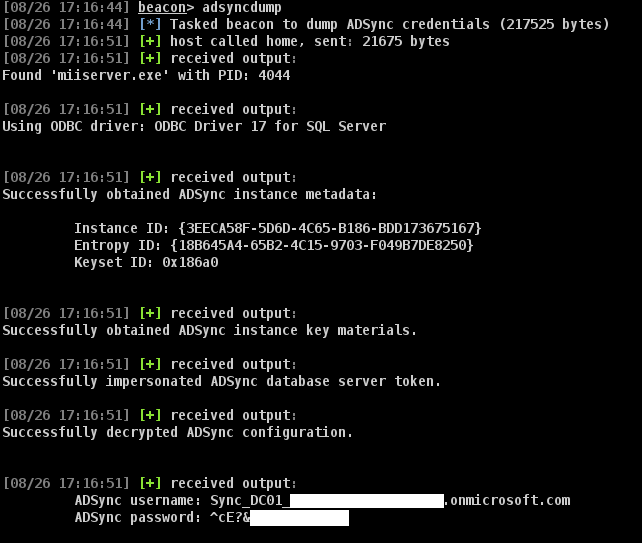 paradoxis/adsyncdump-bof
The ADSyncDump BOF is a port of Dirk-Jan Mollema's adconnectdump.py / ADSyncDecrypt into a Beacon Object File (BOF) with zero dependencies.
 matrix-org/synapse
Synapse: Matrix homeserver written in Python/Twisted.
 nuid/nebulousad
NebulousAD automated credential auditing tool.
 intuitem/ciso-assistant-community
GRC platform for risk management, compliance, and audit with 200+ frameworks, automatic control mapping, vulnerability management, and incident…
 openwisp/openwisp-controller
Network and WiFi controller: provisioning, configuration management and updates, (pull via openwisp-config or push via SSH), x509 PKI management and…
 andresriancho/enumerate-iam
Enumerate the permissions associated with AWS credential set
 netflix/repokid
AWS Least Privilege for Distributed, High-Velocity Deployment
 sachitrafa/yourmemory
Agentic AI memory with Ebbinghaus forgetting curve decay. +16pp better recall than Mem0 on LoCoMo.
 specterops/bloodhound
Six Degrees of Domain Admin
 gerenios/aadinternals
PowerShell module for administering and auditing Azure AD and Office 365, enabling token manipulation, user enumeration, and security assessments of…
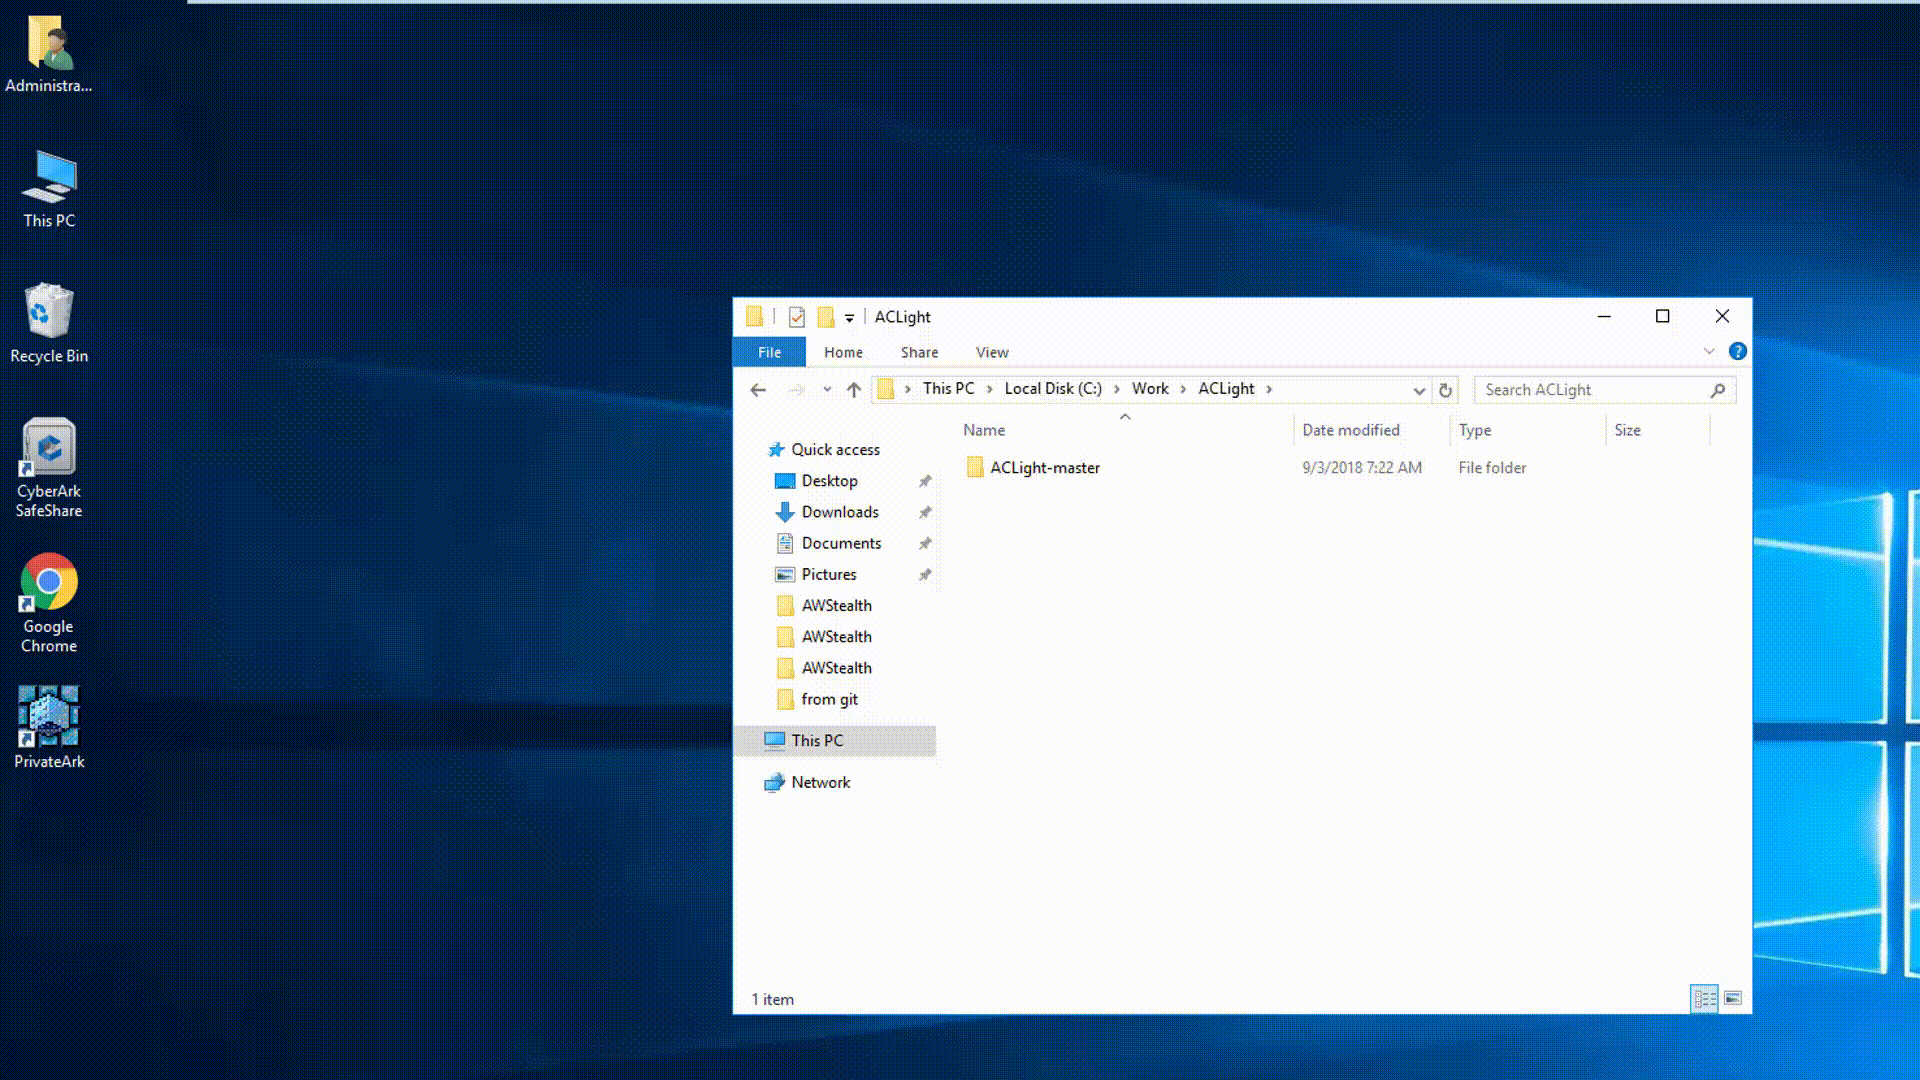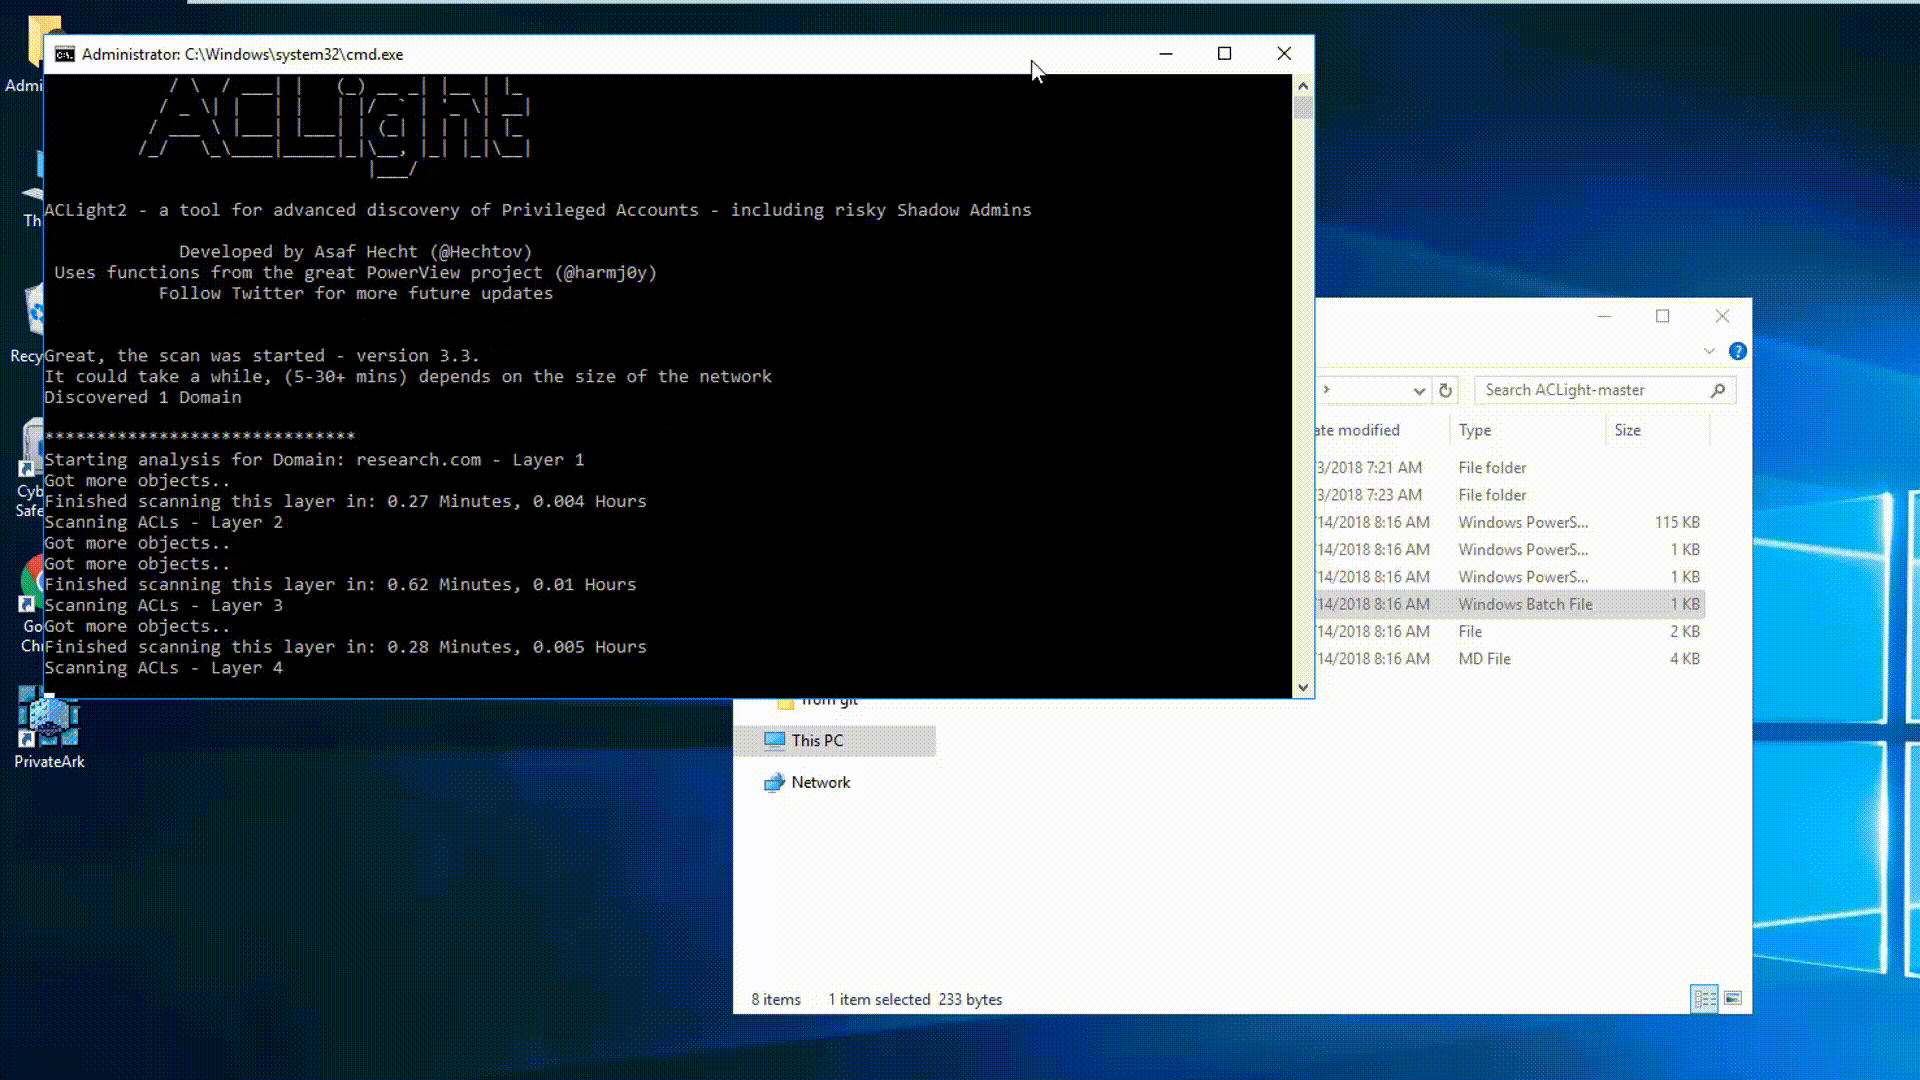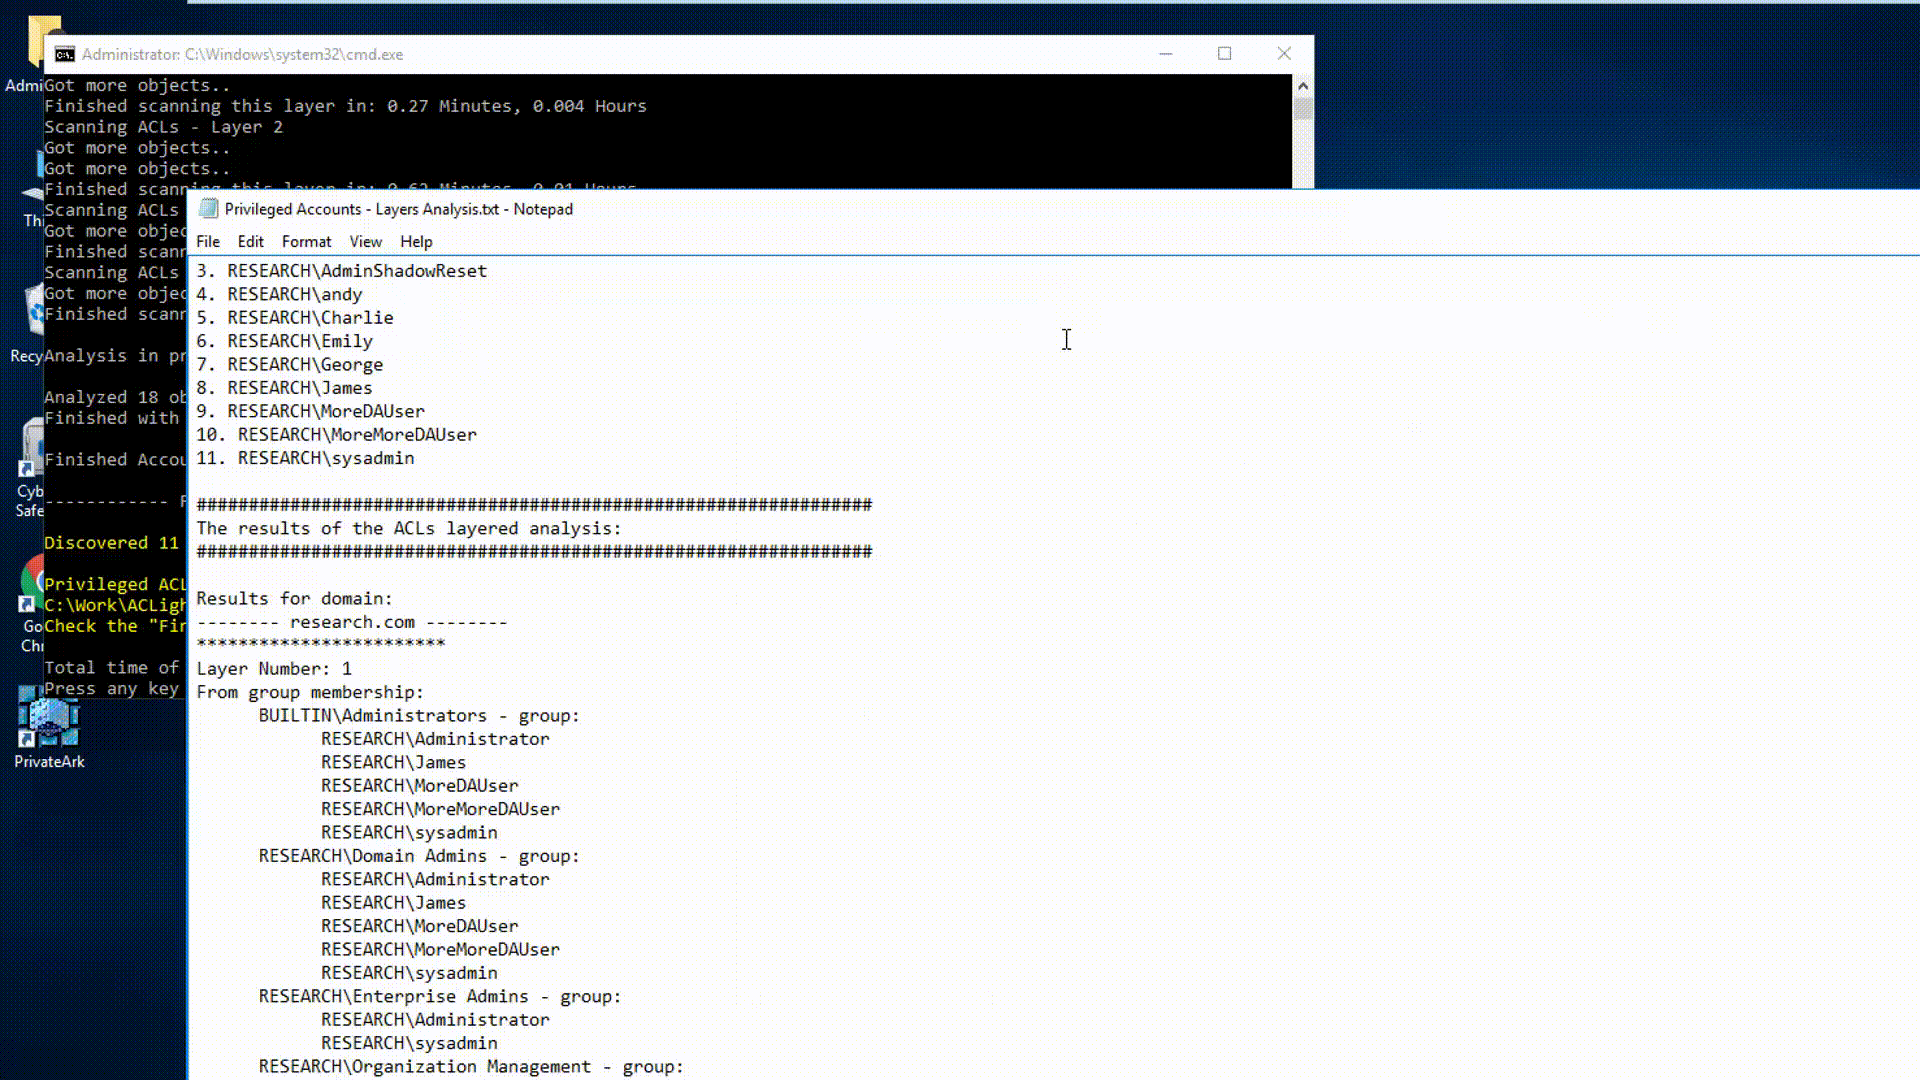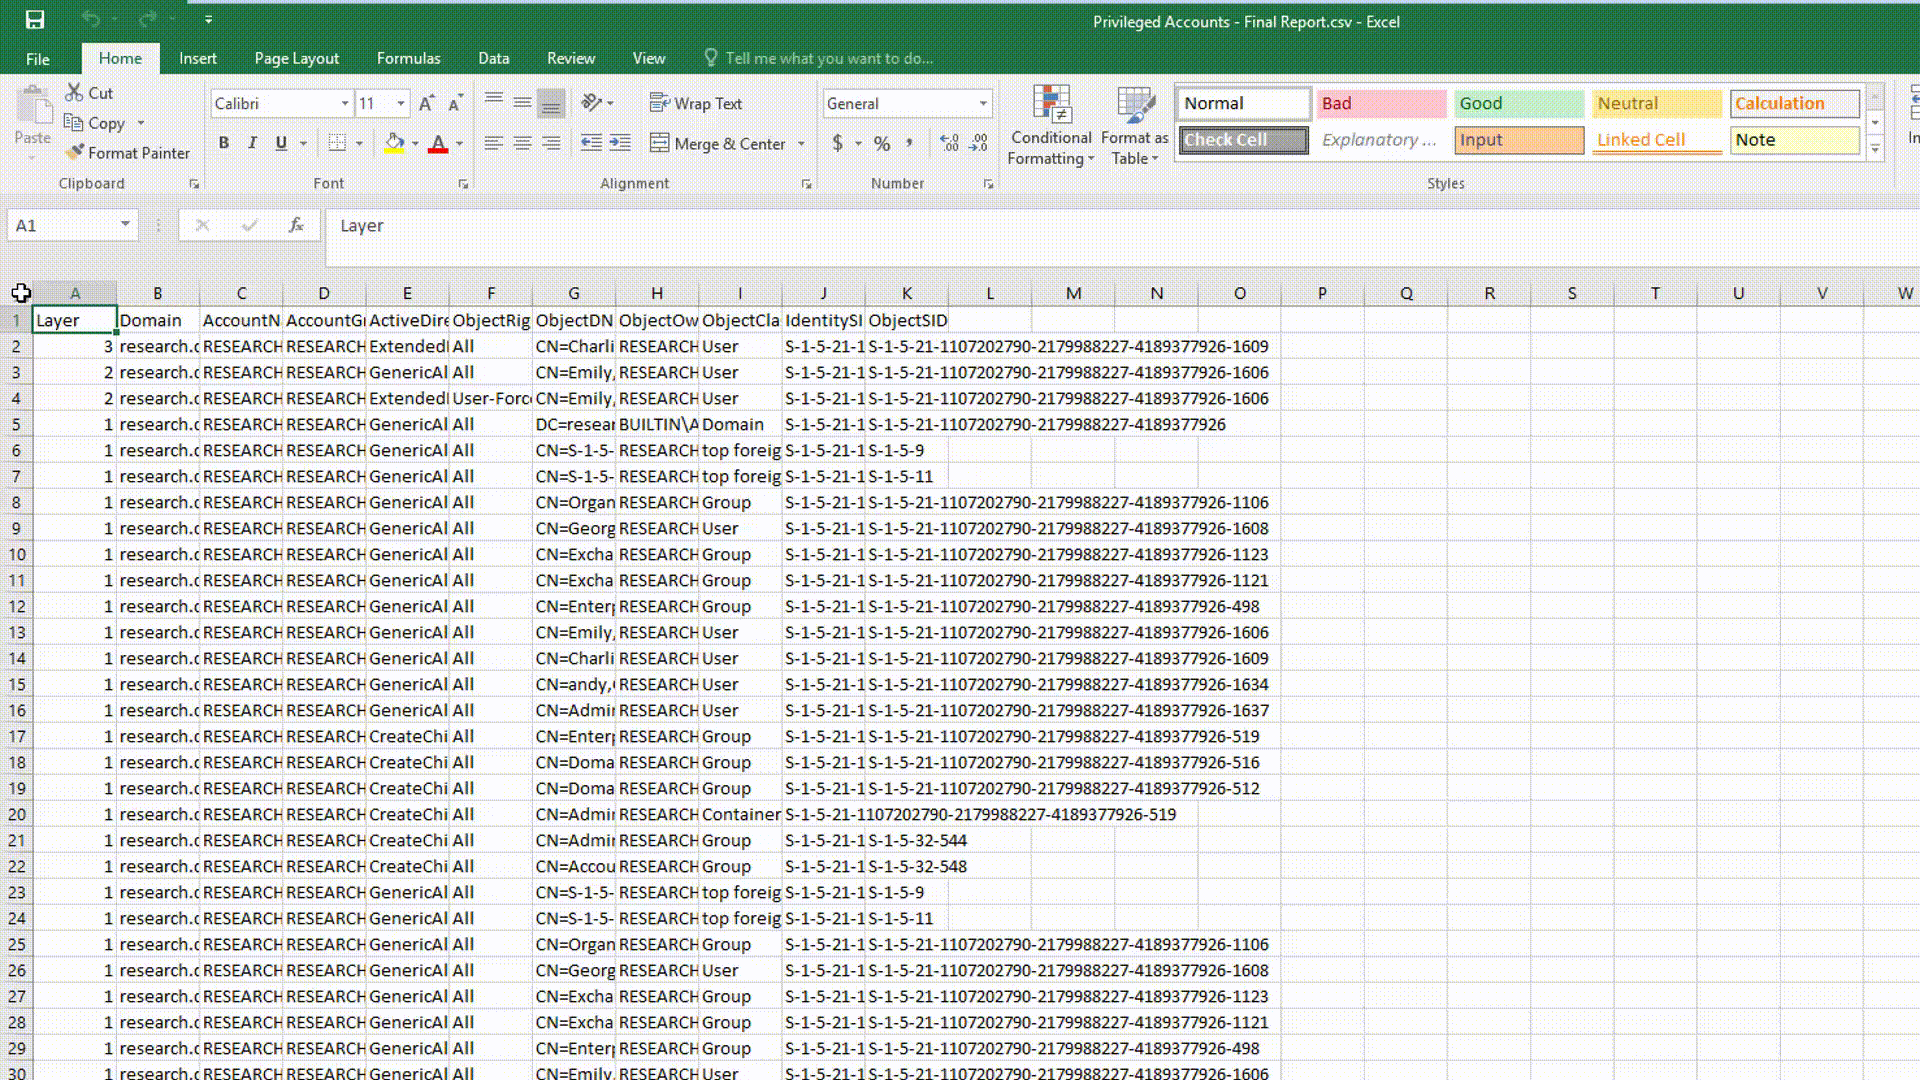 cyberark/aclight
A script for advanced discovery of Privileged Accounts - includes Shadow Admins
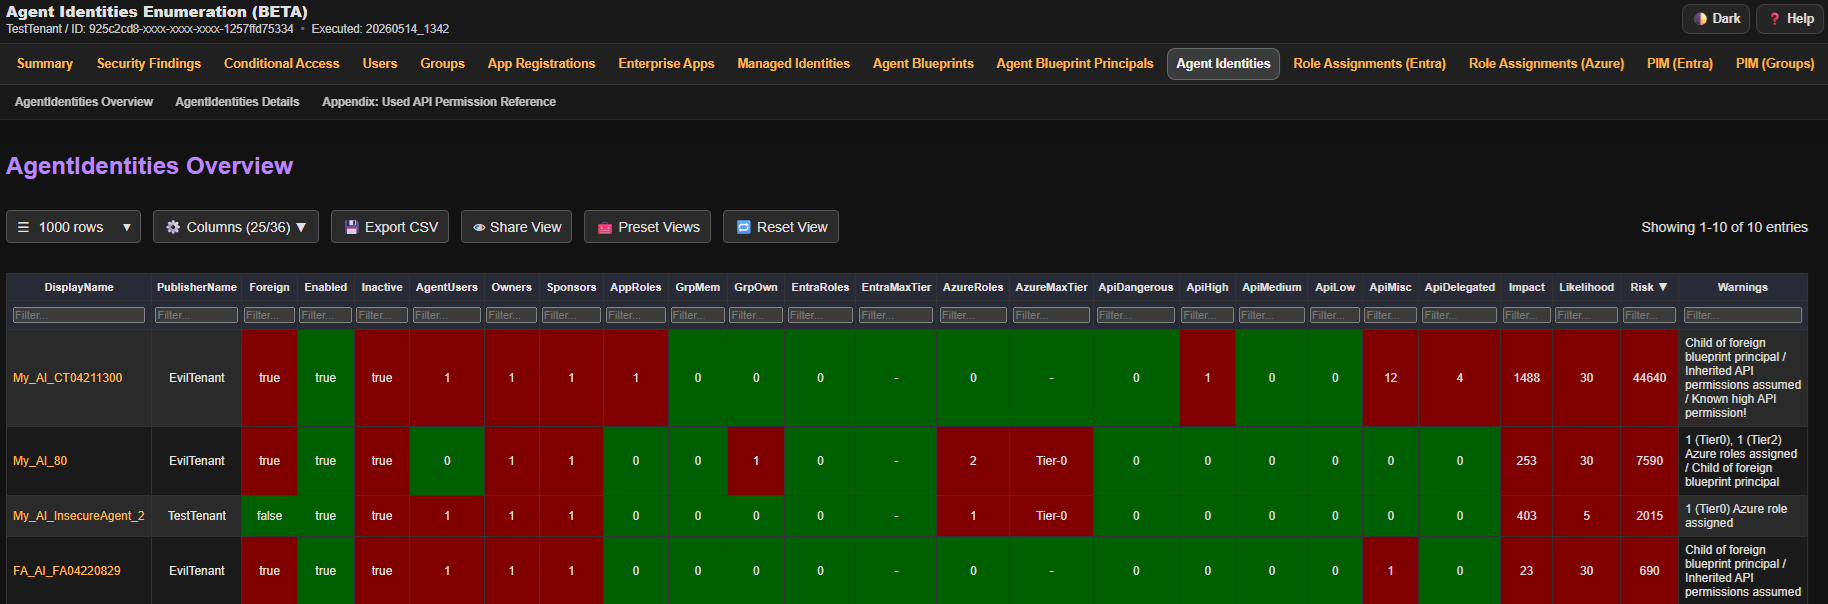 compasssecurity/entrafalcon
A lightweight PowerShell tool for assessing the security posture of Microsoft Entra ID environments. It helps identify privileged objects, risky…
 sap8899/reportly
AzureAD/EntraID user activity reporter for blue teams. Input a suspicious user and time frame to receive a detailed report of user info, actions, and…