
CVE-2026-59358
 abraxas/cve-2026-59358
Proof-of-concept lab and exploit client for CVE-2026-59358, demonstrating Cloud Foundry UAA reuse of a user PKCE token as client_credentials Bearer…
authenticationexploitationidentity-access-management+4
abraxas/cve-2026-59358Proof-of-concept lab and exploit client for CVE-2026-59358, demonstrating Cloud Foundry UAA reuse of a user PKCE token as client_credentials Bearer…
 foxboron/attezt
An open-source TPM device-attest-01 CA server
 renich/genclave
Centralized, TPM 2.0 hardware-backed cryptographic identity enclave and multi-protocol bridge for Linux (FIDO2/CTAP2 WebAuthn Passkeys, OpenSSH…
 freeipa/freeipa
Centralizes identity, authentication, and access control for Linux/UNIX environments using LDAP, Kerberos, PKI, DNS, and Active Directory trust.
 spiffe/spire
Workload identity platform that attests running services, issues SPIFFE IDs/SVIDs, and enables mTLS and JWT authentication for Kubernetes,…
 yubico/libfido2
Provides library functionality for FIDO2, including communication with a device over USB or NFC.
 t94j0/adexplorersnapshot-rs
Converts Active Directory Explorer snapshot (.dat) files into BloodHound CE JSON archives for graph-based AD attack-path analysis and reconnaissance.
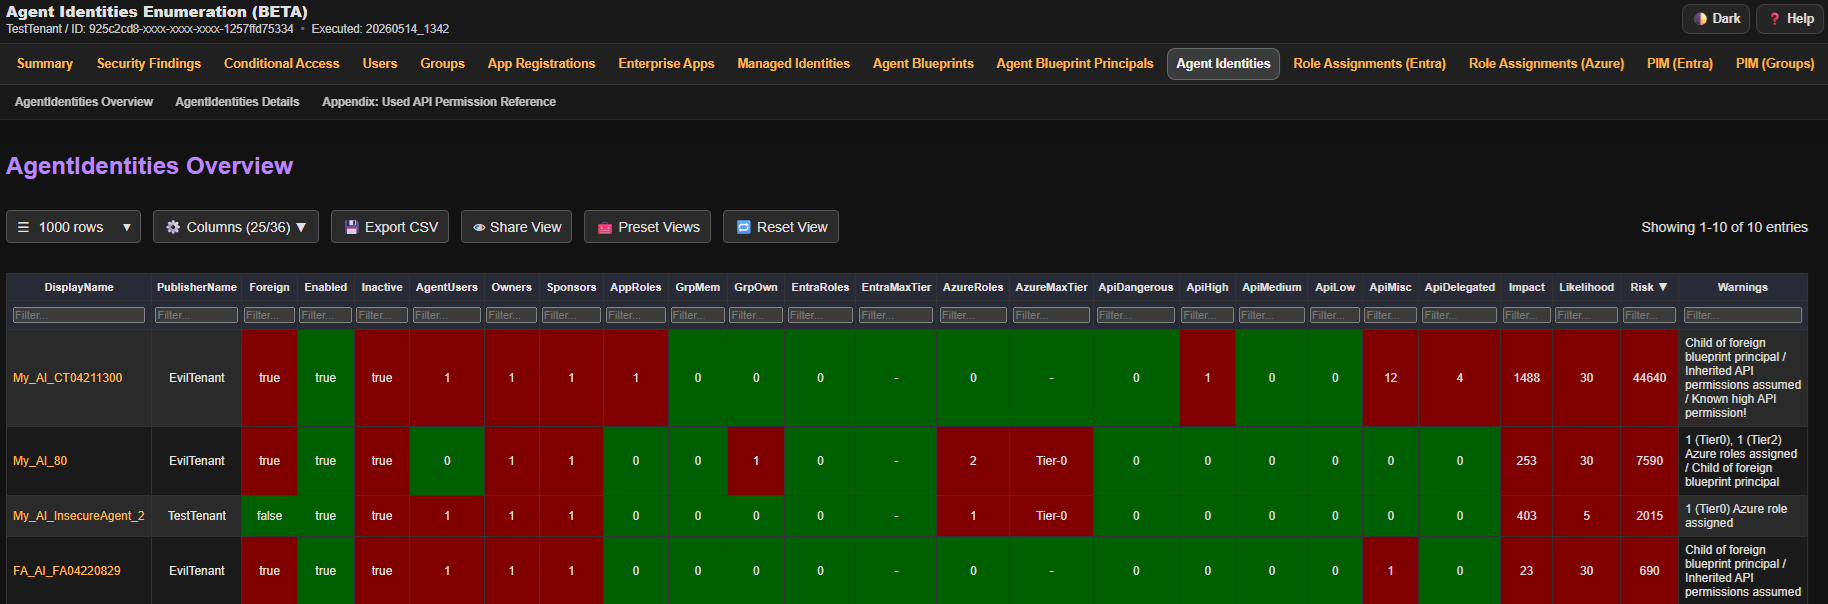 compasssecurity/entrafalcon
A lightweight PowerShell tool for assessing the security posture of Microsoft Entra ID environments. It helps identify privileged objects, risky…
 bishopfox/cirro
Creating attacks paths across management and data planes
 boltgolt/howdy
🛡️ Windows Hello™ style facial authentication for Linux