
CVE-2026-59358
 abraxas/cve-2026-59358
Proof-of-concept lab and exploit client for CVE-2026-59358, demonstrating Cloud Foundry UAA reuse of a user PKCE token as client_credentials Bearer…
authenticationexploitationidentity-access-management+4
abraxas/cve-2026-59358Proof-of-concept lab and exploit client for CVE-2026-59358, demonstrating Cloud Foundry UAA reuse of a user PKCE token as client_credentials Bearer…
 anthonyk2923/cve-2026-94609
Write-up and proof-of-concept for CVE-2026-94609, an authentik privilege-escalation flaw letting users with add_user_to_group join superuser groups…
 les-k/wp-secure-mcp
A WordPress plugin exposing an MCP server over the REST API, with the security model as the point -- closes the CVE-2026-15015 OAuth-bypass shape by…
 franklincg/secdim-assurance-drift-challenge
SecDim Challenge Builder repro inspired by CVE-2026-88861: AAL1 MFA bypass at privileged credential boundary
 ivanesk315/cve-2026-18963
Docker-based lab and Python exploit for CVE-2026-18963, a Keycloak reset-credentials flow bypass enabling account takeover via email verification…
 squeeze440/tugtainer-poc
PoC — OIDC id_token accepted without signature/audience/expiry check in Tugtainer (GHSA-crjc-6vc7-xrfh, CVE-2026-87004, CVSS 8.1).
 bakos-sandor-nx/teamcity-cve-2026-63077-remediation
JetBrains TeamCity On-Premises CVE-2026-63077 Emergency Hardening & Patch Runbook Package
 v-jfanca/cve-2026-20833-rc4-kerberos
Kerberos RC4 deprecation: detection, remediation and guidance (CVE-2026-20833)
 siyad01/agentbox
Open-source sandboxed runtime for AI agents — gVisor/Docker isolation, credential vault, immutable audit log. Built after CVE-2026-25253.
 karitamw/printnightmare-detection-mitigation-lab
Sanitised Windows security lab demonstrating Active Directory administration, host and network detection, and layered mitigation of CVE-2021-34527.
 michael-kanda/wp2shell-ioc-scanner
Detects shadow-administrator accounts in WordPress via configurable indicators and heuristics, then removes selected accounts through guarded, logged…
 fusionauth/fusionauth-samlv2
SAML v2.0 bindings in Java using JAXB
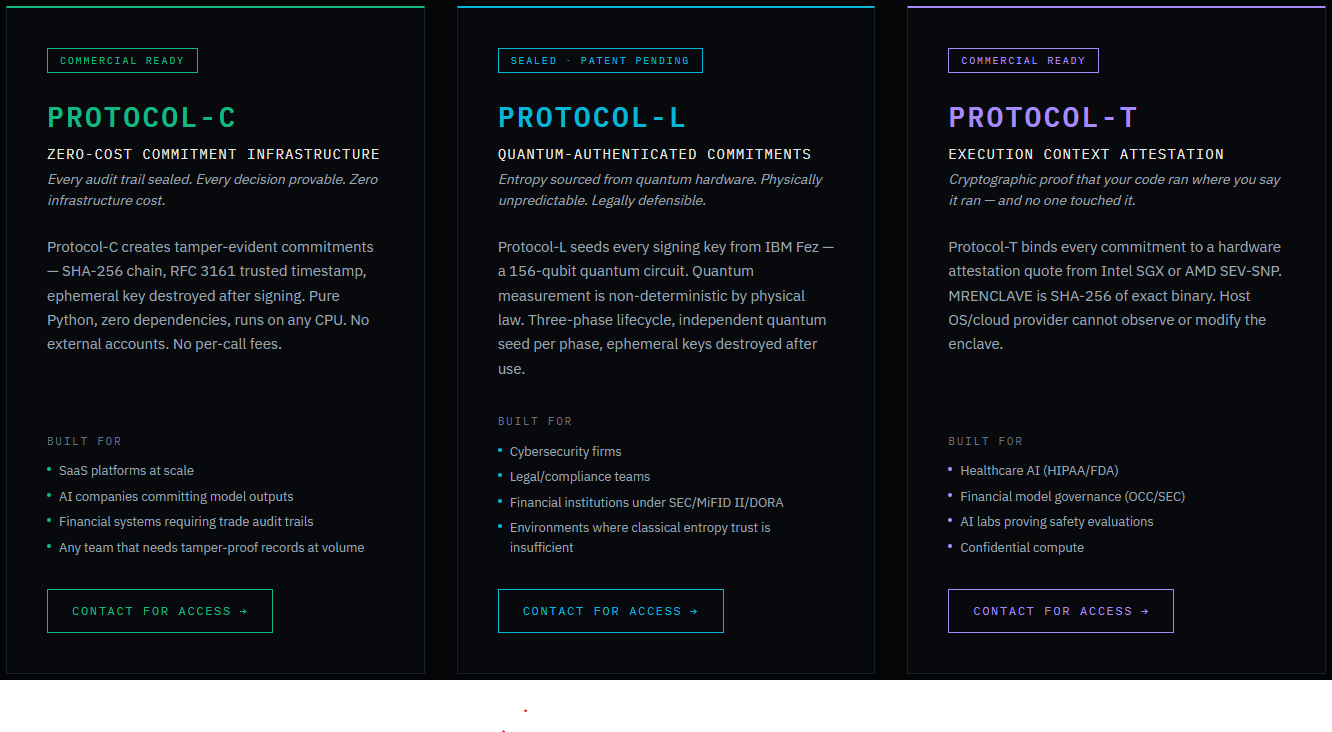 aetherai3/aether-protocol-p
Working implementation: cryptographically verified short-lived identities for AI decision authentication — CVE-2025-59536 (Patent Pending US…
 rajsidwadkar/uap-protocol
A unified, security-first wire protocol for tool access and agent coordination. UAP eliminates CVE-2025-49596 and MCP tool-poisoning vulnerabilities…
 rockmelodies/blackash-cve-2025-41115
CVE-2025-41115
 shanika04/cloudfoundry_uaa
CVE-2016-4468
 rhymeswithmogul/set-zerologonmitigation
Protect your domain controllers against Zerologon (CVE-2020-1472).
 notitssixtyn3in/cve-2025-4172025
Security advisory for CVE-2025-4172025: an authentication bypass vulnerability in Copilot enabling unauthorized account access, session hijacking,…