
Thunderstorm
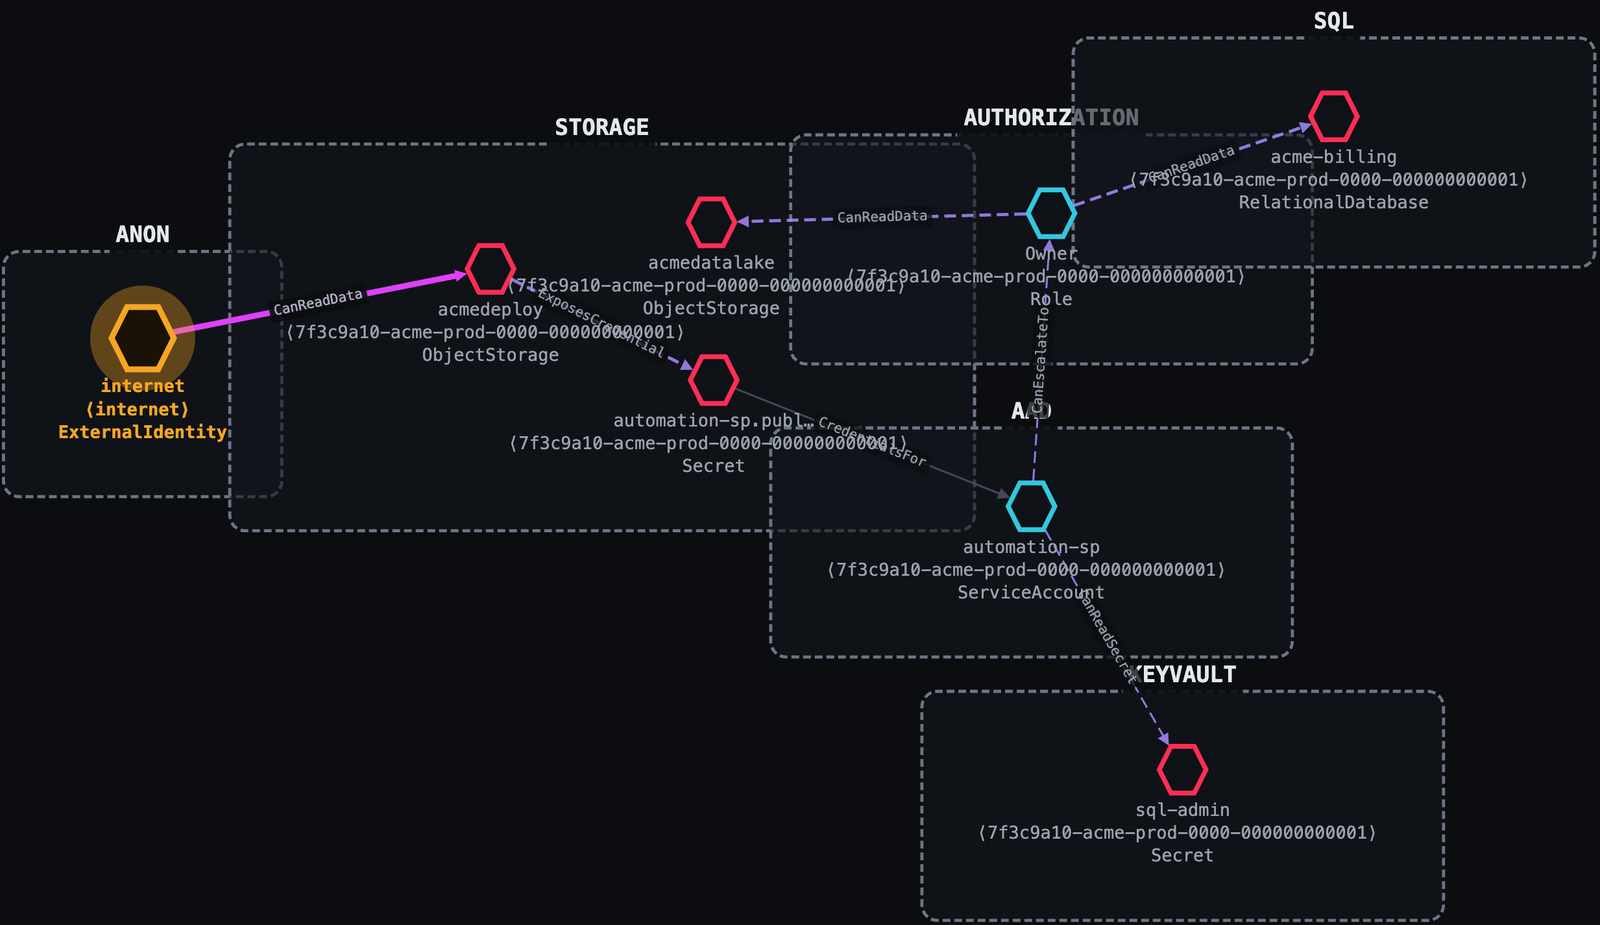
A collector and derivation engine. It maps your environment, evaluates effective permissions and trust, and writes a complete attack graph as a…

A collector and derivation engine. It maps your environment, evaluates effective permissions and trust, and writes a complete attack graph as a…

Safety cannot be a prompt instruction. TBP provides an external execution-layer boundary for autonomous agents, enforcing hard F/I/W invariants via…

Governed execution cells for AI agents.

Policy-governed LLMSecOps framework providing AST-based SAST, secret scanning, supply-chain and multi-cloud CSPM checks, AI-BoM generation, and CI/CD…

Production-grade Security Baseline & Hardening Guide for Ubuntu 24.04/26.04 LTS. Kernel isolation, custom AppArmor/Firejail 0.9.80, Rootless Docker,…

JetBrains TeamCity On-Premises CVE-2026-63077 Emergency Hardening & Patch Runbook Package

Zero-trust agentic AI platform. Supports SaaS and OnPrem (airgapped) deployments.

Kerberos RC4 deprecation: detection, remediation and guidance (CVE-2026-20833)

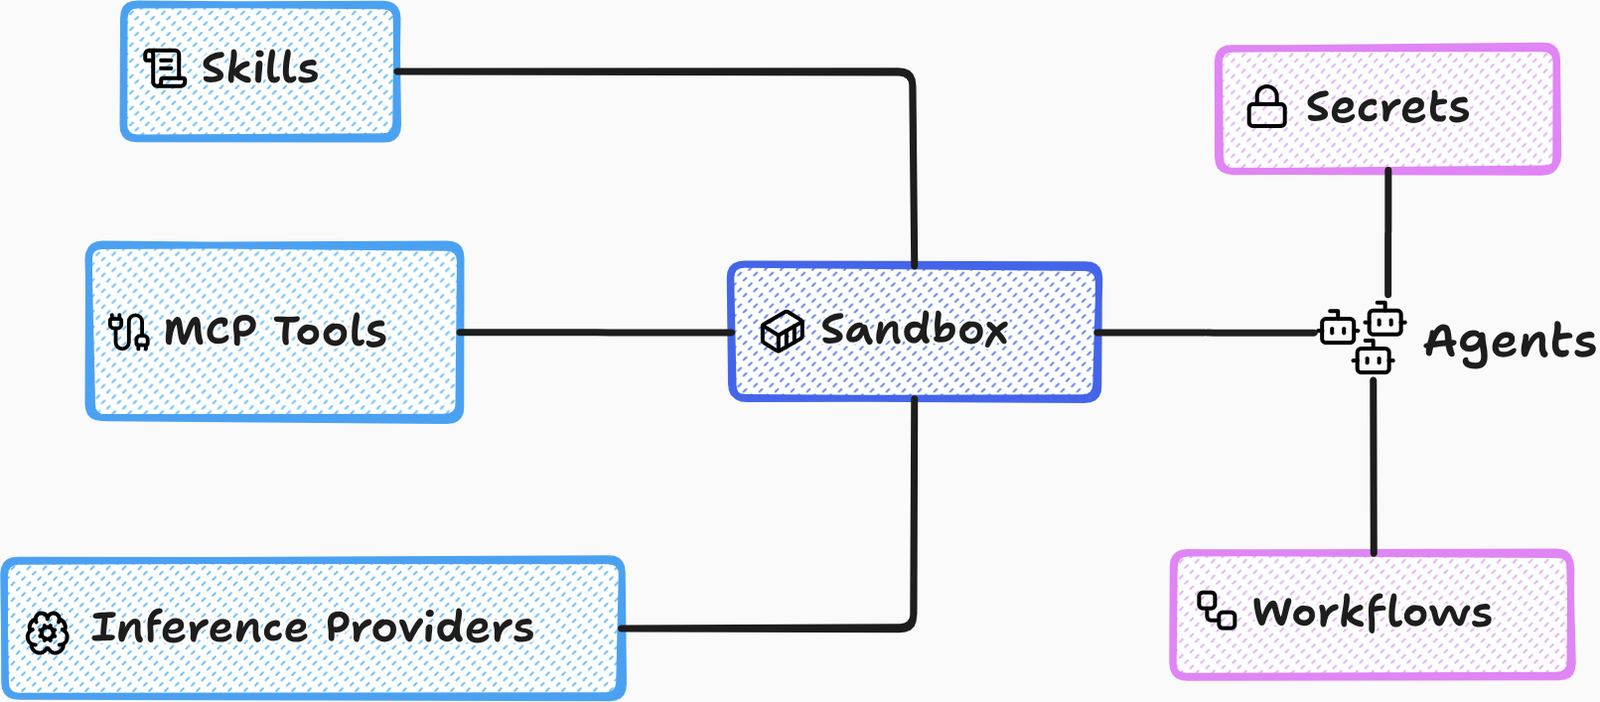
Open-source sandboxed runtime for AI agents — gVisor/Docker isolation, credential vault, immutable audit log. Built after CVE-2026-25253.

💻🛡️ A curated collection of awesome resources, tools, and other shiny things for cybersecurity blue teams.

SAST CLI for scanning Java, JavaScript, and .NET applications plus AWS Lambda functions, detecting code vulnerabilities and over-permissive IAM…

Certificate authority issuing short-lived code-signing certificates tied to OpenID Connect identities, enabling verifiable software supply chain…

Workload identity platform that attests running services, issues SPIFFE IDs/SVIDs, and enables mTLS and JWT authentication for Kubernetes,…

Network and WiFi controller: provisioning, configuration management and updates, (pull via openwisp-config or push via SSH), x509 PKI management and…

Declarative policy engine that enables authorization and policy enforcement across services, Kubernetes, Terraform, Docker, and APIs using the Rego…

Detection-engineering reference mapping Windows, cloud, container, identity, and ICS attack classes to Sigma rules, trust-boundary models, BYOVD…

Offline AD/Entra attack-path analyzer for SharpHound/AzureHound JSON. Surfaces prioritized privilege escalation, credential, and misconfiguration…

Open source solutions for SOC2, GDPR, and ISO27001