

mimikatz
 gentilkiwi/mimikatz
A little tool to play with Windows security
authenticationexploitationexploit-frameworks+10
21.8k
gentilkiwi/mimikatzA little tool to play with Windows security

 joker25000/optiva-framework
Optiva-Framework 🔎 Web Application Scanner🕵️
 nccgroup/redsnarf
RedSnarf is a pen-testing / red-teaming tool for Windows environments
 keithjjones/fileintel
A modular Python application to pull intelligence about malicious files
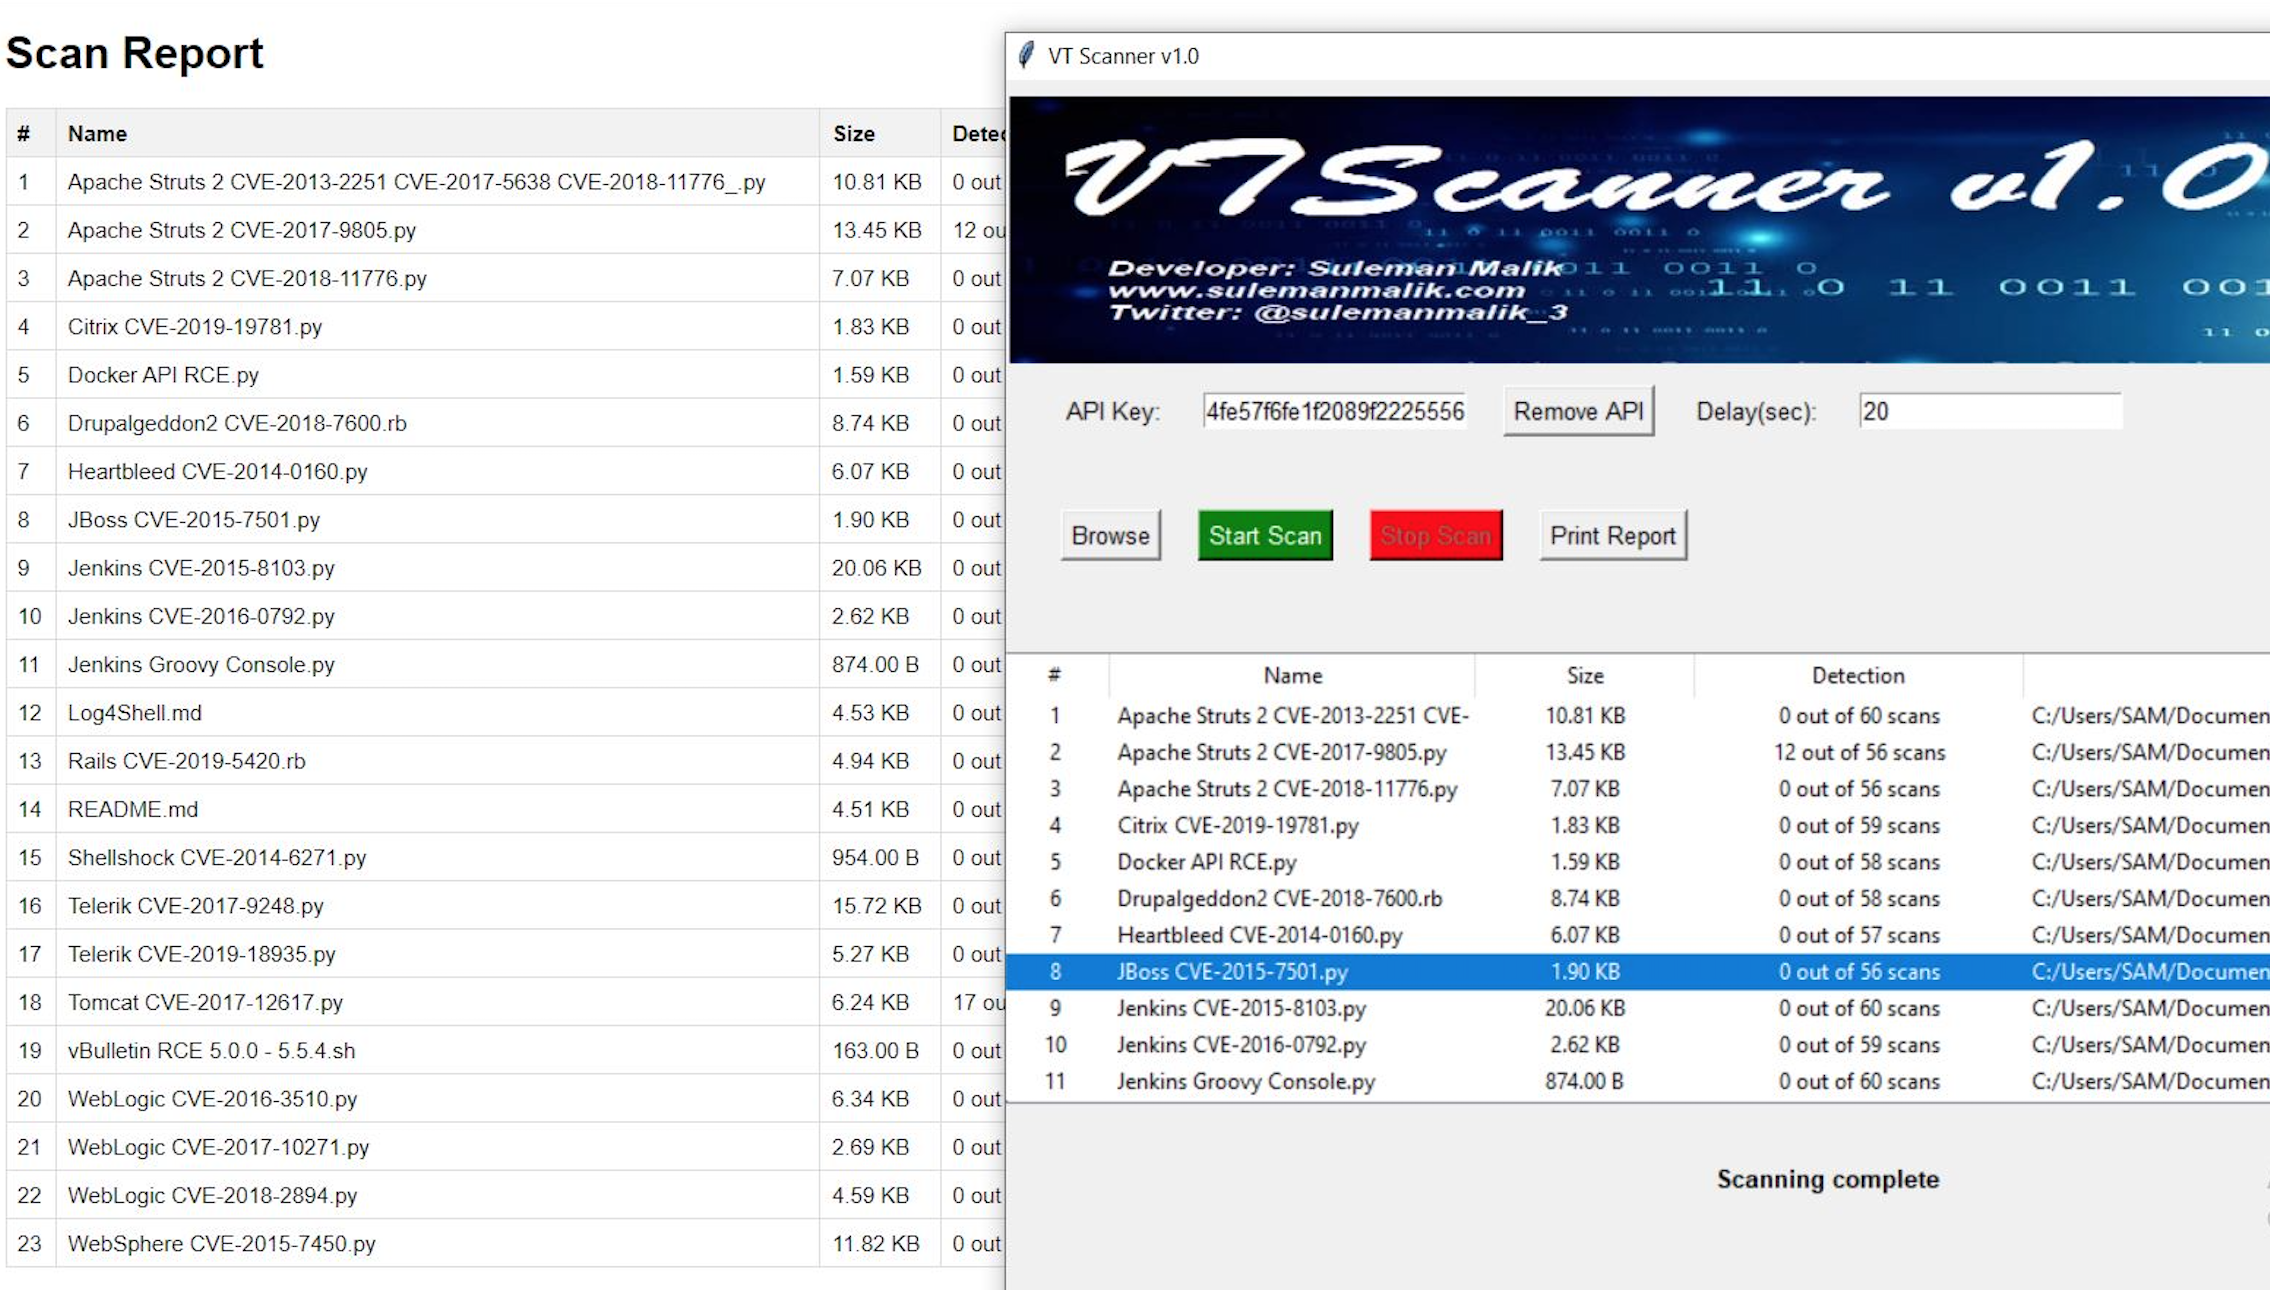 samhaxr/vtscanner
A comprehensive Python-based security tool for file scanning, malware detection, and analysis in an ever-evolving cyber landscape.
 n1ght-w0lf/uchihash
A small utility to deal with malware embedded hashes.
 sepinf-inc/iped
IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…
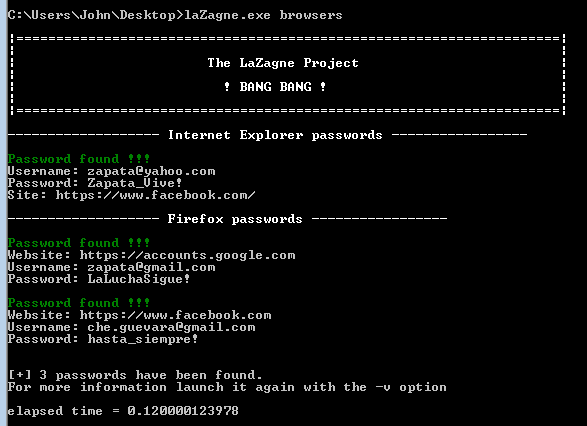 alessandroz/lazagne
Cross-platform credential recovery tool that extracts stored passwords from browsers, email clients, databases, system mechanisms, and network…
 jedisct1/libsodium
A modern, portable, easy to use crypto library.
 jtesta/rainbowcrackalack
Rainbow table generation & lookup tools. Make Rainbow Tables Great Again!
 mr-un1k0d3r/windows-signedbinary
Mutates signed Windows binaries to retain valid catalog signatures while changing file hashes, bypassing hash-based endpoint blocks and exposing…
 lkarlslund/hashmuncher
Grab NetNTLMv2 hashes using ETW with administrative rights on Windows 8.1 / Windows Server 2016 and later
 frizb/hashcat-cheatsheet
Hashcat reference for OSCP/penetration testing: hash identification, cracking syntax for Linux, Windows, archives, databases, Kerberos tickets, and…
 pan-unit42/dotnetfile
Python library for parsing CLR/PE metadata in .NET assemblies, exposing streams and hash fingerprints to support malware analysis and threat hunting.
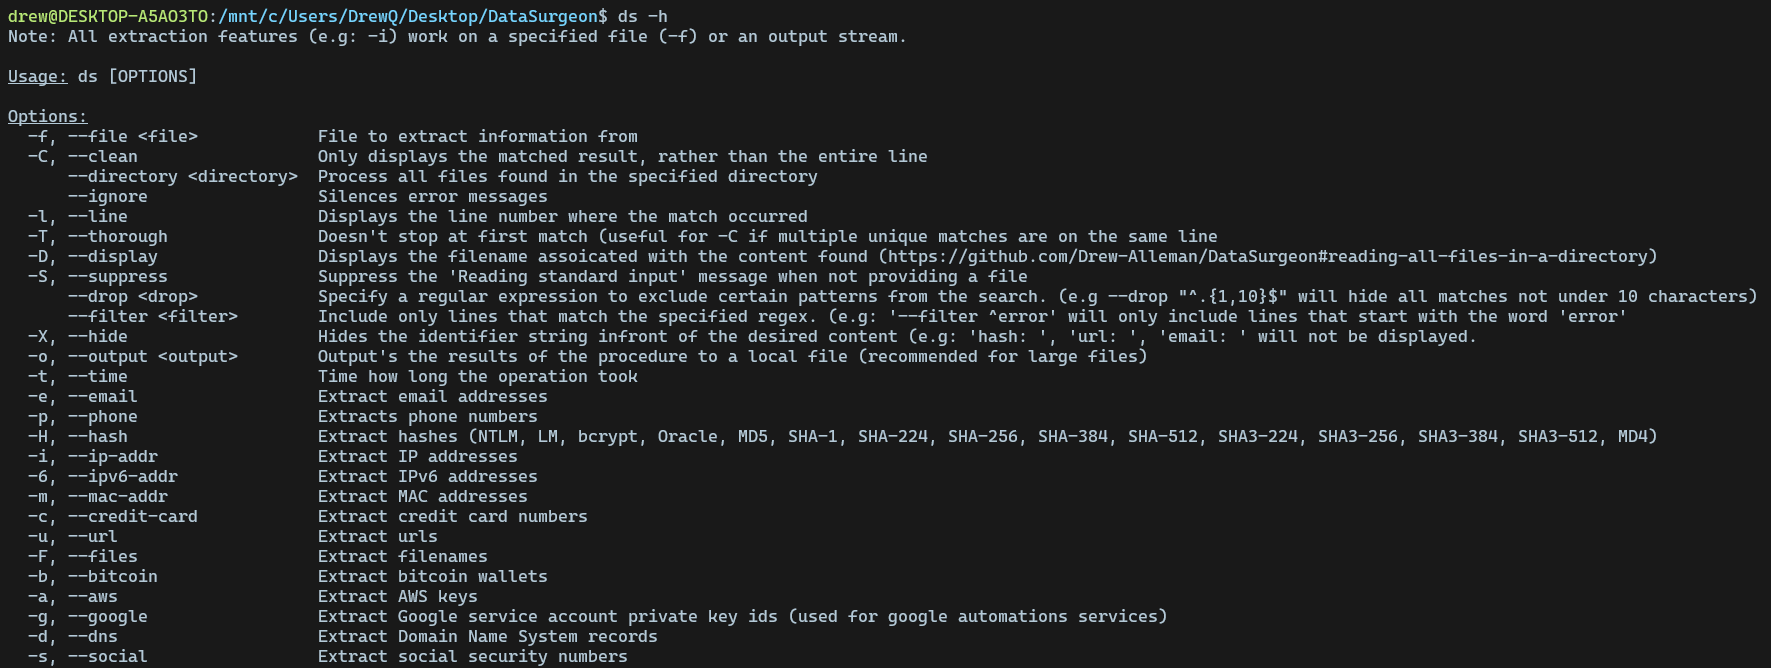 drew-alleman/datasurgeon
Quickly Extracts IP's, Email Addresses, Hashes, Files, Credit Cards, Social Security Numbers and a lot More From Text
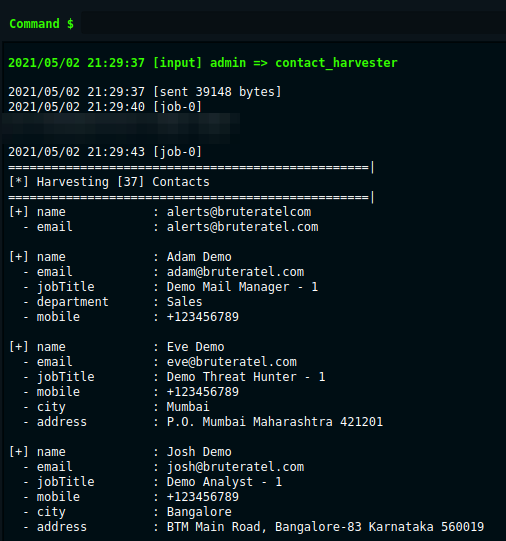 paranoidninja/brc4-bof-artillery
Collection of Brute Ratel C4 BOFs for Windows post-exploitation: process memory access, NetNTLMv2 hash retrieval, contact harvesting, and…
 iomoath/filewatchtower
FWT is a security analysis and file monitoring tool that utilizes Sysmon events.