
 psypanda/hashid
Software to identify the different types of hashes -
 struppigel/portex
Java library to analyse Portable Executable files with a special focus on malware analysis and PE malformation robustness
 jessek/hashdeep
Cross-platform hashing toolset for computing message digests (MD5, SHA-1, SHA-256, Tiger, Whirlpool) with recursive directory traversal and file…
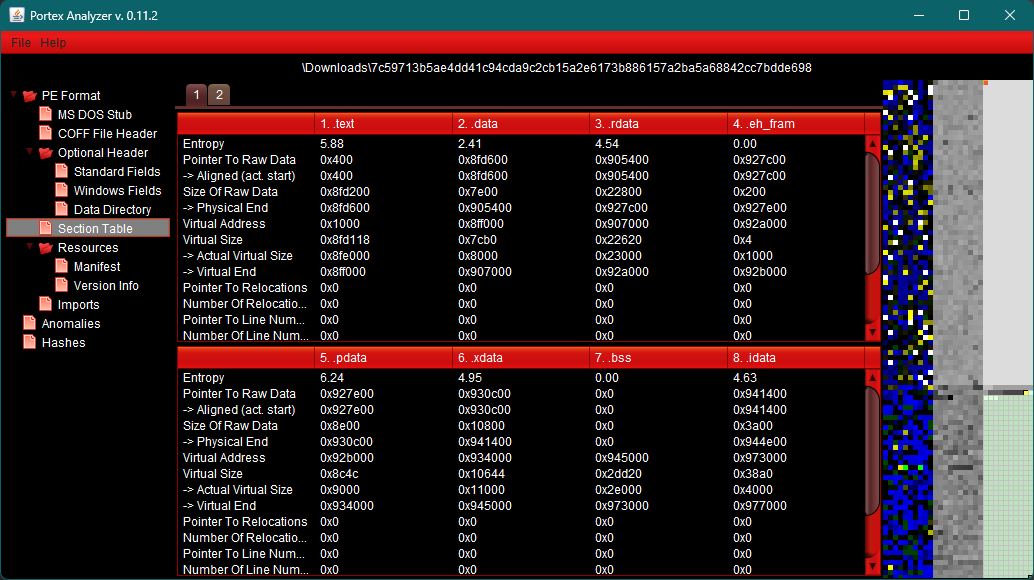 struppigel/portexanalyzergui
Graphical interface for PortEx, a Portable Executable and Malware Analysis Library
 netspooky/inhale
A malware analysis and classification tool.
 pan-unit42/dotnetfile
Python library for parsing CLR/PE metadata in .NET assemblies, exposing streams and hash fingerprints to support malware analysis and threat hunting.
 bmaia/binwally
Binary and Directory tree comparison tool using Fuzzy Hashing
 qsecure-labs/deadmatter
Offset Independent Credential Extraction Tool
 iomoath/filewatchtower
FWT is a security analysis and file monitoring tool that utilizes Sysmon events.
 neorai/vt-py-scanner
Recursively scan folders with VirusTotal API to detect malware. Features hash lookup, CSV export, real-time progress, and rate-limit handling for…
 star-sg/random-scripts
Collection of DFIR and OSINT Python scripts for parsing malicious LNK samples, extracting OLE objects from MHTML, and hashing favicons to hunt…
 sepinf-inc/iped
IPED Digital Forensic Tool. It is an open source software that can be used to process and analyze digital evidence, often seized at crime scenes by…